Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/intuitem/ciso-assistant-community
Defensive ToolsVulnerability AnalysisConfiguration AuditingPrivacyThreat IntelligenceIdentity & Access Management (IAM)Incident Response
GitHub
Share
intuitem/ciso-assistant-community

ciso-assistant-community

GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident response workflows.

View RepositoryWebsite
4.6k9041590 days agoReviewed by Kitploit

Star the project 🌟 to get releases notification and help growing the community!

intuitem%2Fciso-assistant-community | Trendshift
intuitem.com · SaaS Free trial · Roadmap · Docs · Languages · Discord · Frameworks
GitHub Release GitHub contributors GitHub Repo stars GitHub forks Discord

CISO Assistant offers a fresh perspective on Cybersecurity Management and GRC (Governance, Risk, and Compliance) practices:
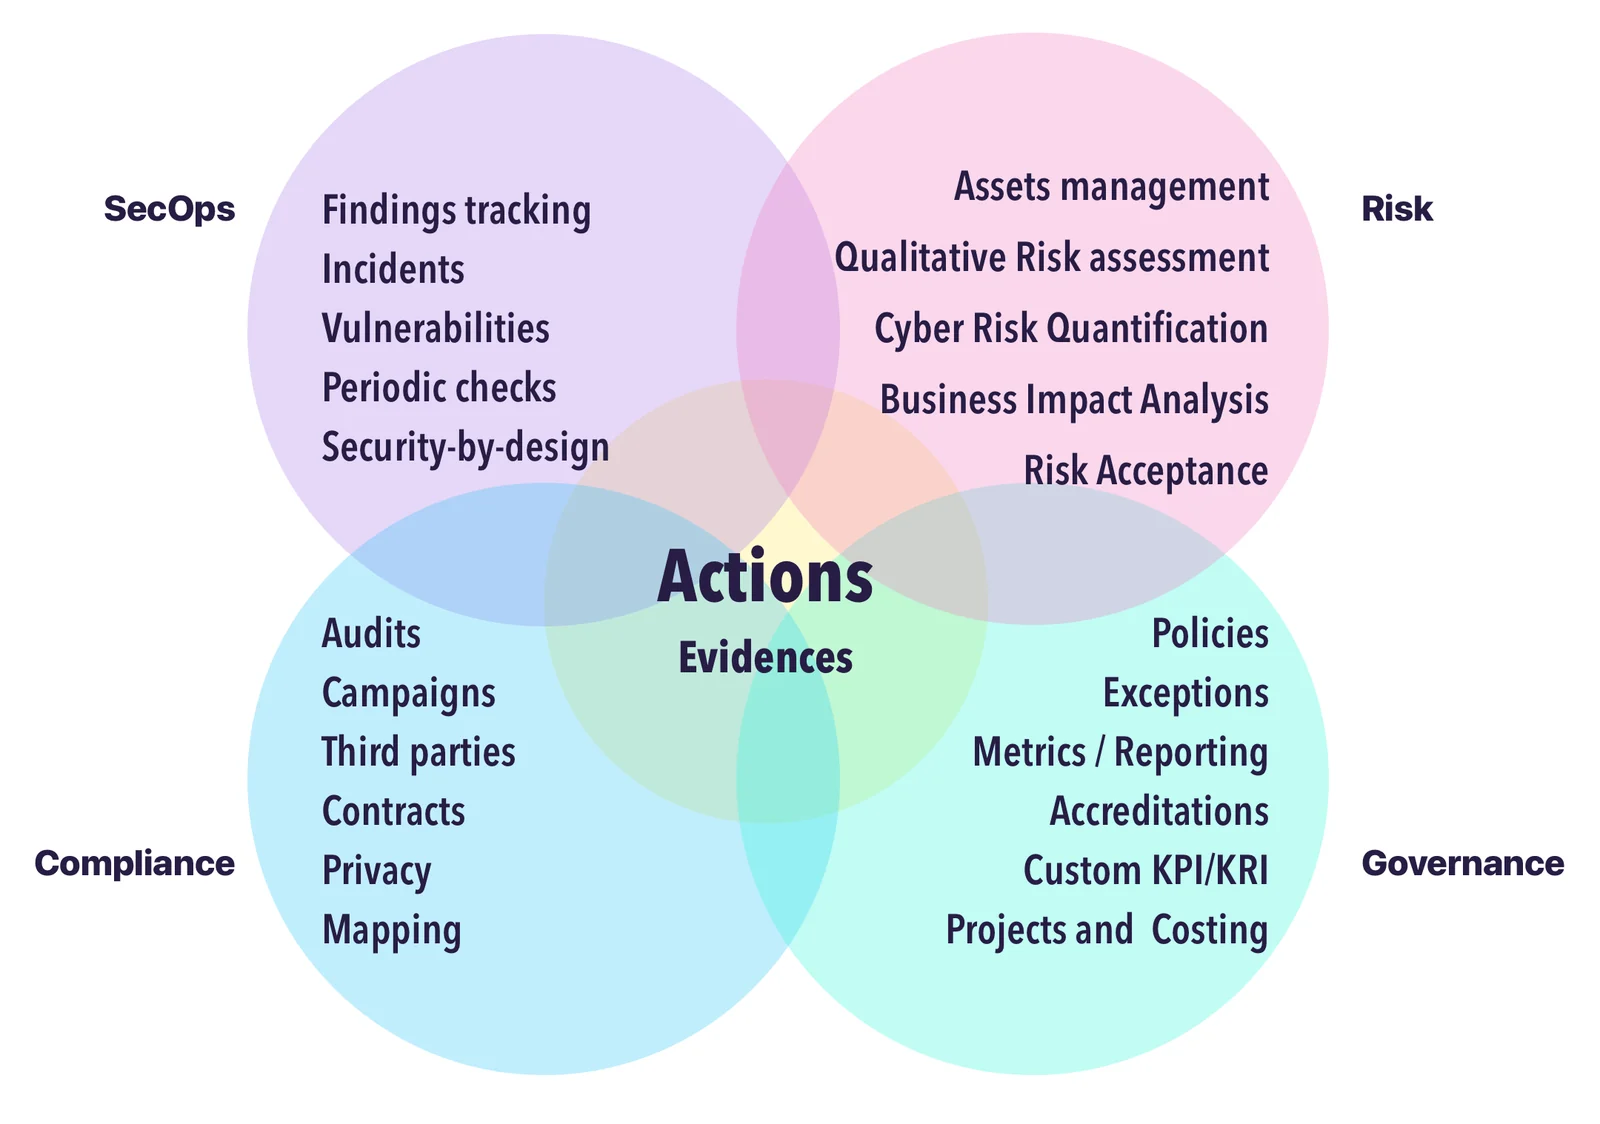
  • Designed as a central hub to connect multiple cybersecurity concepts with smart linking between objects,
  • Built as a multi-paradigm tool that adapts to different backgrounds, methodologies, and expectations,
  • Explicitly decouples compliance from cybersecurity controls, enabling reusability across the platform,
  • Promotes reusability and interlinking instead of redundant work,
  • Developed with an API-first approach to support both UI interaction and external automation,
  • Comes packed with a wide range of built-in standards, security controls, and threat libraries,
  • Offers an open format to customize and reuse your own objects and frameworks,
  • Includes built-in risk assessment and remediation tracking workflows,
  • Supports custom frameworks via a simple syntax and flexible tooling,
  • Provides rich import/export capabilities across various channels and formats (UI, CLI, Kafka, reports, etc.).

Single Hub

Our vision is to create a one-stop-shop for cybersecurity management—modernizing GRC through simplification and interoperability.

As practitioners working with cybersecurity and IT professionals, we've faced the same issues: tool fragmentation, data duplication, and a lack of intuitive, integrated solutions. CISO Assistant was born from those lessons, and we're building a community around pragmatic, common-sense principles.

We’re constantly evolving with input from users and customers. Like an octopus 🐙, CISO Assistant keeps growing extra arms—bringing clarity, automation, and productivity to cybersecurity teams while reducing the effort of data input and output.

CodeFactor API Tests Functional Tests FOSSA Status Plumber Score


Quick Start 🚀

[!TIP] The easiest way to get started is through the free trial of cloud instance available here.

Alternatively, once you have Docker and Docker-compose installed, on your workstation or server:

clone the repo:

git clone --single-branch -b main https://github.com/intuitem/ciso-assistant-community.git

and run the starter script

./docker-compose.sh     # Linux/MacOS
./docker-compose.ps1    # Windows

If you are looking for other installation options for self-hosting, check the config builder and the docs.

[!NOTE] The docker-compose script uses prebuilt Docker images supporting most of the standard hardware architecture. If you're using Windows, make sure to have Docker Desktop with WSL2 installed and trigger the PowerShell script. It will feed Docker Desktop on your behalf.

The docker compose file can be adjusted to pass extra parameters to suit your setup (e.g. Mailer settings).

[!WARNING] If you're getting warnings or errors about image's platform not matching host platform, raise an issue with the details and we'll add it shortly after. You can also use docker-compose-build.sh instead (see below) to build for your specific architecture.

[!CAUTION] Don't use the main branch code directly for production as it's the merge upstream and can have breaking changes during our development. Either use the tags for stable versions or prebuilt images.

Features

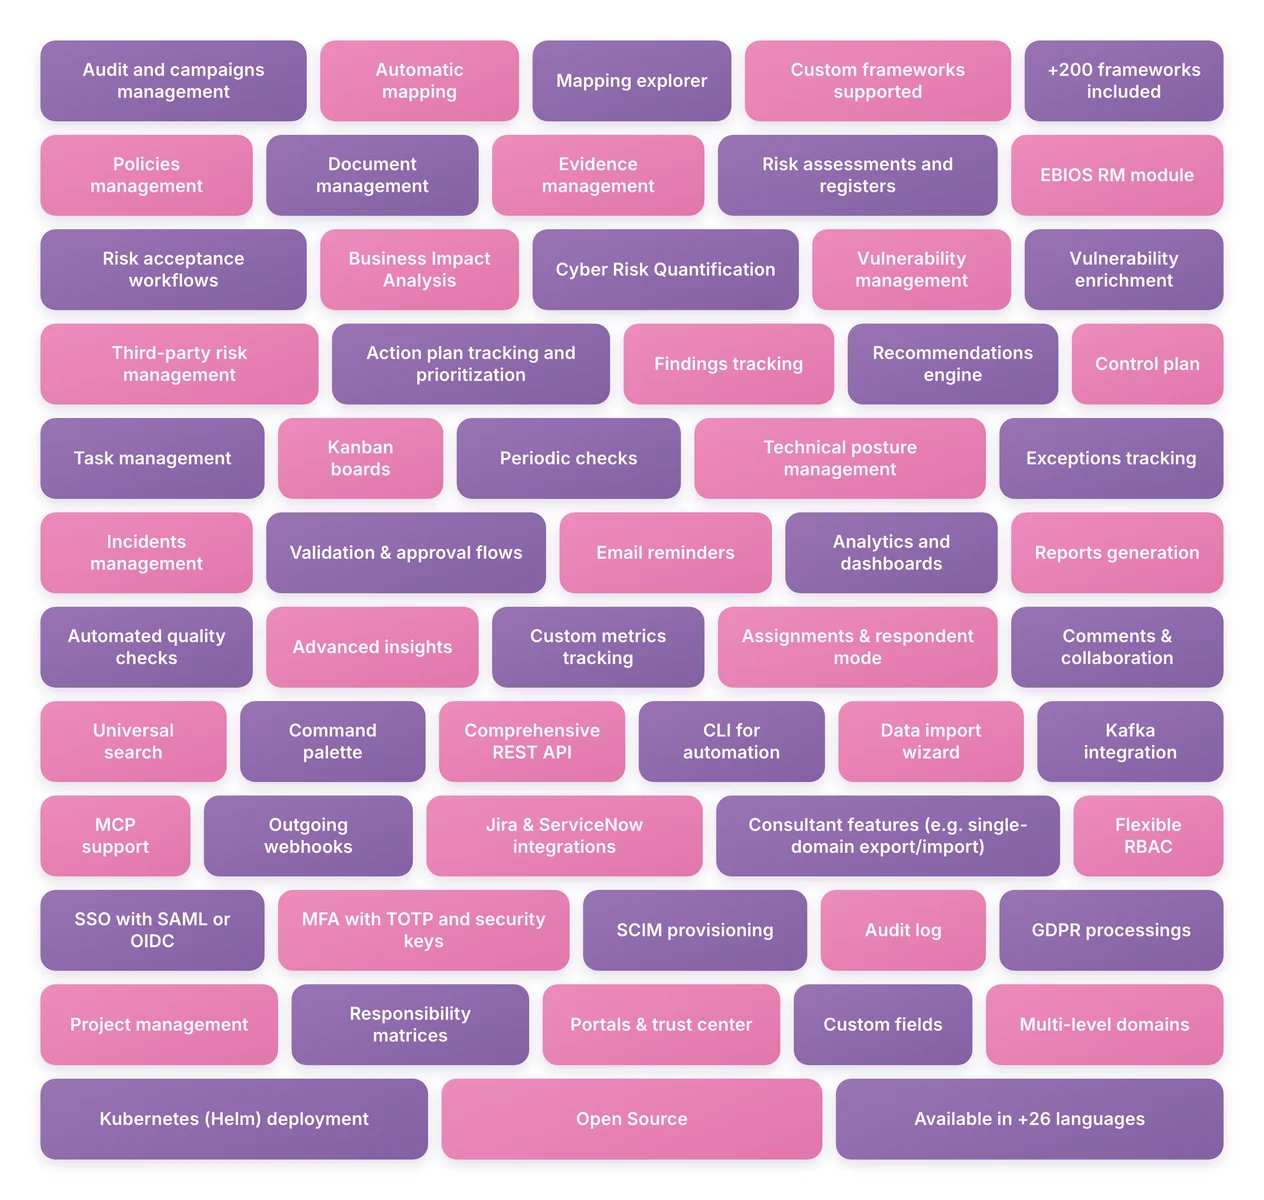
Current features

📋 Full feature list — click to expand (searchable, 73 features)

Compliance & frameworks

  • Audit and campaigns management
  • Automatic mapping
  • Mapping explorer
  • Custom frameworks supported
  • 200+ frameworks included
  • Policies management
  • Document management
  • Evidence management

Risk management

  • Risk assessments and registers
  • EBIOS RM module
  • Threat modeling
  • Risk acceptance workflows
  • Business Impact Analysis
  • Cyber Risk Quantification
  • Risk trajectory & projection
  • Vulnerability management
  • Vulnerability enrichment
  • Security advisories & CWE
  • TTP catalogs

Third-party risk

  • Third-party risk management
  • Contracts management
  • DORA register of information
  • External security ratings
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →