
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-40449 — Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and shellcode injection to achieve SYSTEM privileges. | Kitploit
Tools/GitHubGitHub/hakivvi/cve-2021-40449
Privilege EscalationMemory ForensicsVulnerability AnalysisExploitationShellcodePayload DevelopmentBinary Exploitation
GitHubhakivvi/cve-2021-40449

CVE-2021-40449

Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and shellcode injection to achieve SYSTEM privileges.

View Repository
4815315 years agoReviewed by Kitploit
Share

CVE-2021-40449

My exploit for CVE-2021-40449, a Windows LPE via a UAF in win32kfull!GreResetDCInternal.

short wu

along with the UAF vulnerabilty other primitives are being used to make this exploit possible:

  • leaking the exploit's access token address in ring0 via NtQuerySystemInformation() function with the SystemHandleInformation parameter.
  • using rtlSetAllBits() as a gadget to overwrite the exploit's access_token.privileges with 0xFFs.
  • leaking rtlSetAllBits() address on ring0 by leaking the base address of ntoskrnl.exe module via EnumDeviceDrivers() function.
  • crafting the gadget's parameter BitMapHeader in such a way that will allow us to overwrite the access_token.privileges of the exploit.
  • allocating the crafted BitMapHeader via NtSetInformationThread() primitive and leaking the allocation address in the big pool via NtQuerySystemInformation() function with SystemBigPoolInformation parameter.
  • to interact with the vulnerable function we first enum printers on the system via EnumPrinters() load the driver of one of them one of them then hook the calls to the usermode callback function DrvEnablePDEV().
  • in the hook we proxy the call to the original DrvEnablePDEV() function, do the exploit stuff then return whats returned from the proxied call to the GDI.
  • triggering the UAF via a second call to ResetDC() in the hooked DrvEnablePDEV().
  • reclaim the freed PDC object via spraying a crafted object of the same size using the CreatePalette() primitive.
  • abusing the new aquired SeDebugPrivilege privilege to get NT AUTHORITY\SYSTEM via injecting shellcode to winlogon.exe process.

More information can be found on this article by Kaspersky.
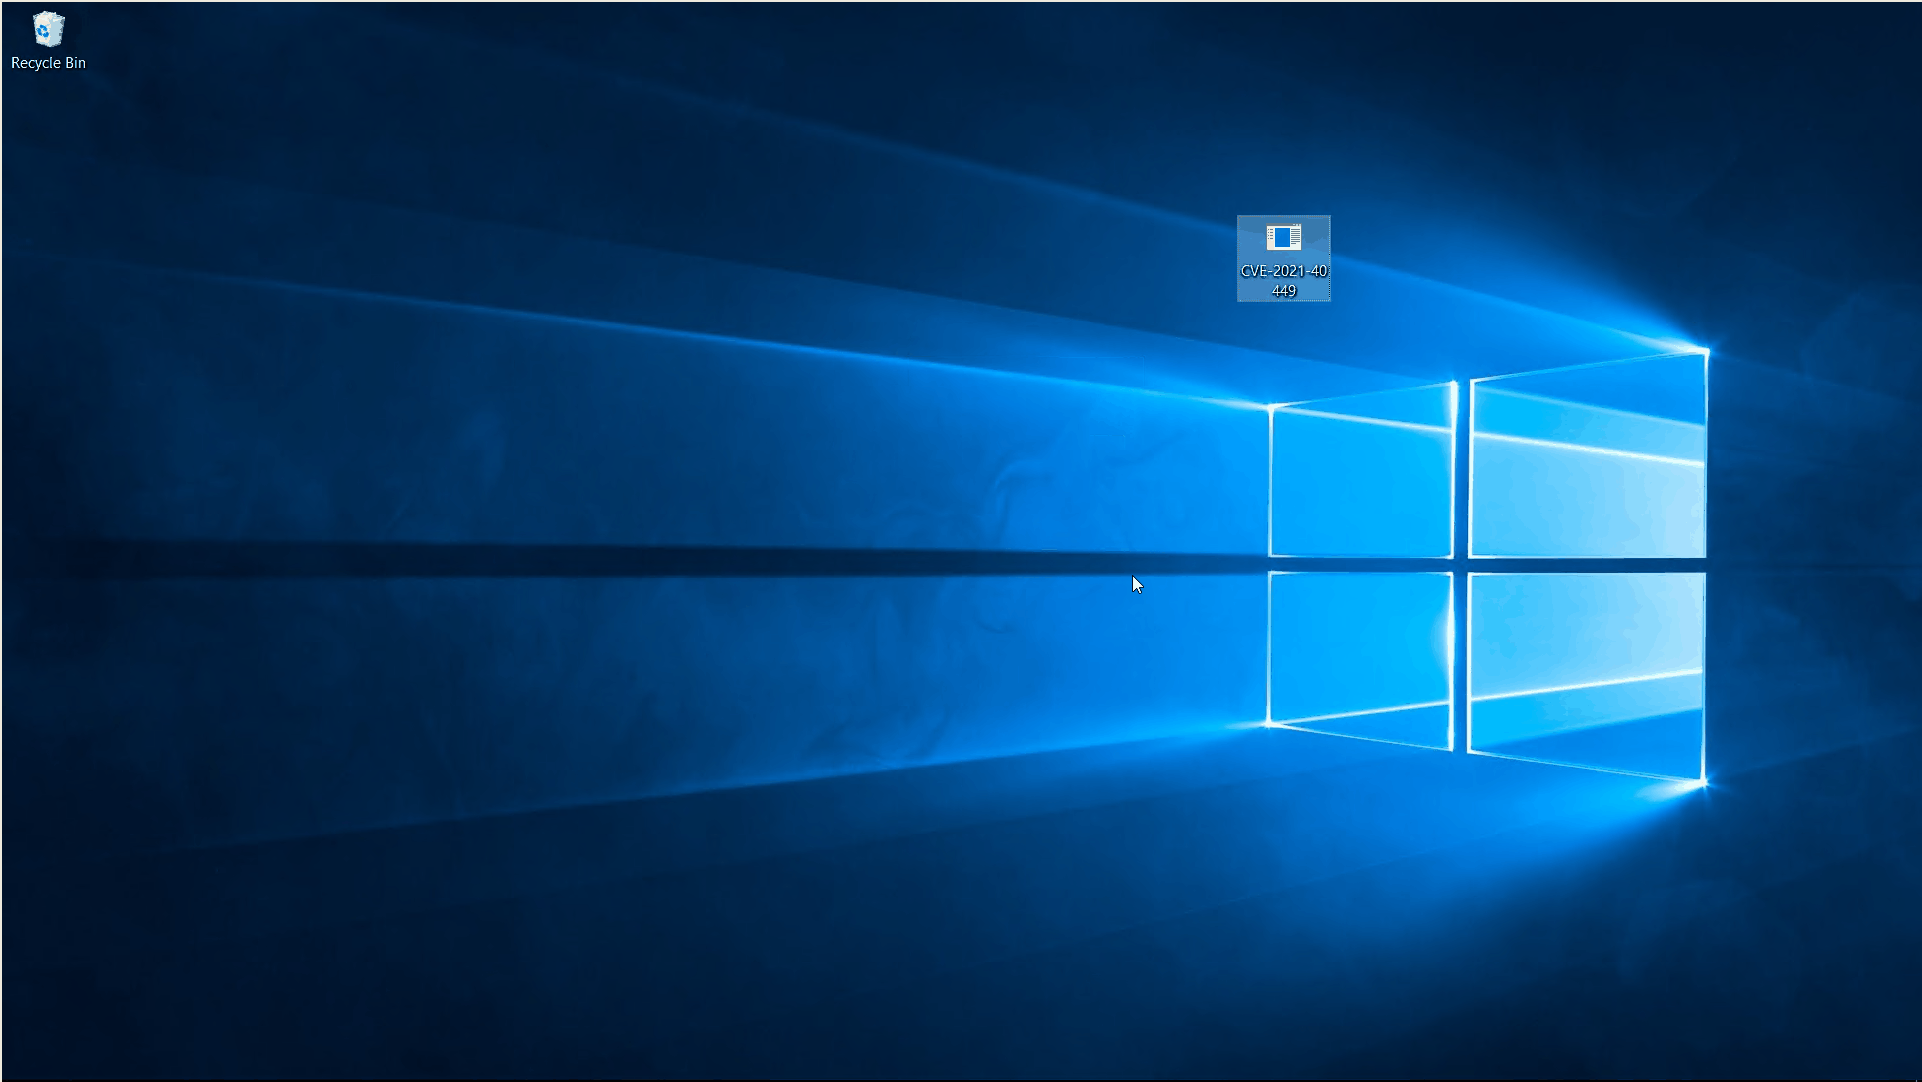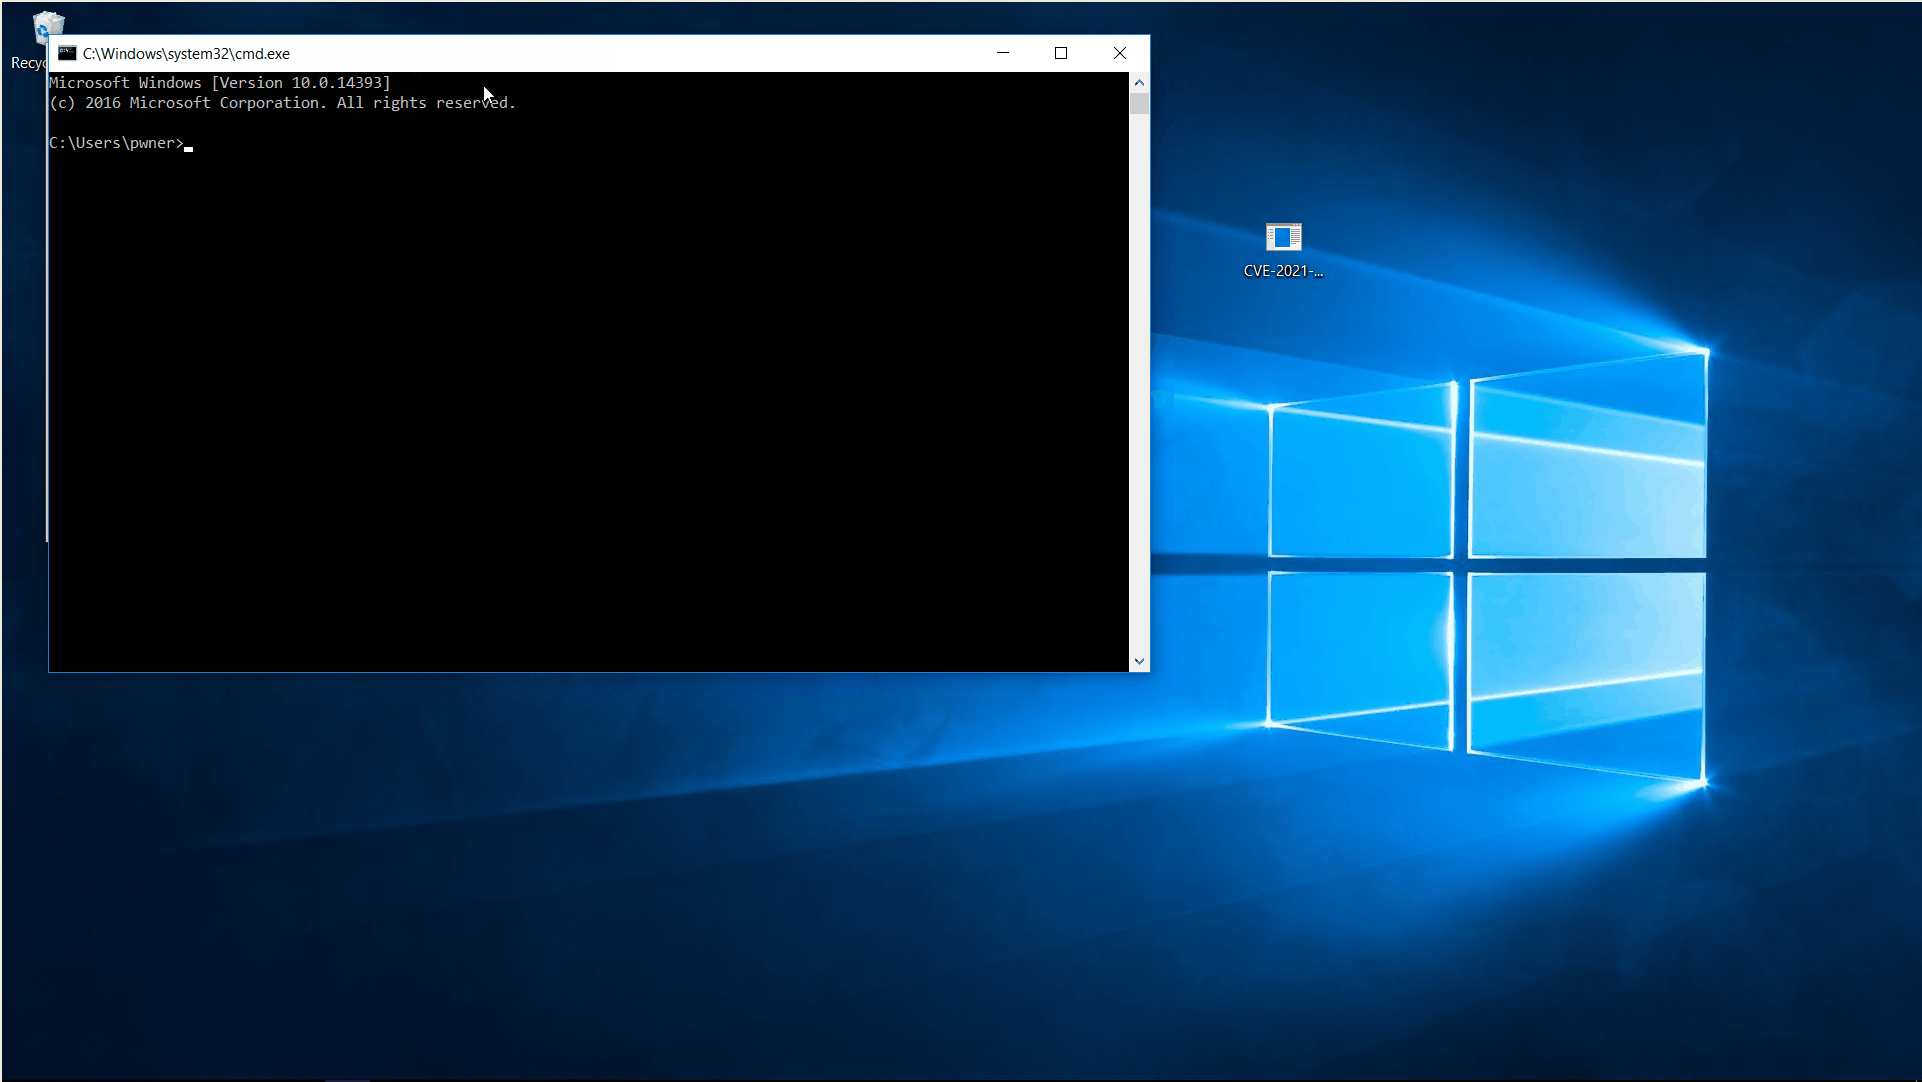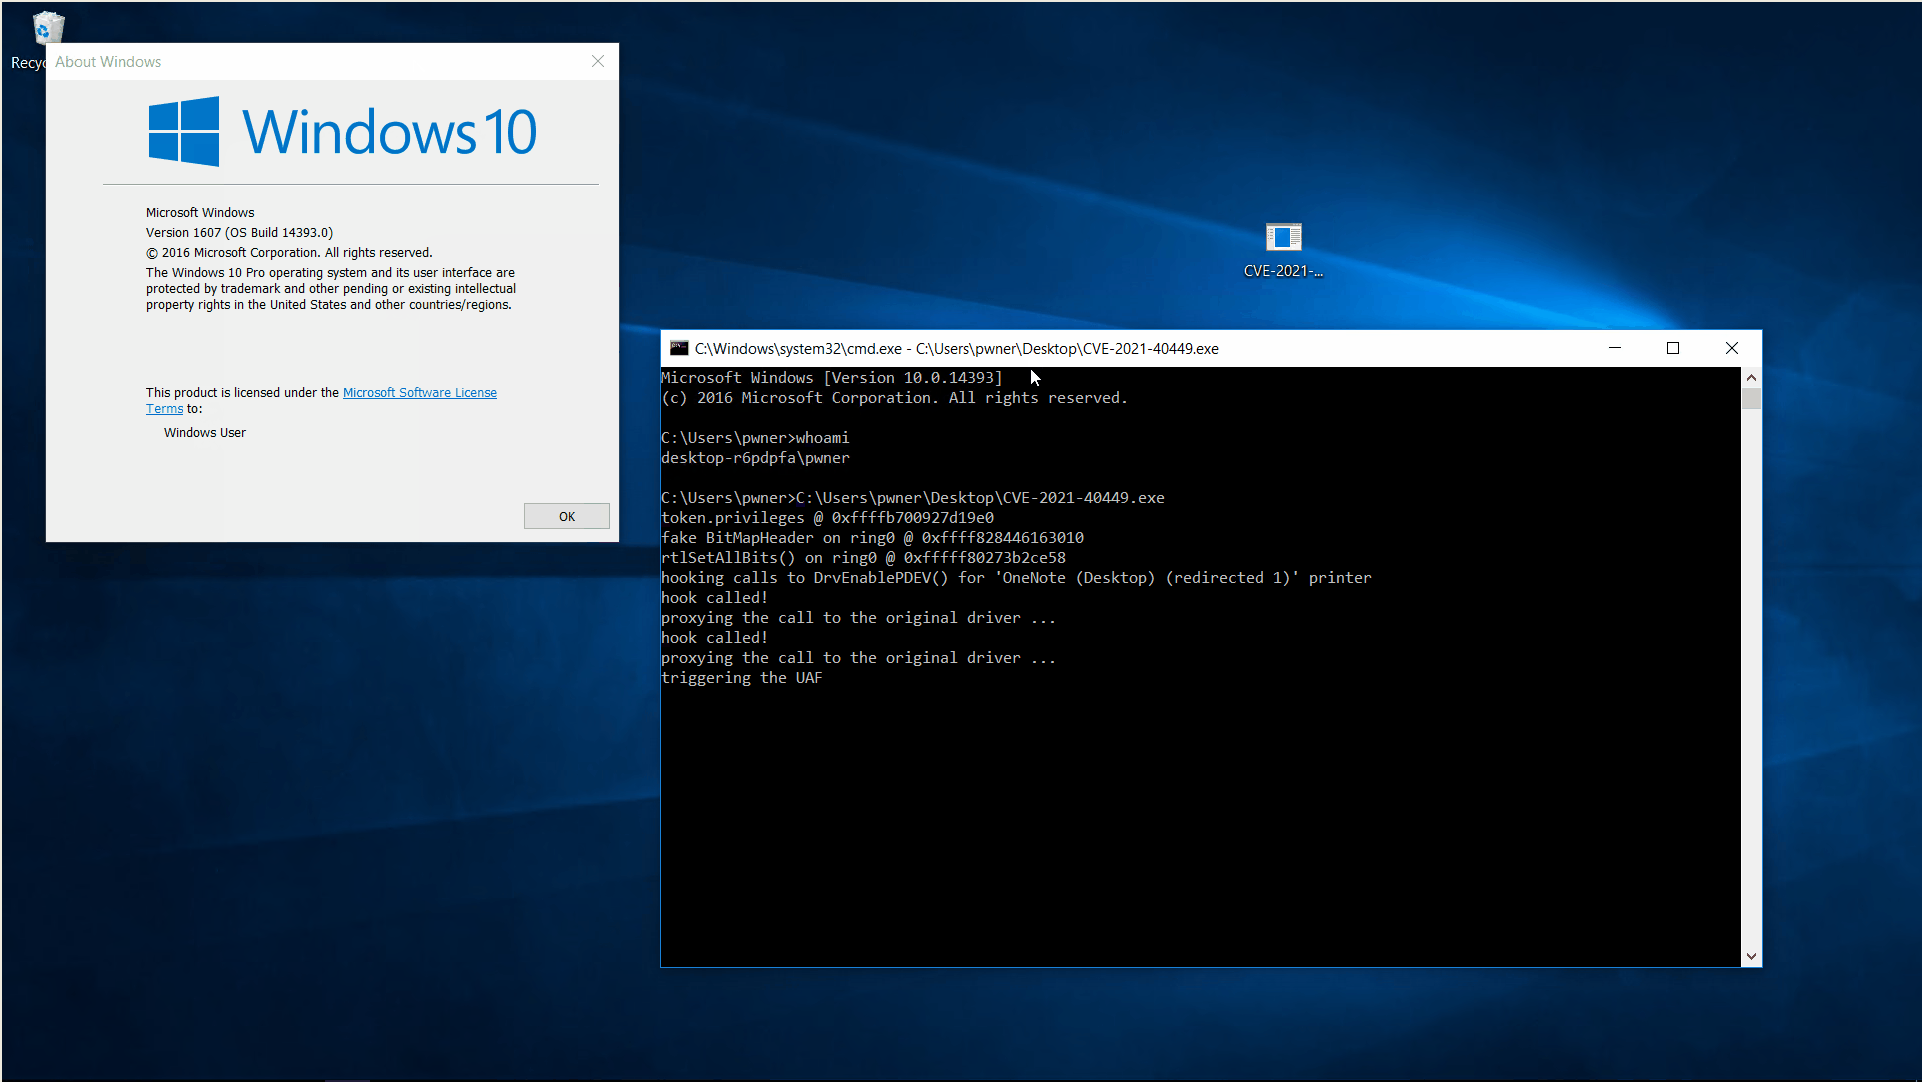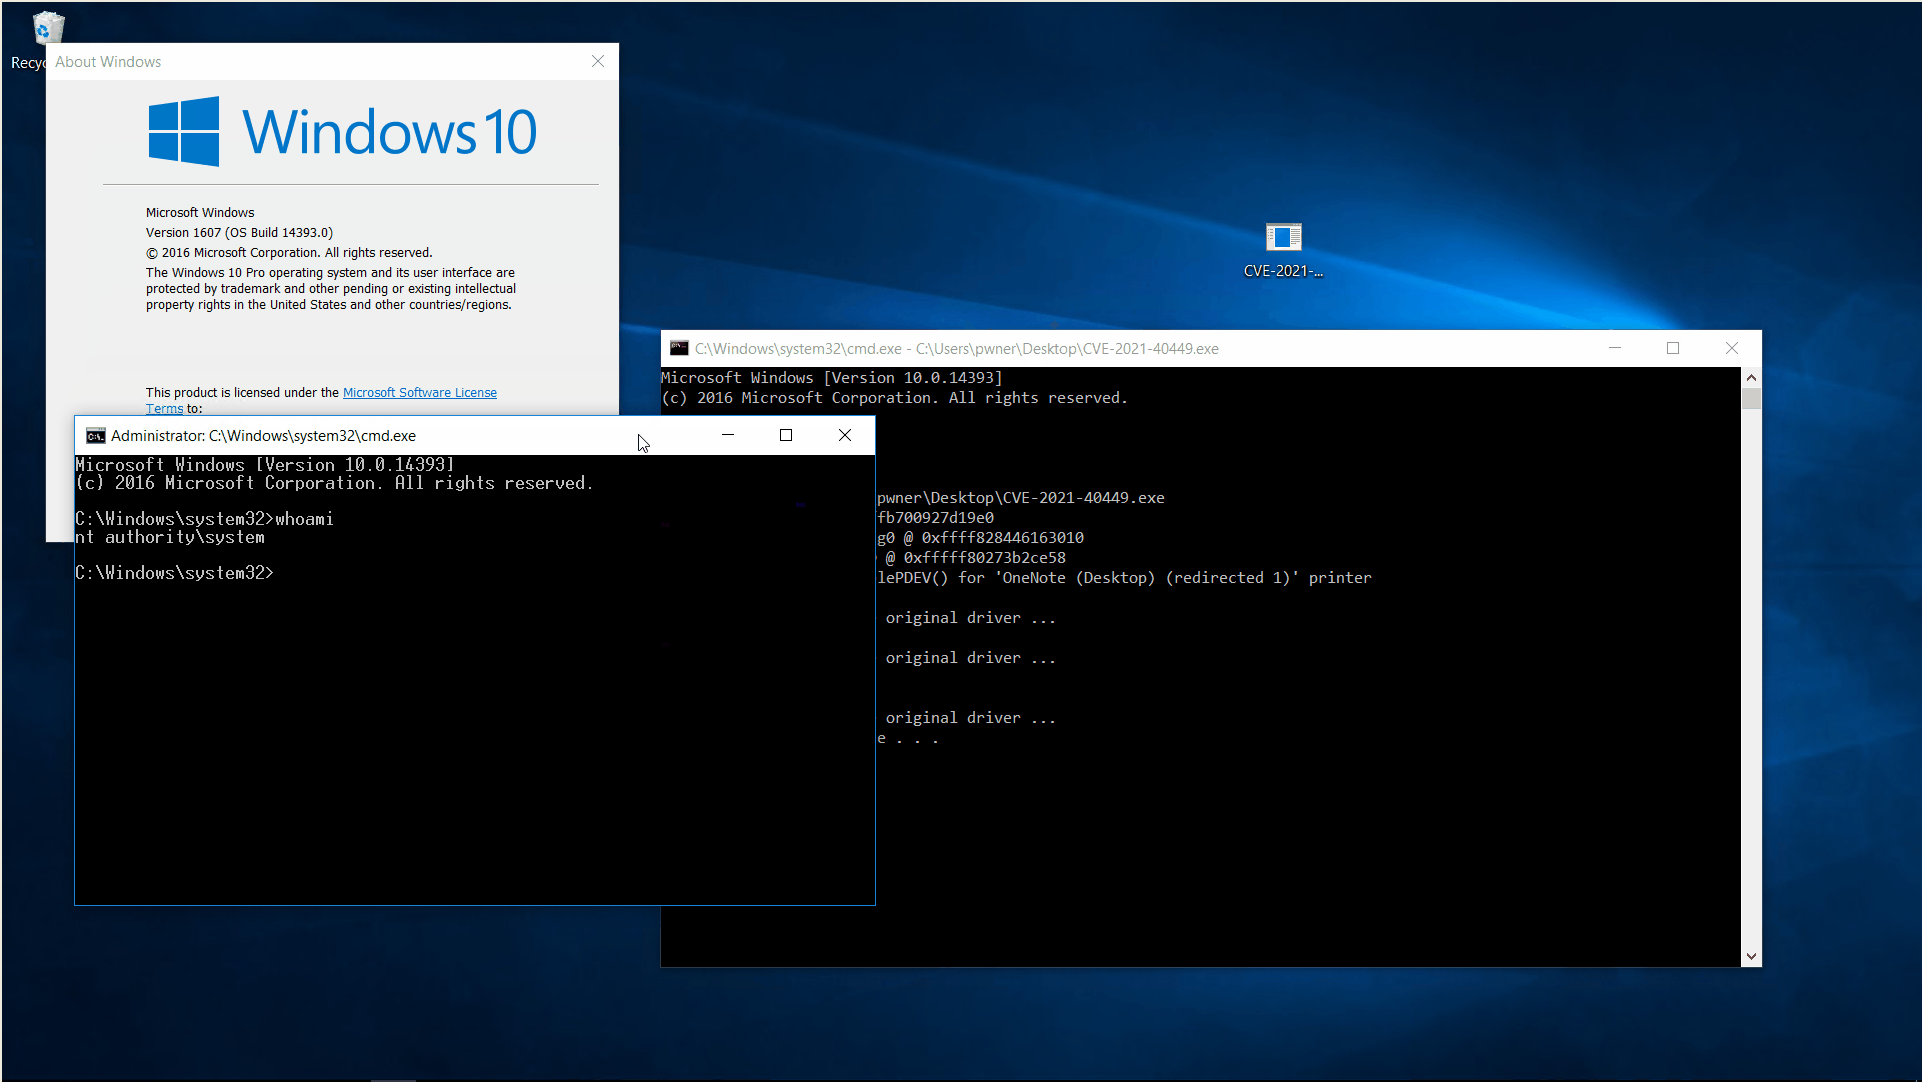
PoC

PoC tested on Win10 Redstone (build 14393).

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →





