g0thamrabb1t/cve-2026-48907-joomla-jce-detection
Defensive lab validation and SOC detection guidance for CVE-2026-48907 in Joomla JCE <= 2.9.99.4, including Apache/Joomla/auditd telemetry, webshell artifacts, Sigma rules, MITRE ATT&CK mapping and mitigation recommendations.

Defensive validation report and SOC-oriented detection notes for CVE-2026-48907 affecting Joomla Content Editor (JCE) versions up to 2.9.99.4.
This repository documents a controlled laboratory validation of CVE-2026-48907 in Joomla JCE and focuses on practical detection engineering for SOC teams.
The goal is not to provide exploitation guidance. The goal is to show which telemetry sources were useful during validation, which artifacts were created, and how defenders can detect and respond to this activity.
| Area | Finding |
|---|---|
| Vulnerability | CVE-2026-48907 in Joomla Content Editor (JCE); unauthenticated profile creation/import workflow that may lead to PHP upload and code execution. |
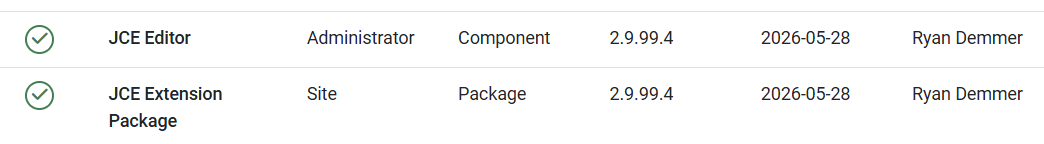
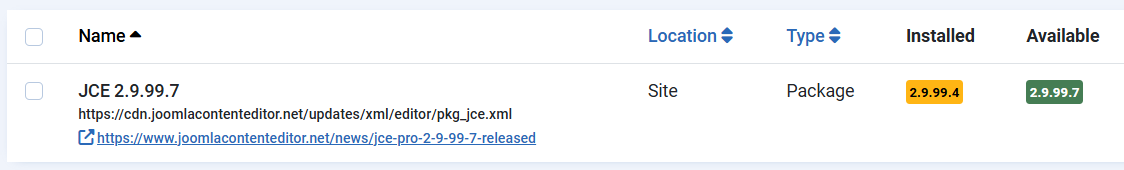
| Tested version | JCE 2.9.99.4. The Joomla administrator panel showed an available update to 2.9.99.7. |
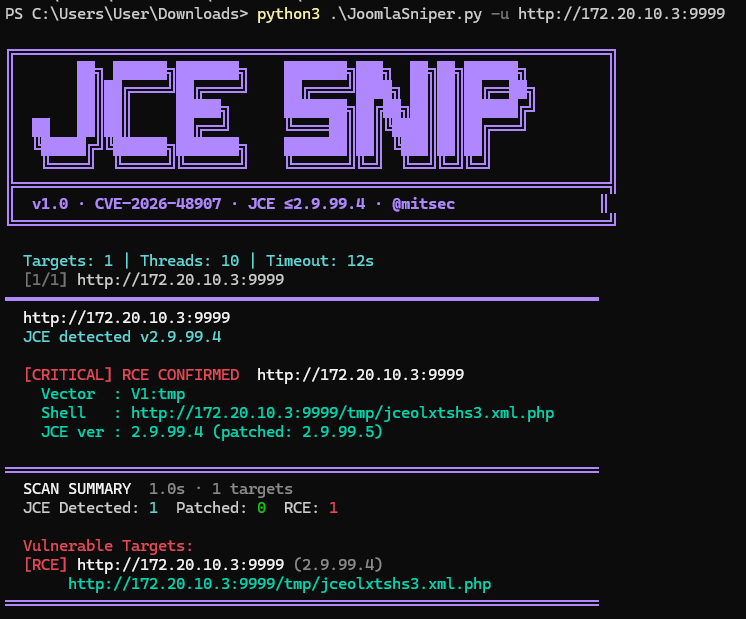
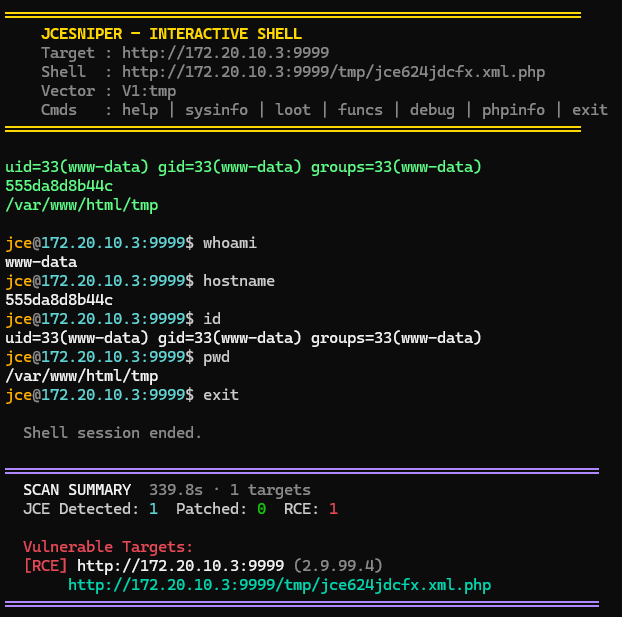
| Lab result | Public PoC validation confirmed RCE and created a PHP webshell in Joomla /tmp as jce*.xml.php. Commands were executed as www-data. |
| Most valuable telemetry | Apache access.log, Apache/PHP error.log, auditd execve telemetry and filesystem artifacts in joomla_html/tmp. |
| Joomla logs | Useful as supporting context, but insufficient on their own. Joomla application logs did not reconstruct the full chain: exploit → webshell → command execution. |
| SOC priority | Critical for internet-facing Joomla instances or Joomla instances reachable from less trusted internal networks. |
| Parameter | Value |
|---|---|
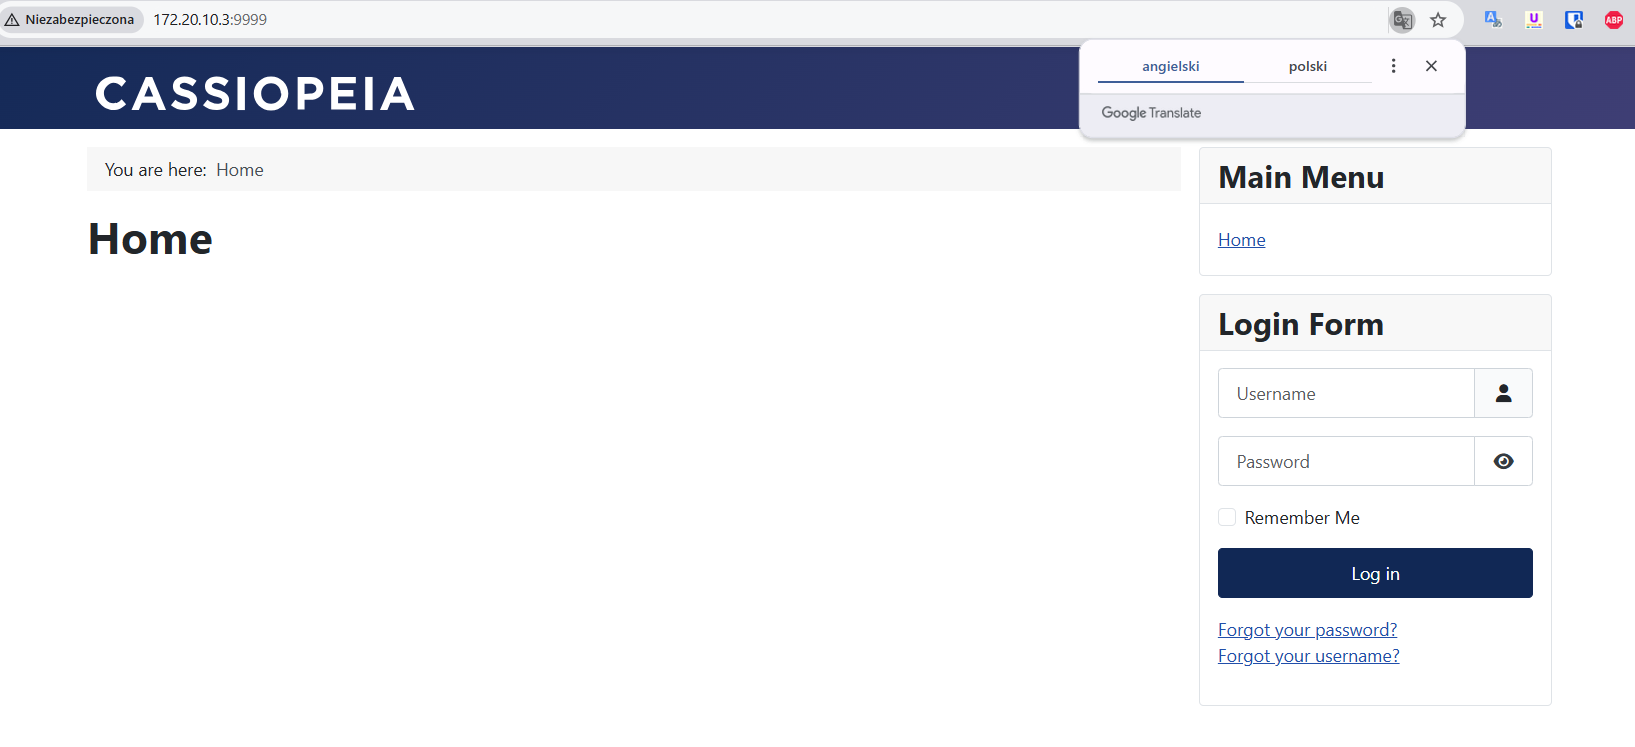
| Application URL | http://172.20.10.3:9999 |
| Joomla container | joomla-jce-lab, image joomla:5-apache |
| Database container | joomla-jce-db, image mariadb:11 |
| Port mapping | 0.0.0.0:9999 -> 80/tcp |
| Apache | Apache/2.4.67 (Debian) |
| PHP | PHP 8.3.31 |
| MariaDB | 11.8.8-MariaDB |
| Joomla | Joomla 5.4.6 Stable |
| JCE | 2.9.99.4 |
| Test source | Windows 11, IP 172.20.10.2 |
| Logging | Apache access/error logs, Joomla logs, auditd, Docker logs, filesystem artifacts |
A key operational finding is that Joomla application logs were not enough.
During the lab test, Joomla logs recorded application-level context such as a joomlafailure event, but they did not show the full exploitation chain. The useful chain was visible mainly in:
access.logerror.logexecve recordsjoomla_html/tmpFor SOC monitoring, Joomla logs should be treated as supporting telemetry, not as the primary detection source for this vulnerability.
High-level chain observed during the controlled test:
JCE version discovery
    ↓
POST to Joomla JCE component
    ↓
PHP webshell written to Joomla /tmp
    ↓
HTTP request to /tmp/jce*.xml.php
    ↓
Command execution through webshell
    ↓
auditd confirms /usr/bin/dash and commands executed as www-data
The clearest evidence was present in Apache access.log:
GET  /plugins/editors/jce/jce.xml
GET  /
POST /index.php?option=com_jce
GET  /tmp/jceolxtshs3.xml.php
GET  /plugins/editors/jce/jce.xml
POST /index.php?option=com_jce
GET  /tmp/jce624jdcfx.xml.php
GET  /tmp/jce624jdcfx.xml.php?c=id%20%26%26%20hostname%20%26%26%20pwd
GET  /tmp/jce624jdcfx.xml.php?c=whoami
GET  /tmp/jce624jdcfx.xml.php?c=hostname
GET  /tmp/jce624jdcfx.xml.php?c=id
GET  /tmp/jce624jdcfx.xml.php?c=pwd
The Apache/PHP error log contained valuable parser-related traces:
simplexml_load_string()
administrator/components/com_jce/helpers/profiles.php
RXST
RXEND
The RXST and RXEND markers were particularly useful indicators for this specific PoC family because they appeared in the payload handling path.
Joomla logs confirmed application logging was active, but they did not reconstruct exploitation:
#Software: Joomla! 5.4.6 Stable [ Kutegemea ] 26-May-2026 16:00 GMT
#Fields: datetime priority clientip category message
2026-06-18T20:37:57+00:00 INFO 172.20.10.2 joomlafailure Username and password do not match or you do not have an account yet.
This means that collecting only Joomla logs may miss the most important evidence of CVE-2026-48907 exploitation.
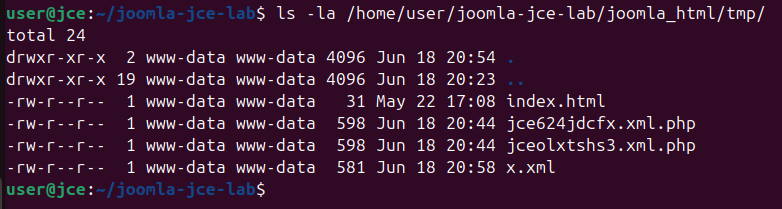
The test created PHP webshell files in Joomla tmp:
/var/www/html/tmp/jce624jdcfx.xml.php
/var/www/html/tmp/jceolxtshs3.xml.php
Host-side paths in the lab:
/home/user/joomla-jce-lab/joomla_html/tmp/jce624jdcfx.xml.php
/home/user/joomla-jce-lab/joomla_html/tmp/jceolxtshs3.xml.php
Observed SHA256 hashes:
b6fa303daef8aa8cb39566c73d2cb4a458efb2b1fba48052dd039d45c3beb0aa  jce624jdcfx.xml.php
f8bcc802ab56b845c968ed6727228f200f8f4bcd332b8ce82c6980d93ac228fd  jceolxtshs3.xml.php
Hash-based detection should be treated as low-resilience because file names and payloads may vary. Path, extension, ownership and behavioral correlation are more useful.
auditd confirmed that the web server user executed commands from the Joomla tmp directory:
CWD=/var/www/html/tmp uid=www-data comm=sh exe=/usr/bin/dash
CWD=/var/www/html/tmp uid=www-data comm=id exe=/usr/bin/id
CWD=/var/www/html/tmp uid=www-data comm=hostname exe=/usr/bin/hostname
CWD=/var/www/html/tmp uid=www-data comm=whoami exe=/usr/bin/whoami
This is the strongest confirmation that the activity was not only scanning, but actual remote code execution.