 cyber-courses/cyber-library
Community-maintained Markdown knowledge base covering cybersecurity foundations, offensive and defensive practice, governance, threat intelligence, OSINT, and career guidance.

Learn cybersecurity, from the foundations up.
A structured, community-maintained knowledge base: six tracks, one tree, from how a network works to how an attacker thinks.



Read the library → · Browse the structure · Connect your assistant
⭐ If the library helps you, star the repo. Stars help other learners find it.
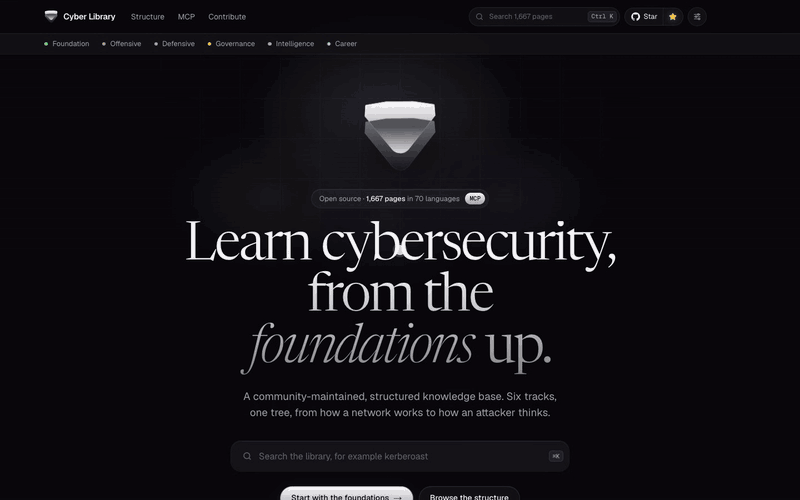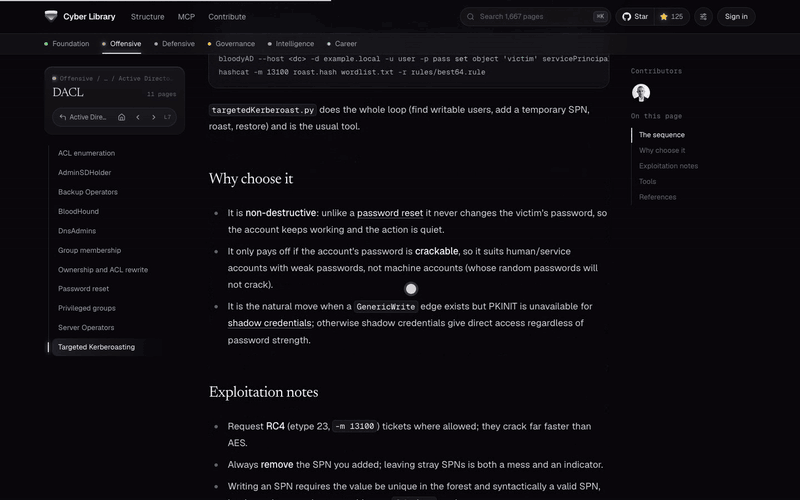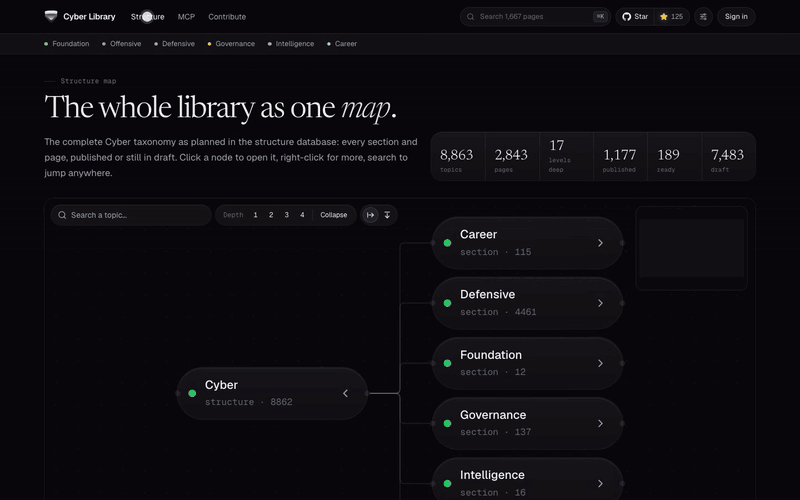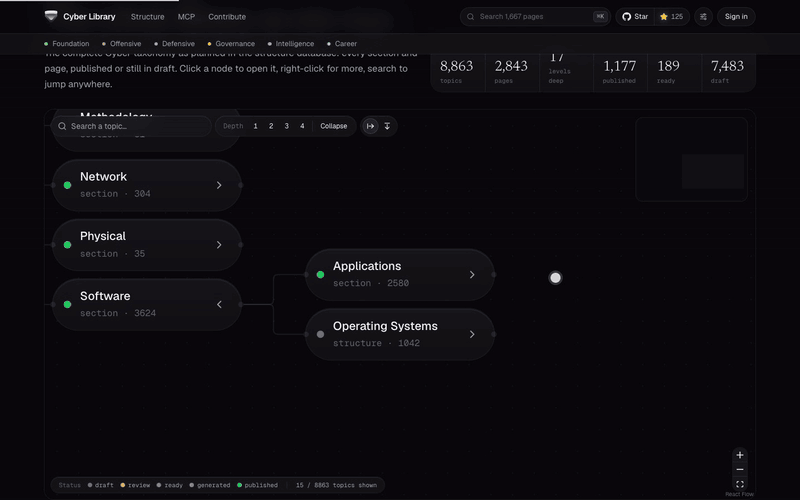
Search with ⌘ K, read an article, move through the tracks and the sidebar, explore the structure map.
Security knowledge is scattered across blog posts, slide decks and tool READMEs. Cyber Library puts it in one tree, so every technique sits next to the ones that share its mental model, with real commands, the mechanism behind them, and links to primary sources.
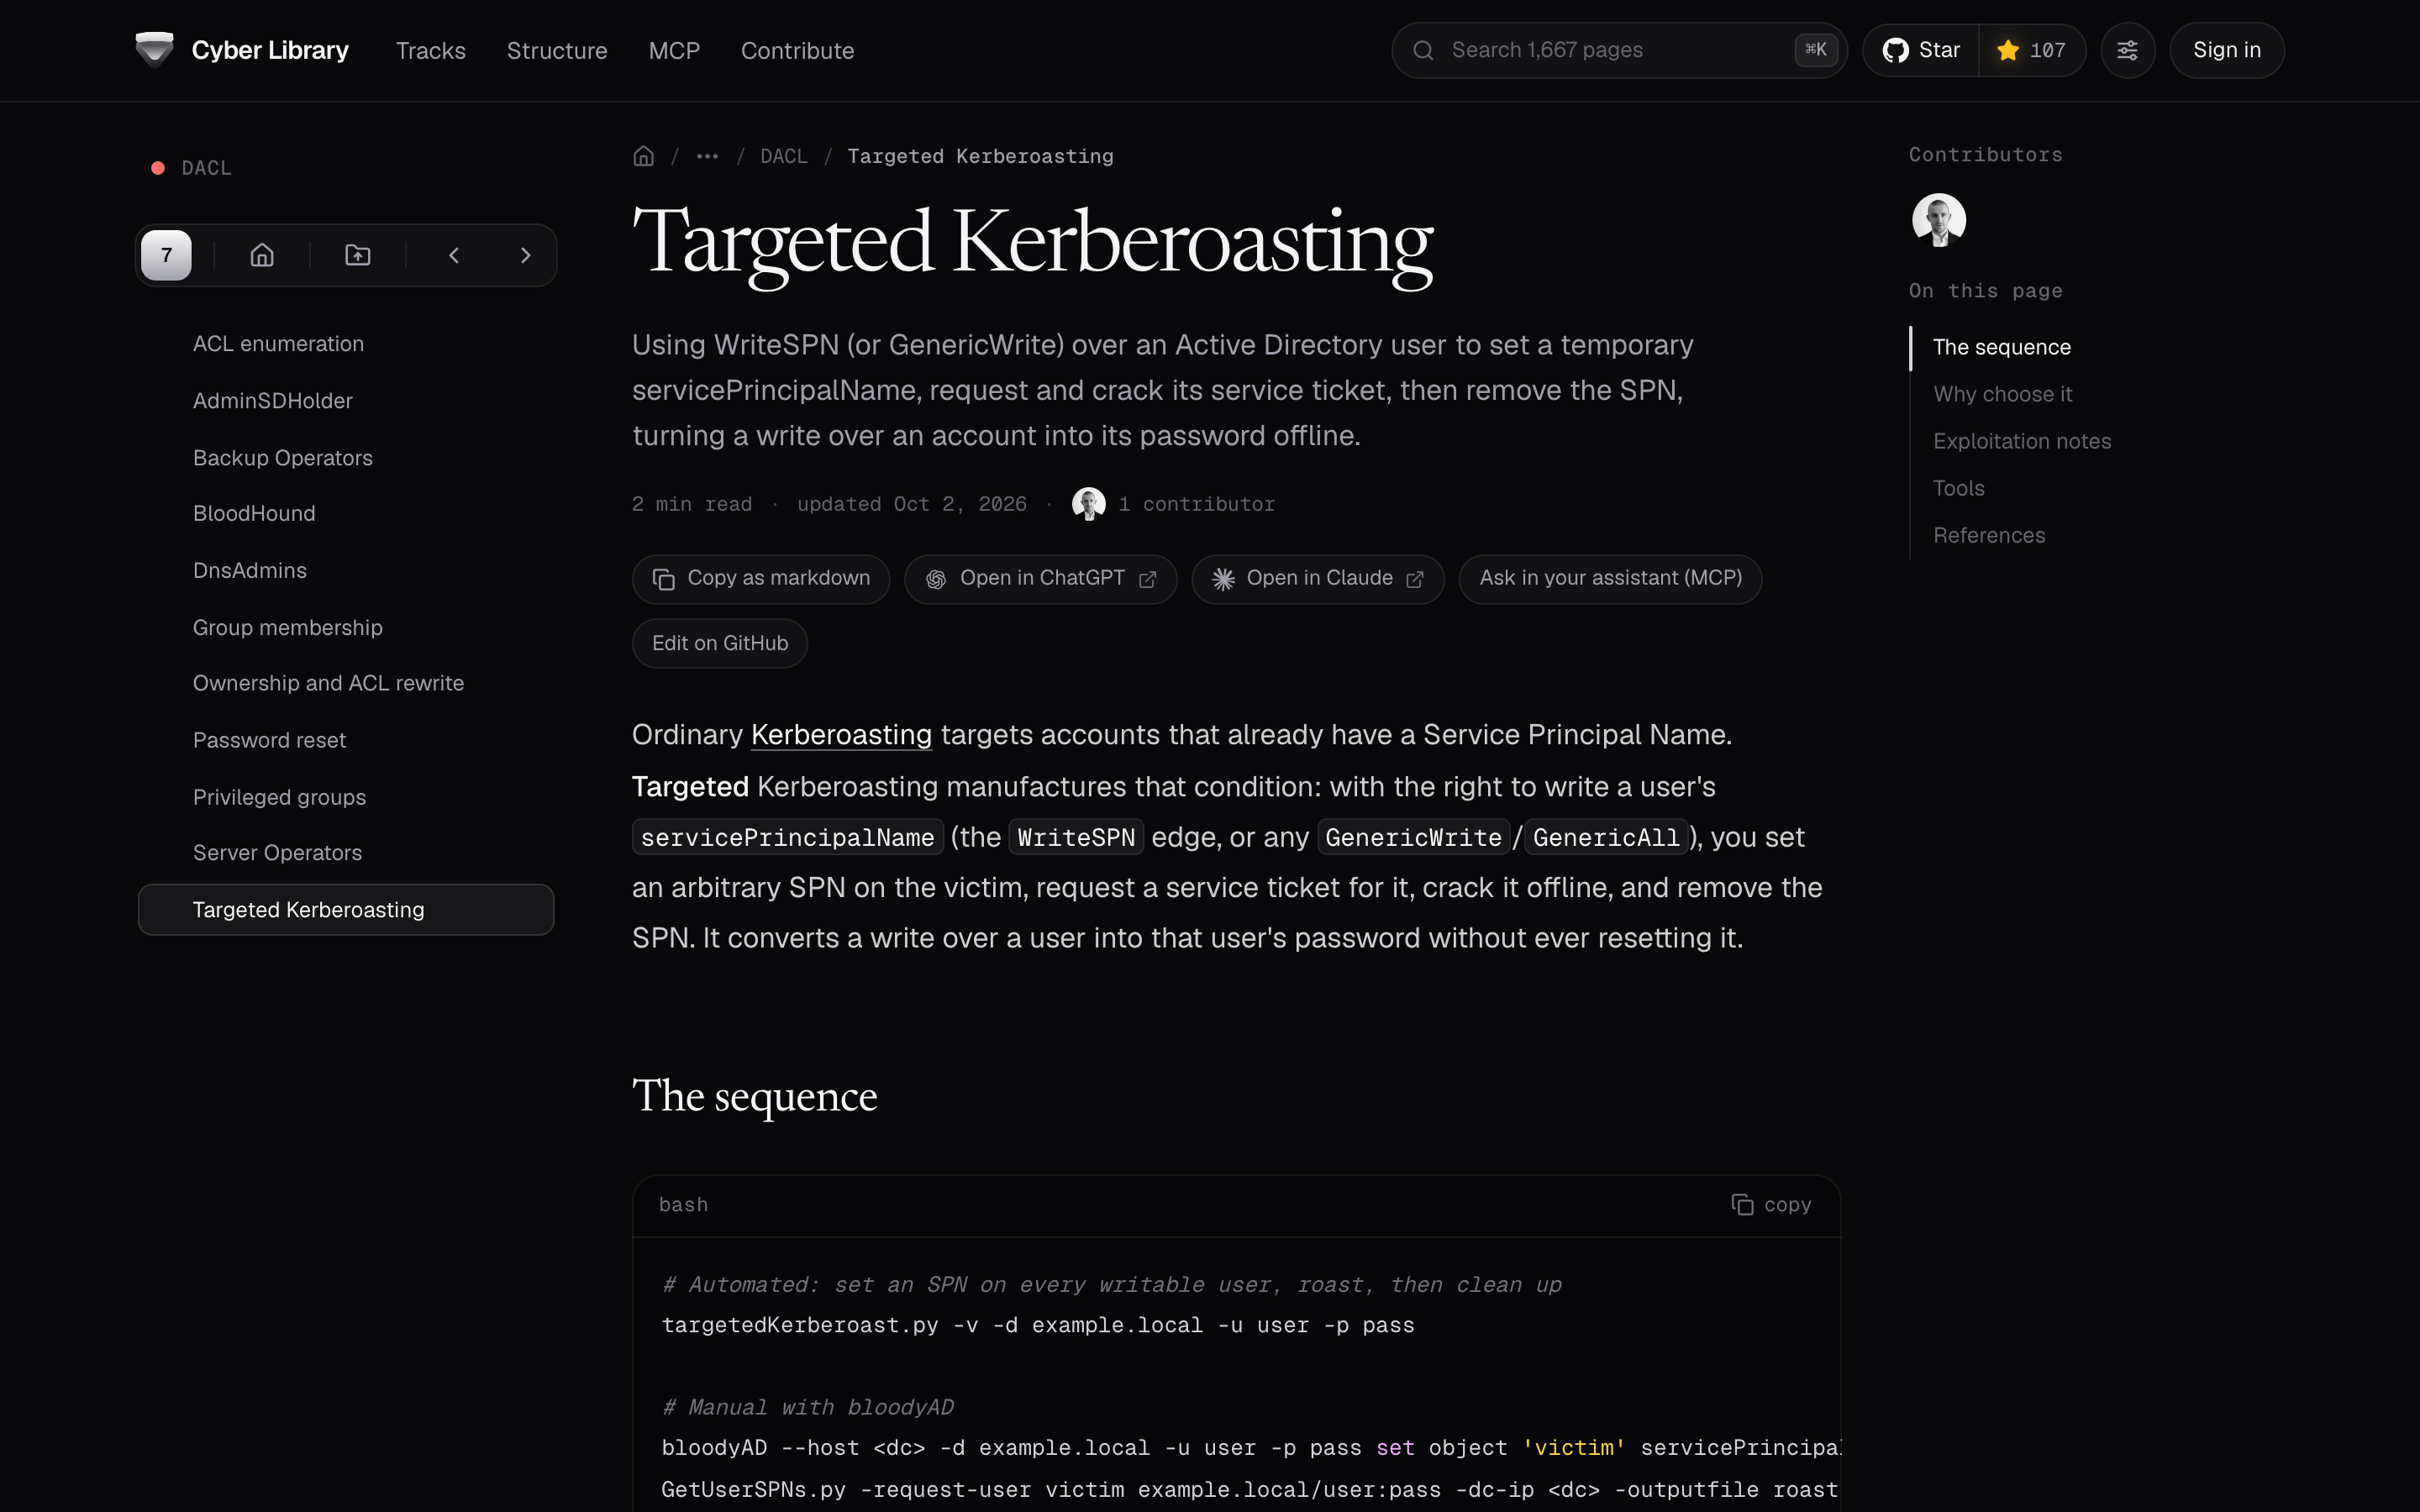
Read Focused articles with runnable commands, a table of contents, and one-click export to Markdown, ChatGPT or Claude. |
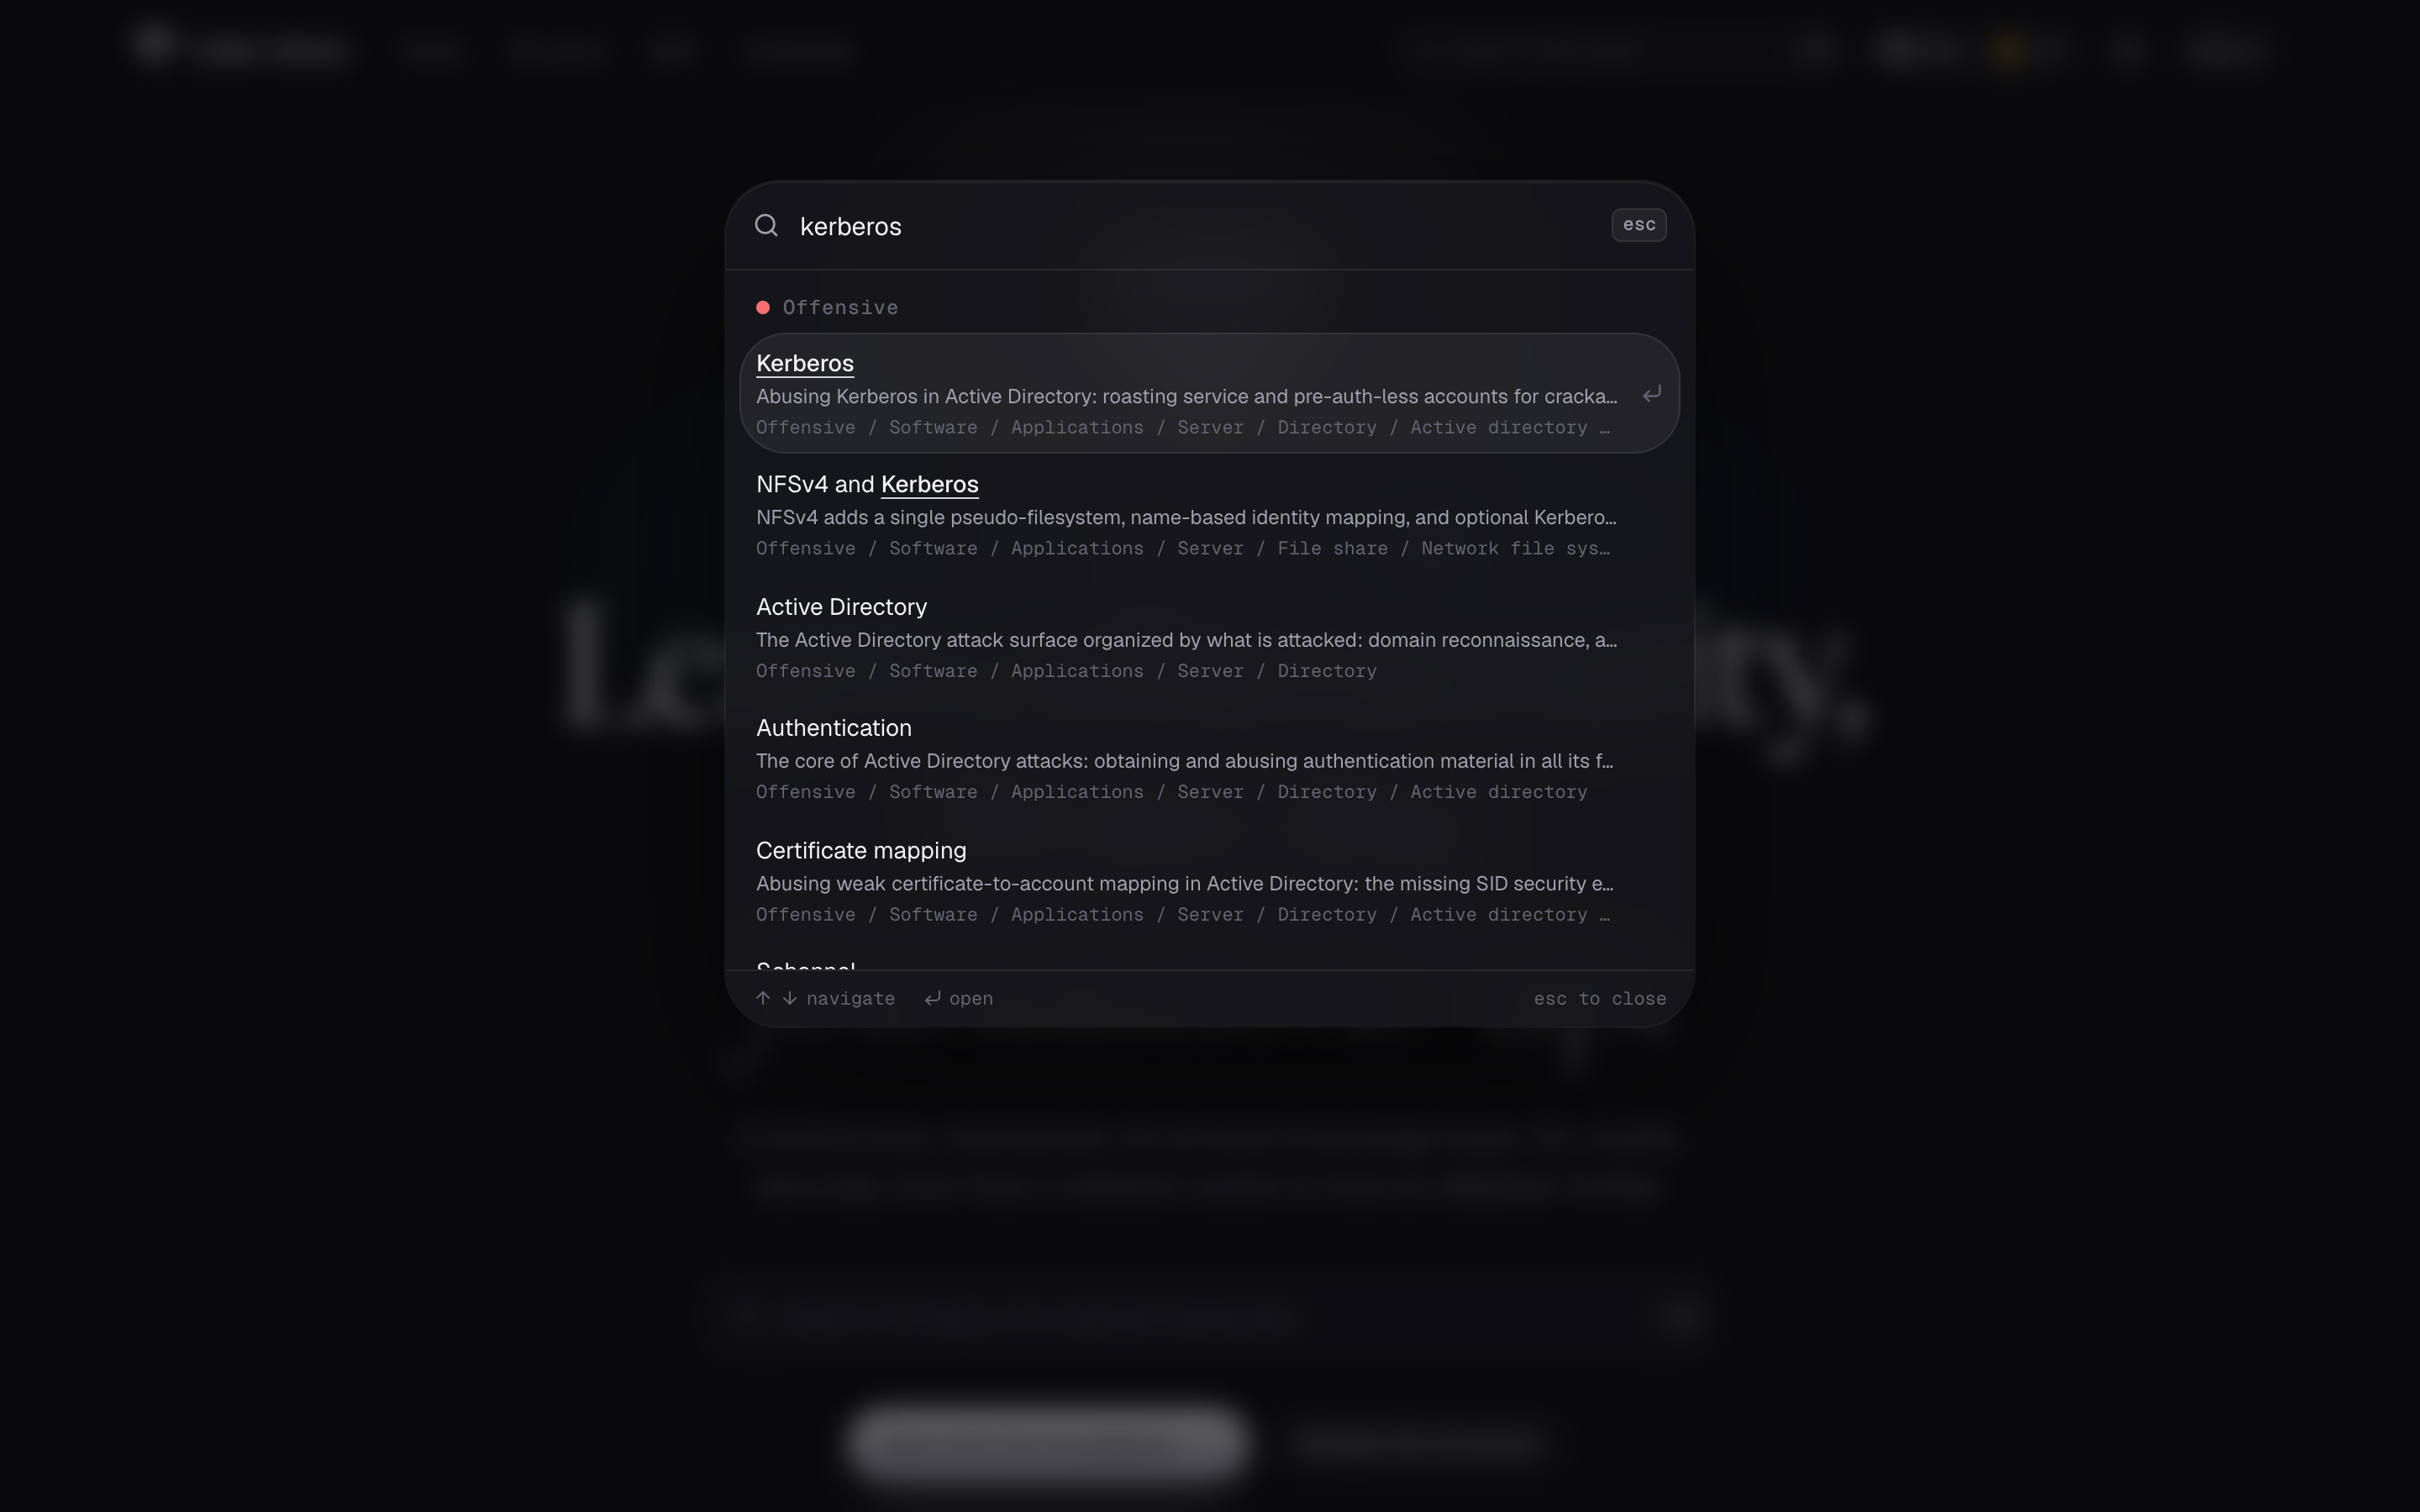
Search Press ⌘ K anywhere to jump to any of the 1,600+ pages, with its place in the tree. |
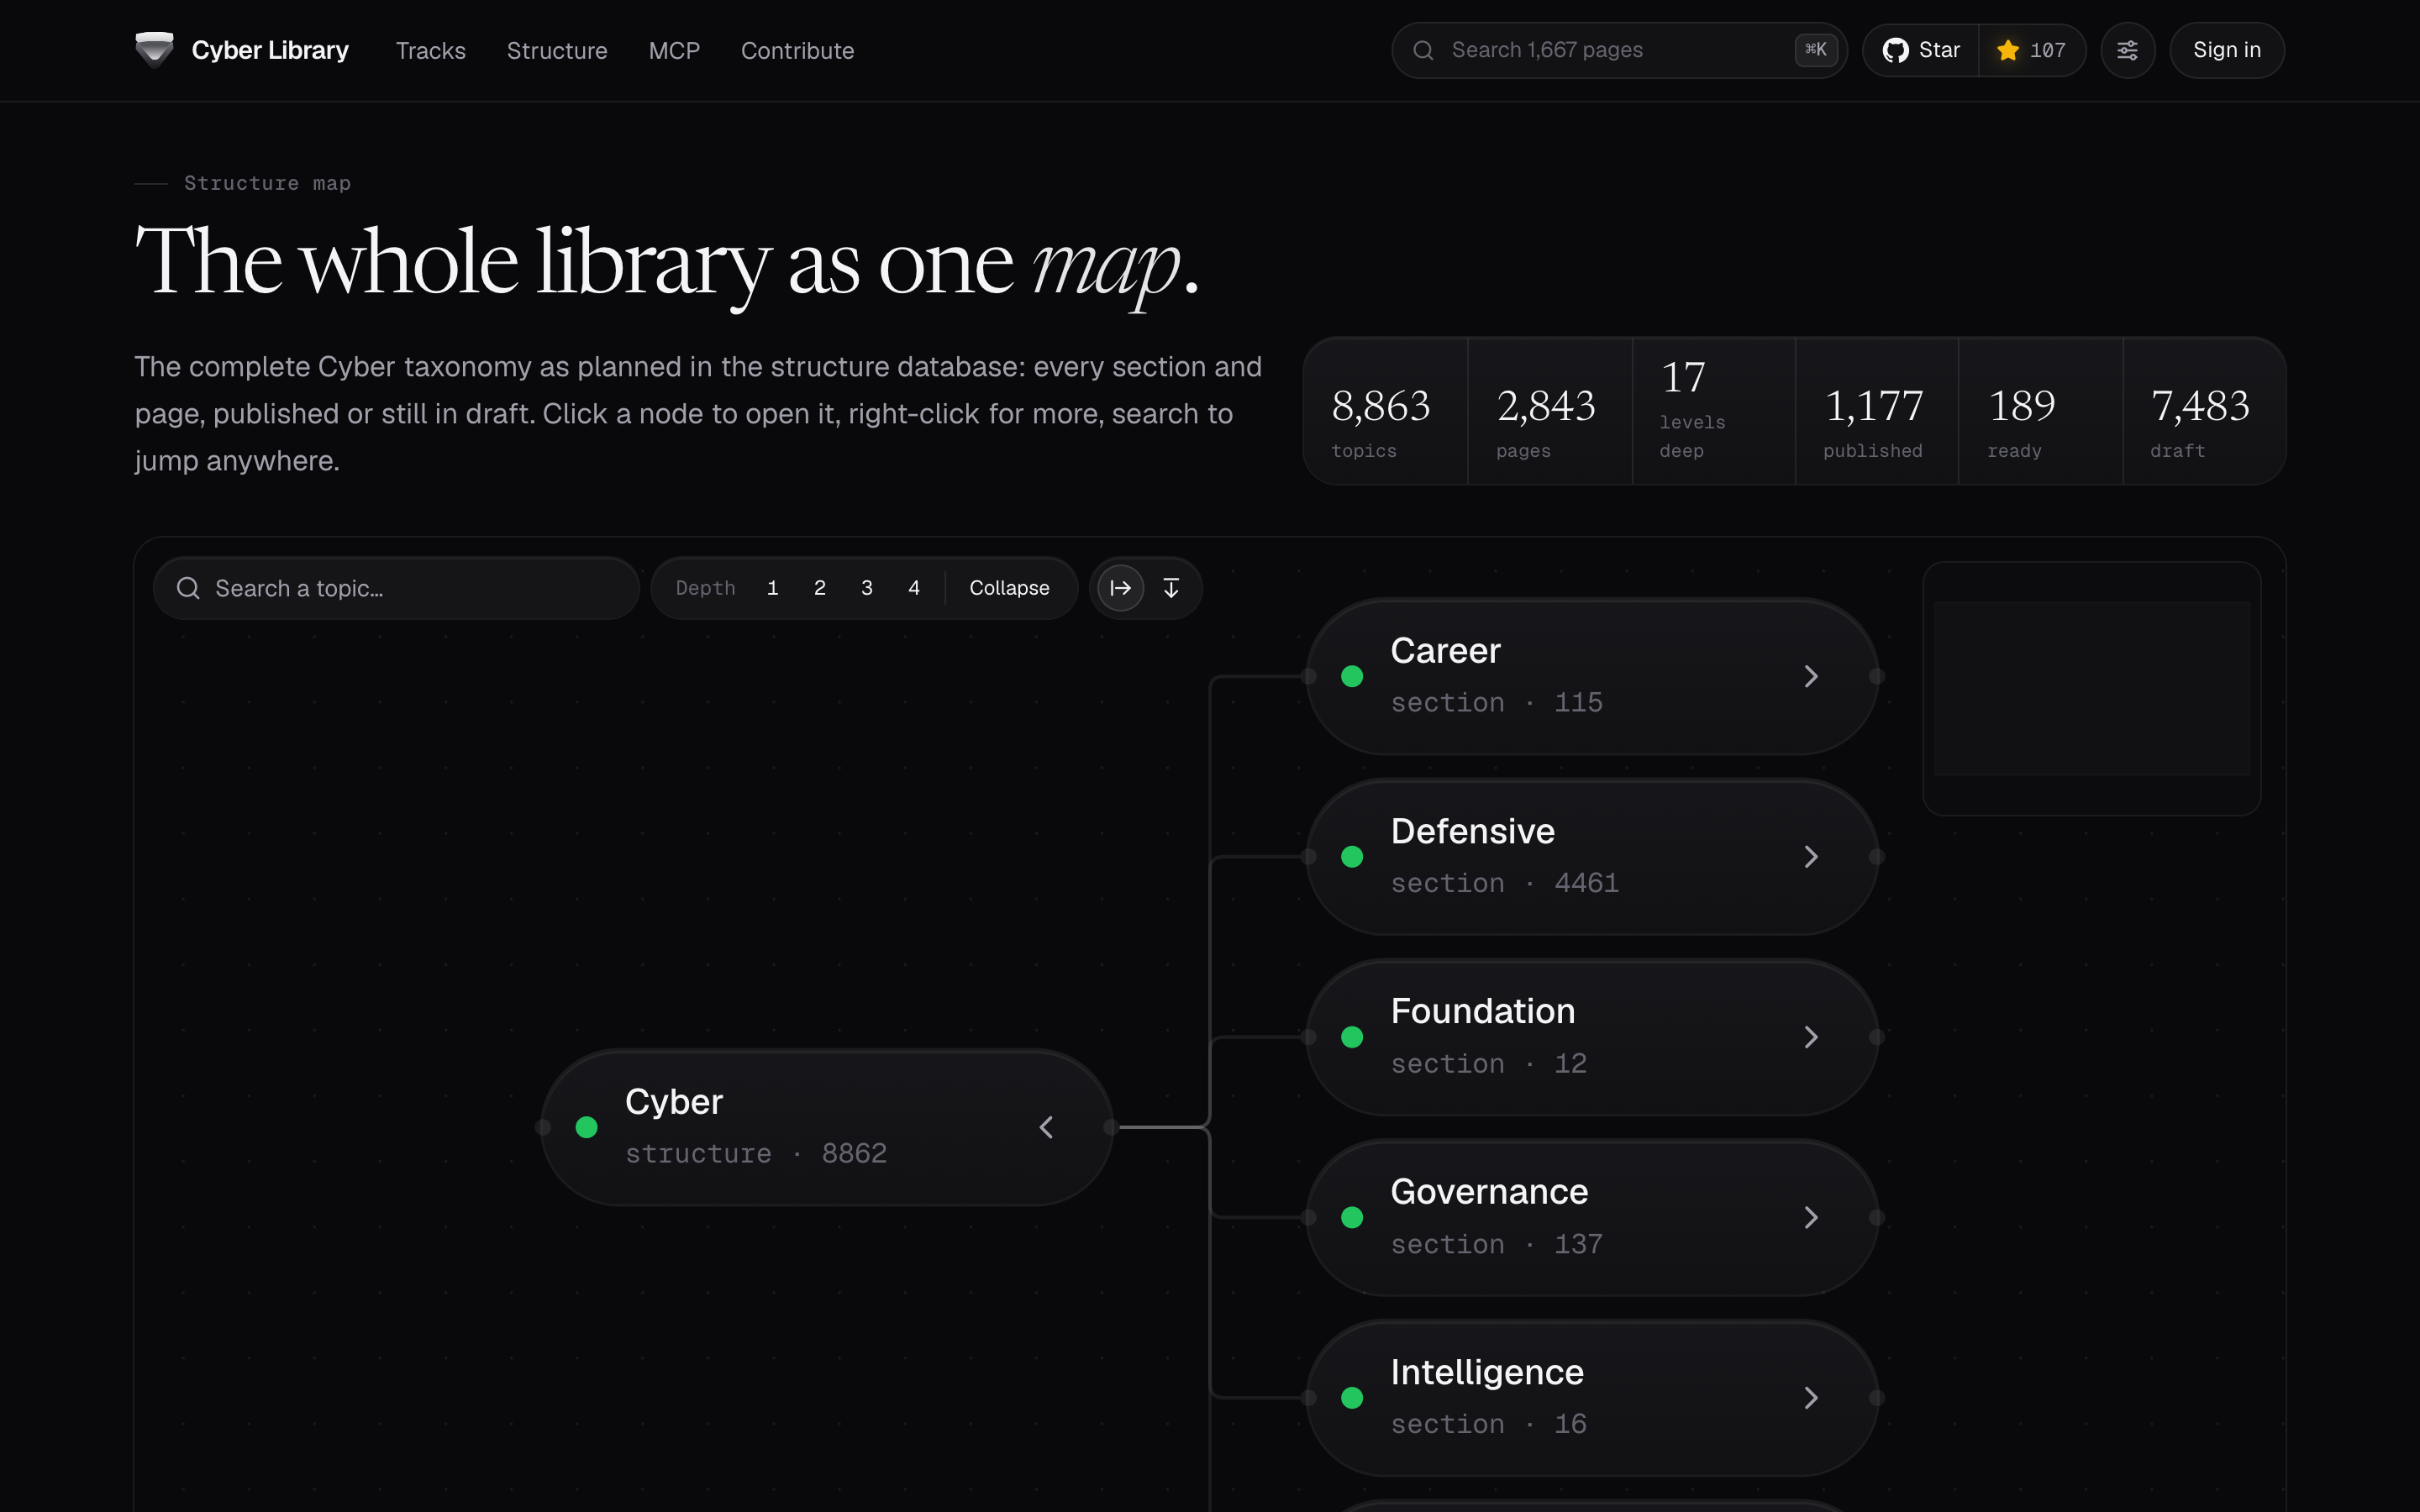
Explore The whole taxonomy as one interactive map: 8,800+ topics, 17 levels deep, published and planned. |
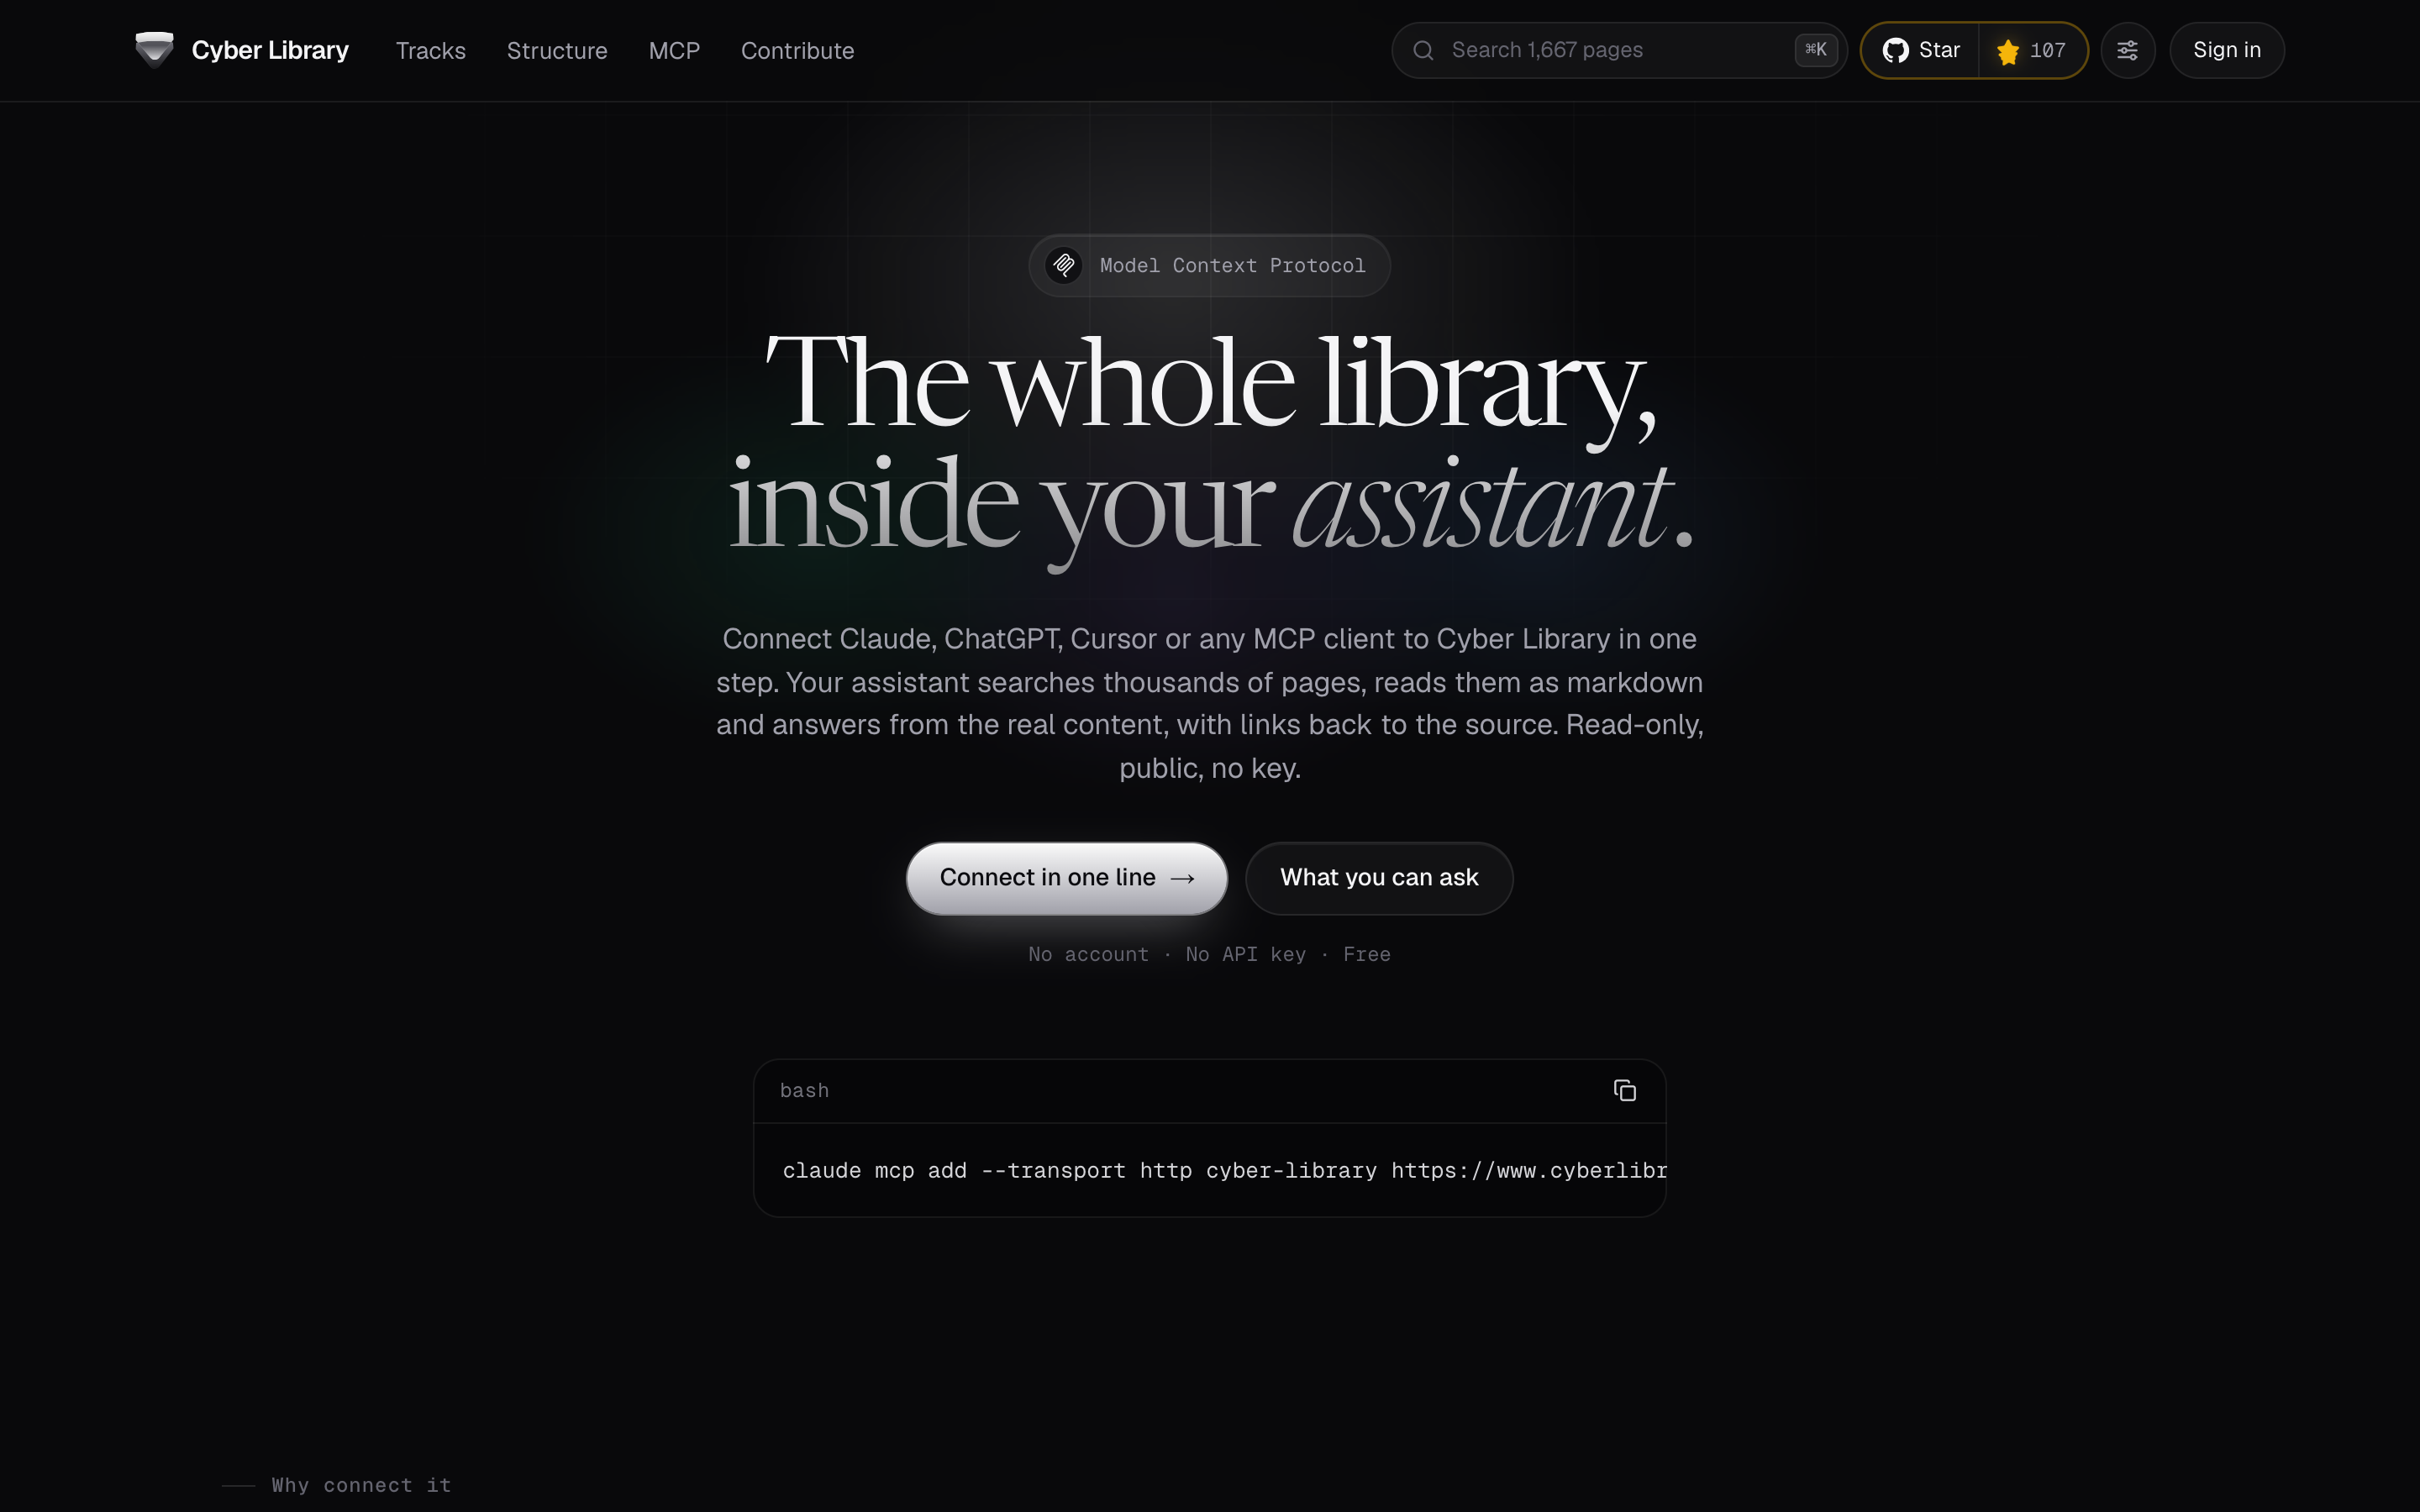
Ask your assistant A public, read-only MCP server: Claude, ChatGPT, Cursor or any MCP client can search and read the library. |
A public, read-only MCP server. No account, no API key, nothing to run.
Claude Code, one line:
claude mcp add --transport http cyber-library https://www.cyberlibrary.com/api/mcp
Cursor: one-click install, or add this to .cursor/mcp.json (Windsurf takes the same block in mcp_config.json):
{ "mcpServers": { "cyber-library": { "url": "https://www.cyberlibrary.com/api/mcp" } } }
VS Code and GitHub Copilot: one-click install, or add this to .vscode/mcp.json:
{ "servers": { "cyber-library": { "type": "http", "url": "https://www.cyberlibrary.com/api/mcp" } } }
Claude Desktop and claude.ai: Settings, Connectors, Add custom connector, paste https://www.cyberlibrary.com/api/mcp.
ChatGPT: Settings, Connectors, Advanced, turn on Developer mode, then create a connector with the same URL.
Stdio-only clients: bridge it with npx -y mcp-remote https://www.cyberlibrary.com/api/mcp.
Then ask: "Explain how Kerberoasting works and link me the page." Your assistant gets six tools (search_library, get_page, list_topics, get_outline, search_planned_topics, get_planned_subtree) and cites the page URLs. Full setup for every client is on cyberlibrary.com/mcp.
| Section | Focus |
|---|---|
| Foundation | History, ethics, risk, and the human side of security |
| Offensive | Ethical hacking, testing, and adversarial simulation |
| Defensive | Monitoring, incident response, and resilience |
| Governance | Policy, compliance, and executive-level security |
| Intelligence | Threat intelligence and OSINT |
| Career | Roles, skills, certifications, and growth |
The content is plain Markdown, generated from a shared taxonomy and published to cyberlibrary.com. Pages are written in a consistent house style: offensive topics explain the vulnerability and how it is exploited, with real commands and references.
git clone https://github.com/Cyber-Courses/Cyber-Library.git
cd Cyber-Library
Open the Markdown in your editor, or point your own static-site pipeline at it.








