
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
sonicwall-sma1000-cve-2026-102257-check — Offline SonicWall SMA1000 evidence checker for CVE-2026-102257. Reported build and configuration evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads. | Kitploit
Tools/GitHubGitHub/completetech-security/sonicwall-sma1000-cve-2026-102257-check
Defensive ToolsVulnerability ScannersVulnerability AnalysisConfiguration AuditingNetwork SecurityIncident Response
GitHubcompletetech-security/sonicwall-sma1000-cve-2026-102257-check

sonicwall-sma1000-cve-2026-102257-check

Share

Offline SonicWall SMA1000 evidence checker for CVE-2026-102257. Reported build and configuration evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.

View RepositoryWebsite
125 days agoNot yet reviewed

sonicwall-sma1000-cve-2026-102257-check by CompleteTech LLC

Tests Python 3.10+ No runtime dependencies AGPL-3.0 or commercial license

sonicwall-sma1000-cve-2026-102257-check

Offline, version-only triage for CVE-2026-102257: SonicWall SMA1000 (6210, 7210, 8200v) AMC archive path traversal. The checker compares operator-supplied build strings with the vendor's affected and fixed build table and reports JSON, CSV or script-free HTML.

It never contacts a target, probes a device or sends exploit payloads. Missing, qualified, custom, conflicting and uncovered evidence stays unknown.

Contents

  • Scope and honest limits
  • Requirements
  • Quick start
  • Synthetic report preview
  • Version rules
  • Usage
  • Output
  • Exit status
  • Output files and interruptions
  • External threat metadata
  • Sources and provenance
  • Documentation
  • Contributing, security and license

Scope and honest limits

  • One advisory only. This repository covers CVE-2026-102257 on SonicWall SMA1000 models 6210, 7210 and 8200v. Other SonicWall products are outside scope, and this CVE is independent of the other vulnerabilities in the same vendor bulletin.
  • Version evidence, not verified state. A build string is a claim made by whoever supplied it. A reported fixed build is not patch attestation, and a reported affected build is not confirmed exploitability.
  • exploitability is always not_tested. The checker has no network mode, runs no application code and sends no exploit payloads. No deployed-target assessment is claimed.
  • Unknown is never safe. Builds in the gap between the affected and fixed bounds, branches the vendor table does not list, custom builds, conflicting or malformed values and missing versions are all unknown.
  • Configuration observations are hints. The optional authenticated_archive_handling observation (inventory field or --authenticated-archive-handling true|false|unknown) records operator-supplied authenticated AMC archive handling. It never changes the version assessment and is not proof of reachability or effective configuration.

Requirements

  • Python 3.10 or newer. CI runs Python 3.10 and 3.14 on Linux, Windows and macOS.
  • Standard library only; there is nothing to install. No other checker is required at runtime.
  • Local input only: command-line --version values, JSON inventories or CSV lists. The checker has no URL or network input.

Quick start

# Assess one reported build (prints JSON; exits 1 because this build is potentially affected)
python sonicwall_sma1000_cve_2026_102257_check.py --version 12.4.3-03526

# Assess the synthetic inventory and write a standalone HTML report
python sonicwall_sma1000_cve_2026_102257_check.py --inventory examples/inventory.example.json --format html --output report.html

# Show all options and exit statuses
python sonicwall_sma1000_cve_2026_102257_check.py --help

# Run the local-only test suite
python -m unittest -v

The synthetic inventory deliberately includes findings and unknowns, so its example command exits 1. Keep real inventories, reports and targets outside version control.
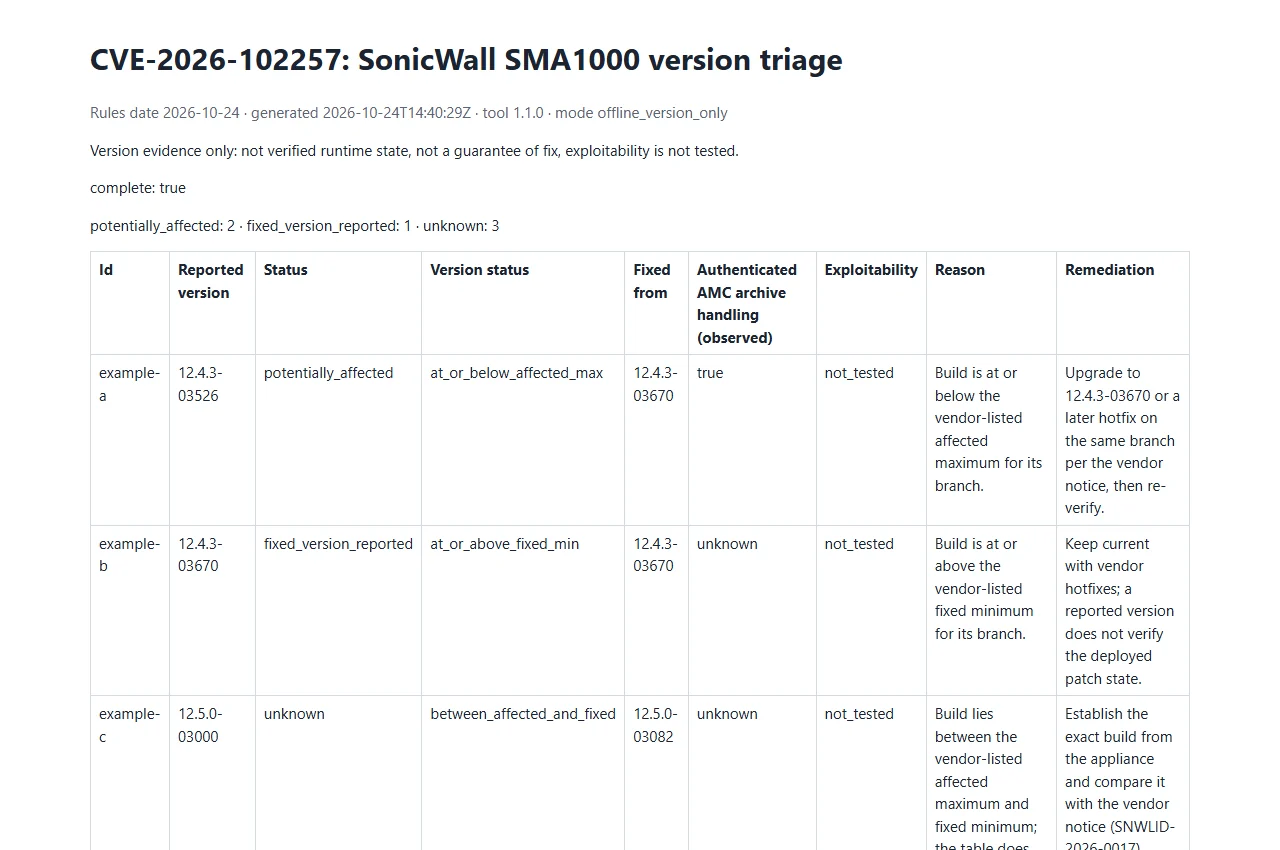
Synthetic report preview

SonicWall SMA1000 synthetic report

Open the synthetic example report. Example data only; this is not a live assessment.

Version rules

Rule date 2026-10-24, from SonicWall product notice SNWLID-2026-0017.

BranchAffected throughFixed from
12.4.312.4.3-0352612.4.3-03670
12.5.012.5.0-0295212.5.0-03082
  • Builds are compared by build number within the exact branch. The vendor lists "and older versions" and "and higher versions", so 12.4.3-9999999 is fixed_version_reported, and an unpadded 12.4.3-3526 is read as build number 3526 (1 to 8 digits; leading zeros optional).
  • Builds in the gap between the affected and fixed bounds are unknown.
  • Other branches, including older ones (the notice does not state their coverage), and every unparsable value are unknown.
  • Only SMA1000 models 6210, 7210 and 8200v are covered; any other model is unknown.

Usage

Supply at least one of --version, --inventory or --csv-list; with no input the checker exits 2. Sources can be combined, and the flags marked repeatable may be given more than once.

OptionPurpose
--version BUILDReported build to assess (repeatable). Strict <major>.<minor>.<patch>-<build>, such as 12.4.3-03526. No leading v, prerelease or vendor suffix.
--branch BRANCHOptional branch cross-check, such as 12.4.3. Applies to --version values. A branch that disagrees with the build gives unknown.
--model MODELOptional model: 6210, 7210 or 8200v. Applies to --version values. An uncovered model gives unknown.
--authenticated-archive-handling true|false|unknownOperator observation only (default unknown). Applies to --version values; never changes version_status.
--inventory FILEJSON inventory, an object or an array (repeatable).
--csv-list FILECSV list with a header that includes version (repeatable).
--format json|csv|htmlReport format. Default json.
--output FILEWrite the report to a file instead of stdout. Refuses to overwrite an existing file.
--forceAllow --output to replace an existing file.
--strictCount unknown results as findings for the exit status.

Input files

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    945
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    350
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    338
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    292

Explore all tools

Browse our collection of tools

View all tools →








