
 completetech-security/node-cve-2026-58042-check
Offline Node.js evidence checker for CVE-2026-58042: DNS resolveAny process abort. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline evidence checker for CVE-2026-58042 — Node.js: DNS resolveAny process abort.
It compares Node.js versions that you report against the fixed releases named in the vendor advisory and writes a CSV, JSON or HTML report. Python 3.10+, standard library only; the single executable can be copied on its own.
unknown. A public URL is not an inventory.exploitability: not_tested. A reported fixed version is not proof that the deployed runtime is patched.Requirements: Python 3.10 or newer. No packages to install.
python node_cve_2026_58042_check.py --version 22.23.2 --format json
python node_cve_2026_58042_check.py --inventory examples/inventory.example.json --format html --output report.html
python node_cve_2026_58042_check.py --csv-list inventory.csv --fail-on-finding
python node_cve_2026_58042_check.py --help
python -m unittest -v
Supply the version of the executable actually used by the serving process. A different node on the host or container PATH may report another version; a package upgrade alone does not establish that an already-running process restarted with it. --version is repeatable; each value describes a separate runtime. The default output format is CSV on stdout.
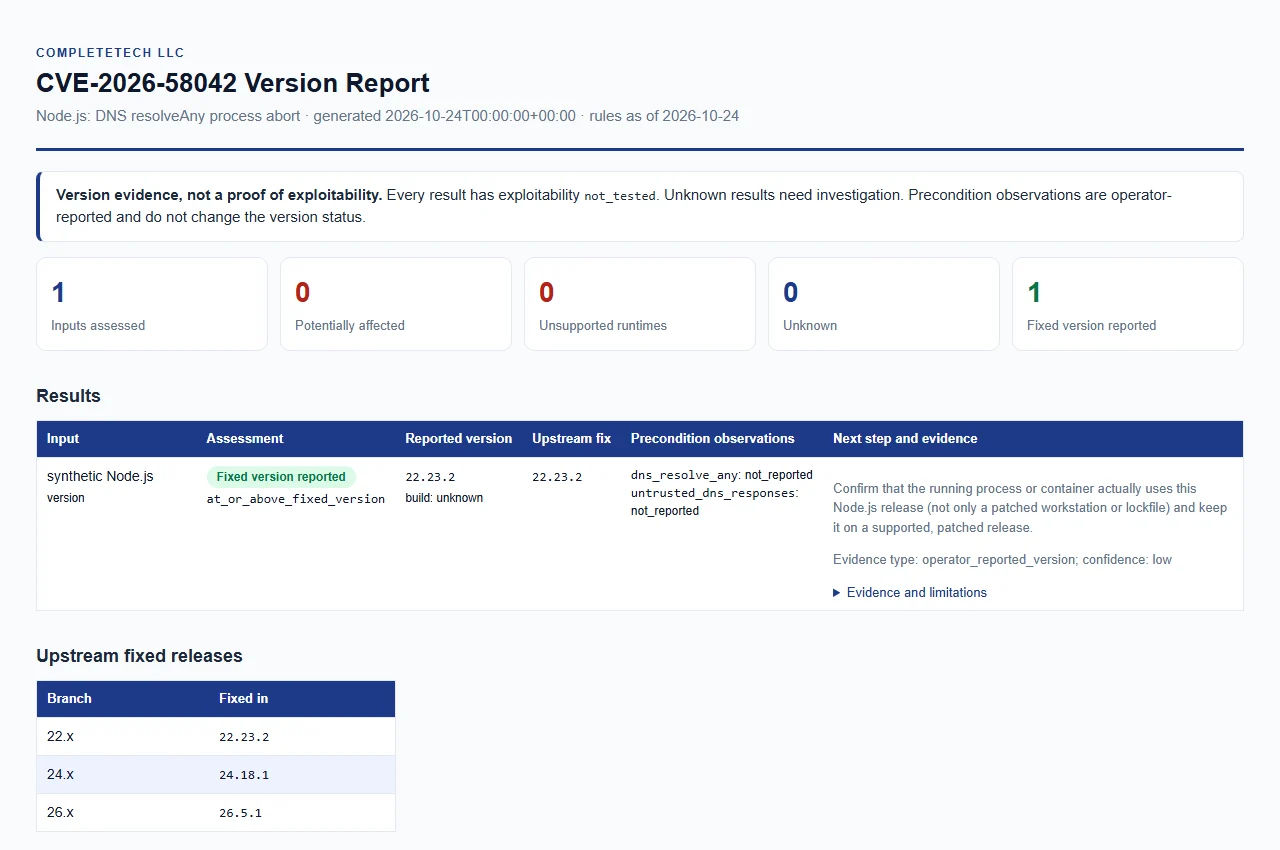
Open the synthetic example report. Example data only; this is not a live assessment.
Reviewed 2026-10-24 against the official release advisory and the linked fixed releases.
| Node.js major | Fixed version |
|---|---|
| 22.x | 22.23.2 |
| 24.x | 24.18.1 |
| 26.x | 26.5.1 |
For each listed major, versions below its fixed version require remediation. The vendor does not specify an introduced version in the release advisory, so every earlier version on a listed major is treated as possibly affected.
| Reported version | Result |
|---|---|
| Plain version on a listed major, below the fixed version | potentially_affected |
| Fixed version, or a later plain version on the same listed major | fixed_version_reported |
| Plain version on an end-of-life major | unsupported_runtime |
| Any other active or future major | unknown (release_line_not_in_rules) |
| Missing, malformed, conflicting, prerelease, nightly/rc, suffixed or otherwise qualified version | unknown |
Vendor, distribution, custom or unrecognized build_source | unknown (vendor_build_unverified) |
unsupported_runtime is upgrade guidance, not a claim that this particular flaw exists in every historical build. The end-of-life majors are taken from the Node.js release schedule, reviewed 2026-10-24 (the 0.x series is an inference from that schedule).unknown (the default), upstream, official, official_upstream or blank are compared as upstream builds.v and surrounding ASCII whitespace are ignored; anything else beyond MAJOR.MINOR.PATCH makes the version qualified.| Status | Meaning |
|---|---|
potentially_affected | The reported version is below the fixed release of its major and needs remediation review. This is not confirmed exploitability. |
fixed_version_reported | The reported version is at or above the fixed release. This is not deployed-patch attestation: confirm the running process or container actually uses that release, not only a workstation or lockfile. |
unsupported_runtime | The major is past end of life. Migrate to a supported, fixed release. |
unknown | Evidence is missing or unclassifiable. Collect the exact upstream version and build provenance of the running process and run the checker again. |
Each result also carries a more specific version_status (such as below_fixed_version, at_or_above_fixed_version, unsupported_release_line, release_line_not_in_rules, version_not_disclosed, qualified_version_unverified, unrecognized_or_partial_version or vendor_build_unverified), the applicable fixed_version, a recommendation, and notes. evidence_type is operator_reported_version; evidence_confidence is low, or insufficient for unknown.
Exploitability is never tested. Optional precondition observations are operator-supplied and unverified; they are recorded separately, never change the version result, and do not establish reachability.
| Observation key | Meaning |
|---|---|
dns_resolve_any | dns resolve any |
untrusted_dns_responses | untrusted dns responses |
Each observation is reported as reported_true, reported_false or not_reported.
python node_cve_2026_58042_check.py [options]
At least one of --version, --inventory or --csv-list is required. Run --help for the authoritative option list.






