 completetech-security/node-cve-2026-106074-check
Offline Node.js evidence checker for CVE-2026-106074: Crypto entropy cache duplication in snapshots. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline version-evidence checker for CVE-2026-106074 — Node.js: Crypto entropy cache duplication in snapshots.
It compares the Node.js versions you report against the fixed releases named in the official October 2026 Node.js security release and classifies each one as potentially_affected, fixed_version_reported, unsupported_runtime or unknown. Results are triage evidence, not a runtime assessment, a patch attestation or an exploit verification.
unknown.exploitability: not_tested.Python 3.10 or newer and the standard library only. There are no runtime dependencies, and node_cve_2026_106074_check.py can be copied and used on its own. CI runs the tests on Ubuntu and Windows with Python 3.10 and 3.14.
# Assess one reported version; print JSON to stdout
python node_cve_2026_106074_check.py --version 22.23.4 --format json

# Assess the synthetic example inventory and write an HTML report
python node_cve_2026_106074_check.py --inventory examples/inventory.example.json --format html --output report.html

# Assess a CSV list; exit 1 if any result is potentially_affected or unsupported_runtime
python node_cve_2026_106074_check.py --csv-list inventory.csv --fail-on-finding

# List every option
python node_cve_2026_106074_check.py --help
CSV is the default format and stdout is the default destination. --version is repeatable and may be combined with --inventory and --csv-list; each value or entry describes a separate runtime. JSON, CSV and HTML are rendered from the same evidence. See Command-line options for details.
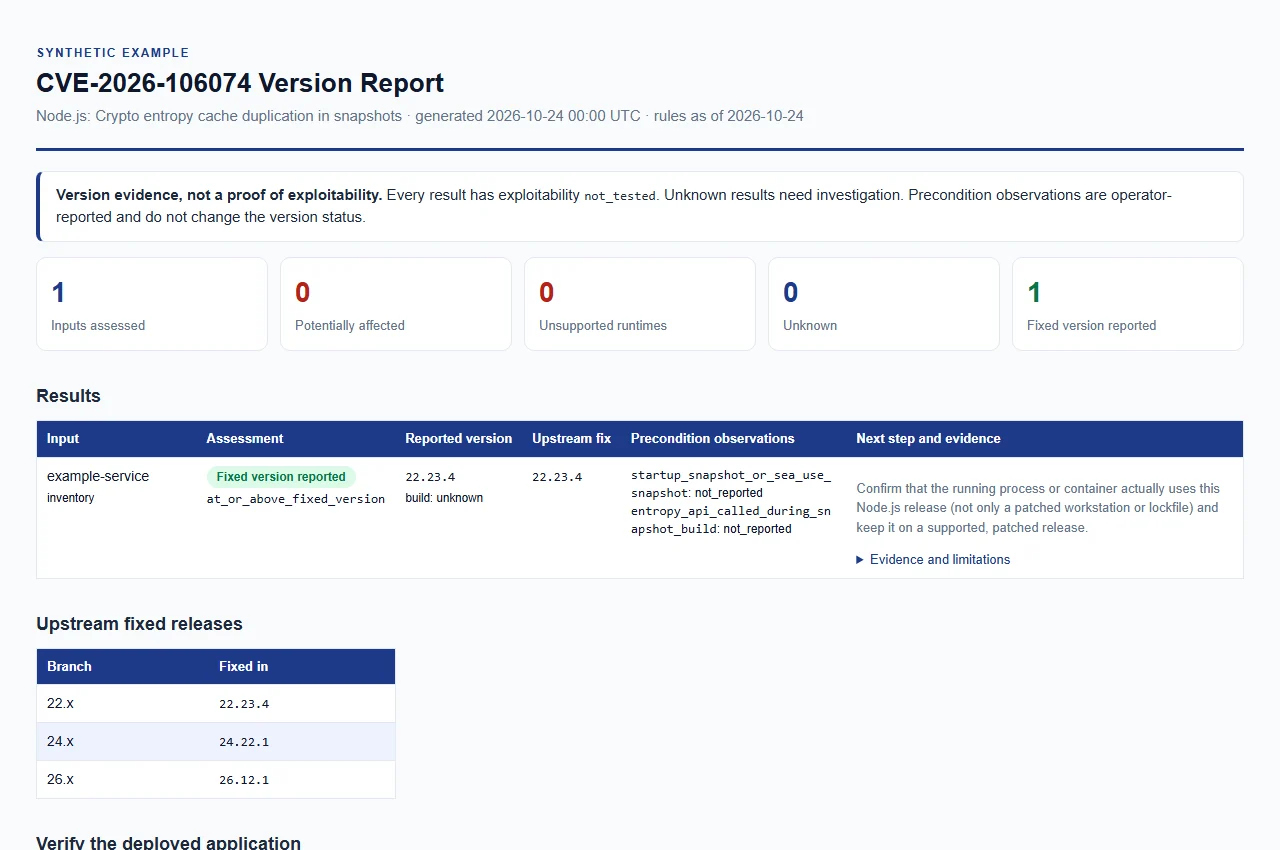
Open the synthetic example report. It uses example data only and is not a live assessment.
Rules reviewed on 2026-10-24 against the official release advisory and the linked fixed releases (the advisory was published 2026-10-21).
| Node.js major | Fixed version |
|---|---|
| 22.x | 22.23.4 |
| 24.x | 24.22.1 |
| 26.x | 26.12.1 |
For each listed major, versions below its fixed version require remediation. The vendor does not specify an introduced version in the release advisory, so every earlier version of a listed major is treated as potentially affected.
| Reported version | Result |
|---|---|
| Plain version below the fixed version of a listed major | potentially_affected |
| Fixed version, or a later plain version on the same listed major | fixed_version_reported |
| Major that is end-of-life in the Node.js release schedule | unsupported_runtime |
| Any other major (not listed and not end-of-life in the reviewed schedule) | unknown |
| Missing, conflicting, malformed, prerelease, nightly or other qualified version | unknown |
| Vendor, distribution, custom or unrecognized build source | unknown |
Notes on these rules:
unsupported_runtime is upgrade guidance, not a claim that this particular flaw exists in every historical build. It applies to majors 4–21, 23 and 25 as listed in the Node.js release schedule reviewed on 2026-10-24, and to major 0 by inference (the schedule lists only 0.8, 0.10 and 0.12, all ended by 2016-12-31).unknown (the default), upstream, official or official_upstream, or none at all, is compared as an upstream release; any other value is treated as a vendor or custom build.fixed_version_reported is a statement about the reported version. It is not proof of the deployed runtime and not a verified deployed patch; a lockfile or patched workstation does not establish what the running process uses.v. Only plain MAJOR.MINOR.PATCH versions are compared.Each input describes one Node.js runtime. Inputs are limited as described in Limits, exit codes and interruption.
| Field | Required | Description |
|---|---|---|
schema_version | JSON only | Integer 1. |
node_version | Yes | Version string reported for the runtime. |
runtime | No | JSON only. If present, must be "node". |
label | No | Name shown in reports. Defaults to the file name and entry number, such as inventory:1. |
build_source | No | Provenance of the build; see Fixed versions and classification. Defaults to unknown. |
startup_snapshot_or_sea_use_snapshot | No | Operator observation: startup snapshot or SEA use snapshot. |
entropy_api_called_during_snapshot_build | No | Operator observation: entropy API called during snapshot build. |
Observations are operator-supplied and unverified. They are recorded in the report as reported_true, reported_false or not_reported; they never change the version result and never establish reachability.







