Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
log4j-log4shell-affected — Lists of affected components and affected apps/vendors by CVE-2021-44228 (aka Log4shell or Log4j RCE). This list is meant as a resource for security responders to be able to find and address the vulnerability | Kitploit
Tools/GitHubGitHub/authomize/log4j-log4shell-affected
Vulnerability AnalysisThreat IntelligenceSupply Chain SecurityLearning & EducationIncident ResponseCurated Resources
GitHubauthomize/log4j-log4shell-affected

log4j-log4shell-affected

Lists of affected components and affected apps/vendors by CVE-2021-44228 (aka Log4shell or Log4j RCE). This list is meant as a resource for security responders to be able to find and address the vulnerability

View Repository
528304 years agoReviewed by Kitploit
Share

log4j-log4shell-affected

Lists of affected components and affected apps/vendors by CVE-2021-44228 (aka Log4shell or Log4j RCE) for security responders.

We believe it is important to classify the vendors and products between:

  1. Internal risk - what you need to patch first to remove risk internally
  2. External risk - all third/fourth-party vendors that have custody of your data that might've been hacked that you will need to monitor and tackle once you're done patching

Here are the lists:

External Risk - Affected Apps

i.e. all vendors you should worry about if you have data in their environemnt or if they access to your environment

Internal Risk - Affected Components

i.e. software components you might have used in building your products that you should worry if they cause you to be vulnerable

Other useful resources

Lists

Artifacts using log4j

Compromised apps with confirmation

List of responses from various vendors, some affected and some not

Official list maintained by CISA - US Govt

Official list maintained by NCSC - NL govt, high update frequency

Guides how to repsond

A fast and simple guide on what to do to respond to the log4j incident

General incident response guide in case you discover a 3rd party vendor of yours got hacked

Contributing

We are happy to recieve contributions from the community. Contribution guidelines:

  • Please make a PR editing the raw CSV files.
  • Please be sure to include a reference source for each added row (claims without a validated link for source of claim will not be accepted)

About this repo

This repo is maintained to simplify response for enterprises and organizations by separating between:

  1. Internal risk - Software components you need to search for and patch in your products / internal environment
  2. External risk - Third and fourth-party vendors/apps who might've been affected and you should to monitor if your data is in their custody

This list is a community project open for everyone to contribute to and is curated by: Authomize Logo
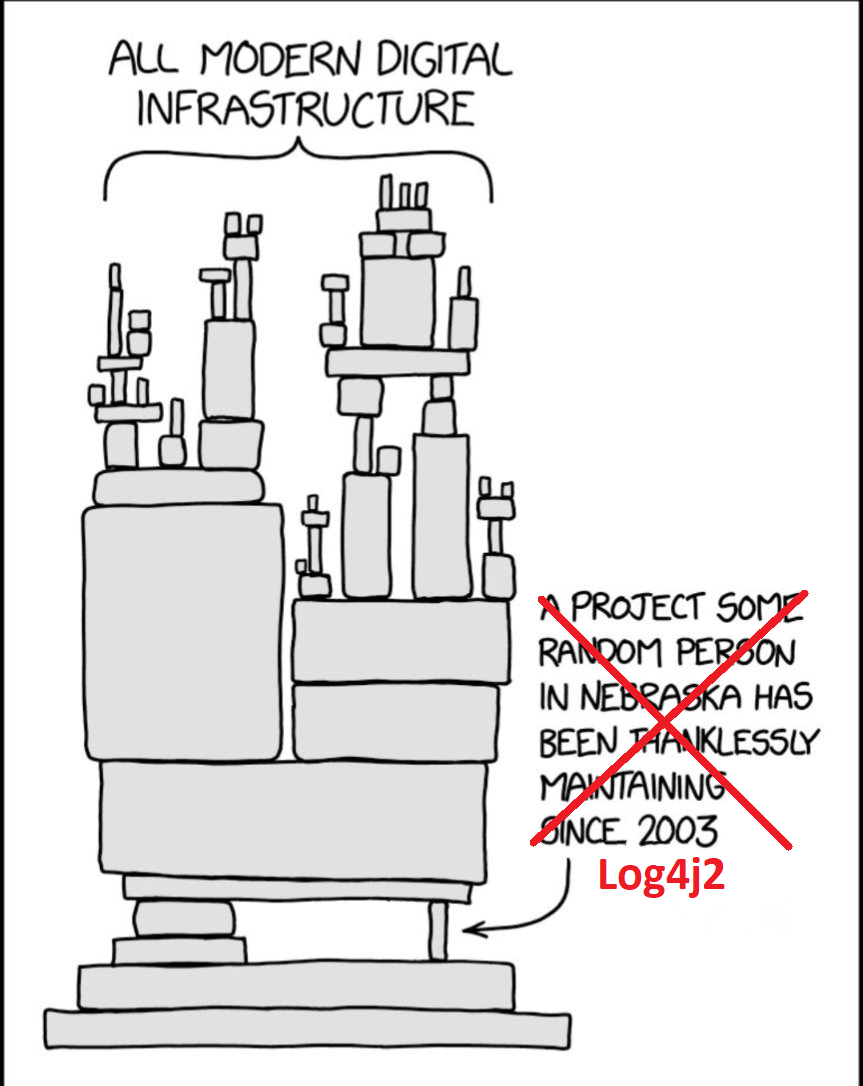
Our favorite description of the situation

Meme

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →