Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyยฉ 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-22812 โ€” Security advisory and technical analysis for CVE-2026-22812, an unauthenticated localhost HTTP server RCE in OpenCode, with detection guidance, mitigation steps, and patch notes. | Kitploit
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-22812
Defensive ToolsVulnerability AnalysisWeb SecurityThreat IntelligenceLearning & EducationIncident Response
GitHubashrafzaryouh/cve-2026-22812

CVE-2026-22812

Security advisory and technical analysis for CVE-2026-22812, an unauthenticated localhost HTTP server RCE in OpenCode, with detection guidance, mitigation steps, and patch notes.

Share
View Repository
17 months agoNot yet reviewed

๐Ÿ” CVE-2026-22812 - OpenCode Unauthenticated HTTP Server โ†’ Remote Code Execution (RCE)

bda545bb-f57e-4905-be5d-42c67ba41d04_1280x721

CVE Severity CVSS Status License


Security advisory, technical analysis, detection guidance, and mitigation notes for CVE-2026-22812


๐Ÿ“Œ Overview

CVE-2026-22812 is a high-severity Remote Code Execution (RCE) vulnerability affecting OpenCode versions prior to 1.0.216.

The issue exists because OpenCode automatically starts an unauthenticated local HTTP server that can be accessed by:

  • local malicious processes
  • browser tabs through permissive CORS
  • injected web content
  • localhost cross-origin requests

This allows attackers to execute arbitrary shell commands with the privileges of the current user


๐Ÿšจ Severity

MetricValue
CVE IDCVE-2026-22812
SeverityHigh
CVSS8.8
CWECWE-306, CWE-749, CWE-942
Attack TypeRemote Code Execution
Fixed Version1.0.216+

Source: NVD / GitHub Advisory


๐Ÿง  Technical Root Cause

The vulnerable versions automatically expose a localhost HTTP service without authentication.

Because the service also accepts requests from permissive cross-origin sources, any malicious webpage can trigger requests such as:

POST /session/:id/shell

This can lead to:

  • arbitrary command execution
  • credential theft
  • source code exfiltration
  • SSH key exposure
  • cloud token compromise
  • local persistence

๐Ÿ’ฅ Impact

Successful exploitation may result in:

  • ๐Ÿ”“ Full developer workstation compromise
  • ๐Ÿ—๏ธ Secret leakage (.env, SSH, API tokens)
  • ๐Ÿ“‚ Unauthorized source code access
  • โ˜๏ธ Cloud CLI session hijacking
  • ๐Ÿงช Supply-chain compromise risks
  • ๐Ÿ–ฅ๏ธ Arbitrary shell execution as logged-in user

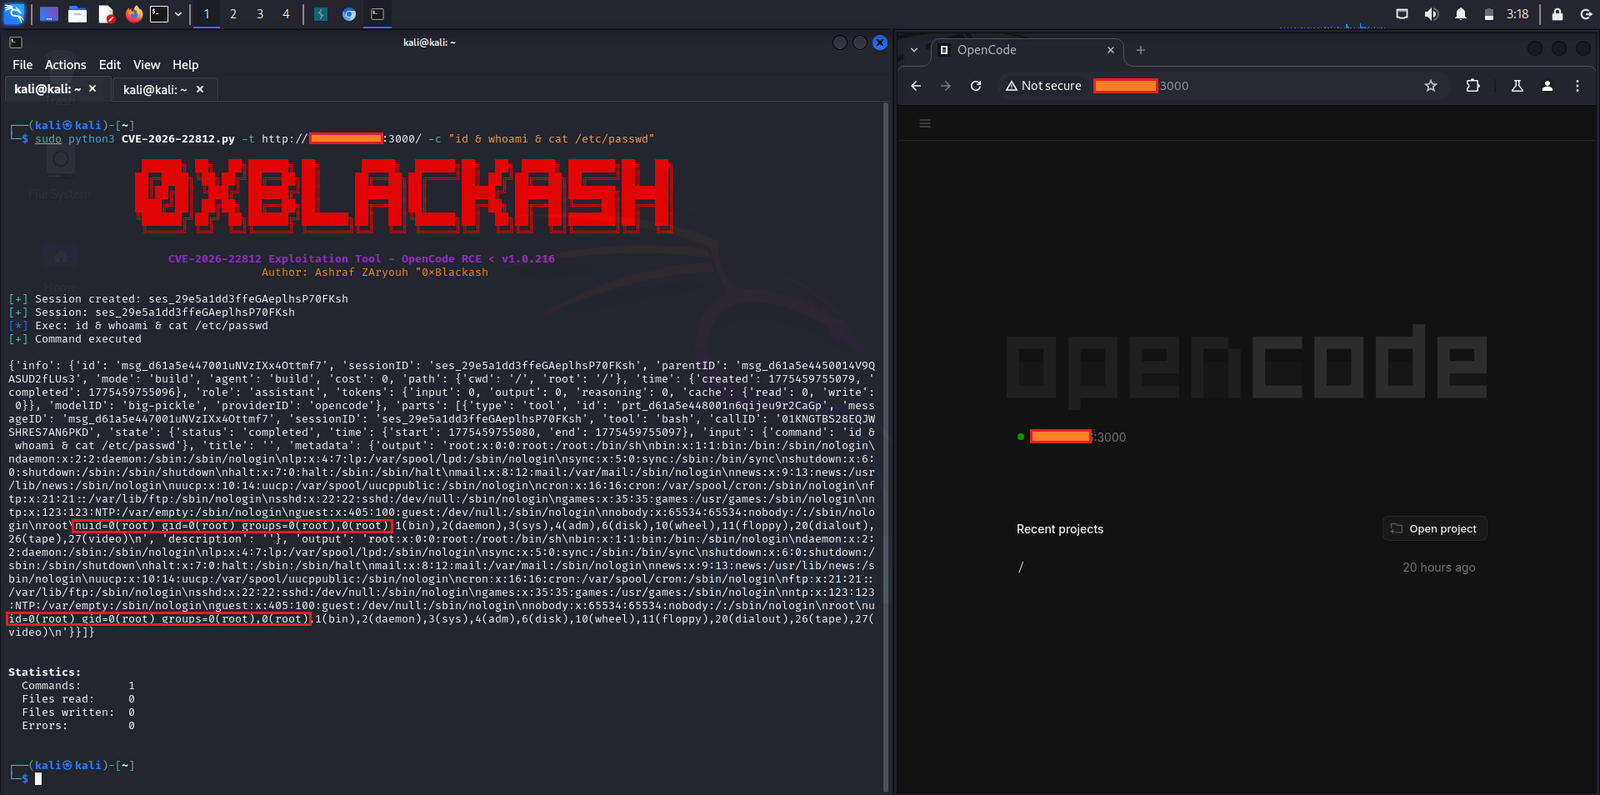
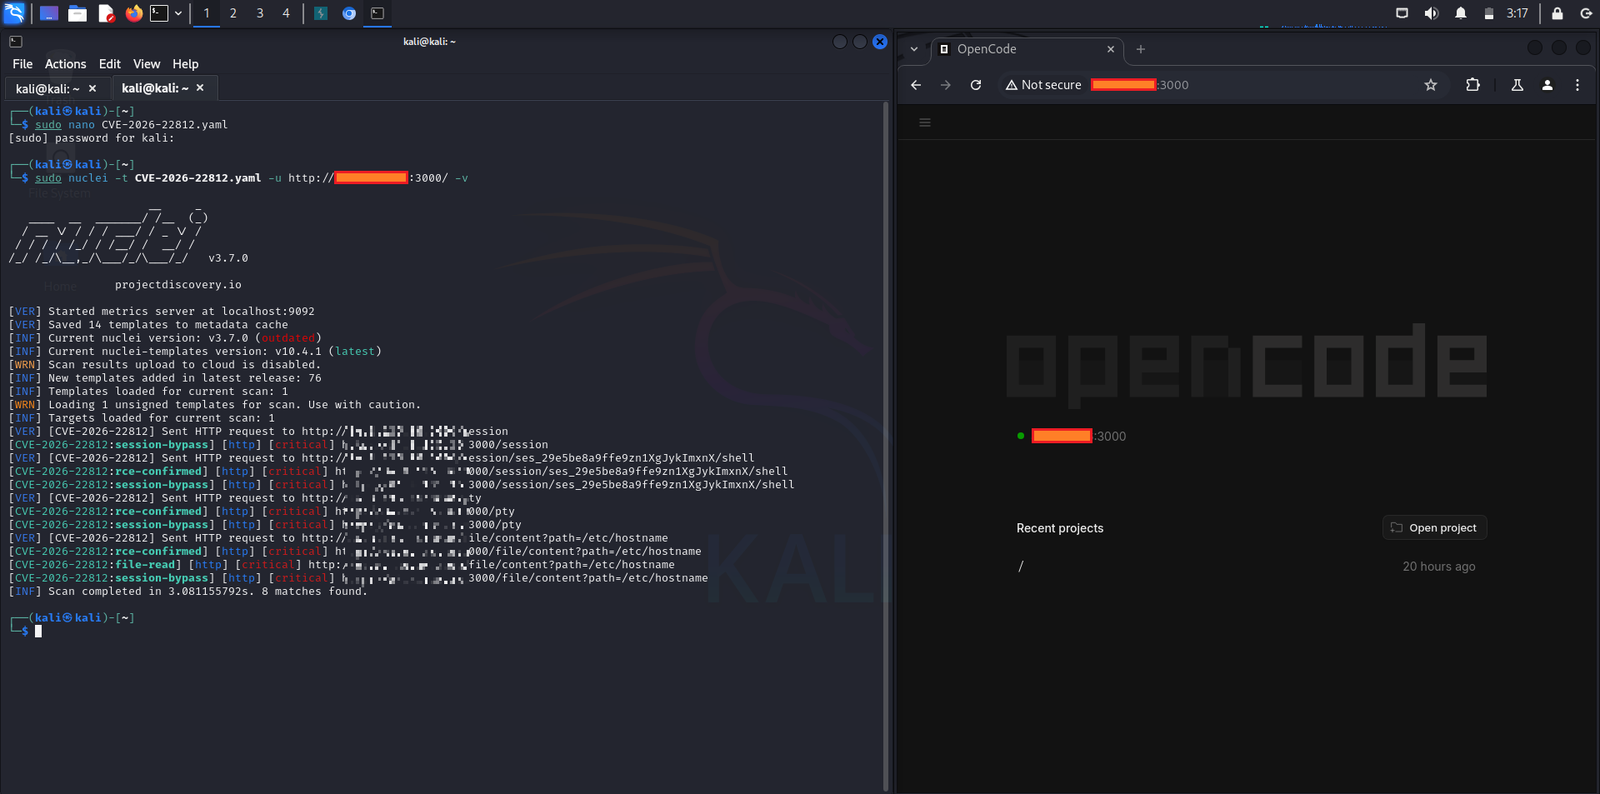
๐Ÿ“ธ Screenshot

cve-2026-22812 1 cve-2026-22812

๐Ÿ“ฆ Affected Versions

Vulnerable: < 1.0.216
Safe:       >= 1.0.216

๐Ÿ› ๏ธ Mitigation

โœ… Recommended Fix

Upgrade immediately:

npm update opencode

or install a safe version:

npm install [email protected]

๐Ÿงฑ Temporary Workarounds

If upgrading is not immediately possible:

  • restrict localhost port access
  • isolate OpenCode inside a container
  • block suspicious localhost requests
  • close untrusted browser tabs
  • rotate exposed credentials
  • disable permissive CORS if configurable

๐Ÿ” Detection Tips

Indicators of possible exploitation:

  • unusual shell commands spawned by OpenCode
  • suspicious localhost POST requests
  • browser-originated requests to OpenCode ports
  • unexpected file access in project directories
  • abnormal terminal child processes

Recommended telemetry:

  • EDR process tree monitoring
  • localhost HTTP access logs
  • shell execution auditing
  • browser security telemetry

๐Ÿงช Proof of Concept Status

โš ๏ธ Public exploitation details exist in advisory discussions.

For responsible disclosure and safety, avoid publishing weaponized PoCs in public production repositories.


๐Ÿ“š References

  • NVD Advisory NVD CVE Entry
  • OSV Database OSV Entry
  • Vendor Advisory GitHub Security Advisory

โš–๏ธ Disclaimer

This repository is intended for:

  • defensive security research
  • blue-team awareness
  • patch validation
  • vulnerability management
  • secure development education

Do not use this information on systems you do not own or have permission to test.


๐Ÿ›ก๏ธ Secure your AI developer tools before they secure your code

Download Tool

Most Popular

View all โ†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    ๐ŸŽฏ The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    790
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    508
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    435
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityโ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    263
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    260

Explore all tools

Browse our collection of tools

View all tools โ†’