

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-20127 — Advisory for CVE-2026-20127, a critical Cisco Catalyst SD-WAN authentication bypass (CVSS 10.0), covering root cause, exploitation flow, affected products, detection and mitigation. | Kitploit
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-20127
Vulnerability AnalysisNetwork SecurityThreat IntelligenceAuthenticationMisconfigurationIncident Response
GitHubashrafzaryouh/cve-2026-20127

CVE-2026-20127

Advisory for CVE-2026-20127, a critical Cisco Catalyst SD-WAN authentication bypass (CVSS 10.0), covering root cause, exploitation flow, affected products, detection and mitigation.

View Repository
5 months agoNot yet reviewed
Share

🛡️ CVE-2026-20127 — Cisco Catalyst SD-WAN Authentication Bypass

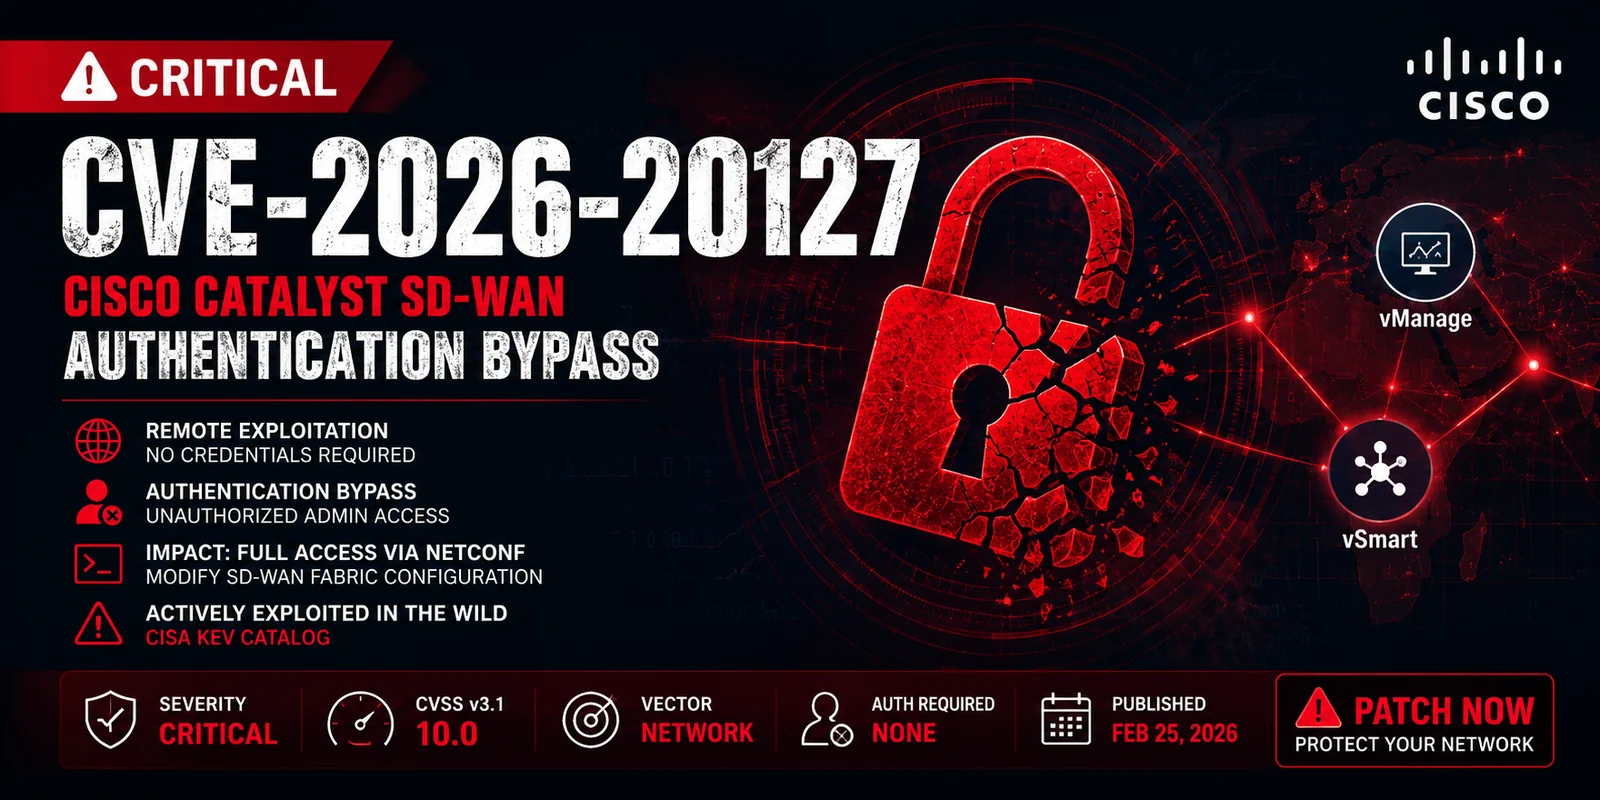
ChatGPT Image Jun 14, 2026, 02_32_26 PM


📌 Overview

CVE-2026-20127 is a critical authentication bypass vulnerability affecting Cisco Catalyst SD-WAN components, including controllers and management systems.

A remote unauthenticated attacker can exploit improper authentication validation in the SD-WAN control plane, resulting in full administrative-level access to network infrastructure.

This issue is considered critical severity (CVSS 10.0) and has been observed as actively exploited in real-world environments.


⚠️ Impact

Successful exploitation may allow an attacker to:

  • 🔓 Bypass authentication mechanisms completely
  • 🧠 Gain unauthorized administrative-level access
  • 🌐 Access internal SD-WAN management services
  • ⚙️ Modify routing and network policies
  • 🧩 Inject rogue SD-WAN peers
  • 🏴 Achieve full control-plane compromise

🧬 Technical Details

Root Cause

The vulnerability is caused by improper validation of SD-WAN peer authentication requests, allowing crafted network traffic to be treated as trusted internal communication.


CVSS v3.1 Vector

CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H
MetricValue
Attack VectorNetwork
Attack ComplexityLow
Privileges RequiredNone
User InteractionNone
ScopeChanged
ConfidentialityHigh
IntegrityHigh
AvailabilityHigh

🧪 High-Level Exploitation Flow

[1] Attacker sends crafted SD-WAN peer request
        ↓
[2] Authentication validation fails
        ↓
[3] System trusts attacker as valid internal peer
        ↓
[4] Access to NETCONF / management APIs granted
        ↓
[5] Full SD-WAN control plane compromise

🖥️ Affected Products

  • Cisco Catalyst SD-WAN Controller (vSmart)
  • Cisco Catalyst SD-WAN Manager (vManage)

Multiple software branches may be affected depending on configuration and version.


🔍 Detection

Security teams should monitor for:

  • Unexpected SD-WAN peer registrations
  • Unauthorized NETCONF sessions
  • Unknown or rogue controller identities
  • Sudden configuration changes in routing policies
  • Authentication anomalies in SD-WAN logs
  • Management access from untrusted sources

🛡️ Mitigation

✅ Recommended Actions

  • Immediately apply Cisco security patches
  • Restrict access to SD-WAN management interfaces
  • Isolate control-plane networks from public exposure
  • Enforce strict segmentation between management and data planes
  • Enable centralized logging and SIEM monitoring
  • Validate all SD-WAN peer relationships

🚫 Workarounds

There are no safe workarounds. Patch deployment is required.


📊 Risk Summary

CategoryLevel
ExploitabilityVery High
ImpactCritical
Detection DifficultyMedium–High
Patch UrgencyImmediate

🧠 Threat Context

This vulnerability is particularly dangerous because it targets the SD-WAN control plane, which acts as the brain of enterprise networking.

A successful exploit may result in:

  • Persistent network compromise
  • Traffic rerouting or interception
  • Enterprise-wide service disruption
  • Stealthy long-term attacker presence

🧷 Security Recommendations

  • Treat SD-WAN controllers as Tier-0 infrastructure
  • Enforce MFA and strict admin access controls
  • Continuously audit SD-WAN topology changes
  • Restrict management access to trusted IP ranges
  • Monitor control-plane behavior anomalies
  • Maintain rapid patch management cycles

📎 References

  • Cisco Security Advisories
  • NVD CVE Database
  • CISA Known Exploited Vulnerabilities (KEV) Catalog
  • Vendor Security Bulletins

⚡ Final Note

“Compromising the SD-WAN control plane is equivalent to compromising the entire network.”

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →





