 ak-cybe/cve-2025-68613-n8n-rce-analysis
CVE-2025-68613 (n8n) Critical RCE analysis + defensive recommendations (patch validation, detection ideas, and hardening tips)



 Matrix GIF

CVE-2025-68613 is a critical remote code execution vulnerability in n8n's workflow automation platform that allows authenticated attackers to execute arbitrary system commands through expression injection.
⚡ Quick Stats
|
🎯 Key Facts
|
| Property | Value |
|---|---|
| 🆔 CVE ID | CVE-2025-68613 |
| 📊 CVSS Score | 9.9 (Critical) 🔴 |
| 🔗 CVSS Vector | CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H |
| 🏷️ CWE | CWE-913 (Improper Control of Dynamically-Managed Code Resources) |
| 📦 Affected Versions | 0.211.0 → 1.120.3, 1.121.0 |
| ✅ Patched Versions | 1.120.4, 1.121.1, 1.122.0+ |
n8n is an open-source workflow automation platform enabling no-code/low-code integration across 400+ applications. It's widely deployed in:
| 🏢 Use Case | 📝 Description |
|---|---|
| 🔧 DevOps | Automation pipelines, CI/CD integrations |
| 🛡️ Security Ops | SOAR workflows, incident response |
| 💼 Business | Process automation, data workflows |
| 📊 Data | ETL processes, API integrations |
🔓 VULNERABILITY CHAIN:
┌─────────────────────────────────────────────────────────────────┐
│  📝 n8n Expression Language → Dynamic Data Handling            │
│                           ↓                                     │
│  ⚠️  Insufficient Sandbox Isolation in Server-Side Eval        │
│                           ↓                                     │
│  💀 Malicious Expression Escapes Sandbox                       │
│                           ↓                                     │
│  🖥️  Access to Node.js child_process Module                    │
│                           ↓                                     │
│  💥 FULL RCE - OS Command Execution                            │
└─────────────────────────────────────────────────────────────────┘
Prerequisites for Exploitation:
| # | 📋 Requirement | 📝 Details |
|---|---|---|
| 1️⃣ | Authentication | Valid n8n user account (low-privilege sufficient) |
| 2️⃣ | Permissions | Workflow creation/editing capability |
| 3️⃣ | Network Access | Ability to reach n8n instance |
| 🏷️ Attribute | 📊 Value | 🔥 Risk |
|---|---|---|
| Complexity | LOW (AC:L) | 🔴 High |
| User Interaction | None Required | 🔴 High |
| Scope | Changed | 🔴 Critical |
graph TD
    A[🔐 Authenticated User] -->|Creates| B[📝 New Workflow]
    B -->|Injects| C[💀 Malicious Expression]
    C -->|Triggers| D[⚡ Expression Evaluation]
    D -->|Exploits| E[🔓 Sandbox Escape]
    E -->|Accesses| F[🖥️ Node.js Runtime]
    F -->|Executes| G[💥 OS Command via child_process]
    G -->|Achieves| H[☠️ FULL SERVER COMPROMISE]

    style A fill:#4CAF50,color:#fff
    style C fill:#ff9800,color:#fff
    style E fill:#f44336,color:#fff
    style H fill:#9c27b0,color:#fff
⚠️ DISCLAIMER: The following is for educational purposes only. Unauthorized exploitation is illegal.
Initial access to vulnerable n8n workflow automation platform.
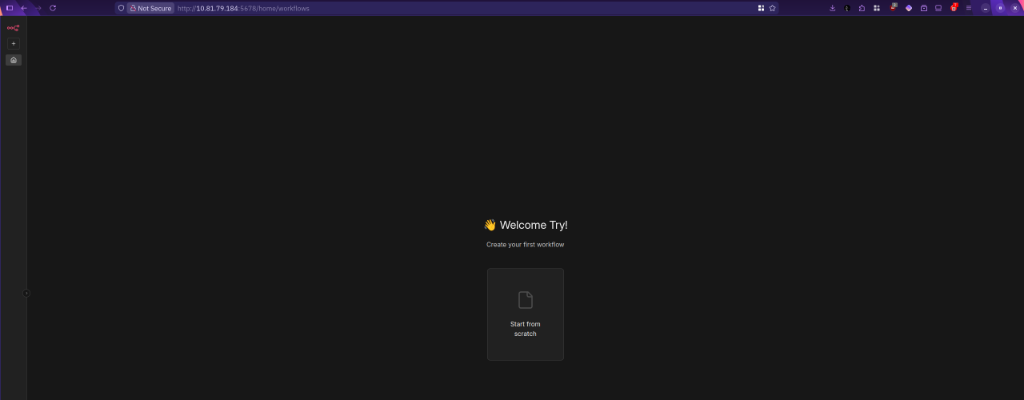
🔓 n8n Welcome Dashboard - Entry Point
Create a new workflow that will contain the malicious payload.
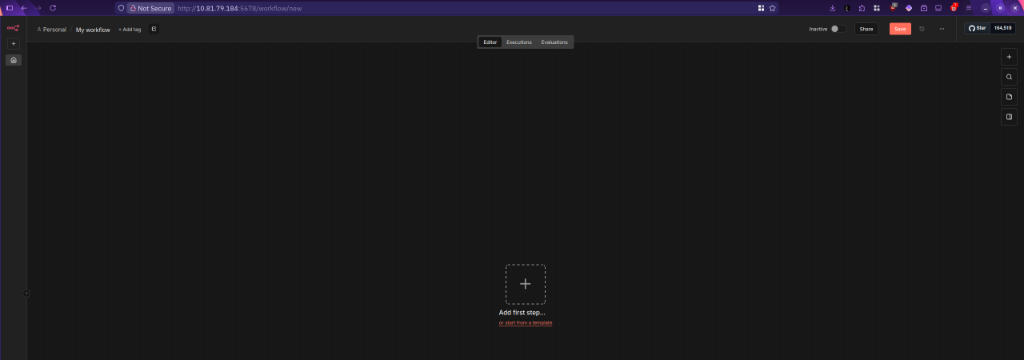
📝 Creating new workflow with "Add first step"
Configure workflow trigger - Manual Trigger allows on-demand execution.






