
 0xblackash/cve-2026-83844
Advisory documentation for CVE-2026-83844, a Windows Paint out-of-bounds read RCE (CVSS 8.1), covering affected versions, detection commands, and patch verification.




Security Research | Vulnerability Analysis | Defensive Investigation
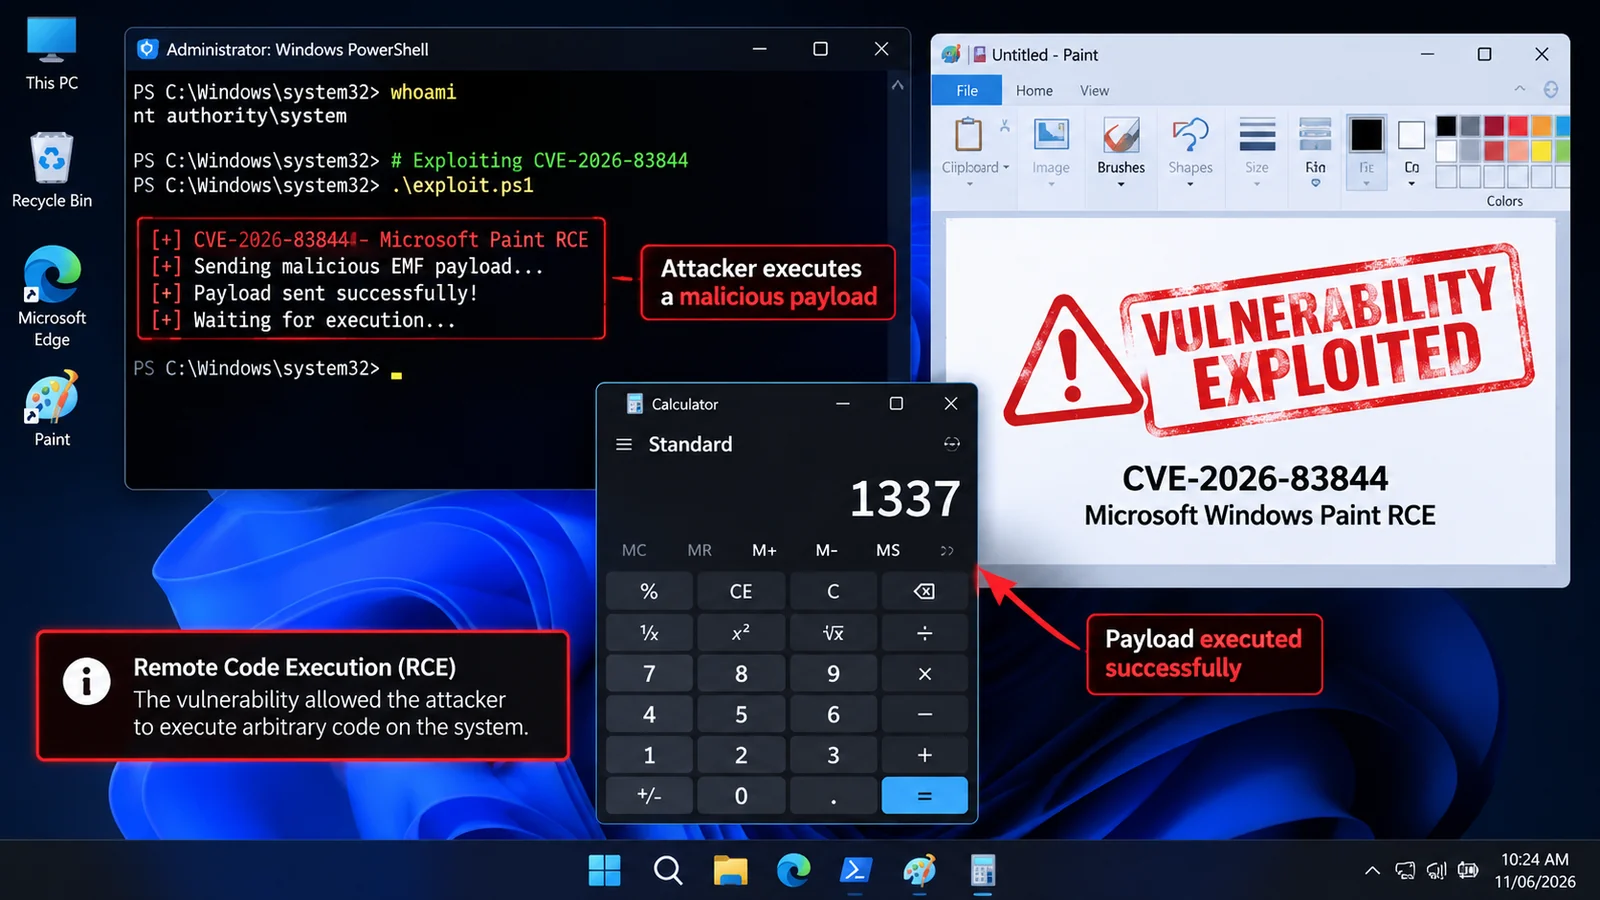
CVE-2026-83844 is a high-severity Remote Code Execution (RCE) vulnerability affecting Microsoft Windows Paint.
The vulnerability is caused by an Out-of-Bounds Read (CWE-125) that may allow an unauthorized attacker to execute code over a network.
Successful exploitation could potentially compromise the confidentiality, integrity, and availability of an affected system.
| Attribute | Details |
|---|---|
| CVE ID | CVE-2026-83844 |
| Vendor | Microsoft |
| Product | Microsoft Paint |
| Vulnerability Type | Out-of-Bounds Read |
| CWE | CWE-125 |
| Attack Category | Remote Code Execution |
| CVSS Version | 3.1 |
| CVSS Score | 8.1 |
| Severity | HIGH |
| Attack Vector | Network |
| Published | October 13, 2026 |
| Research Type | Vulnerability Analysis |
CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H
| Metric | Value |
|---|---|
| Attack Vector (AV) | Network |
| Attack Complexity (AC) | High |
| Privileges Required (PR) | None |
| User Interaction (UI) | None |
| Scope (S) | Unchanged |
| Confidentiality (C) | High |
| Integrity (I) | High |
| Availability (A) | High |
Vendor: Microsoft
Product: Microsoft Paint
The original CVE record identifies the following affected version range:
| Version | Status |
|---|---|
| 11.0.0.0 | Affected |
| Earlier than 11.2605.91.0 | Affected |
| 11.2605.91.0 and later | Original CVE record's stated boundary |
Important version clarification: Subsequent November 6, 2026 reporting identifies Microsoft Paint 11.2609.401.0 as the available fixed build. The originally listed 11.2605.91.0 build reportedly never appeared in the public Store catalog.
For remediation, install the latest Microsoft Paint update through the Microsoft Store and verify that the installed version is at least 11.2609.401.0.
CVE-2026-83844 is classified as:
CWE-125 — Out-of-Bounds Read
An out-of-bounds read occurs when an application attempts to access memory outside the boundaries of an allocated buffer.
Potential consequences include:
The reported vulnerability has the following potential security implications:
| Impact | Description |
|---|---|
| Confidentiality | Potential unauthorized access to information |
| Integrity | Potential unauthorized modification of information |
| Availability | Potential disruption of system or application functionality |
| Remote Code Execution | Microsoft identifies remote code execution as the vulnerability impact |
Technical limitation: The publicly available CVE description does not provide sufficient implementation details to establish the exact vulnerable code path or a reproducible exploitation procedure.
The vulnerability is categorized as network-based.
The published CVSS vector indicates:
These metrics describe the vulnerability's assessed characteristics. They do not establish a confirmed exploitation sequence or prove that every Paint installation is directly reachable over a network.
Open PowerShell and execute:
Get-AppxPackage -Name Microsoft.Paint |
Select-Object Name, Version, PackageFullName
Review the installed package version.
You can also verify the version manually:
Open Microsoft Store:
Recommended defensive measures:
11.2609.401.0 or later.Priority: Systems running vulnerable Paint versions should be updated as soon as possible.
Based on the available vulnerability enrichment information:
| Assessment | Status |
|---|---|
| Known exploitation | None reported |
| Public exploit | Not established |
| Automatable | No |
| Technical impact | Total |
| CISA KEV listing | Not identified in the referenced data |
Absence of reported exploitation does not mean the vulnerability is harmless.
This repository documents a defensive research workflow:
       CVE Identification
               |
               v
       Advisory Collection
               |
               v
       Affected Version Analysis
               |
               v
       Vulnerability Classification
               |
               v
       CVSS Assessment
               |
               v
       Detection & Verification
               |
               v
       Patch Validation
               |
               v
       Security Documentation
CVE-2026-83844/
│
├── README.md
│
├── images/
│   ├── banner.png
│   └── lab-environment.png
│
├── research/
│   └── technical-analysis.md
│
└── references/
    └── sources.md
This repository is intended strictly for educational purposes, cybersecurity research, vulnerability awareness, and defensive security analysis.






