#1
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
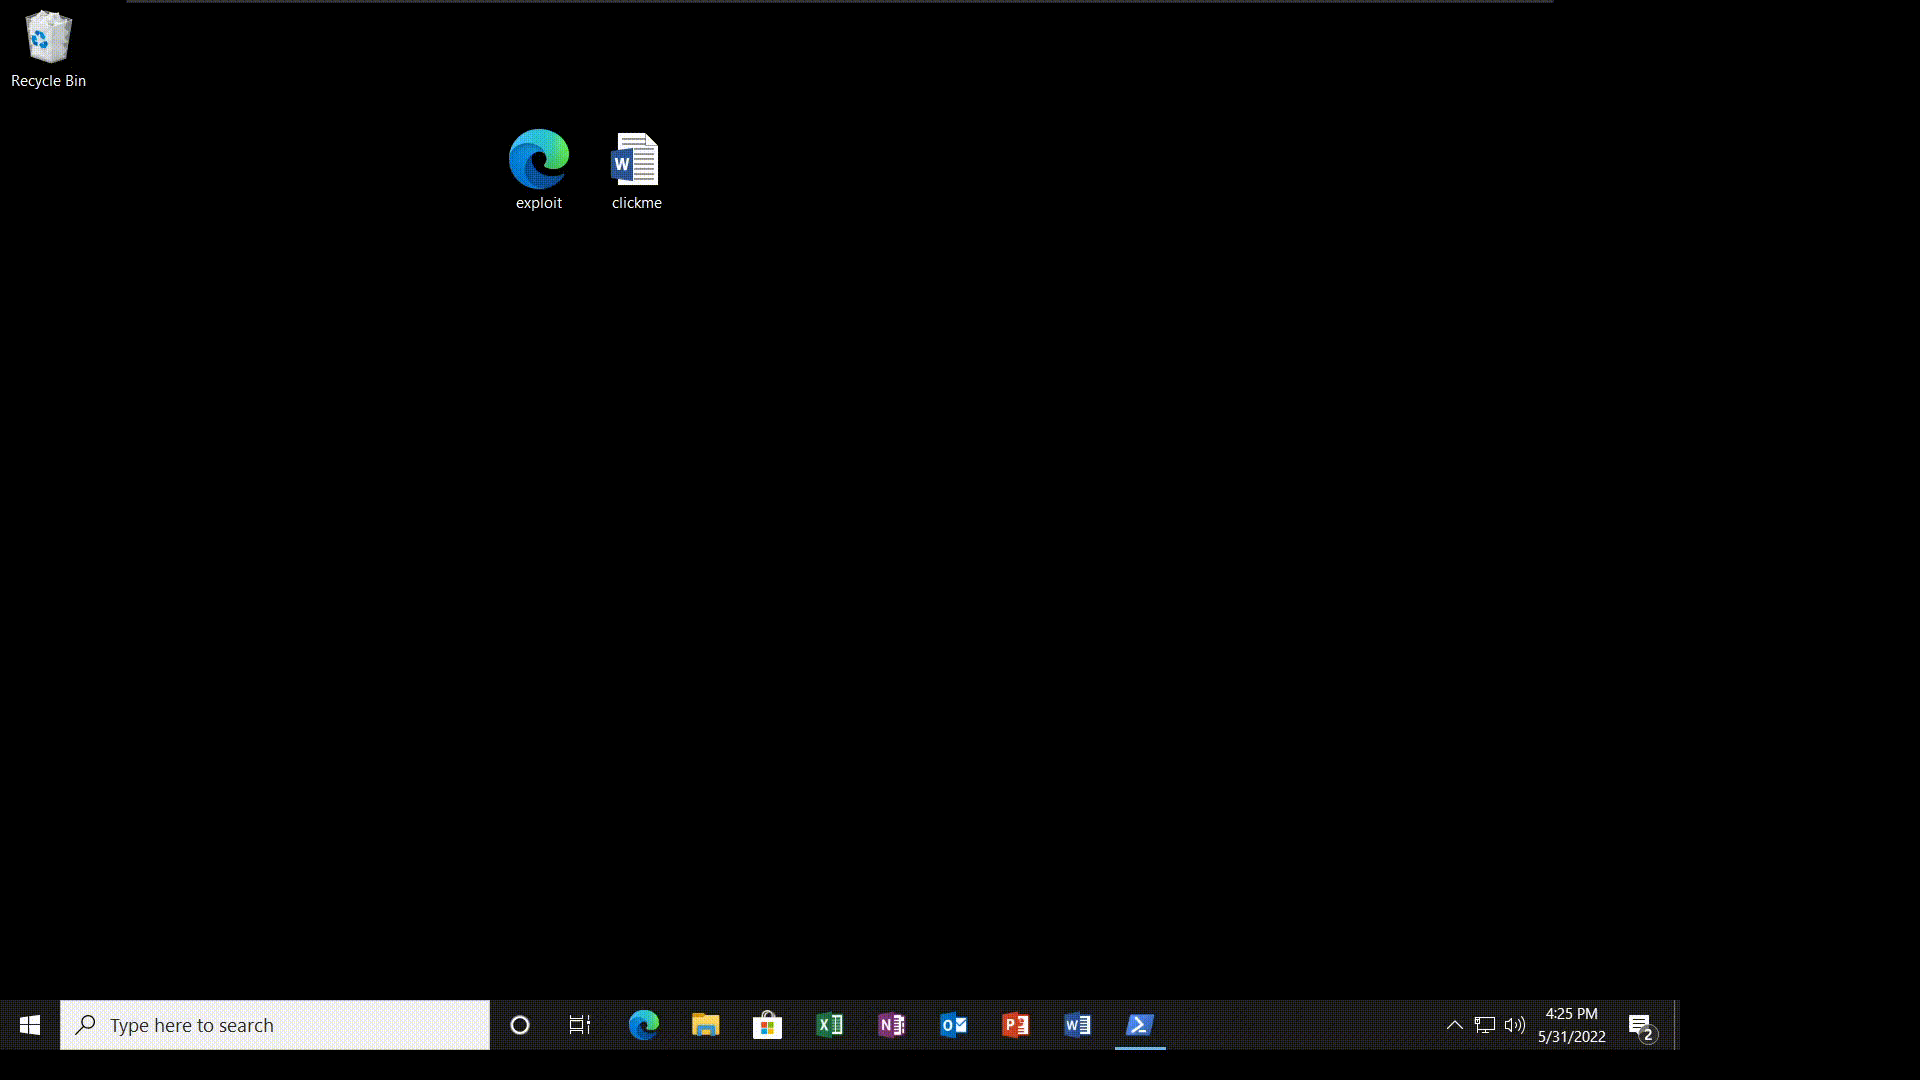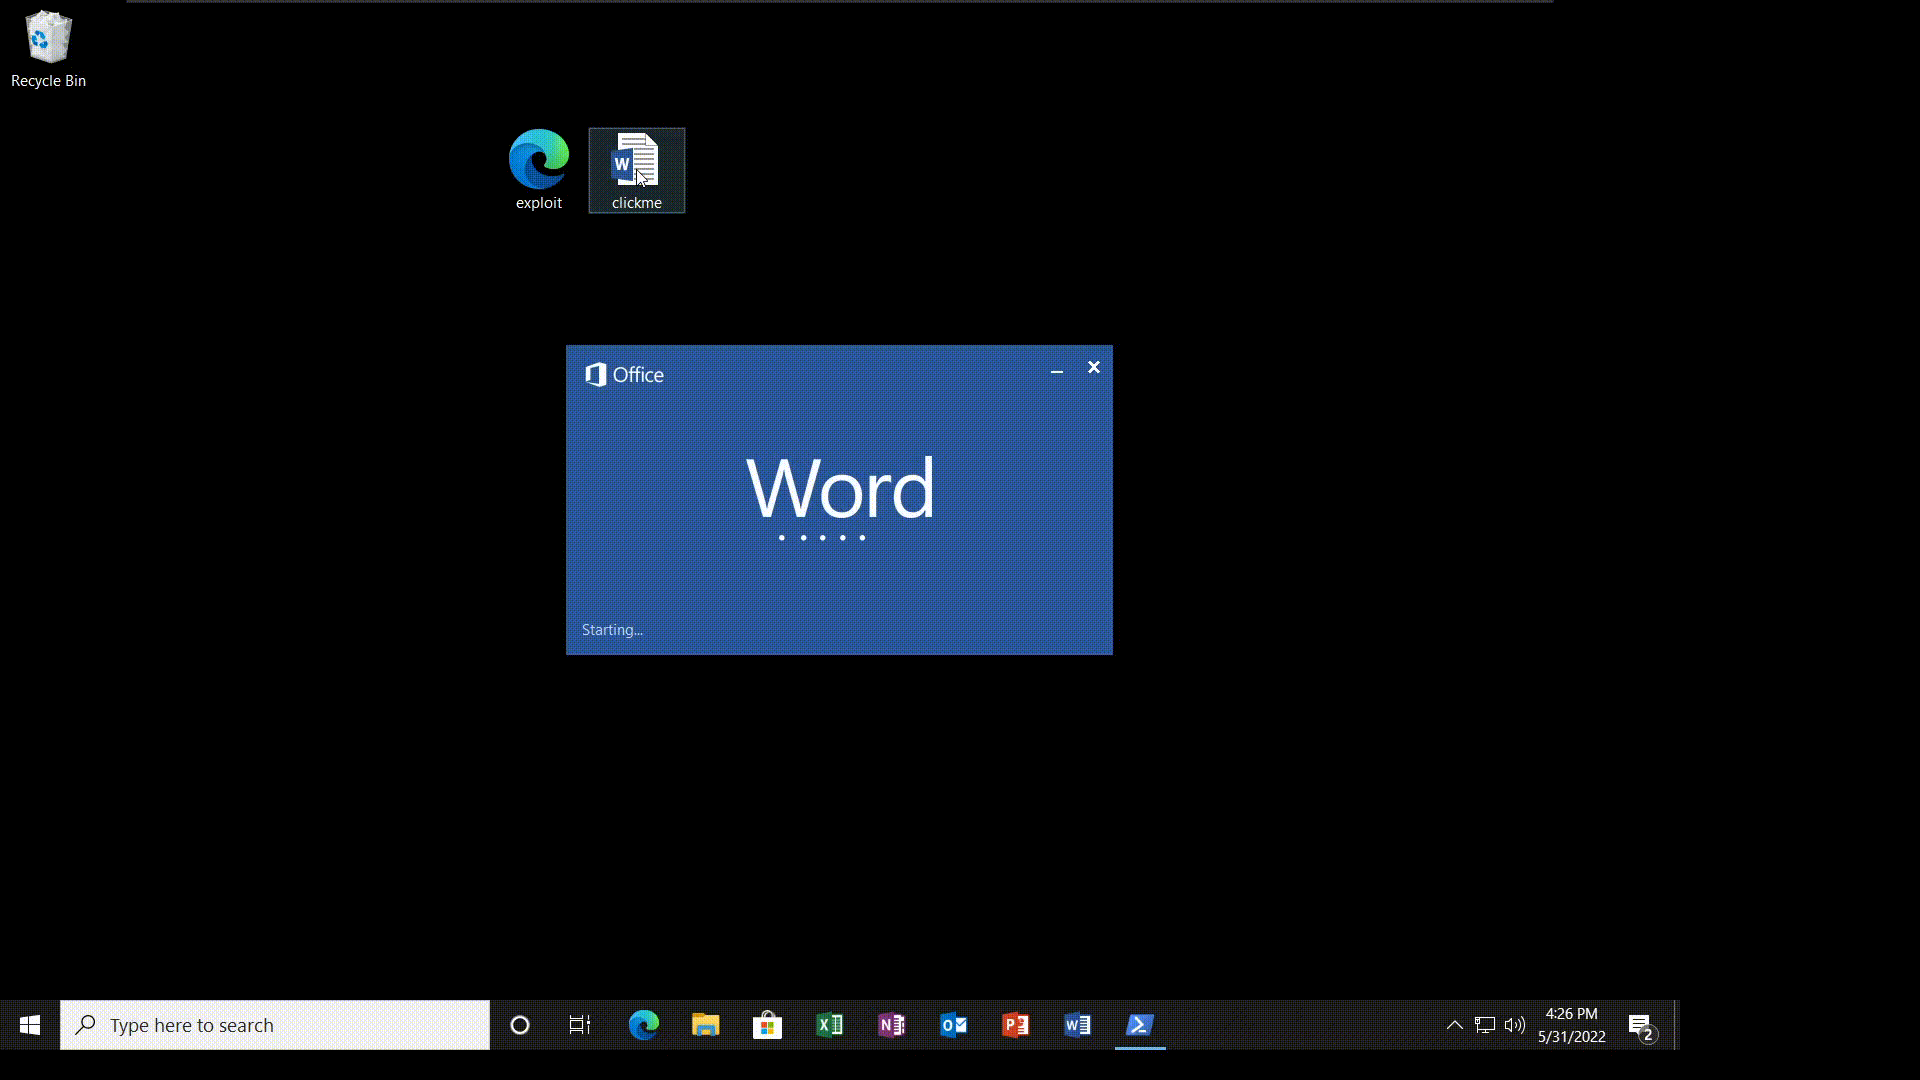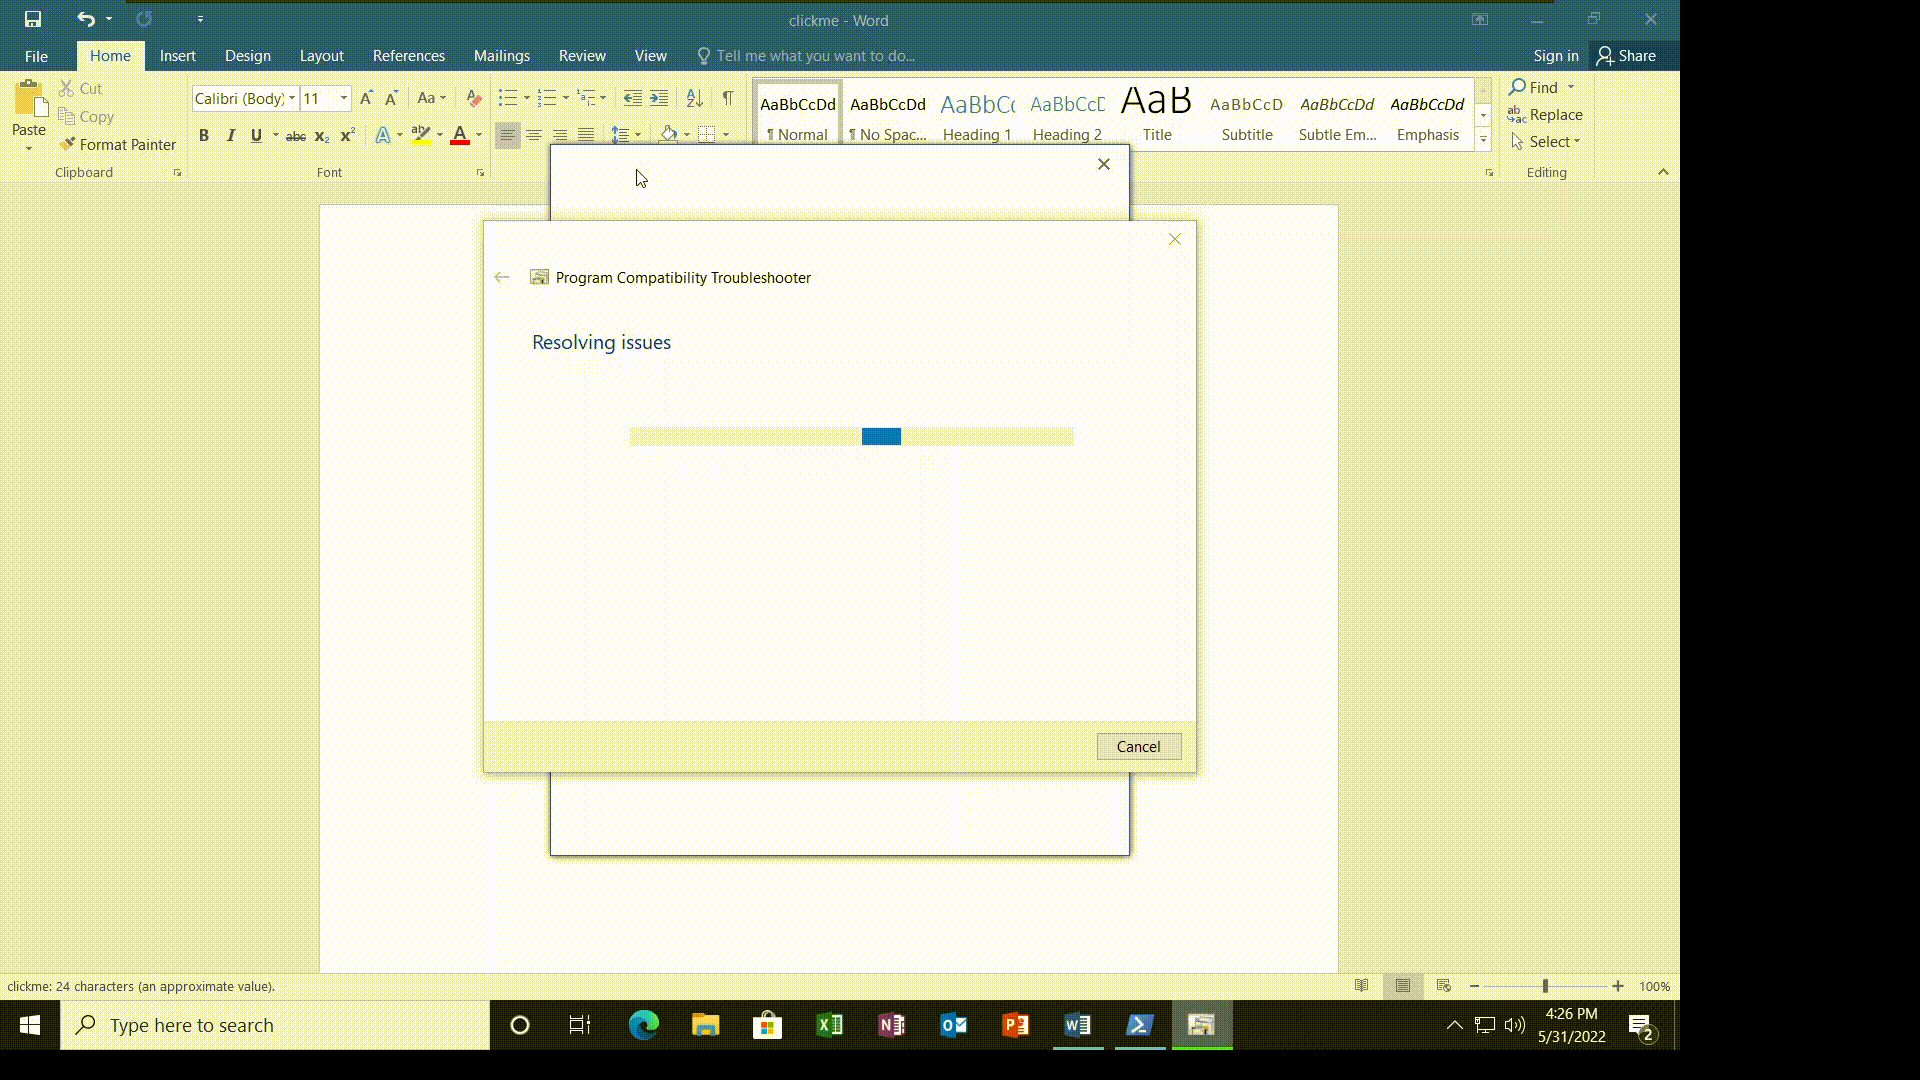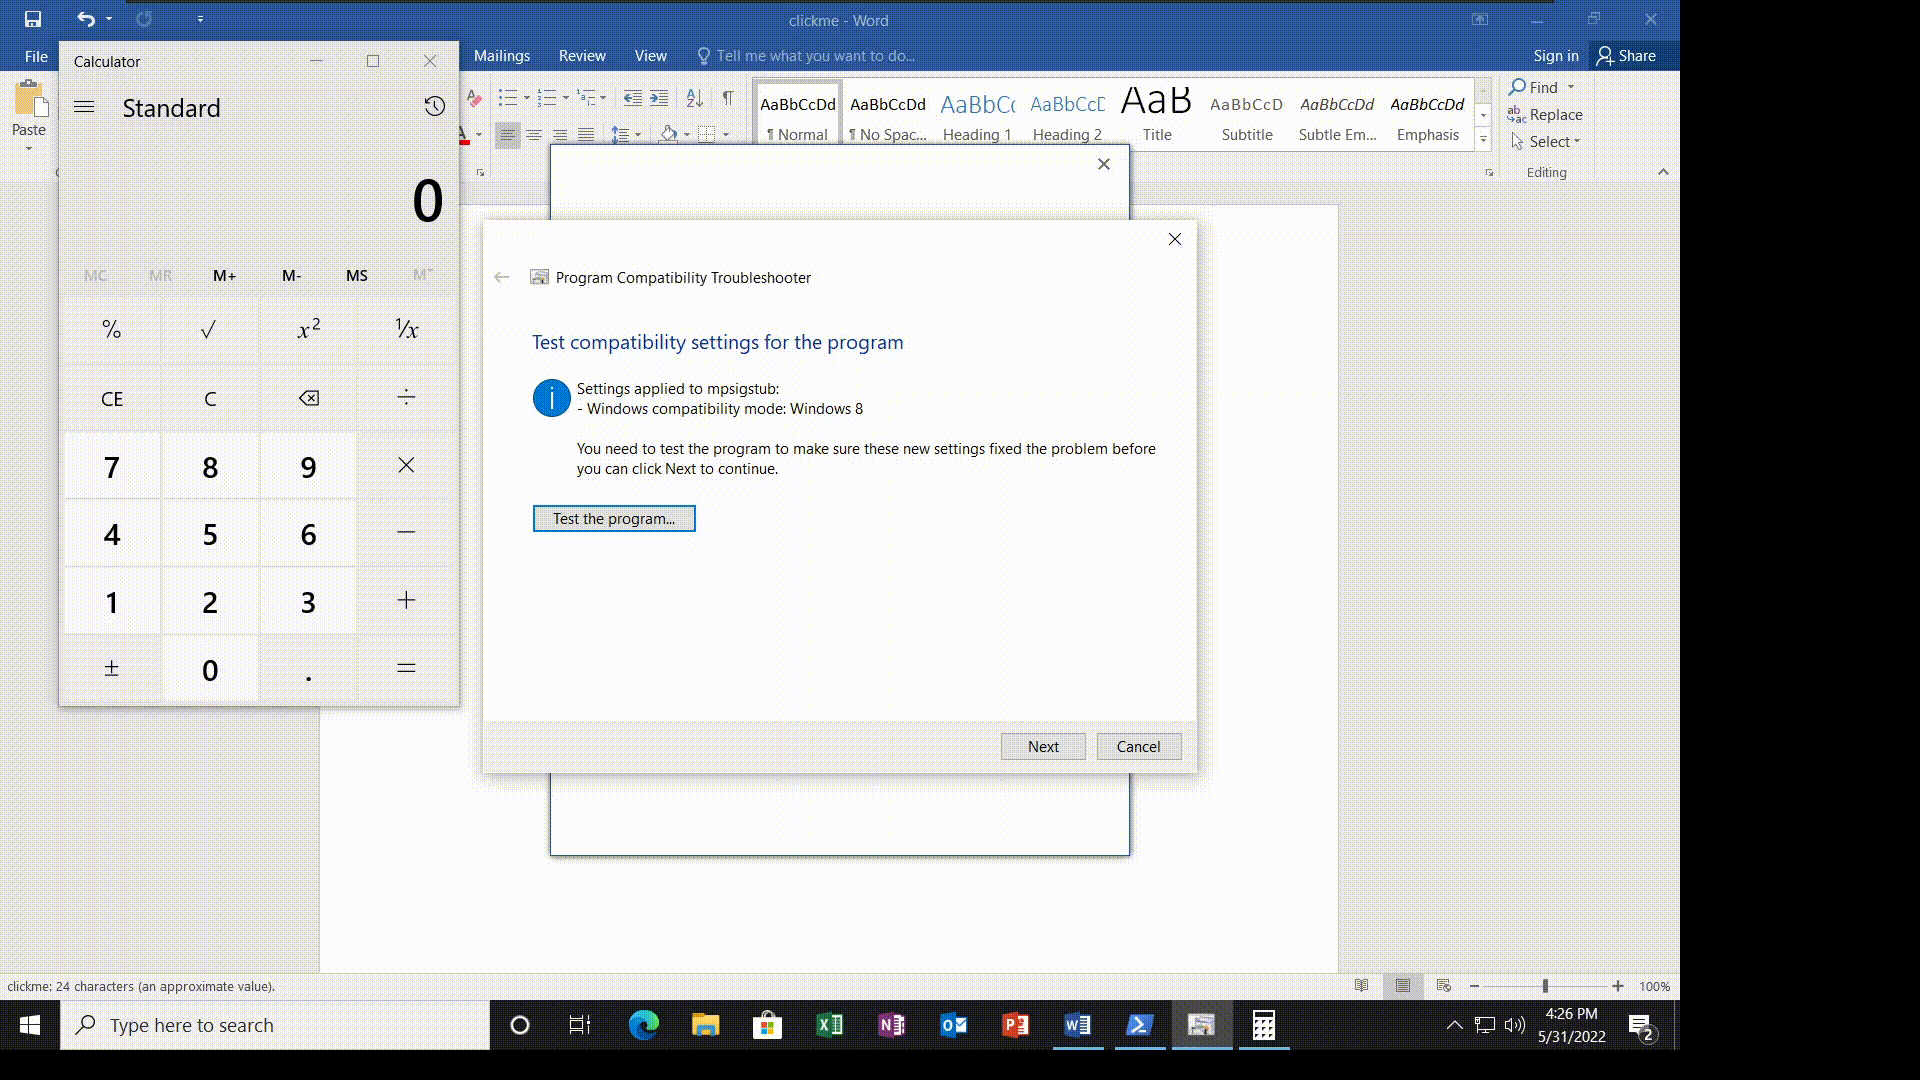
 aslitsecurity/cve-2021-40444_builders
This repo contain builders of cab file, html file, and docx file for CVE-2021-40444 exploit
 mrd0x/webview2-cookie-stealer
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
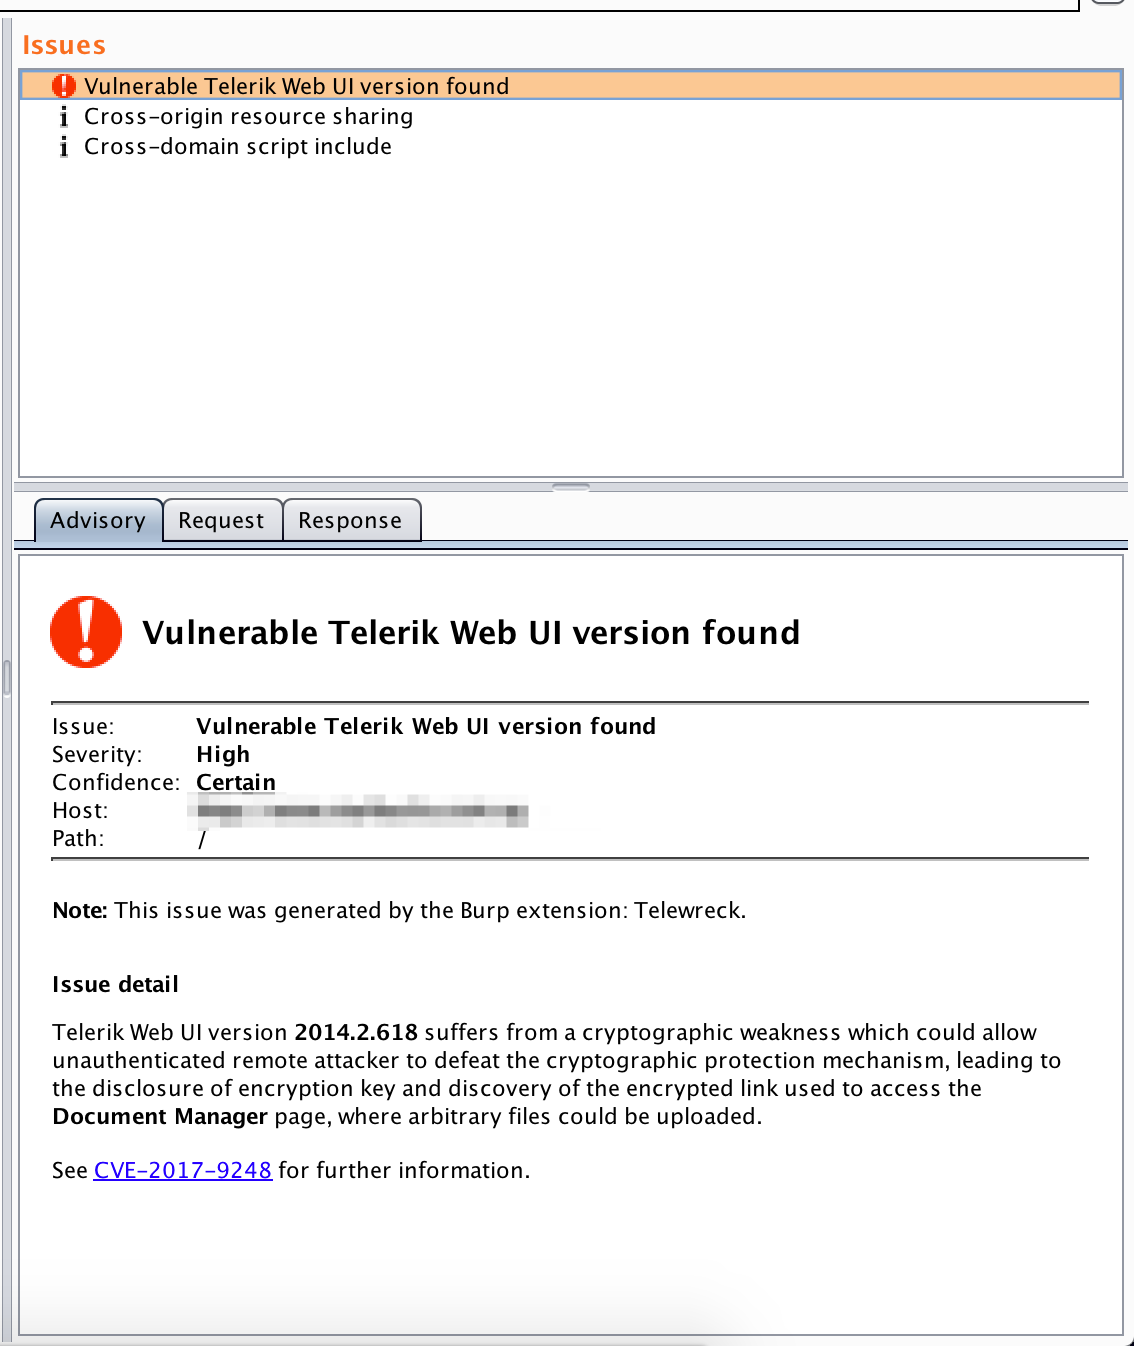 capt-meelo/telewreck
A Burp extension to detect and exploit versions of Telerik Web UI vulnerable to CVE-2017-9248.
 appsecco/dvcsharp-api
Damn Vulnerable C# Application (API)
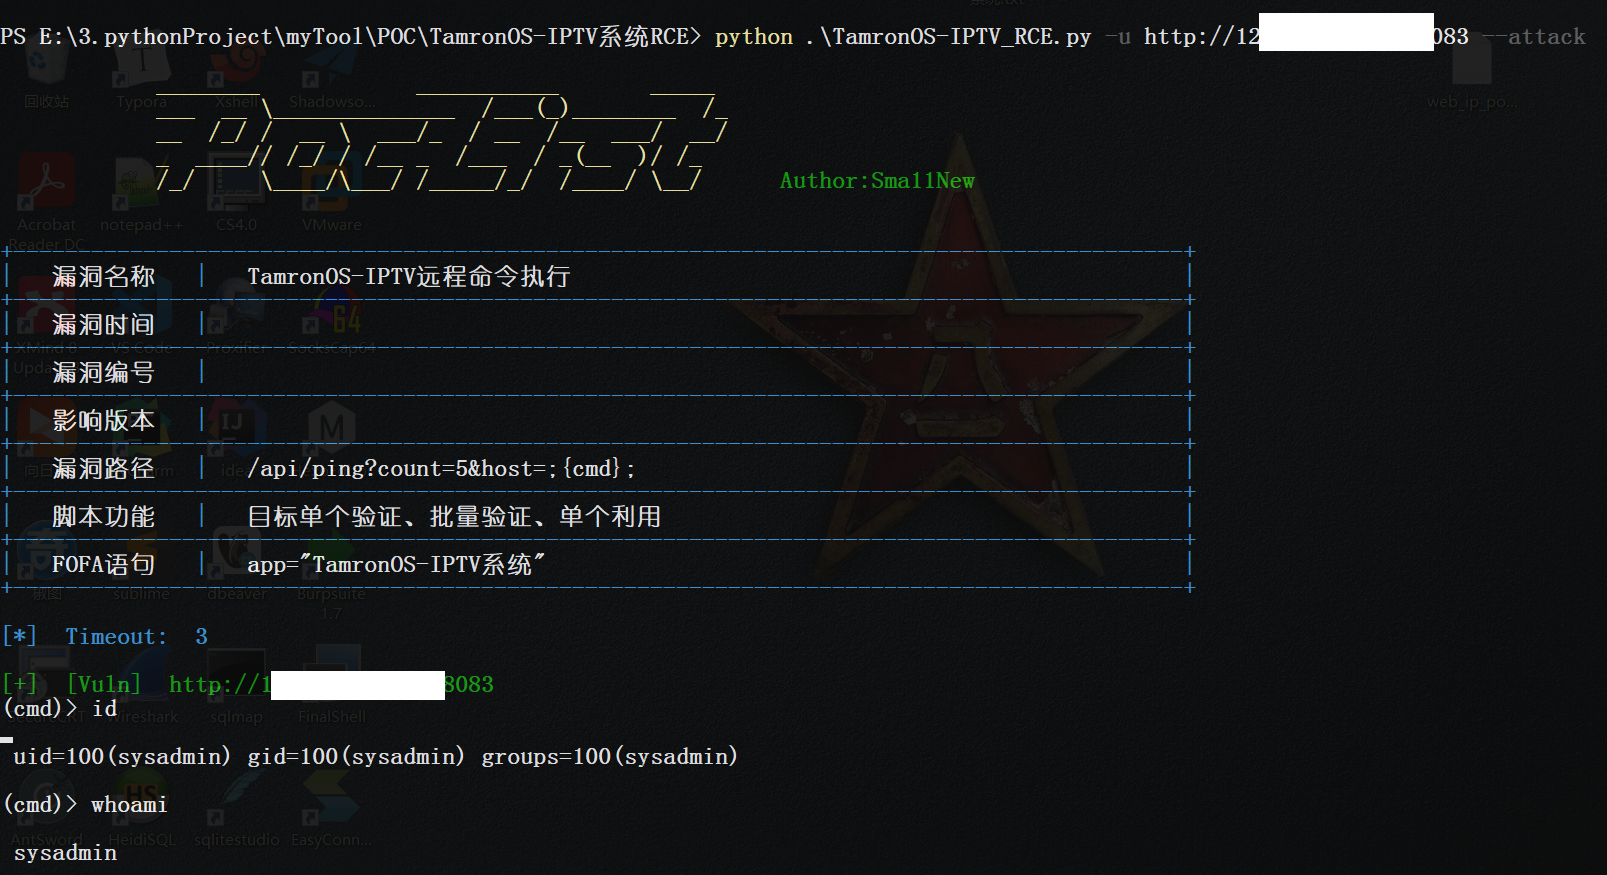 sma11new/poclist
漏洞POC、EXP合集,持续更新。Apache Druid-任意文件读取(CVE-2021-36749)、ConfluenceRCE(CVE-2021-26084)、ZeroShell防火墙RCE(CVE-2019-12725)、ApacheSolr任意文件读取、蓝凌OA任意文件读取、phpStud…
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…
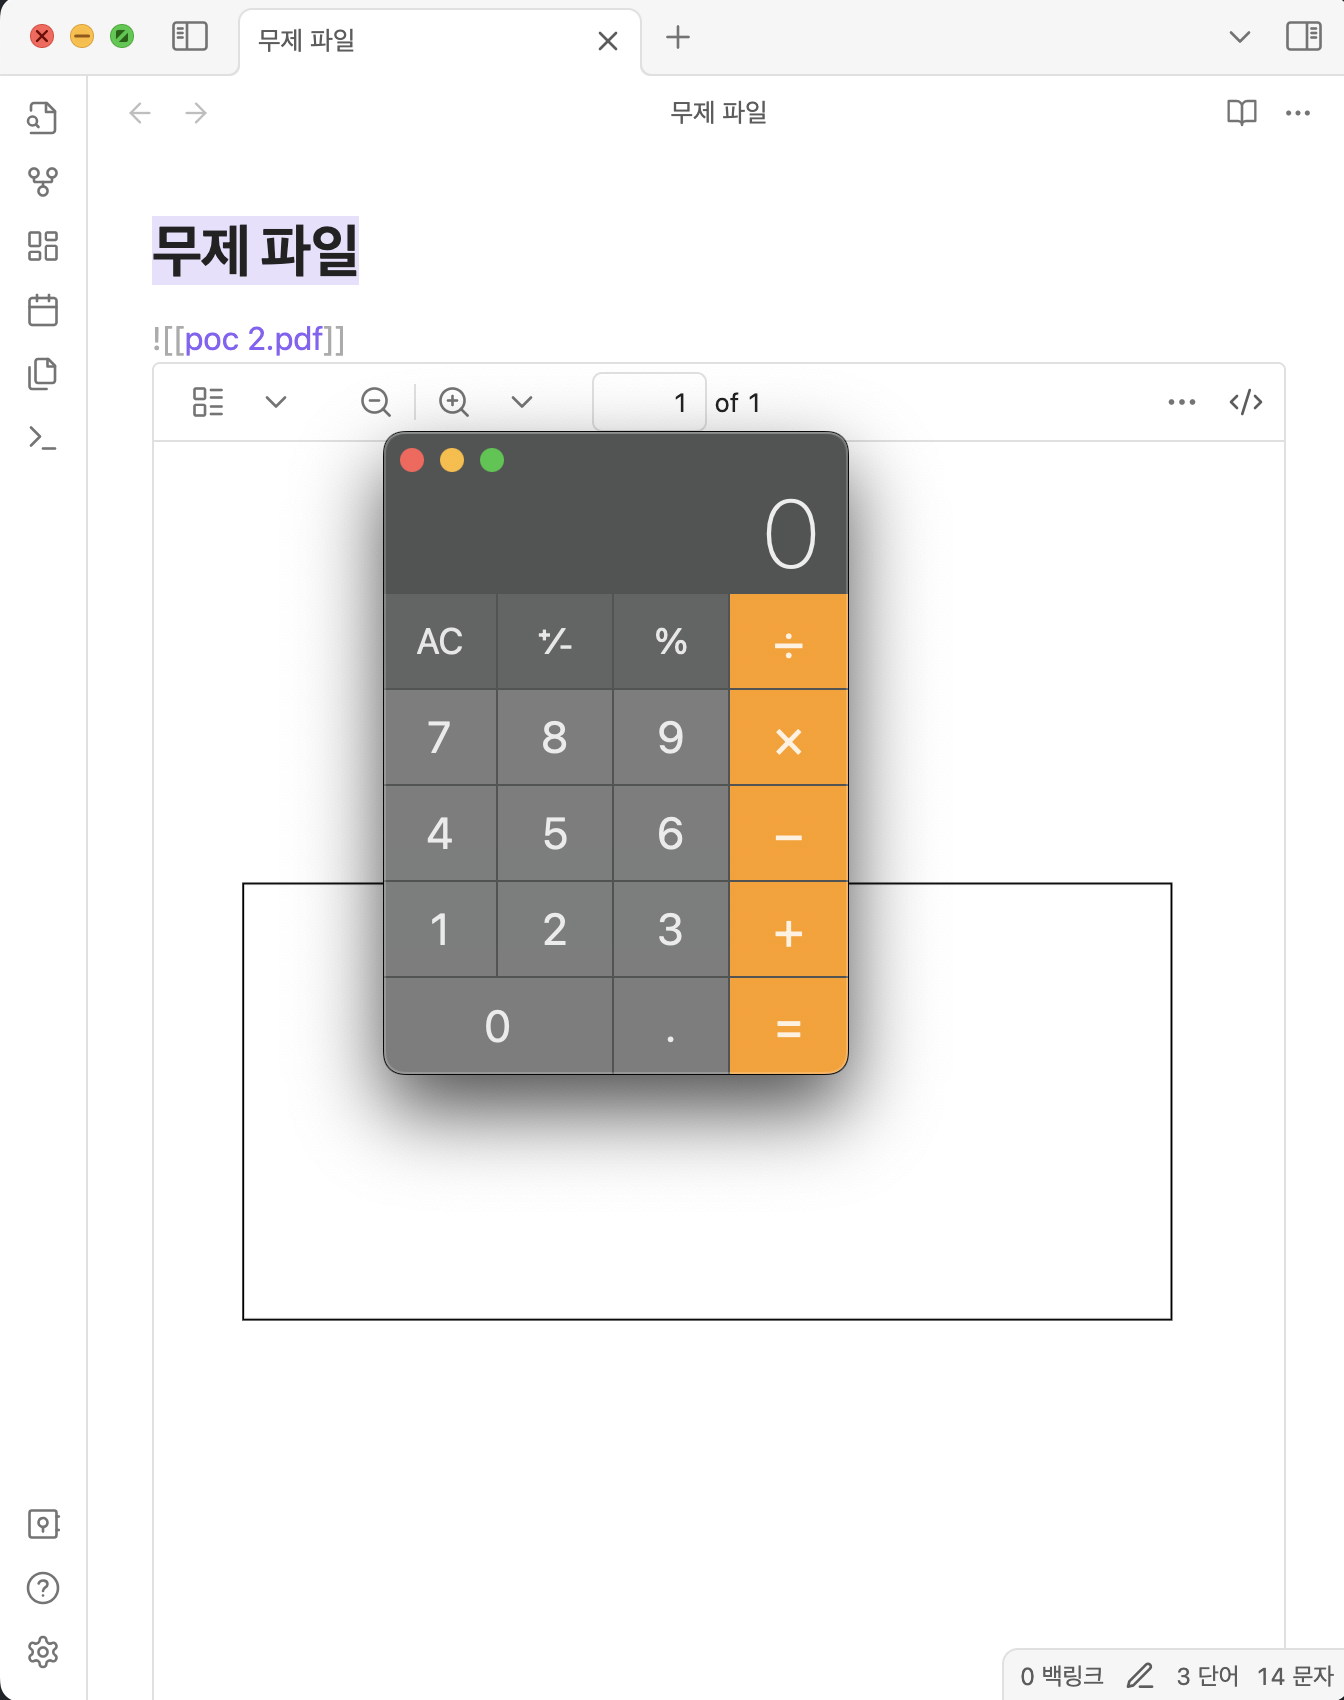 lourc0d3/cve-2024-4367-poc
CVE-2024-4367 & CVE-2024-34342 Proof of Concept
 theori-io/chakra-2016-11
Proof-of-Concept exploit for Edge bugs (CVE-2016-7200 & CVE-2016-7201)
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
 mr-r3bot/gitlab-cve-2021-22205
Unauthenticated remote code execution exploit for GitLab versions < 13.10.3, leveraging ExifTool DjVu annotation parsing to execute arbitrary…
 esmog/nodexp
NodeXP - A Server Side Javascript Injection tool capable of detecting and exploiting Node.js vulnerabilities
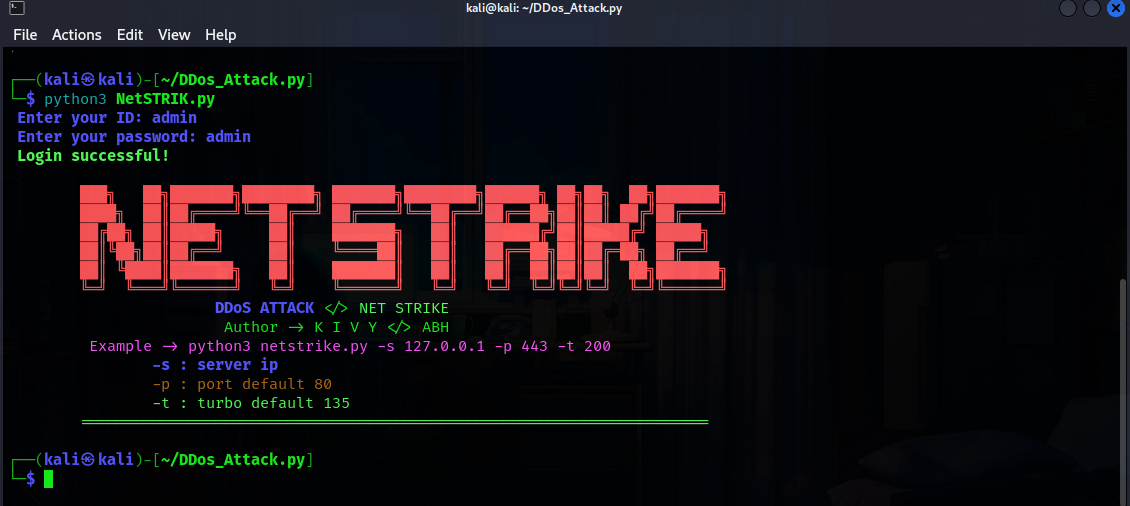 akashblackhat/ddos_attack.py
NetSTRIK is a powerful DDoS (Distributed Denial of Service) attack tool that simulates heavy traffic to test the robustness and security of servers,…
 mdp/linkedin-extension-fingerprinting
Documents and identifies 2,953 Chrome extensions silently probed by LinkedIn, providing tools to fetch extension names and analyze browser…