
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended

 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 dissectmalware/pyonenote
A python library to parse OneNote (.one) files
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
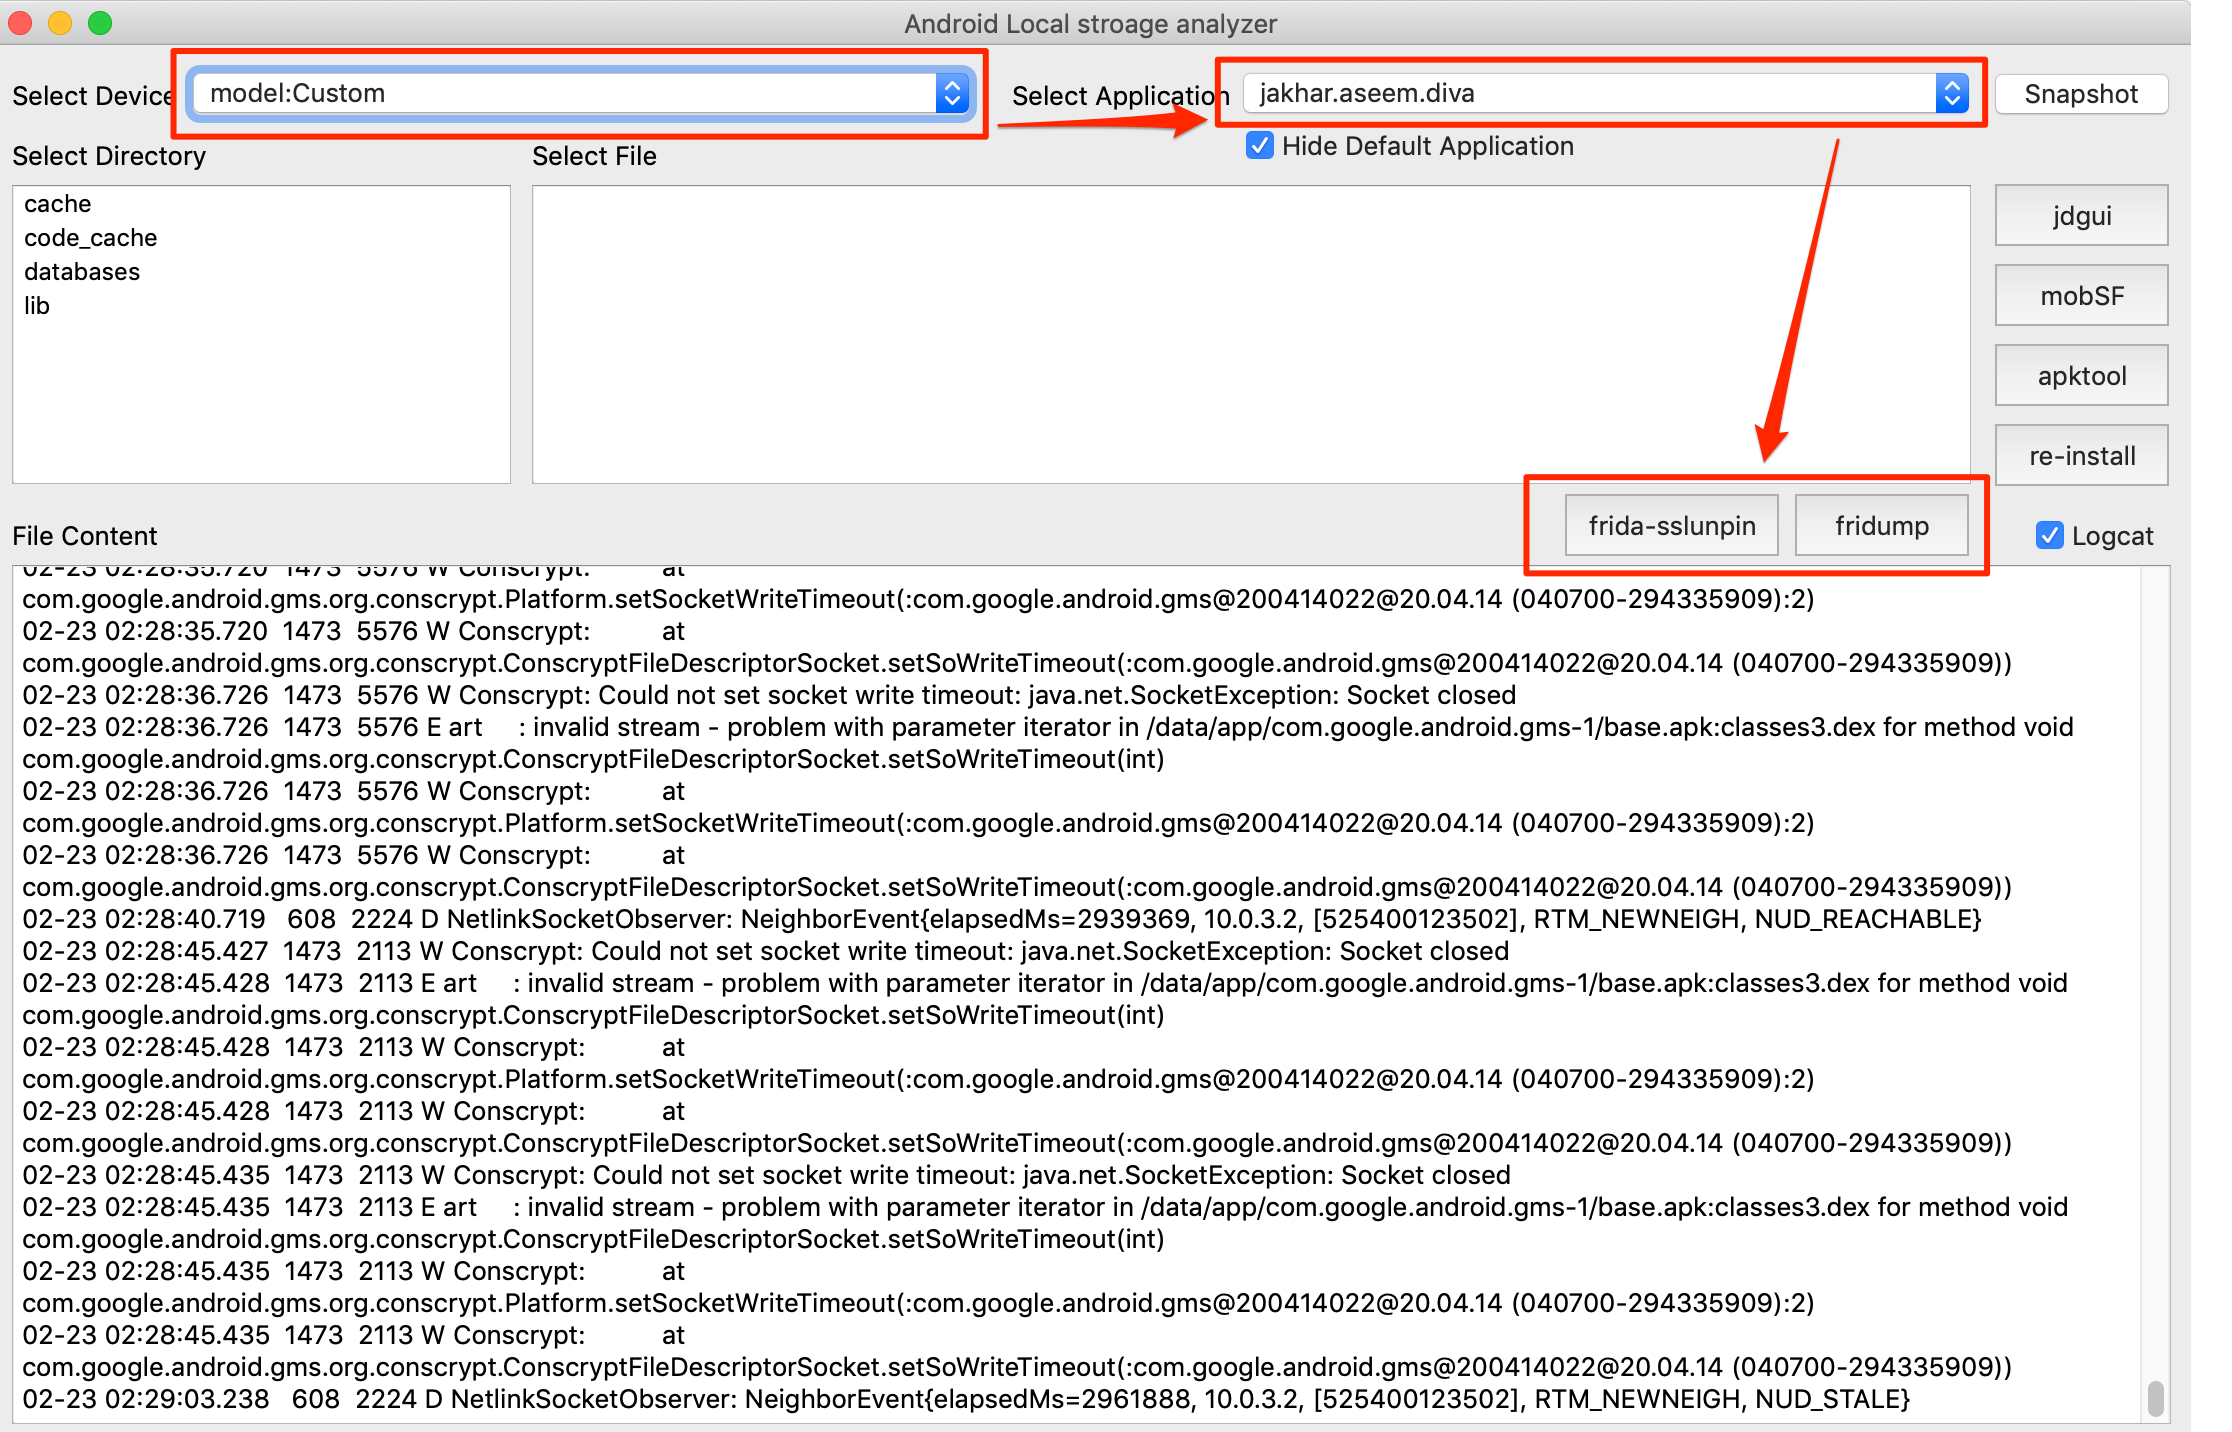 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 santhreal/keyhog
Open-source secret scanner in Rust
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 neo23x0/yara-performance-guidelines
A guide on how to write fast and memory friendly YARA rules
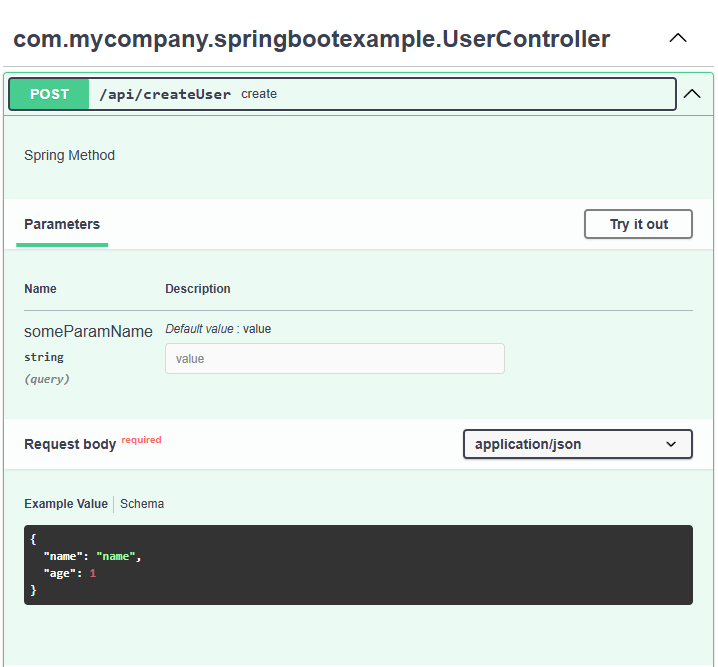 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 owasp/ocsd
OWASP Certified Secure-Software Developer
 ohaswin/pyscan
python dependency vulnerability scanner, written in Rust.
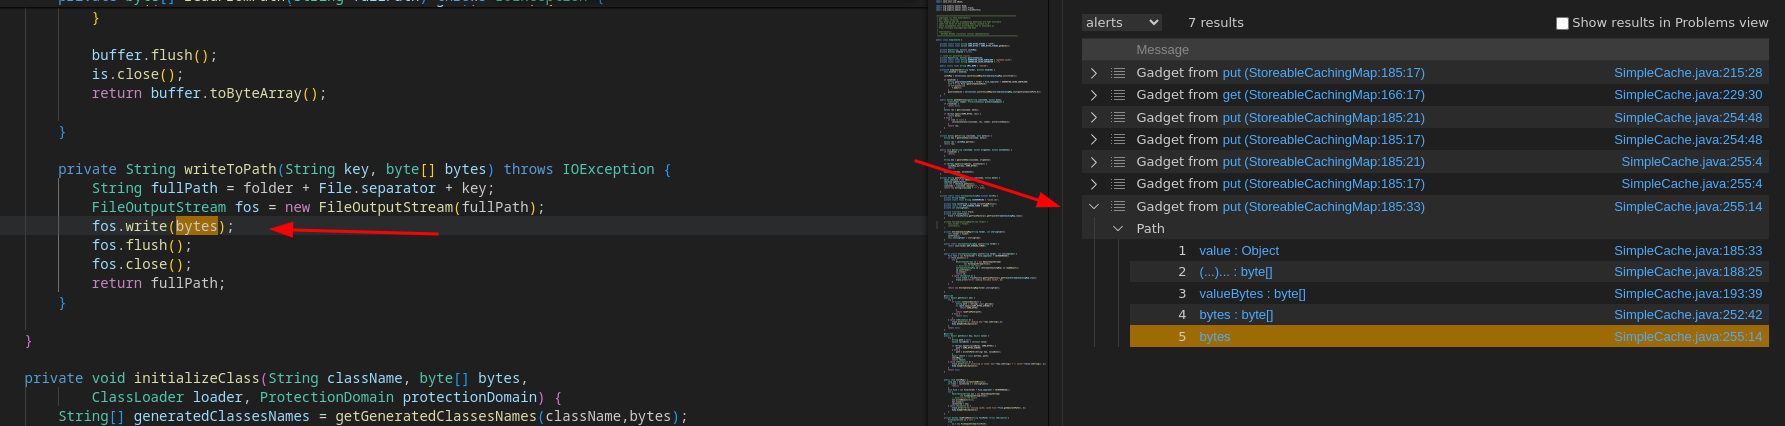 synacktiv/qlinspector
Finding Java/C# gadget chains with CodeQL
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
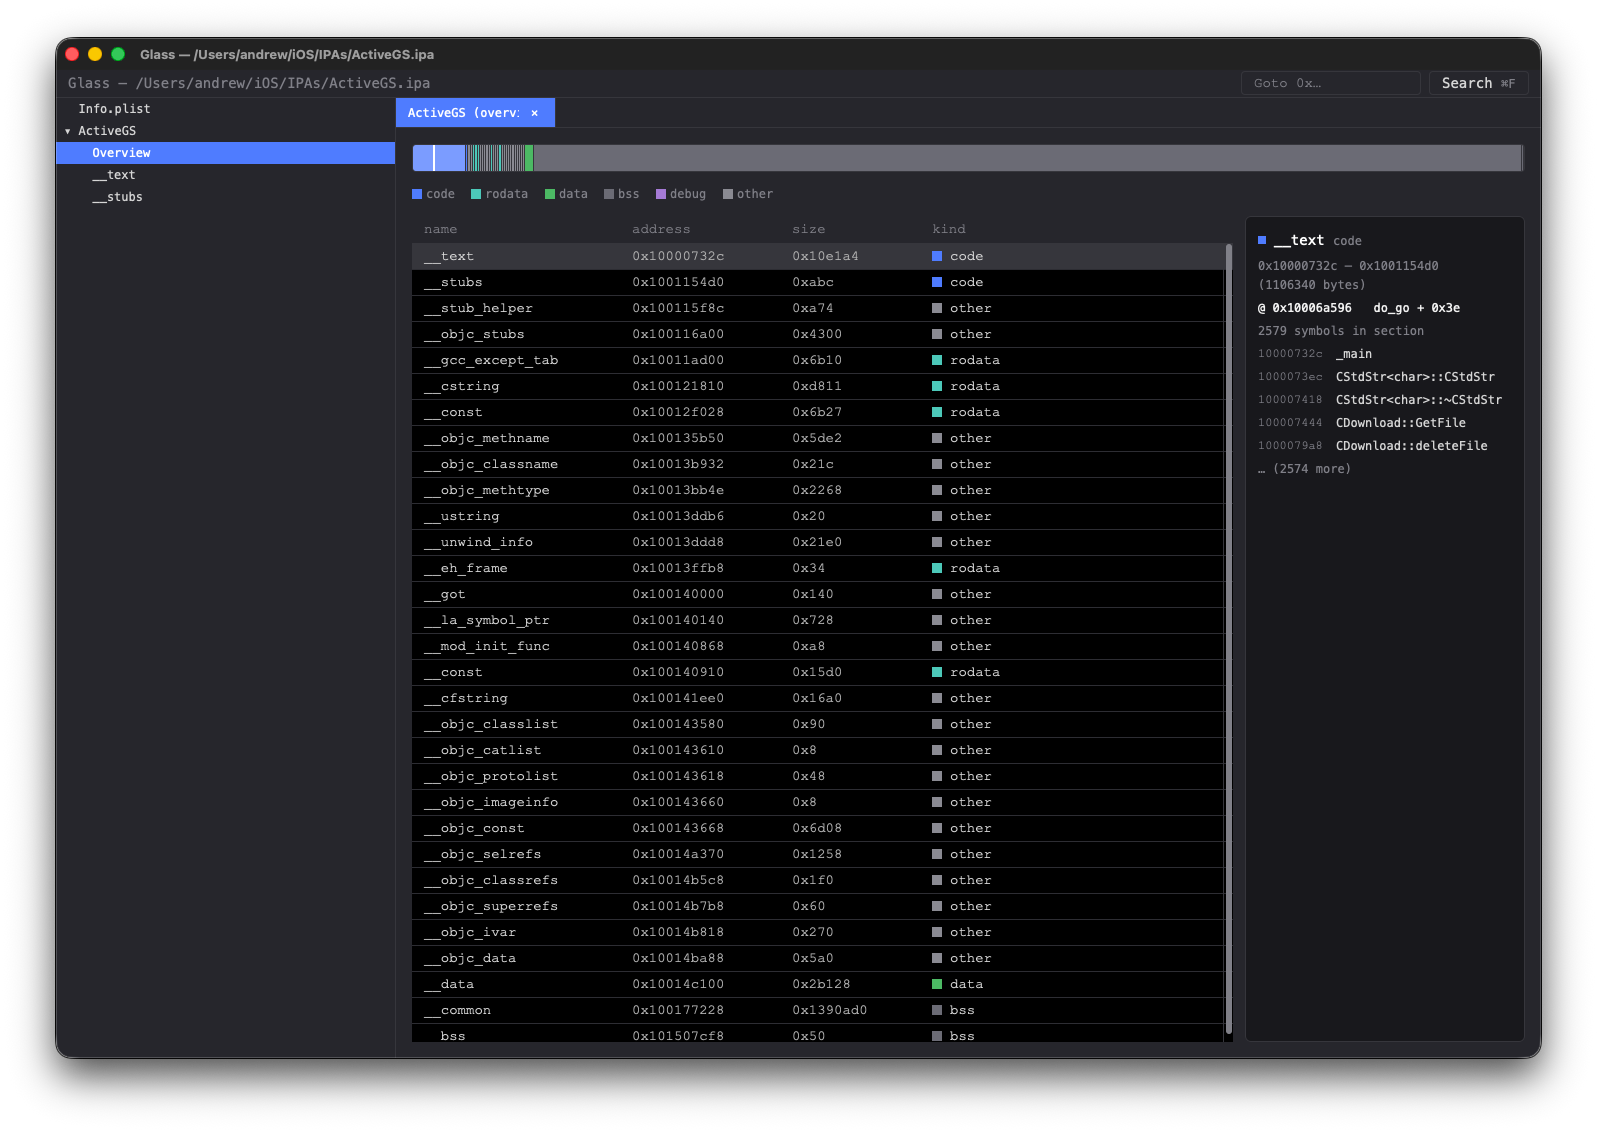 azw413/glass
Glass - a fast and free IDA Pro alternative
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 sfaci/masc
A Web Malware Scanner
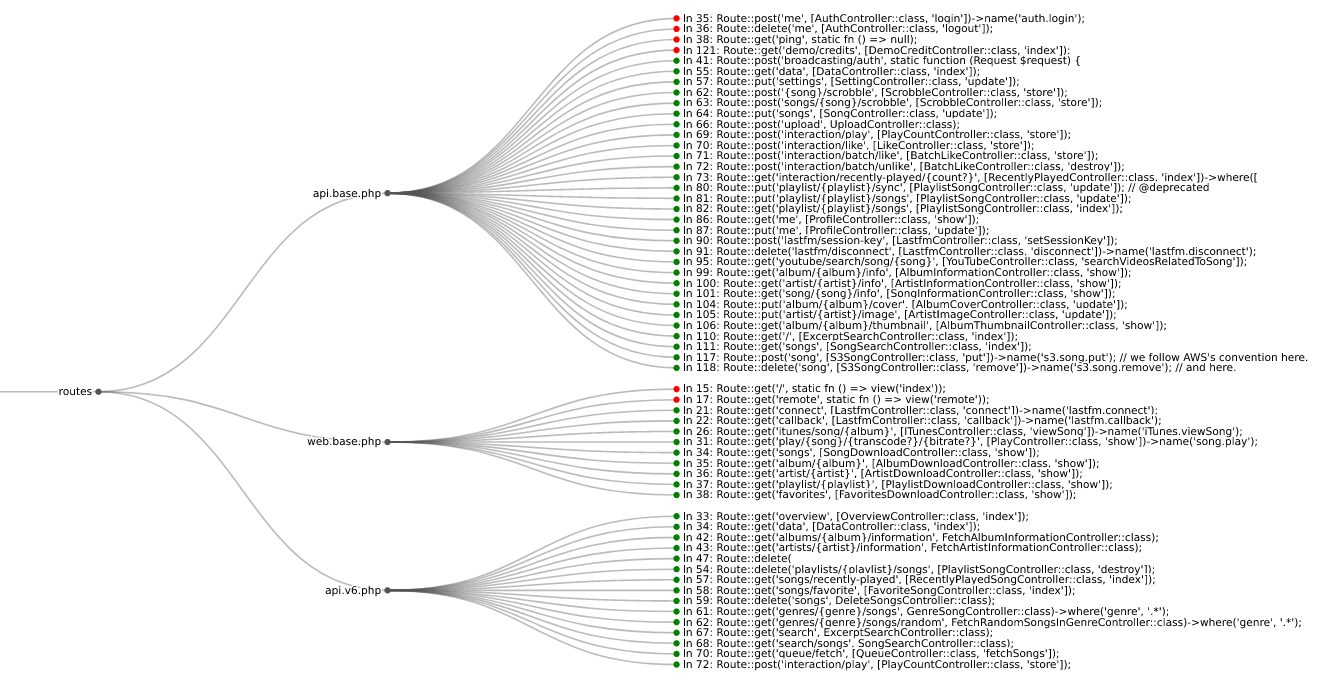 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.








