
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
QLinspector — Finding Java/C# gadget chains with CodeQL | Kitploit

Tools/GitHubGitHub/synacktiv/qlinspector
Static AnalysisVulnerability AnalysisCode AnalysisExploitationPayload Development
GitHubsynacktiv/qlinspector

QLinspector

Finding Java/C# gadget chains with CodeQL

View Repository
18822291 month agoReviewed by Kitploit
Share

QLinspector

Finding Java/C# gadget chains with CodeQL. More information in our article

Installation

Clone the repo

$ git clone https://github.com/synacktiv/QLinspector.git

Search for gadgets:

$ codeql database analyze log4j --format=sarif-latest --output=log4j.sarif --search-path=./QLinspector/ synacktiv/qlinspector-java-queries

Queries

QLinspector.ql

The main CodeQL query that can be used to find gadget chains.

here is an example with the Aspectj gadget chain:

aspectj

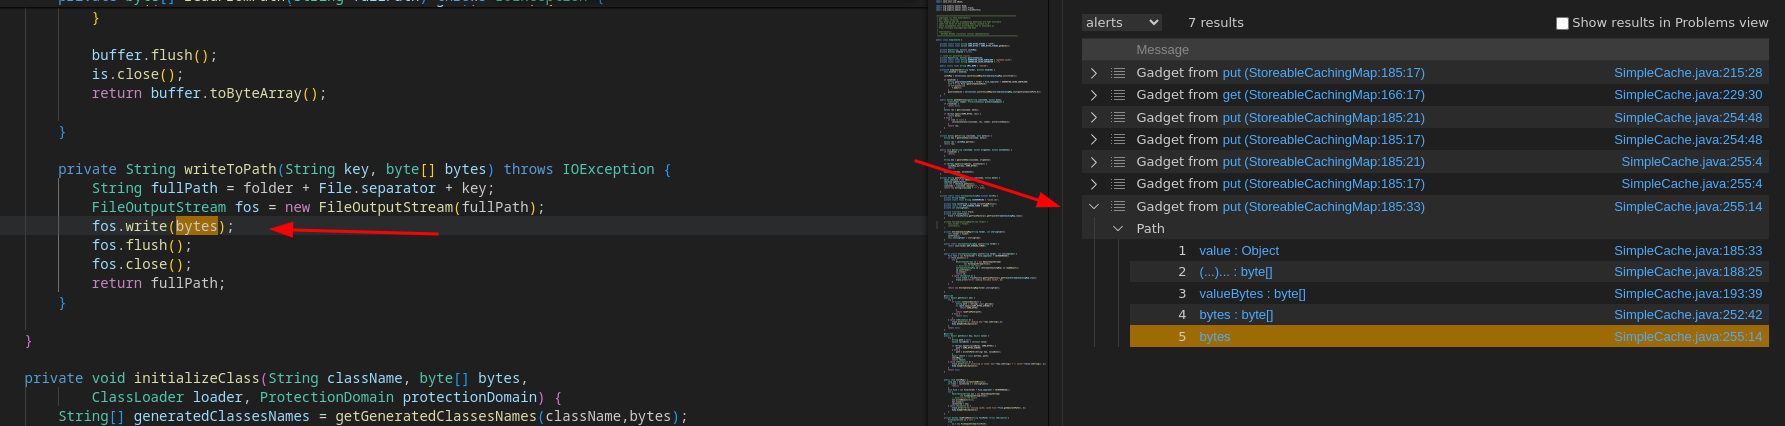
Running the above query can sometimes return a lot of false positives. To filter them the GadgetSanitizer class has been added. You can add conditions to filter out DataFlow::Node:

/**
 * placeholder for adding sanitizing steps
*/
class GadgetSanitizer extends DataFlow::Node {
  GadgetSanitizer() {
    this.getEnclosingCallable().hasName("")
  }
}

QLinspectorOld.ql

Old query that was initially developped. This query do not use the taint model of CodeQL thus it could return different results.

BeanFactoryGadgetFinder.ql

A query that can be used to find new gadget chains based on the org.apache.naming.factory.BeanFactory. The BeanFactory class, allows to create an instance of arbitrary class with default constructor and call any public method with one String parameter.

More information in this blogpost: https://www.veracode.com/blog/research/exploiting-jndi-injections-java


CommonsBeanutilsGadgetFinder.ql

A query that can be used to find alternatives to the getOutputProperties method used in the CommonsBeanutils chain.

More information here:

  • https://www.praetorian.com/blog/relution-remote-code-execution-java-deserialization-vulnerability/
  • https://mogwailabs.de/en/blog/2023/04/look-mama-no-templatesimpl/

ObjectFactoryFinder.ql

A query that can be used to find alternatives to the org.apache.naming.factory.BeanFactory. This could be usefull during JNDI exploitation.

More information in this blogpost: https://www.veracode.com/blog/research/exploiting-jndi-injections-java

Resources

  • https://www.synacktiv.com/publications/finding-gadgets-like-its-2015-part-1.html
  • https://www.synacktiv.com/publications/finding-gadgets-like-its-2015-part-2.html
  • https://www.synacktiv.com/publications/finding-gadgets-like-its-2022.html
  • https://www.synacktiv.com/publications/java-deserialization-tricks
  • https://www.praetorian.com/blog/relution-remote-code-execution-java-deserialization-vulnerability/
  • https://www.veracode.com/blog/research/exploiting-jndi-injections-java

  • https://mogwailabs.de/en/blog/2023/04/look-mama-no-templatesimpl/
  • https://testbnull.medium.com/return-of-the-rhino-analysis-of-mozillarhino-gadgetchain-also-the-writeup-of-hitb-linkextractor-a2074b4ae624
  • https://www.buaq.net/go-53869.html
  • https://b1ue.cn/archives/529.html
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →


