
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended
 cellebrite-labs/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
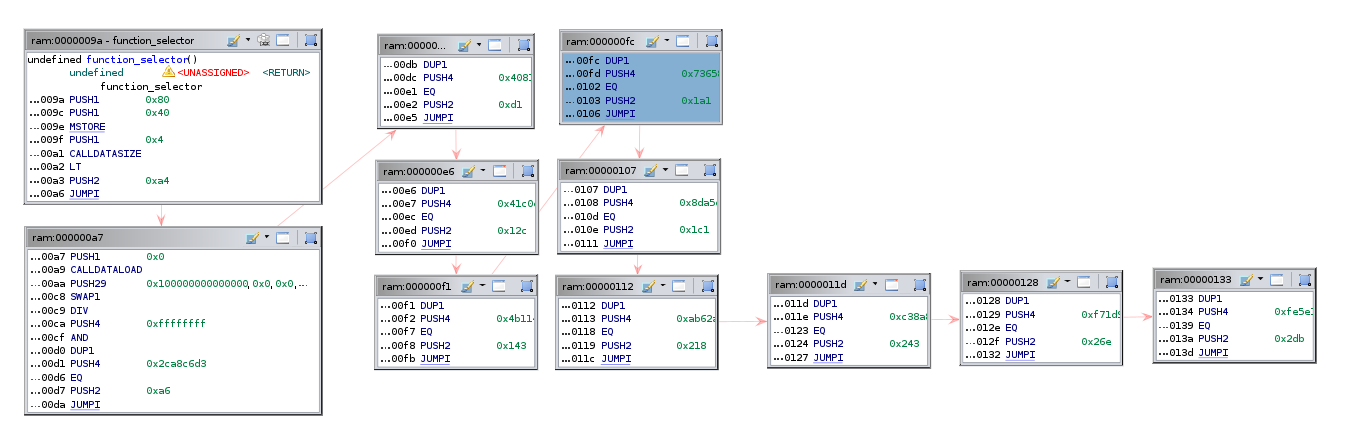 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
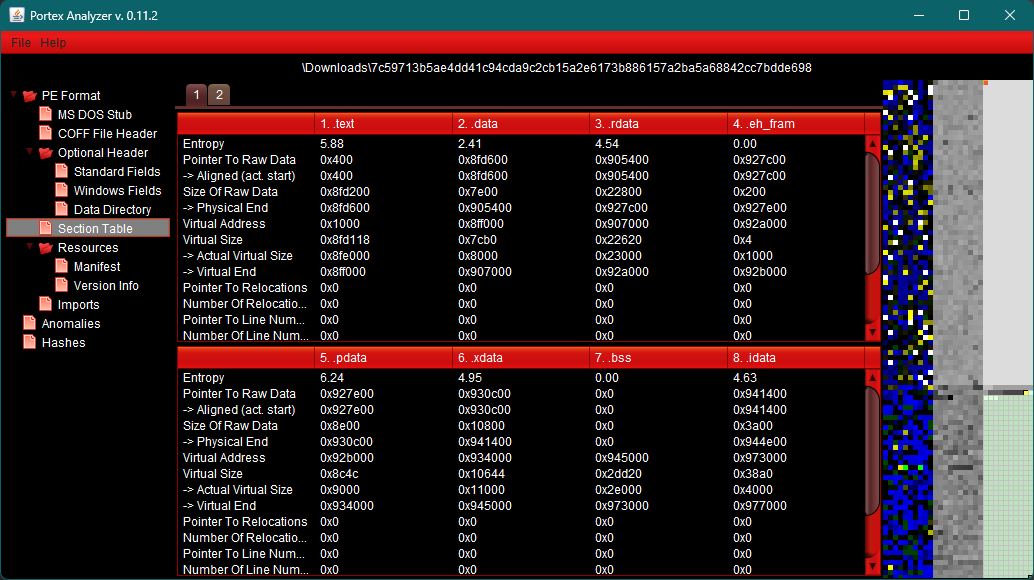 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
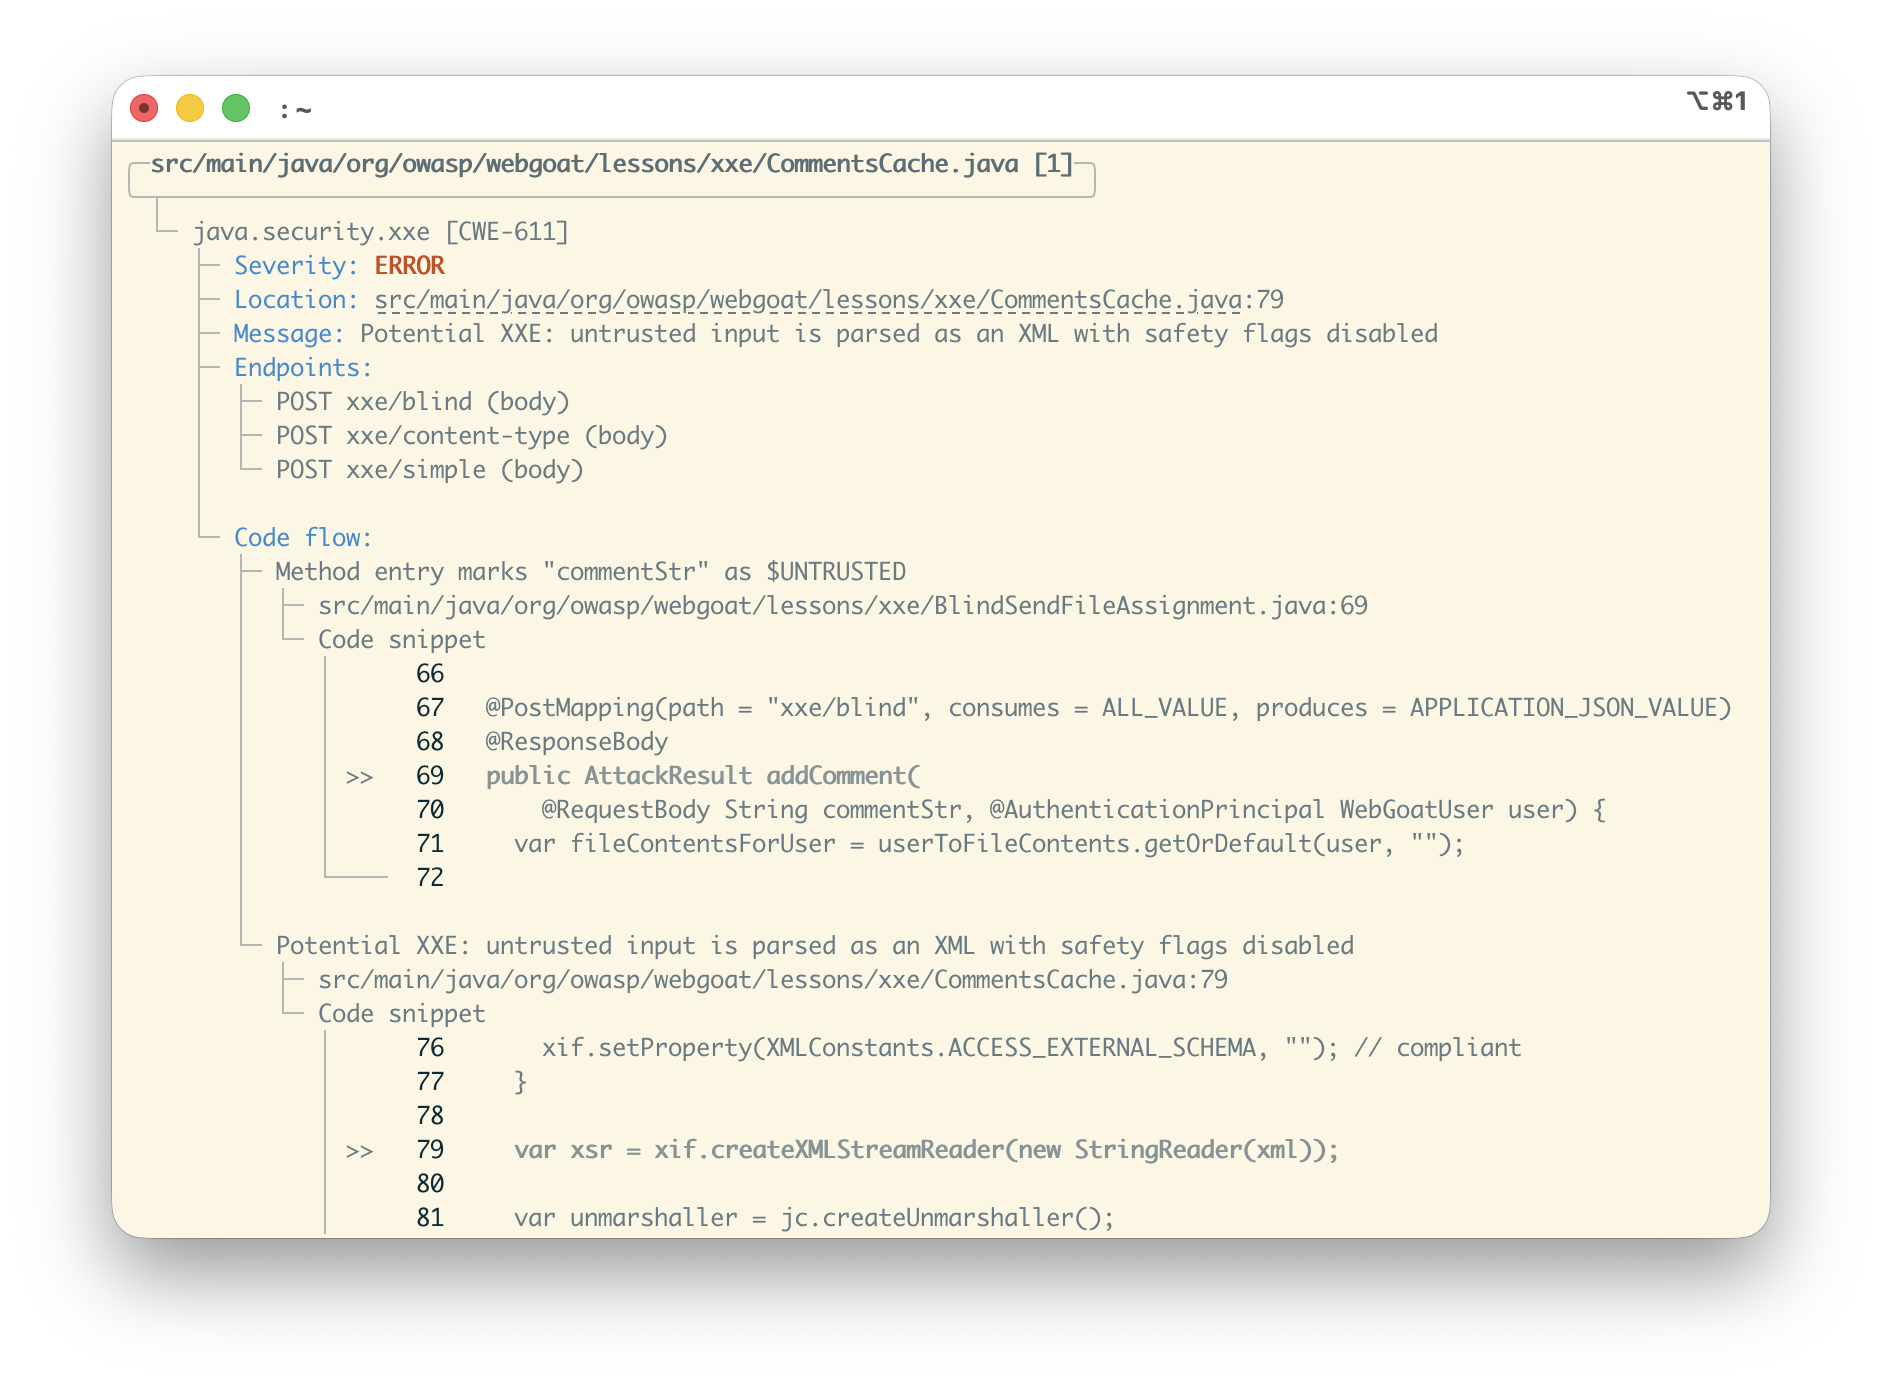 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 cert-polska/malduck
🦆 Malduck is your ducky companion in malware analysis journeys
 florianmattana/sass-king
Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.
 0xpwny/apkatshu
Apkatshu is a Tool for extracting urls , emails , ip address , and interesting data from APK files
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 denuvosoftwaresolutions/gamba
Simplification of General Mixed Boolean-Arithmetic Expressions: GAMBA
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 felixber/findfunc
IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
 delvinru/apk-info
APK full-featured parser








