
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended
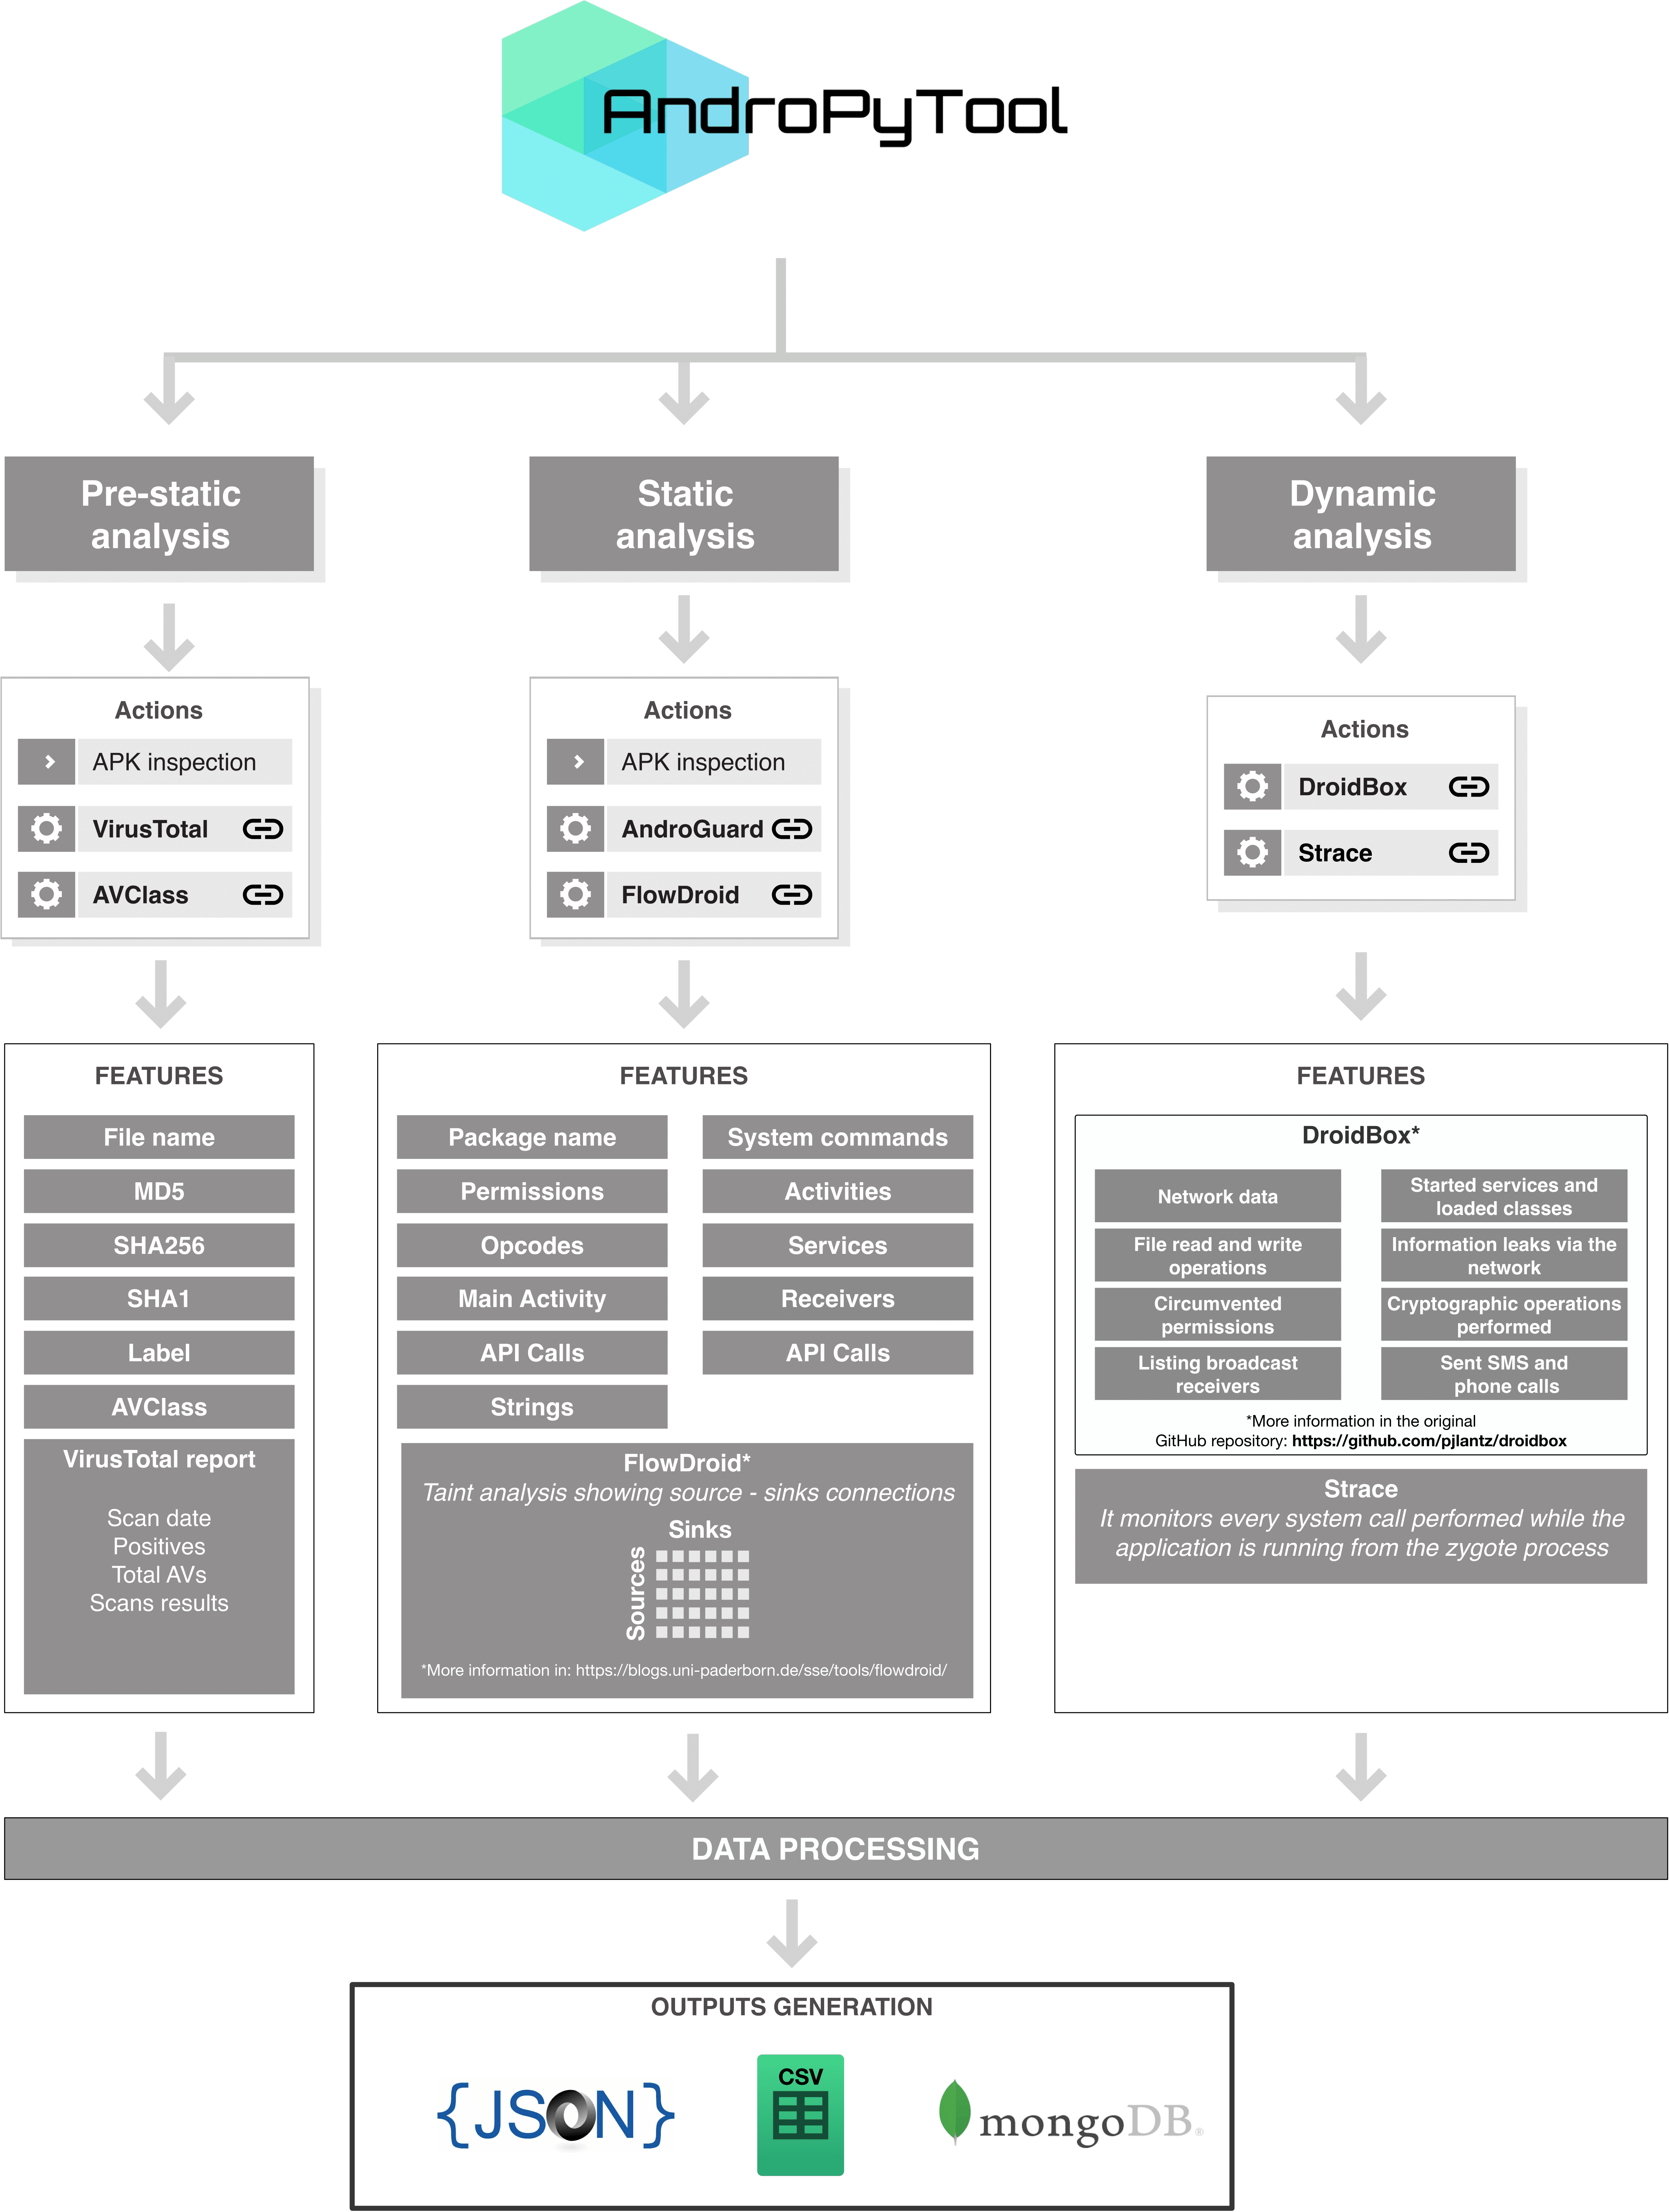
 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 pandare9x/configuration_extractors
Configuration Extractors for Malware
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
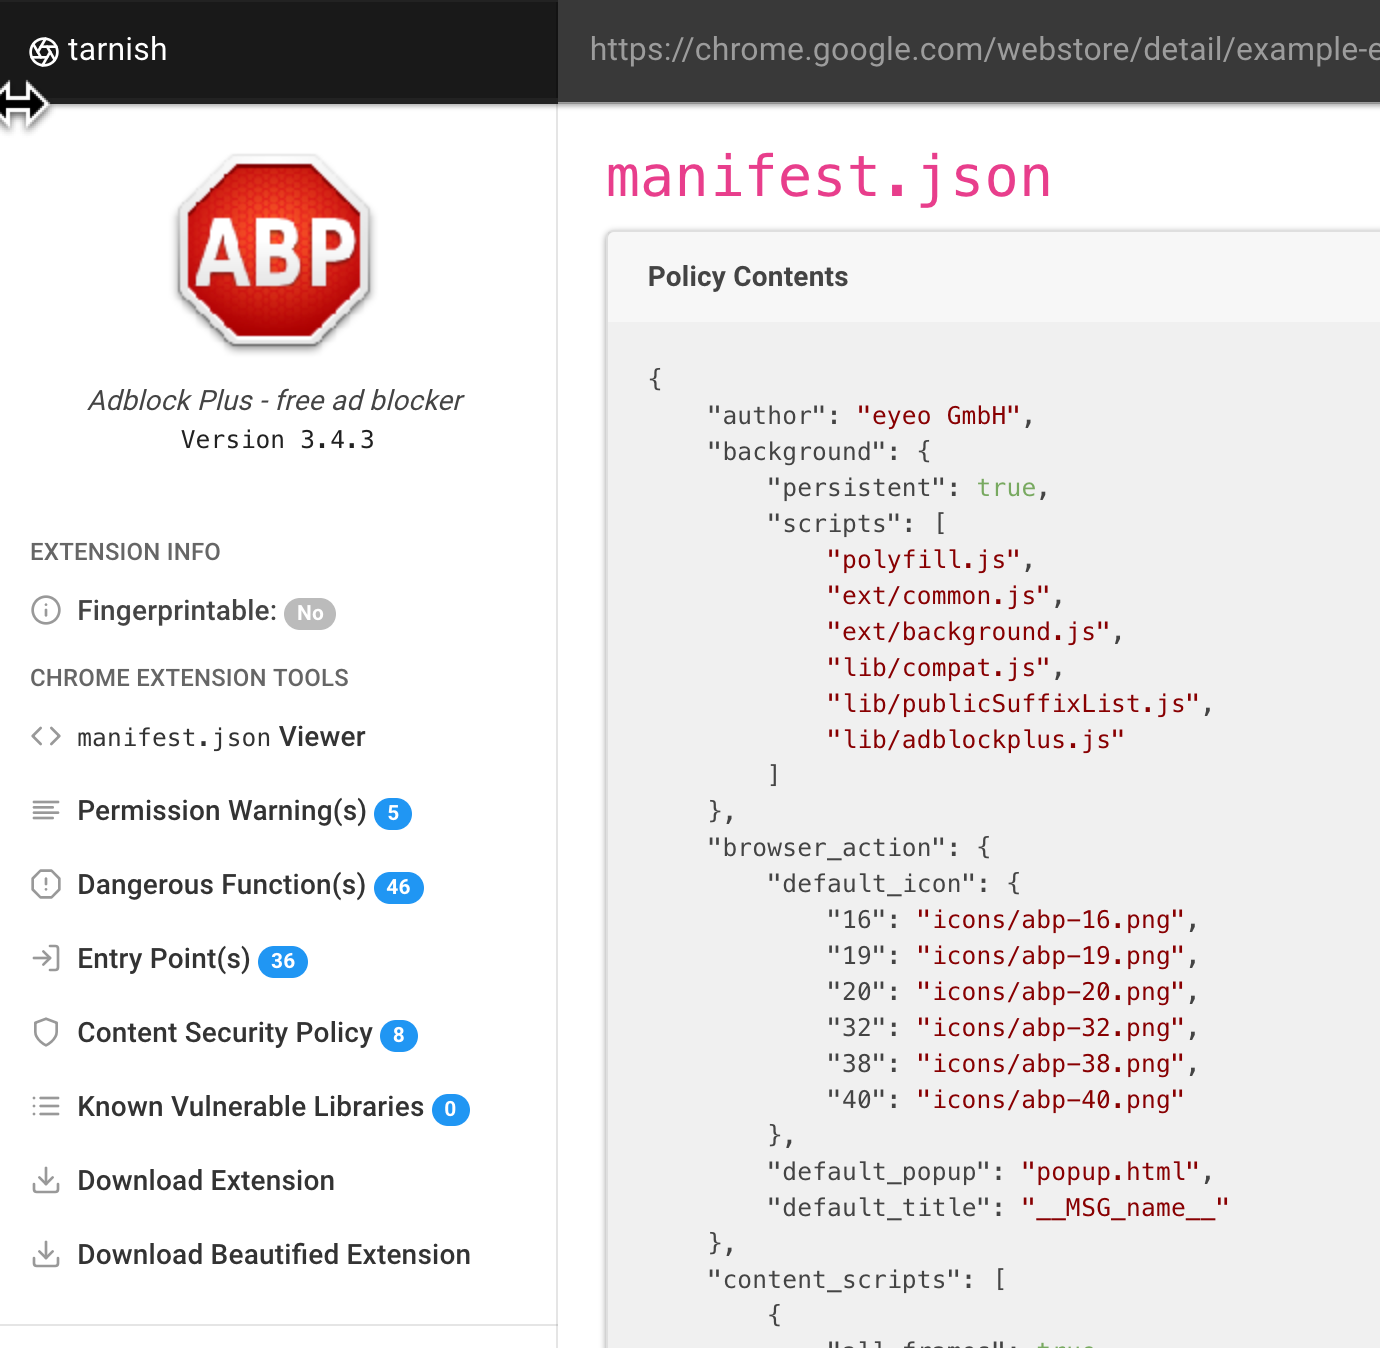 mandatoryprogrammer/tarnish
A Chrome extension static analysis tool to help aide in security reviews.
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 trailofbits/cobra
Coefficient-Based Reconstruction of Arithmetic — a Mixed Boolean-Arithmetic (MBA) expression simplifier for deobfuscation
 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 splunk/shellsweep
ShellSweeping the evil.
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
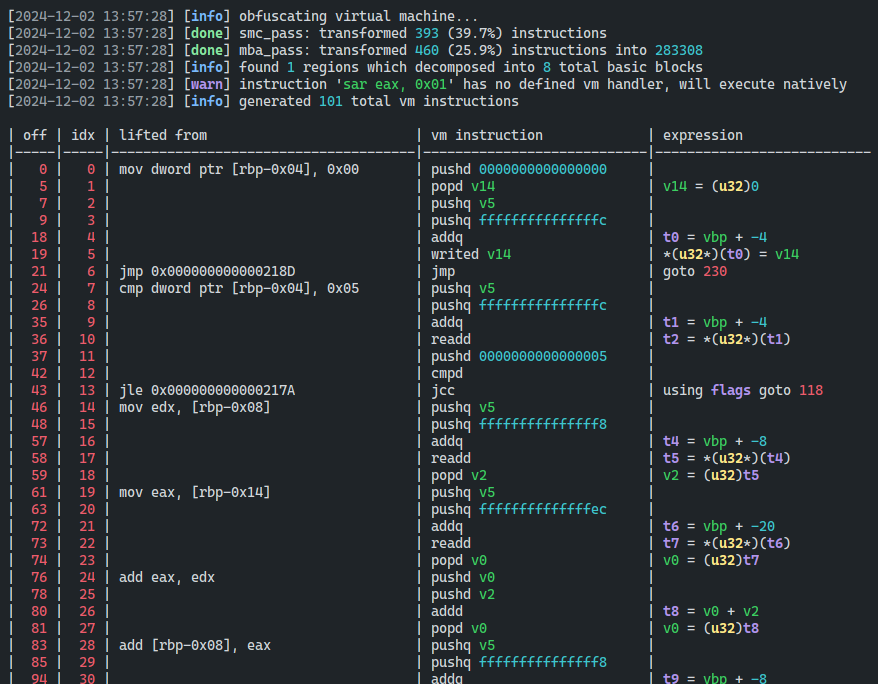 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 cellebrite-labs/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…








