#1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
 libtero/idaguides
indent guides plugin for hex-rays decompiler
 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 hackinglz/svg_phishing_tools
SVG Analysis and generation tools for commonly seen SVG attachment phishing
 libriscv/libloong
The fastest LoongArch sandbox
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
 kcreyts/plugxdecoder
Decodes PlugX traffic and encrypted/compressed artifacts
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
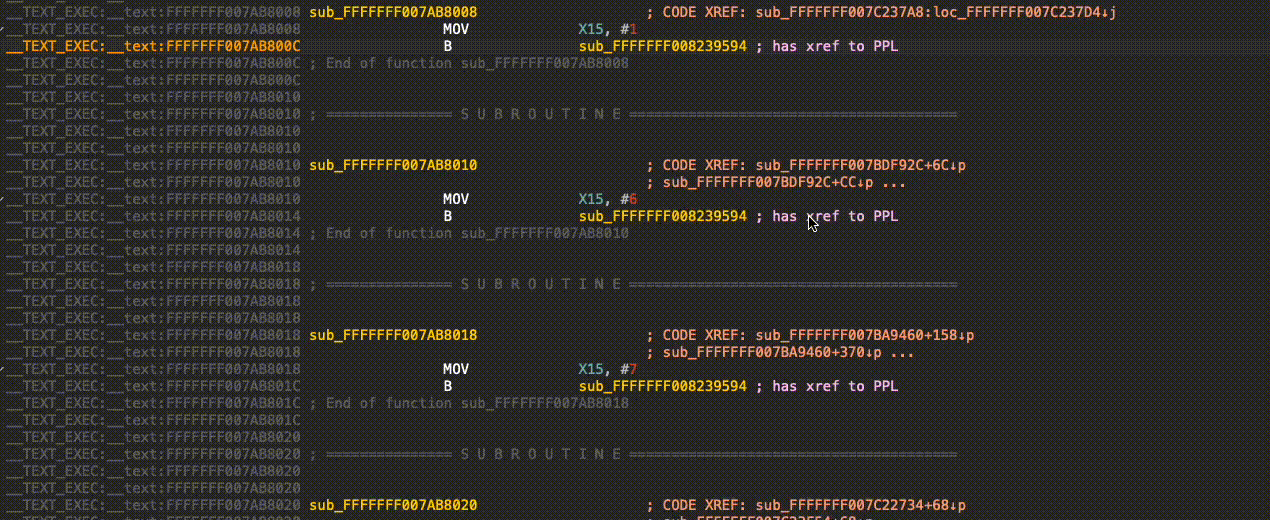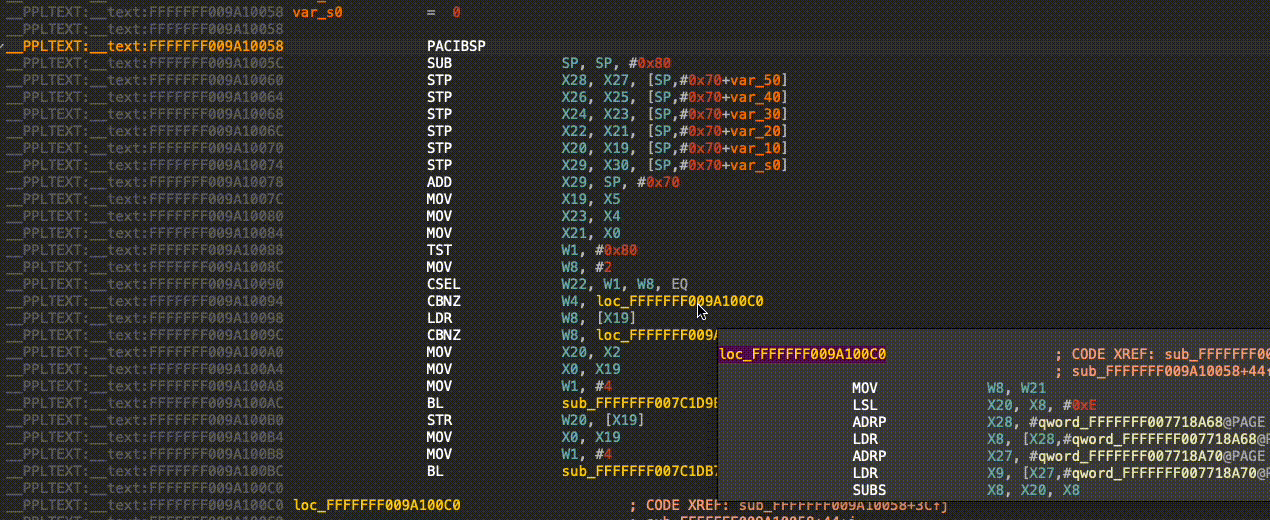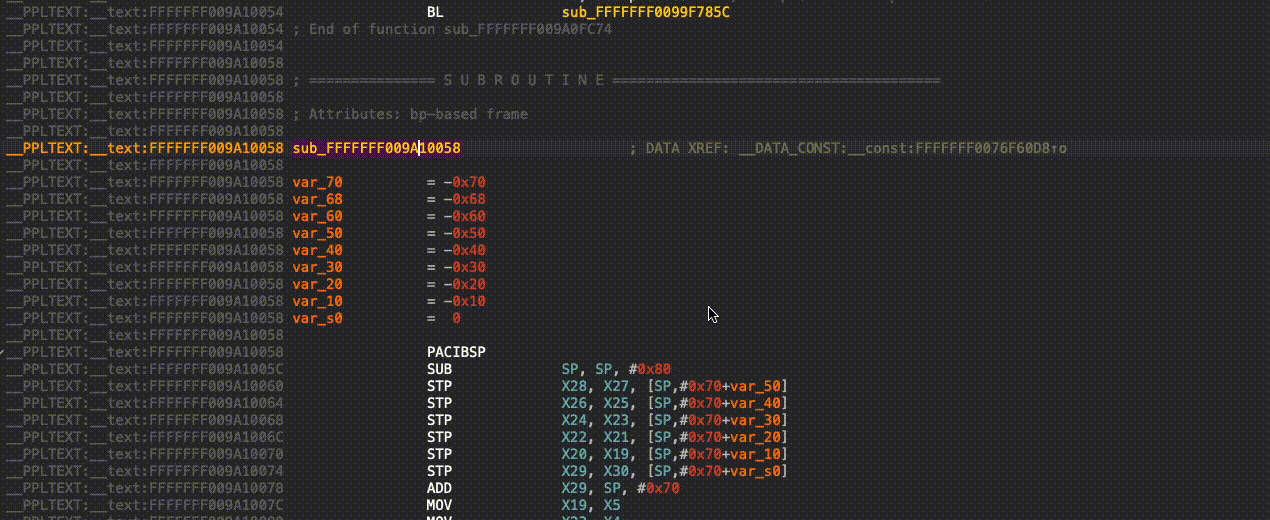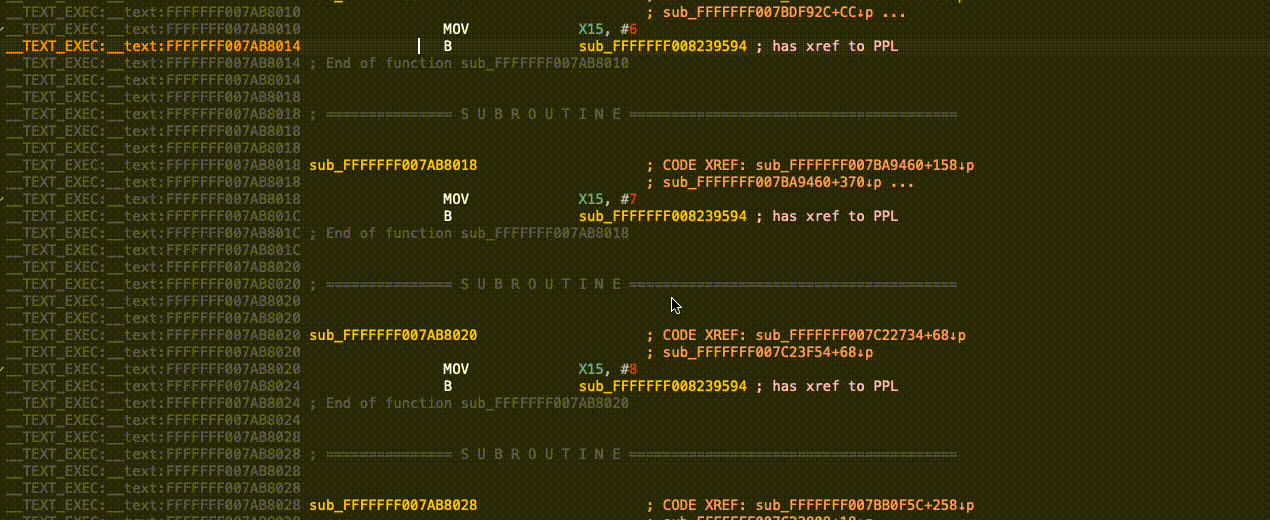 cellebrite-labs/pplorer
IDA plugin that resolves PPL calls to the actual underlying PPL function.
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
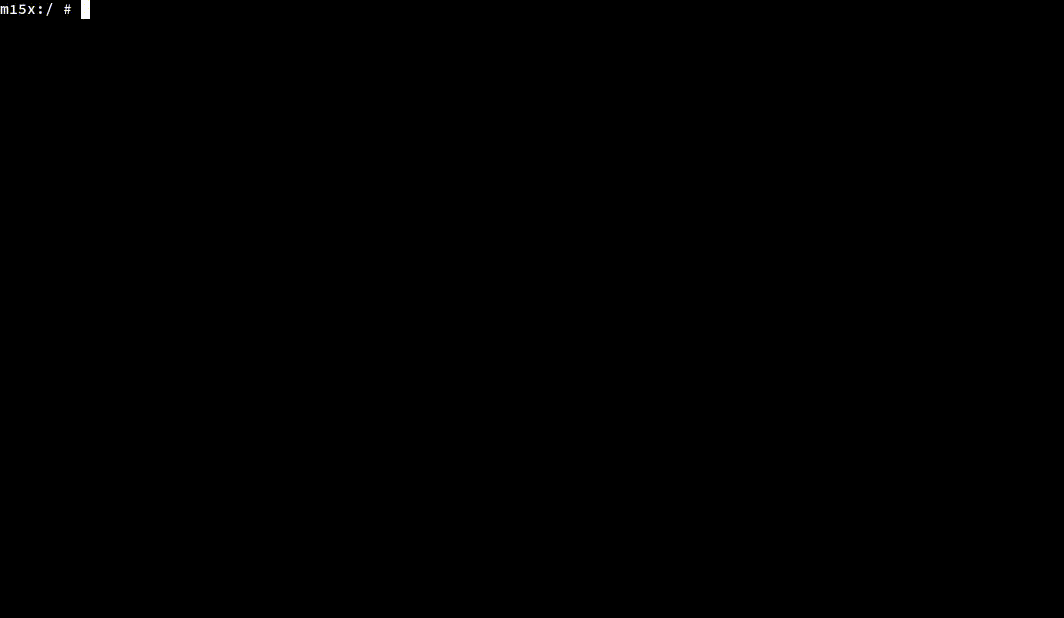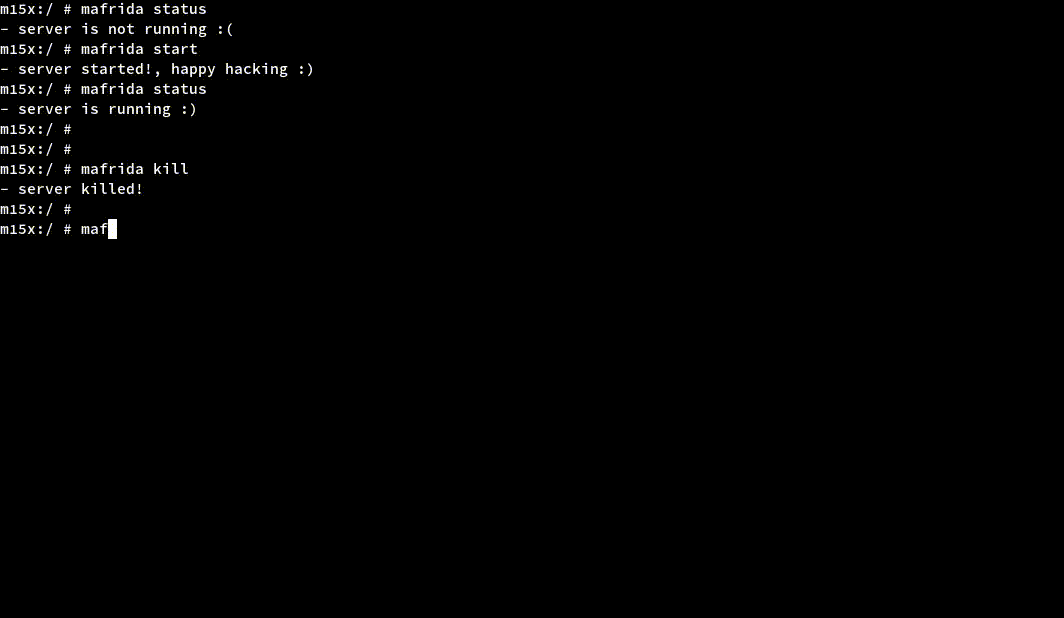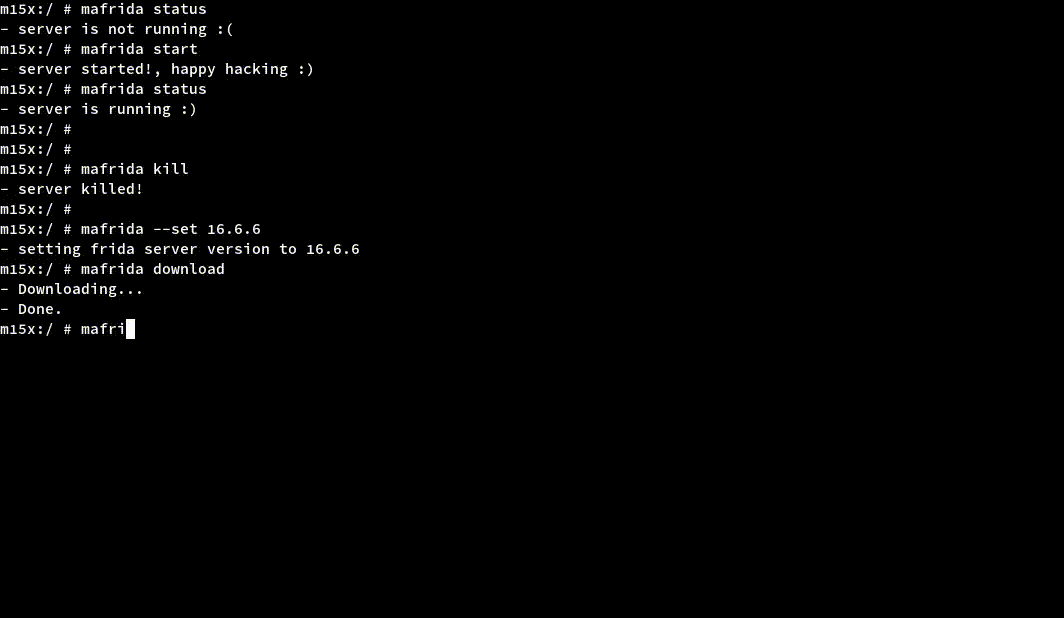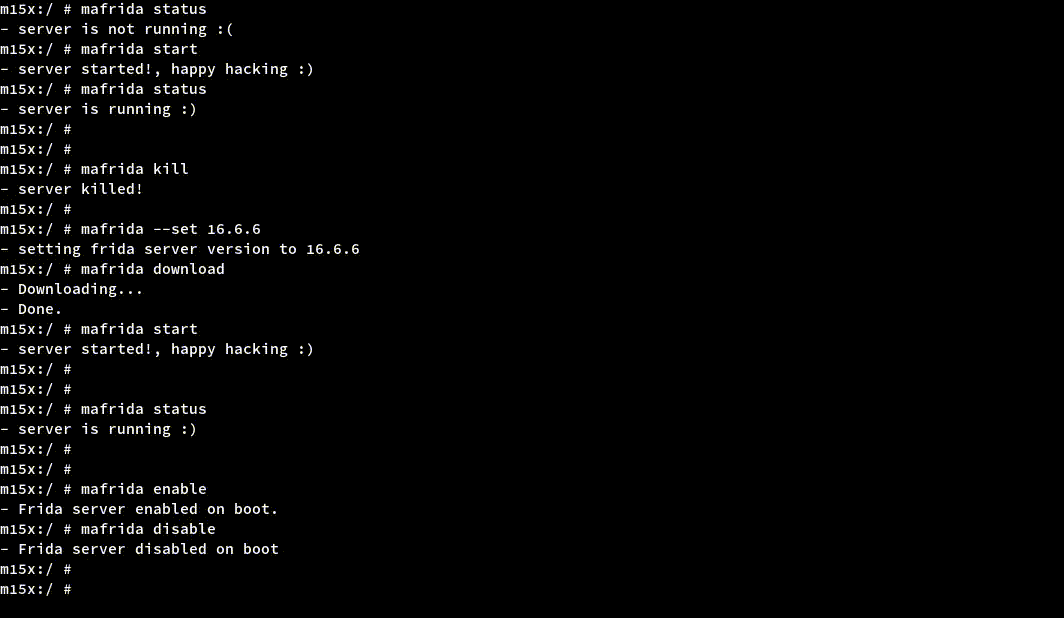 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 nccgroup/icpin
An Integrity-Check Monitoring Pintool
 withsecurelabs/dotnet-gargoyle
A spiritual .NET equivalent to the Gargoyle memory scanning evasion technique
 mindcrypt/stegowiper
A powerful and flexible tool to apply active attacks for disrupting stegomalware
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra