
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 dave_m/clamtk
An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…
 nccgroup/ghostrings
Ghidra scripts for recovering string definitions in Go binaries
 watchdogsecurity/ring3-kit
Hides Process From Task Manager Using NT API Hooking (NtQuerySystemInformation)
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 dbrll/ll-34
Circuit-level PDP-11/34 emulator
 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 sh1n0g1/z9
Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 argos83/ritm
Ruby In The Middle (HTTP/HTTPS interception proxy)
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
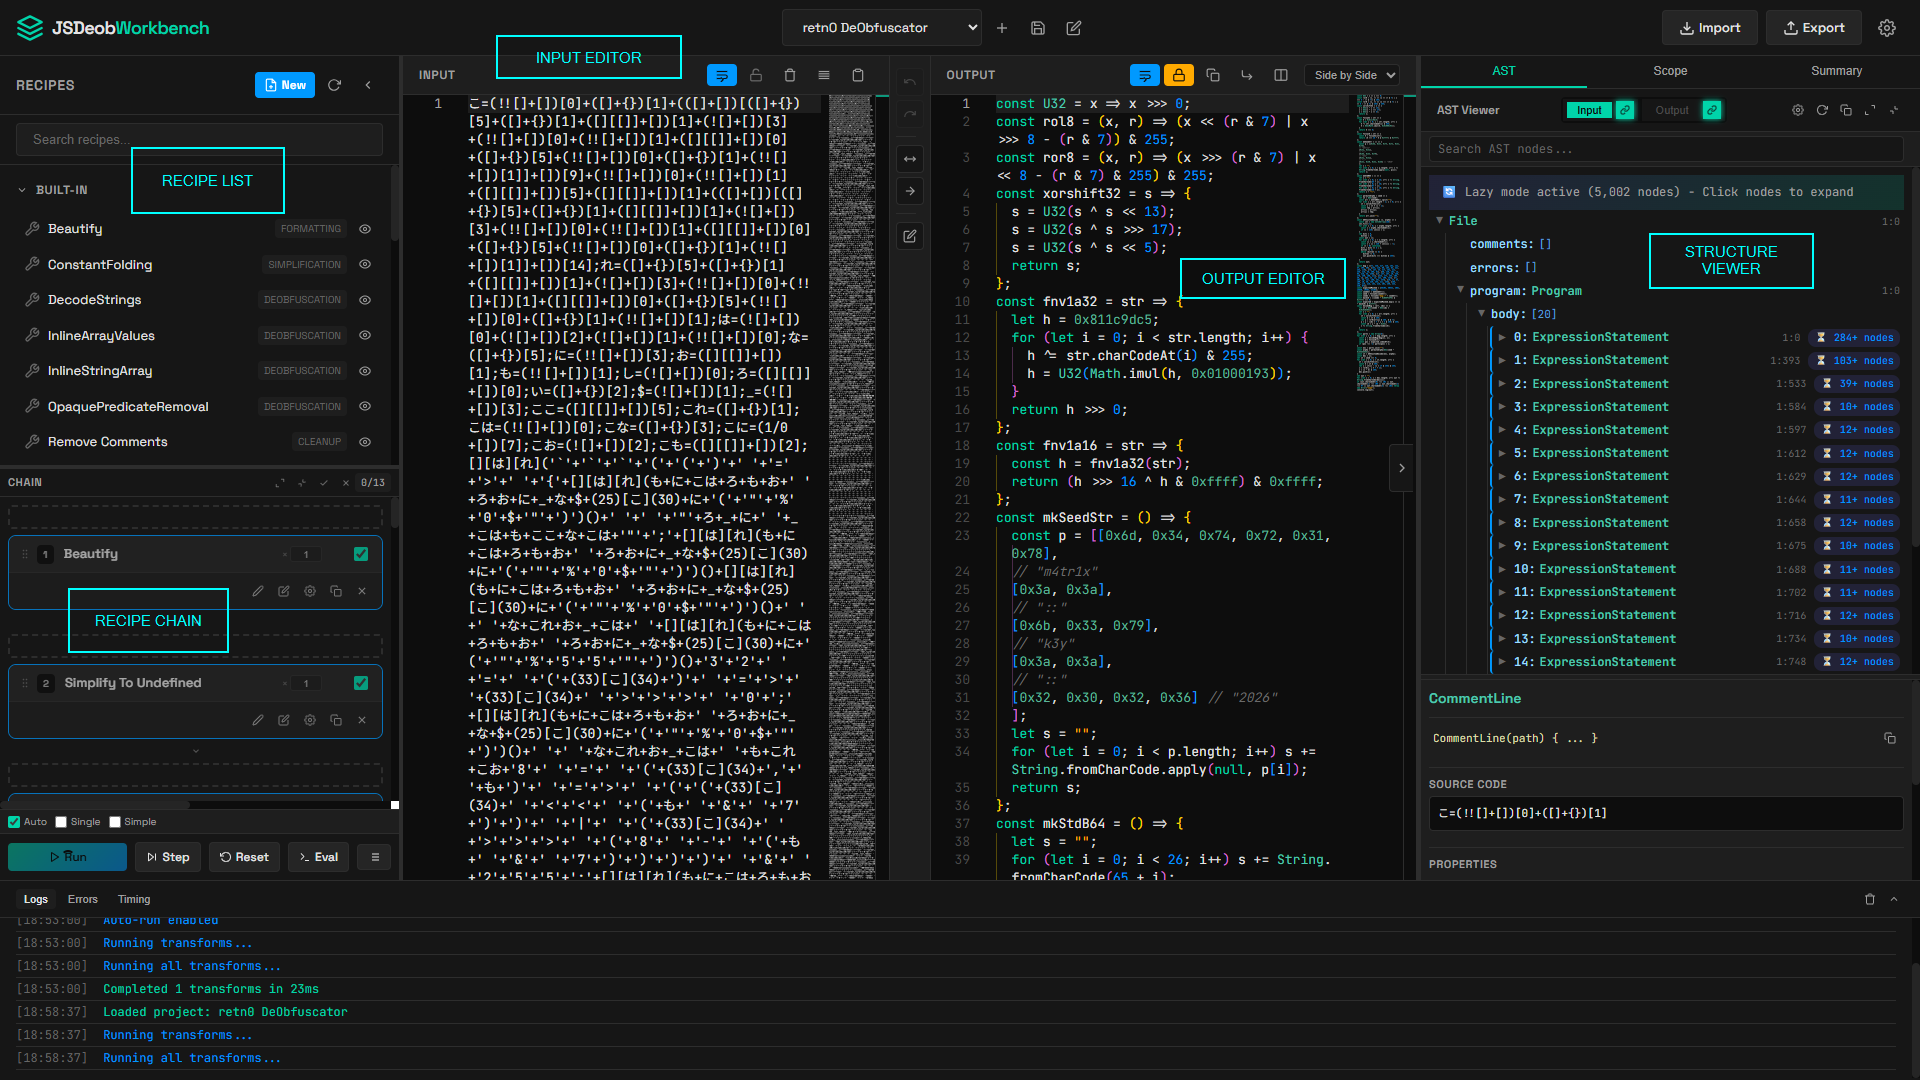 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
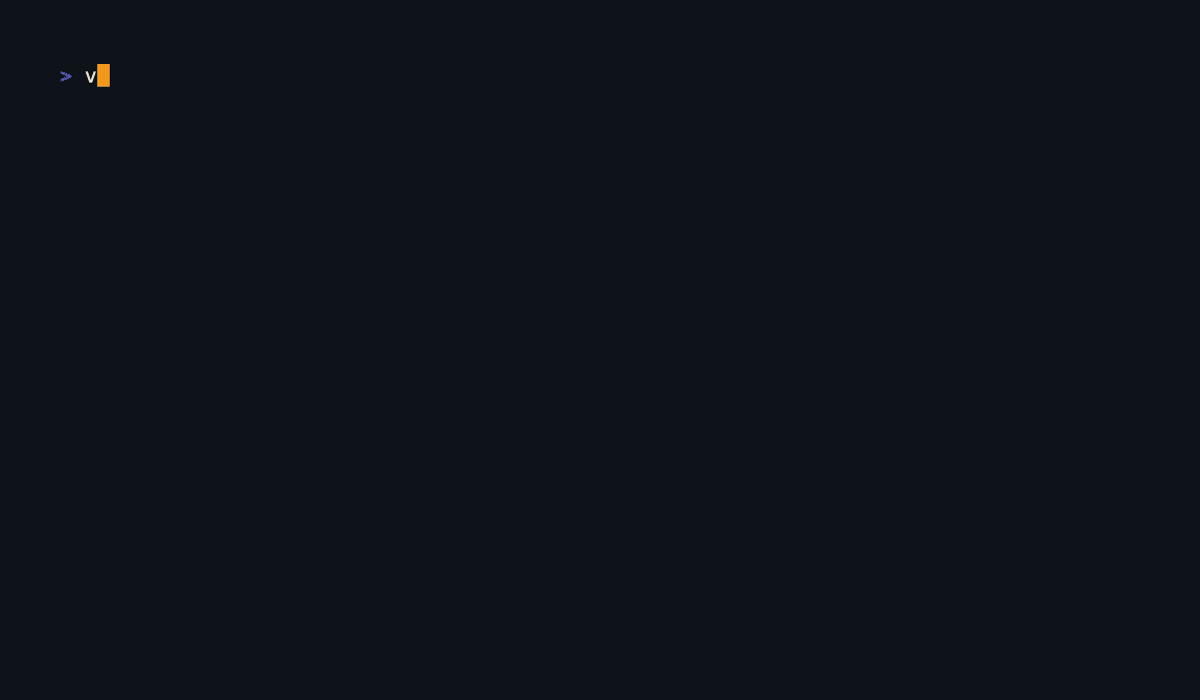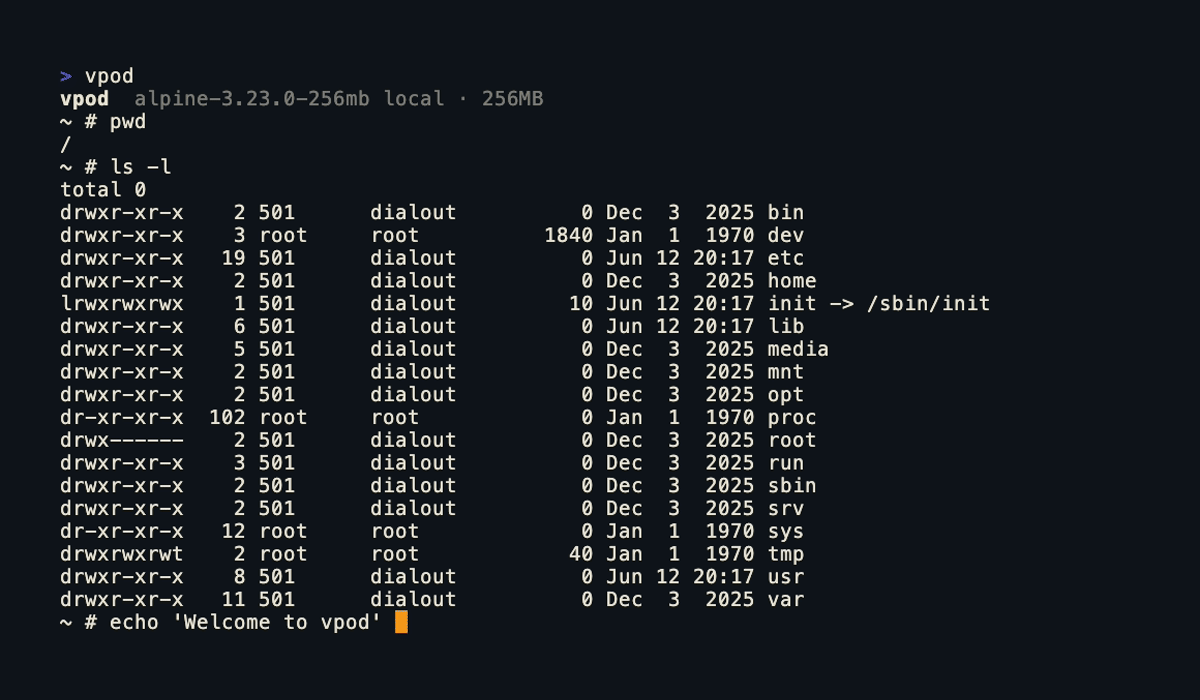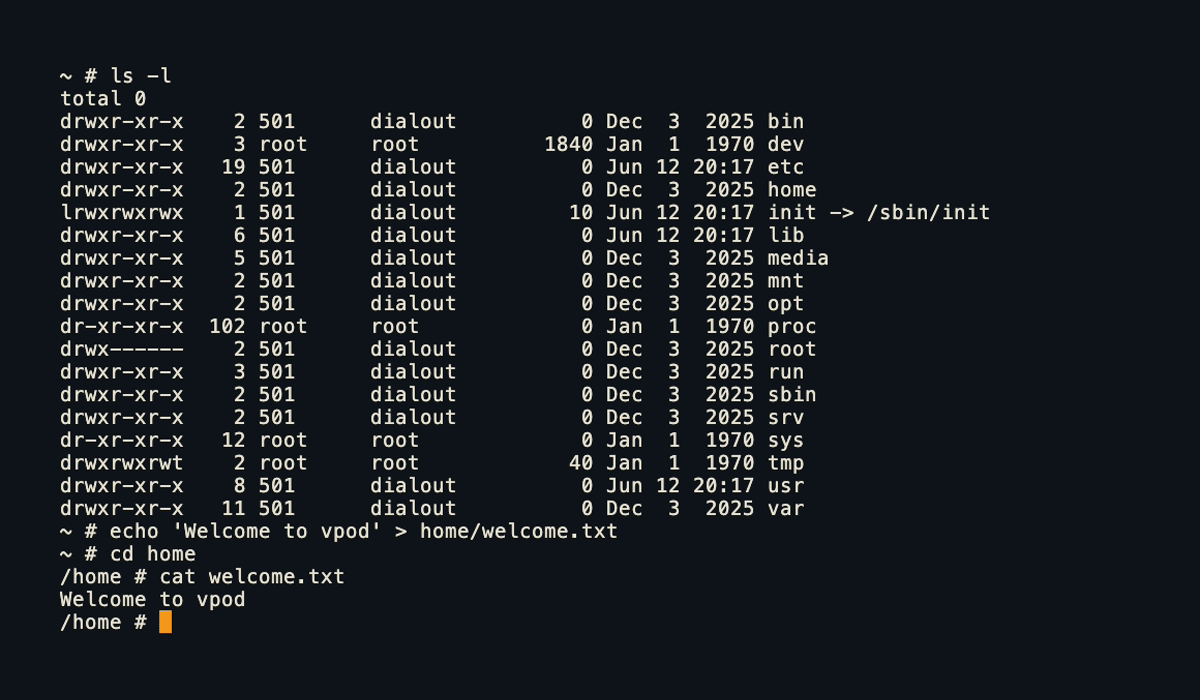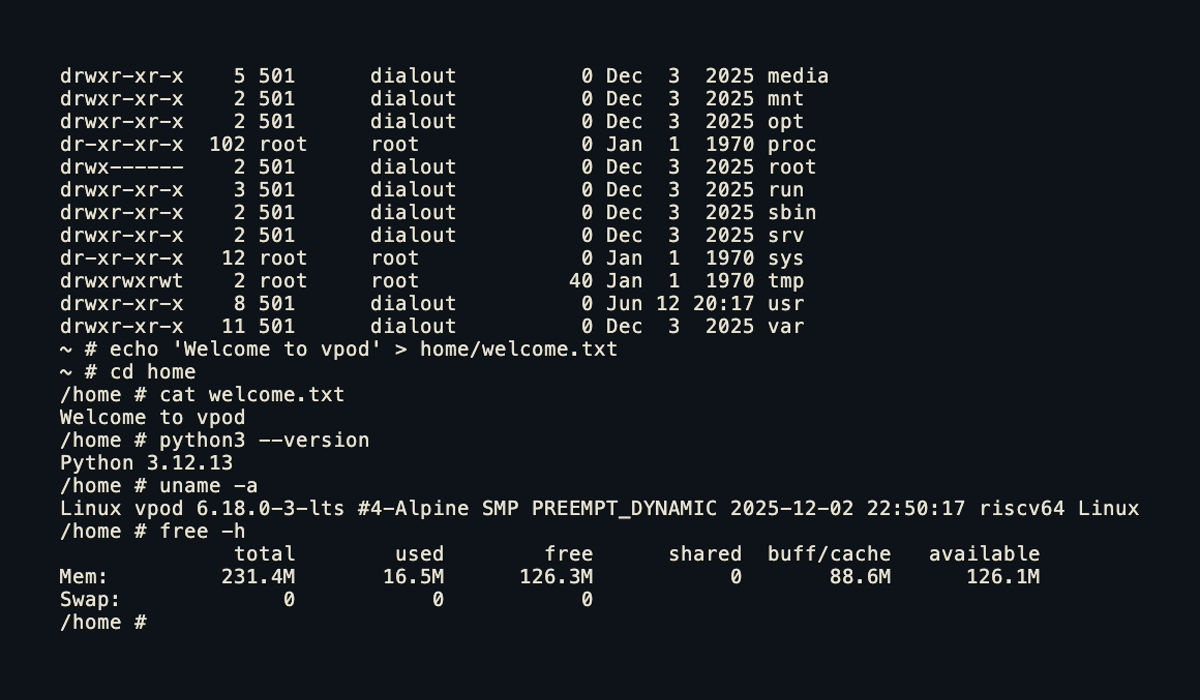 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 tandasat/hello-vt-rp
A simple hypervisor demonstrating the use of the Intel VT-rp (redirect protection) technology.
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…








