
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 dissectmalware/pyonenote
A python library to parse OneNote (.one) files
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 winterknife/evenstar
Intel 64/Windows low-level experiments
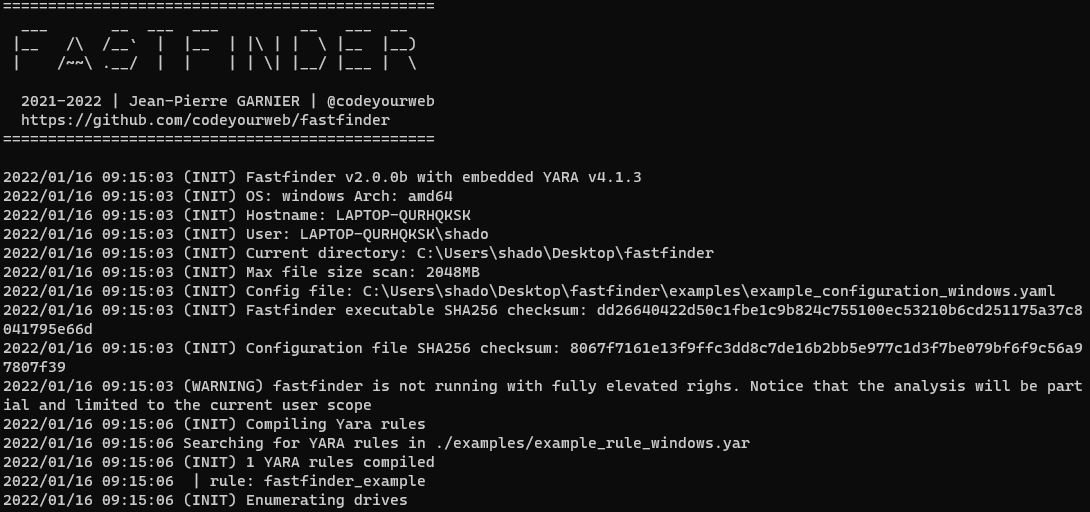 codeyourweb/fastfinder
Incident Response - Fast suspicious file finder
 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
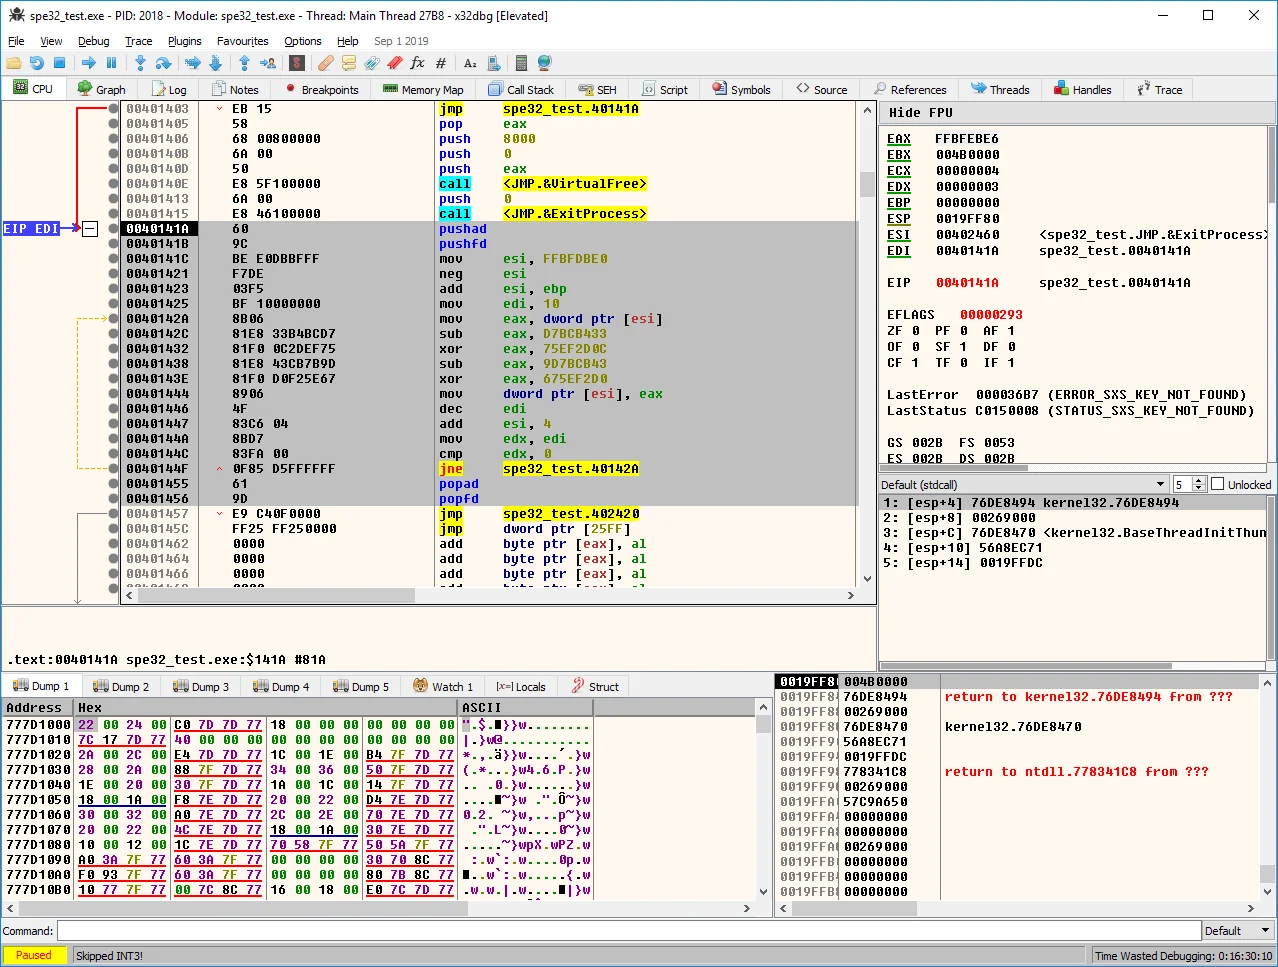 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 romainthomas/reverse-engineering-workshop
Slides & Hands-on for the reverse engineering workshop
 timetravelthree/idarustdemangler
Rust Demangler & Normalizer plugin for IDA
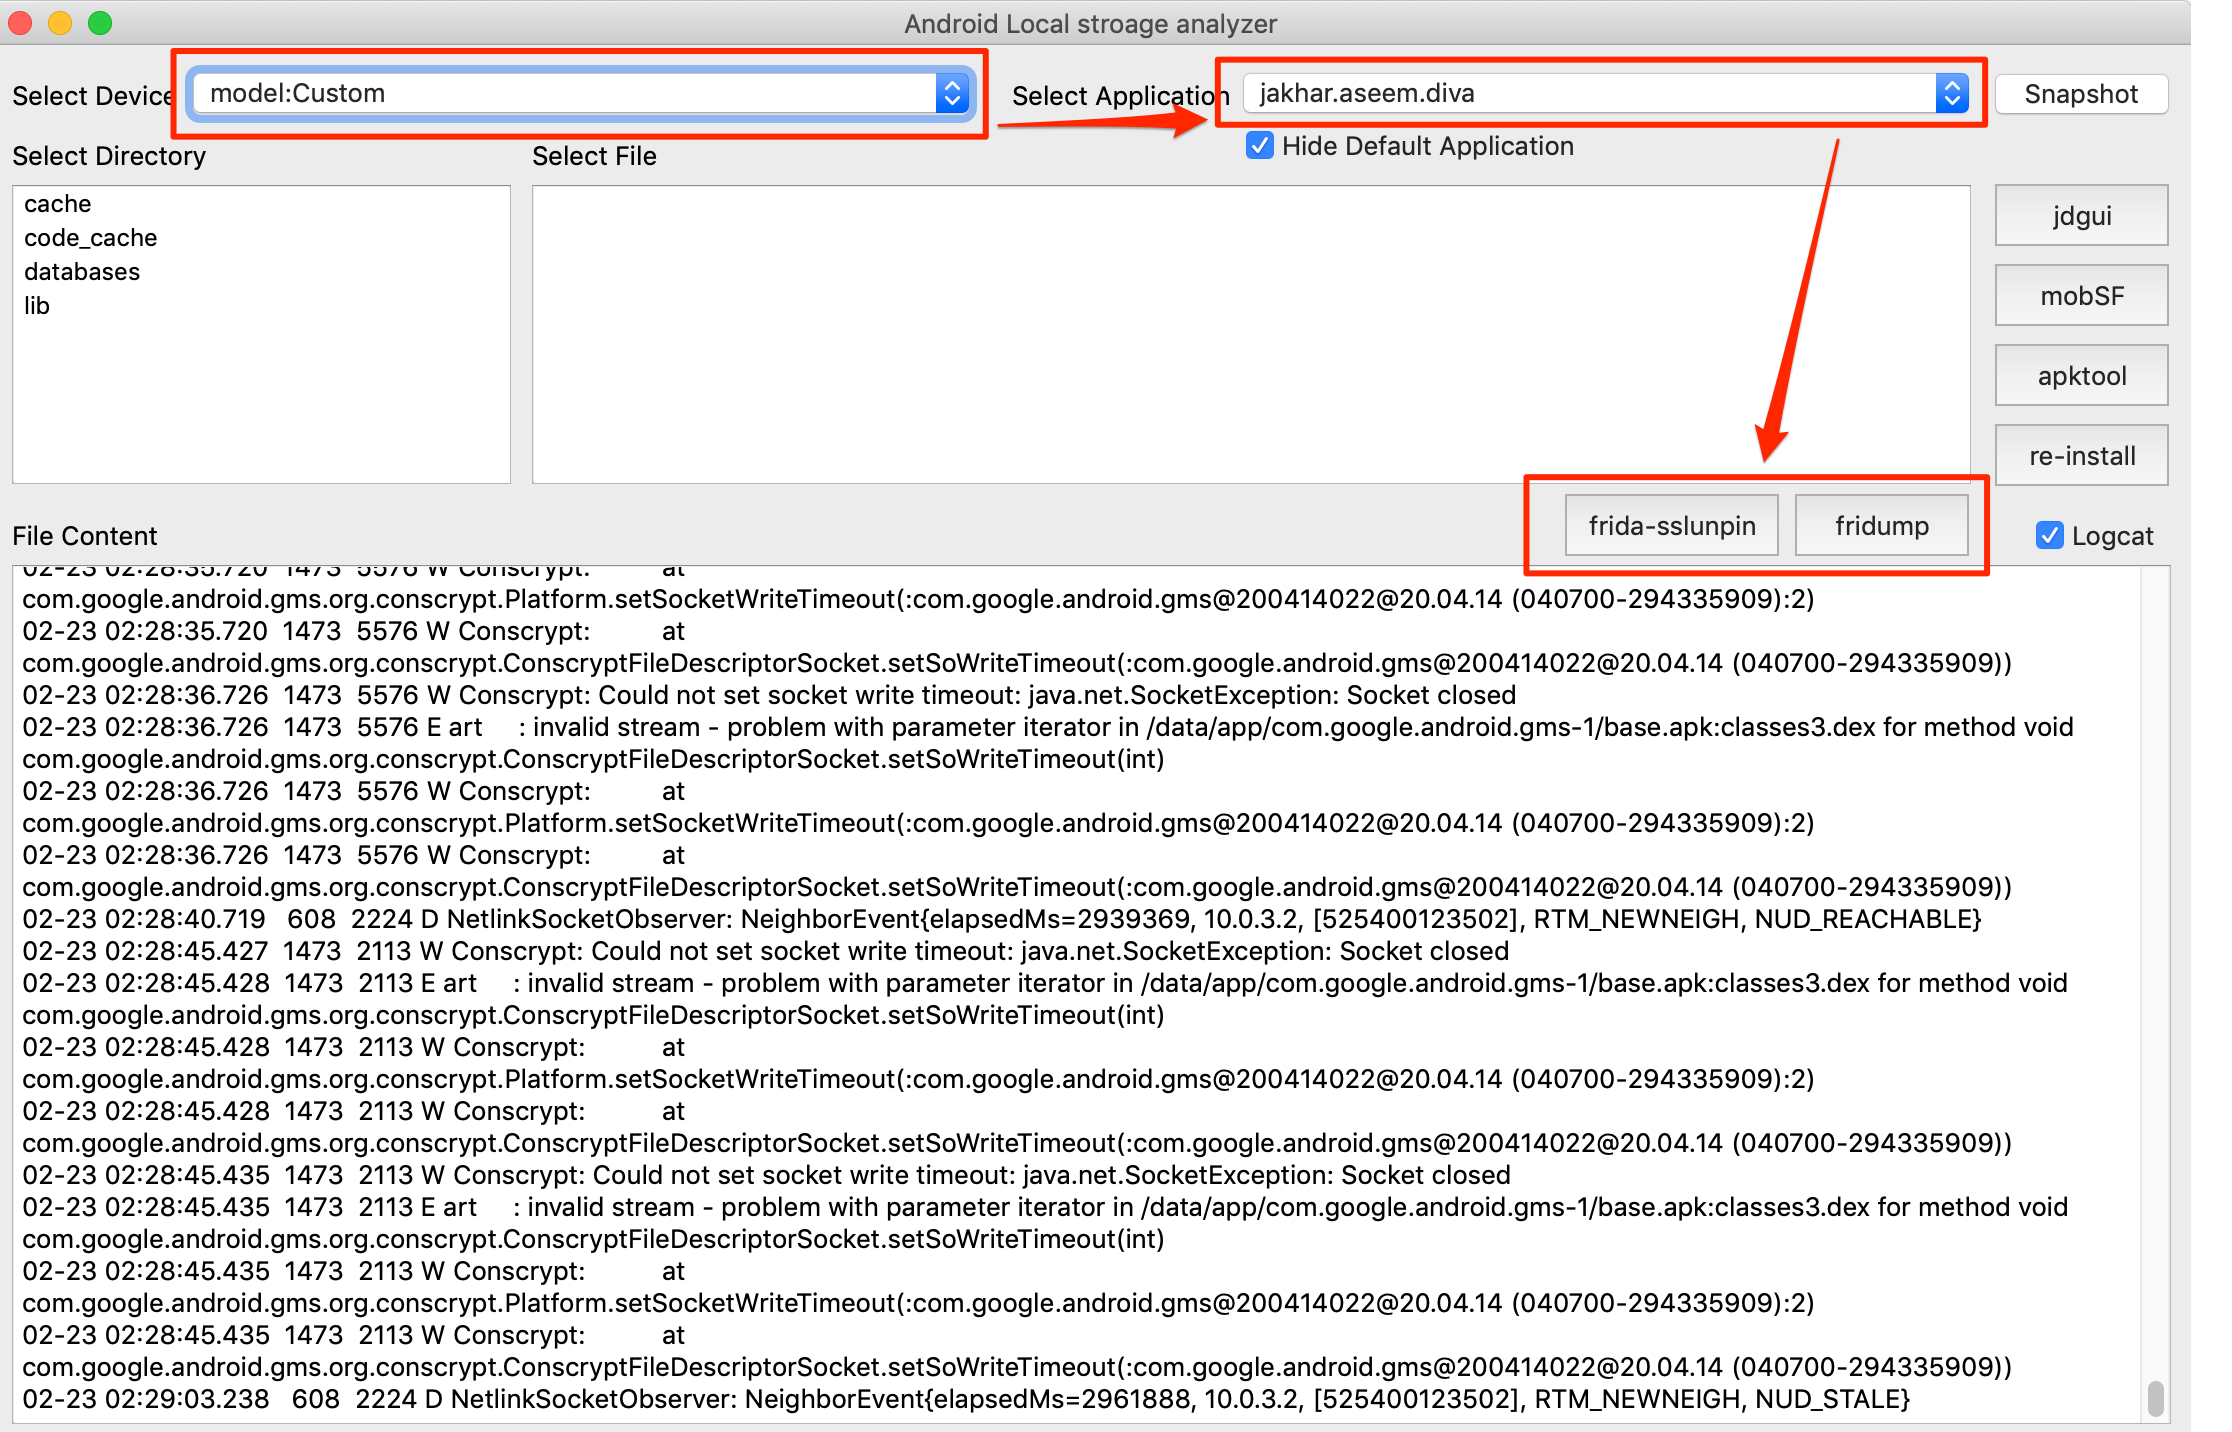 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
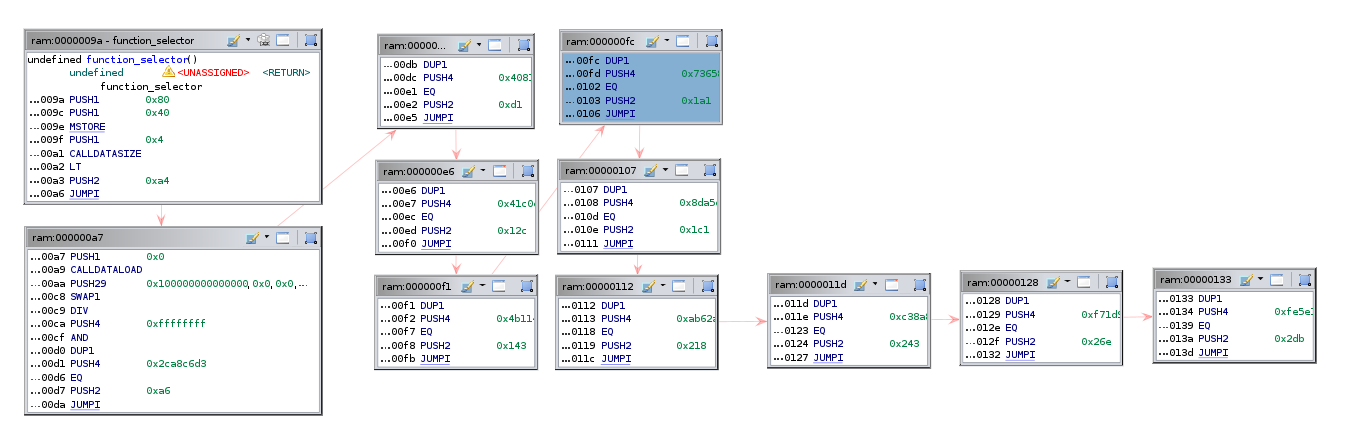 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
 ericlewis/libpo32
C99 library for PO-32 acoustic transfers and drum synthesis.
 parsingteam/teleshadow2
TeleShadow - Telegram Desktop Session Stealer (Windows)
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…








