Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Simple-Polymorphic-Engine-SPE32 — Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written in 32-bit MASM assembly. | Kitploit
Tools/GitHubGitHub/pelock/simple-polymorphic-engine-spe32
Encryption/Decryption ToolsReverse EngineeringShellcodeMalware Analysis
GitHubpelock/simple-polymorphic-engine-spe32

Simple-Polymorphic-Engine-SPE32

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written in 32-bit MASM assembly.

View Repository
Share
Website
16336923 years agoReviewed by Kitploit

Simple Polymorphic Engine — SPE32

Simple Polymorphic Engine (SPE32) is a simple polymorphic engine for encrypting code and data.

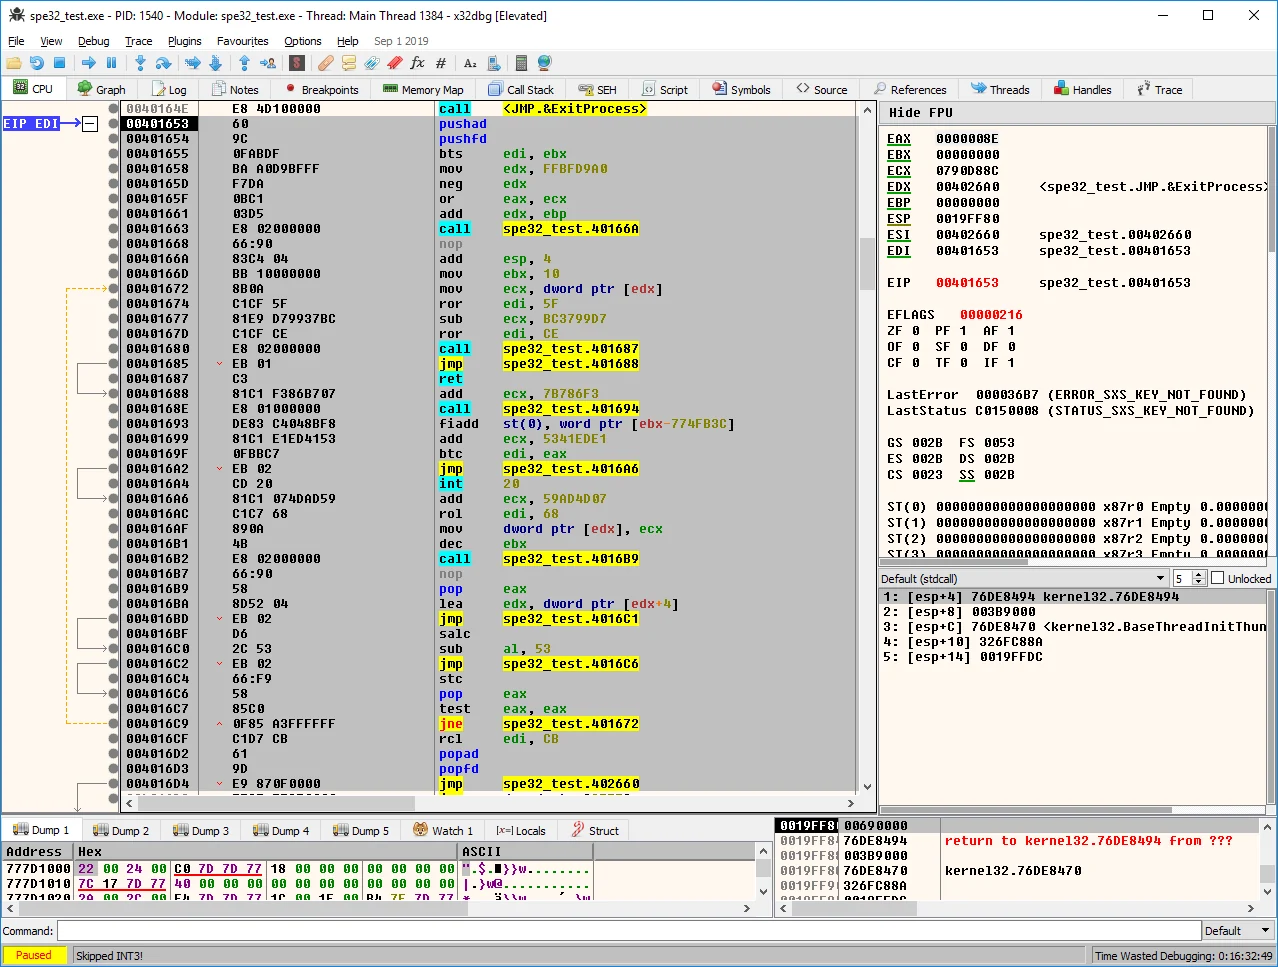
SPE32 allows you to encrypt any data and generate a unique decryption code for this data. The encryption algorithm uses randomly selected instructions and encryption keys.

The generated decryption code will be different each time.
Polymorphic decryption code as viewed in x86dbg debugger

Polymorphic code in x86dbg debugger

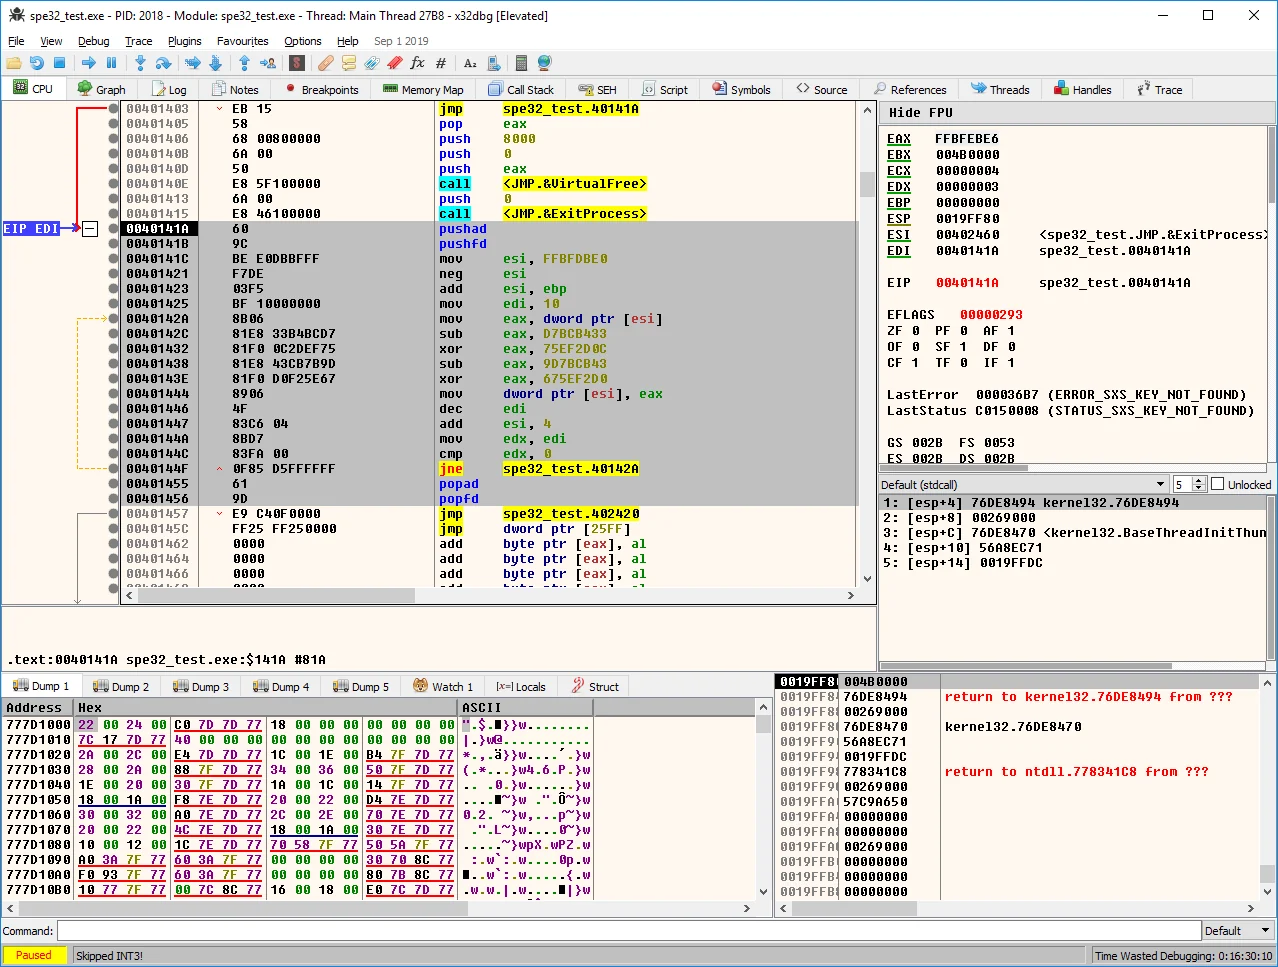
Another polymorphic code mutation, this time with junk instructions

Polymorphic code in x86dbg debugger with junk instructions

SPE32 features and status

The SPE32 engine is an amateur project that can be used to demonstrate what polymorphic engines are. I wrote it some time ago, but I thought it would be a good idea to make it public.

The entire code was written in a 32-bit assembler for the MASM compiler.

Features:

  • entire code is position independent (delta offset is used to access data)
  • XOR, ADD, SUB used for encryption
  • junk opcodes generation - ADD,ADC,SUB,SBB,ROL,ROR,RCR,RCL,SHL,SHR,NOT,NEG,DEC,INC

I don't provide technical support for SPE32, use it at your own risk.

Fully fledged commercial polymorphic engine

If you are looking for professional solution take a look at our Poly Polymorphic Engine.

  • https://www.pelock.com/products/poly-polymorphic-engine

Poly Polymorphic Engine is the only commercial polymorphic engine available on the market. It's a highly specialized cryptographic solution which is used in anti-cracking software protection systems and anti-reverse engineering systems. Due to the complicated nature of their code, polymorphic engines aren't publicly available, and creating one requires highly specialized knowledge in low level assembly programming and reverse engineering as well as an extensive testing process.

Poly Polymorphic Engine

Bartosz Wójcik

  • Visit my site at — https://www.pelock.com
  • Twitter — https://twitter.com/PELock
  • GitHub — https://github.com/PELock
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    945
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    350
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    338
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    292

Explore all tools

Browse our collection of tools

View all tools →