
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 pmd/pmd
An extensible multilanguage static code analyzer.
 emsec/hal
HAL – The Hardware Analyzer
 googlesky/cve-2026-118383
Proof-of-concept for CVE-2026-118383, an unauthenticated MongoDB use-after-free in replication catch-up, with wire-protocol exploit scripts, a gdb…
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 bb1nfosec/information-security-tasks
Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…
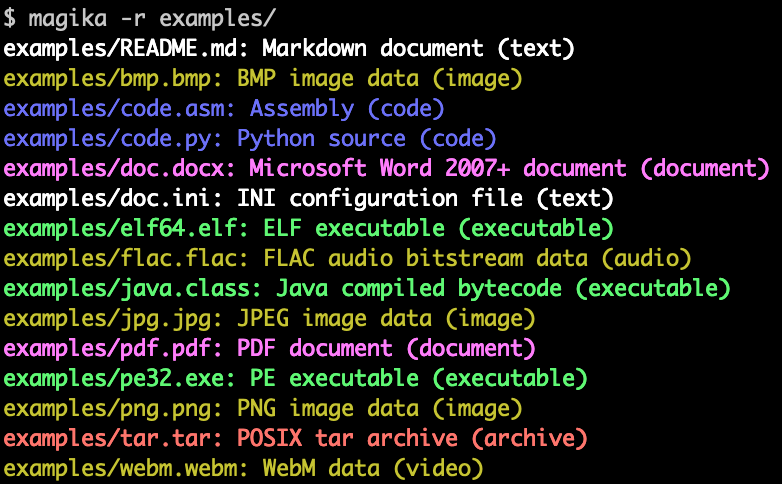 google/magika
Fast and accurate AI powered file content types detection
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 trailofbits/fickling
A Python pickling decompiler and static analyzer
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 snyk/agent-scan
Security scanner for AI agents, MCP servers and agent skills.
 google/oss-fuzz
OSS-Fuzz - continuous fuzzing for open source software.






