
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 malwaretech/appcontainersandbox
An example sandbox using AppContainer (Windows 8+)
 jacobpimental/nanocore_extractor
Extracts nanocore sample from compile AutoIT script
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 lan1oc/cve-2023-34312-exp
Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
 lodi-g/cve-2023-33668
Technical analysis and proof-of-concept bypass for CVE-2023-33668 in DigiExam proctoring software, demonstrating weak VM detection and native module…
 r0ngy40/cve-2025-30208-series
Analysis of the Reproduction of CVE-2025-30208 Series Vulnerabilities
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 mansk1es/caboom
A malicious .cab creation tool for CVE-2021-40444
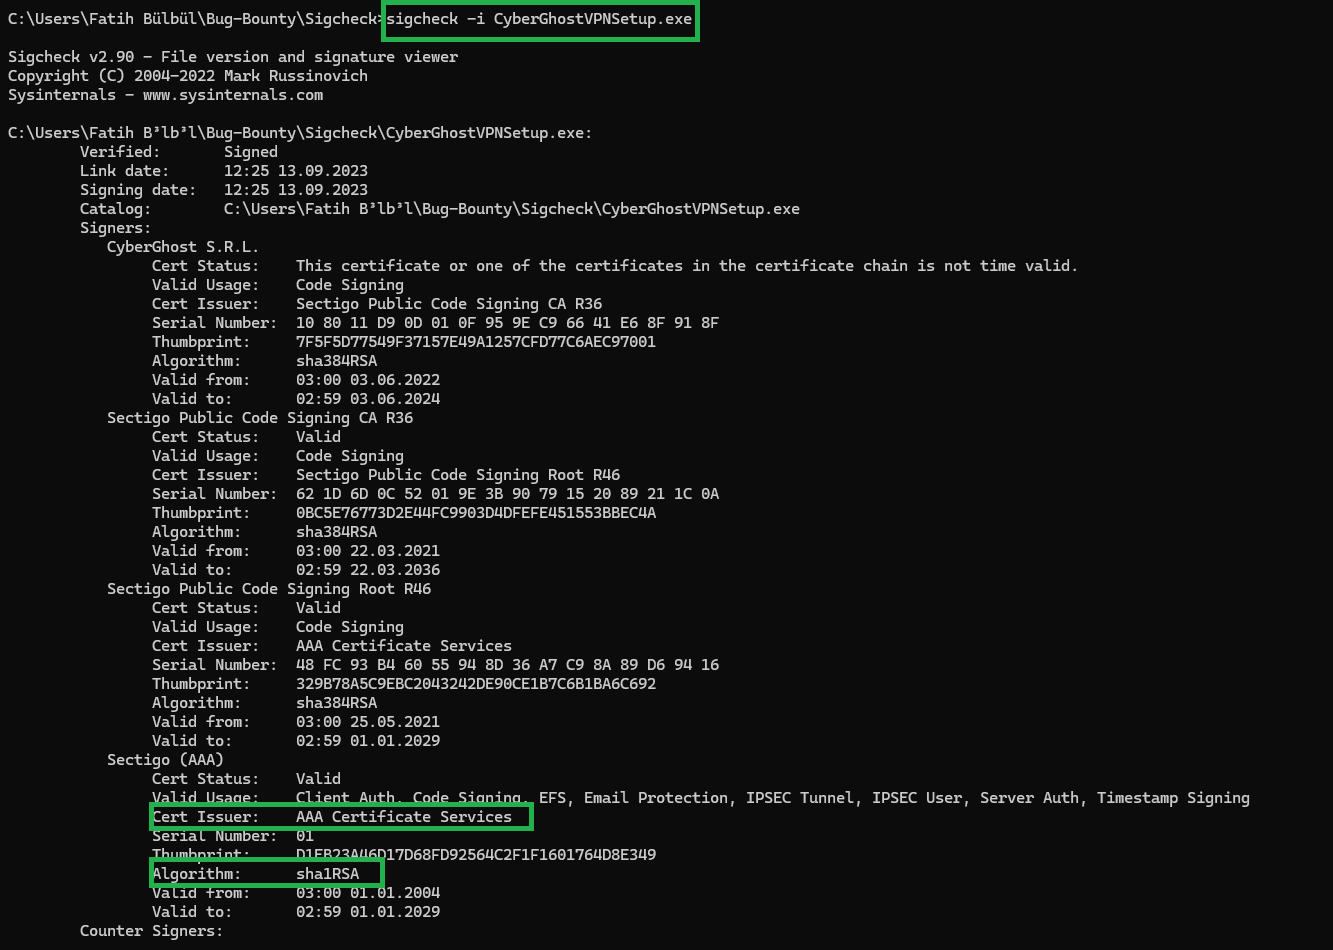 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 mercul1ninna/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 moscovium-mc/tor-0day-javascript-exploit
Firefox/Tor Browser 0day exploit analysis (CVE-2024-9680) A UAF in animation timelines leading to RCE. Patched.








