
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 xiaoqimikko/scc-check
Offline checker for Spring Cloud Config CVE-2026-40982 — tells you whether your version line has an OSS fix at all (3.1.x/4.1.x/4.2.x: it does not)
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 watchfulip/tp-link-decrypt
Decrypt TP-Link Firmware
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 xiaoqimikko/pac4j-check
Offline scanner for CVE-2026-29000 (CVSS 10.0) in org.pac4j:pac4j-jwt. Inspects jars/fat-jars directly, so it works where mvn dependency:tree cannot.…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
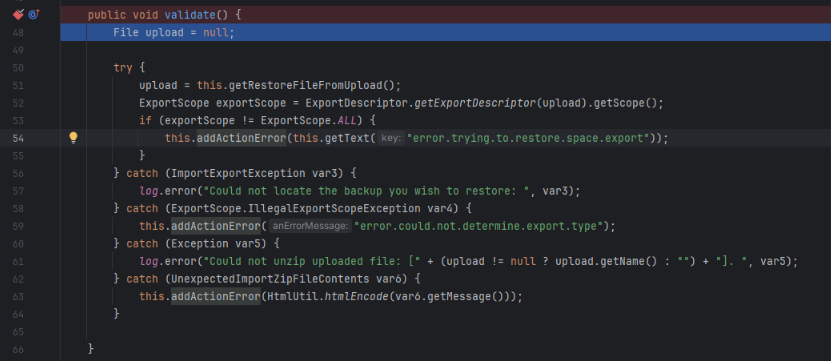 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…
 murf-xd/cve-2023-20768
Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
 themalwareguardian/cve-2024-7344
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…
 cristhiansm0/txdxcristhian_2023-cve-38831
CVE-2023-38831 WinRAR lab: detection with Sysmon/Wazuh, reverse engineering with Ghidra, patch analysis, and remediation.
 allthingsida/idasql
Vibe Reverse Engineer with IDA Pro: An interface for IDA in SQL via live virtual tables. Don't let appearances deceive you! :)
 cybercentrecanada/cart
Python implementation of the CaRT library for (un)inerting files.
 allthingsida/allthingsida
Repository for the code snippets from the AllThingsIDA video channel
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries








