
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
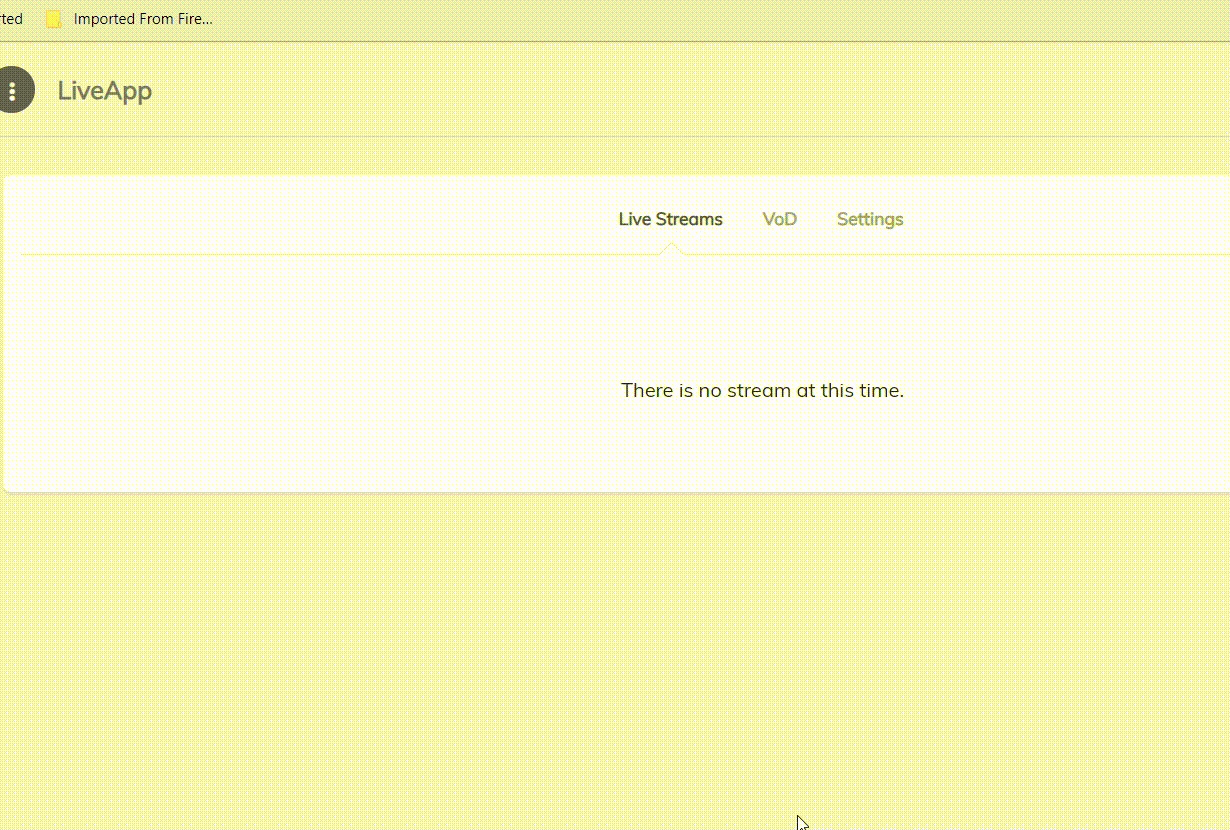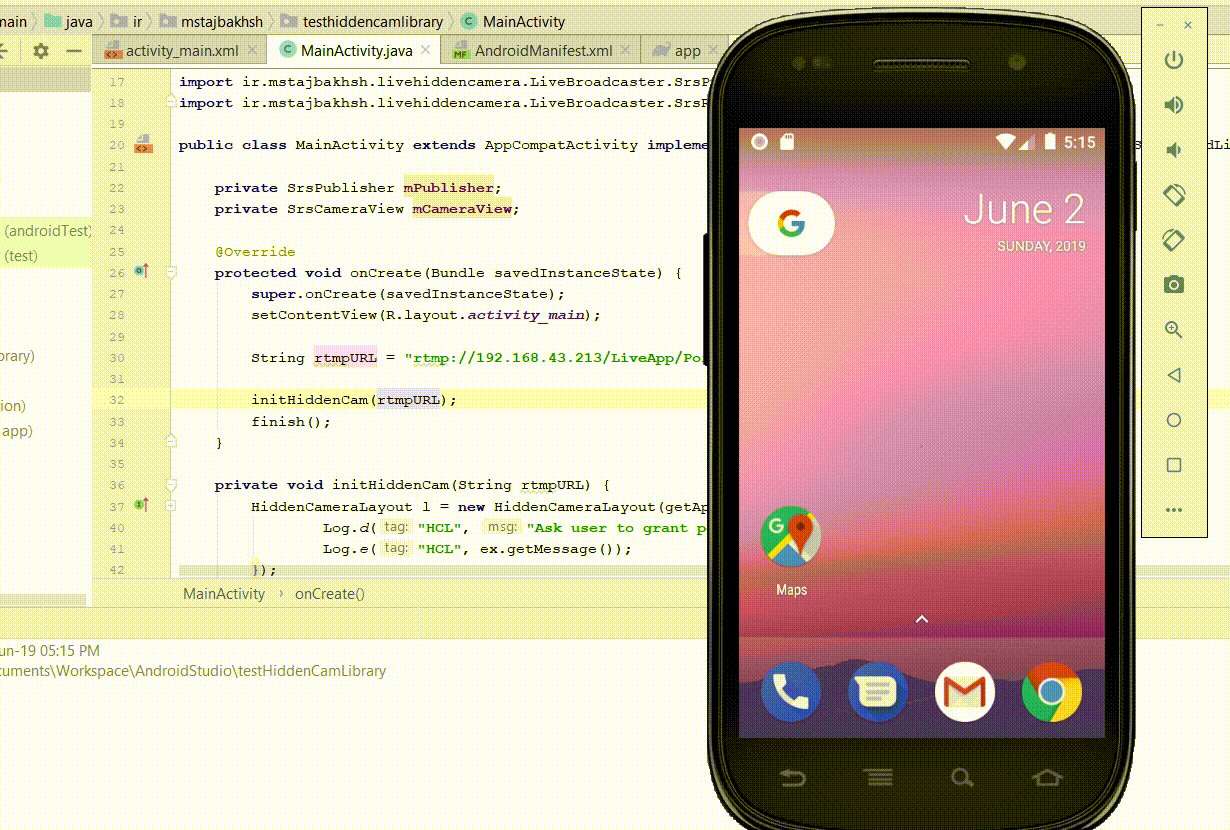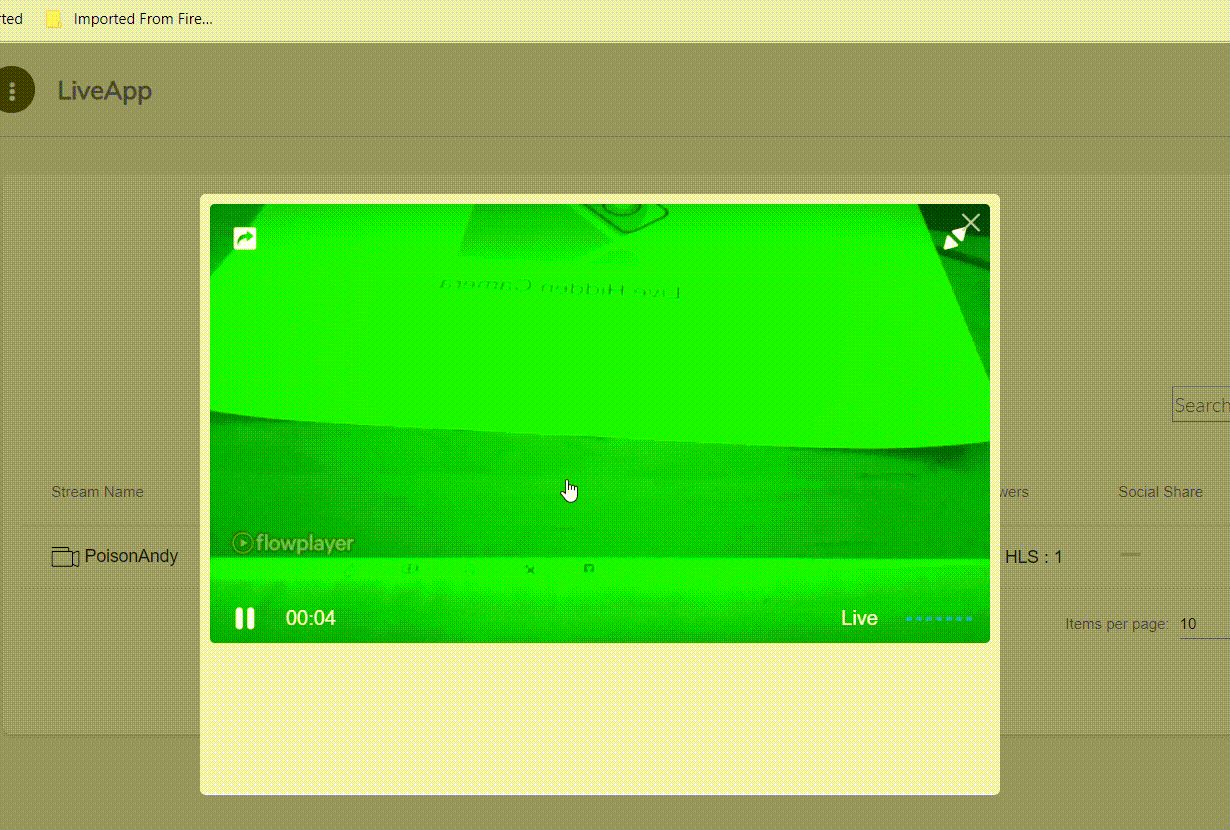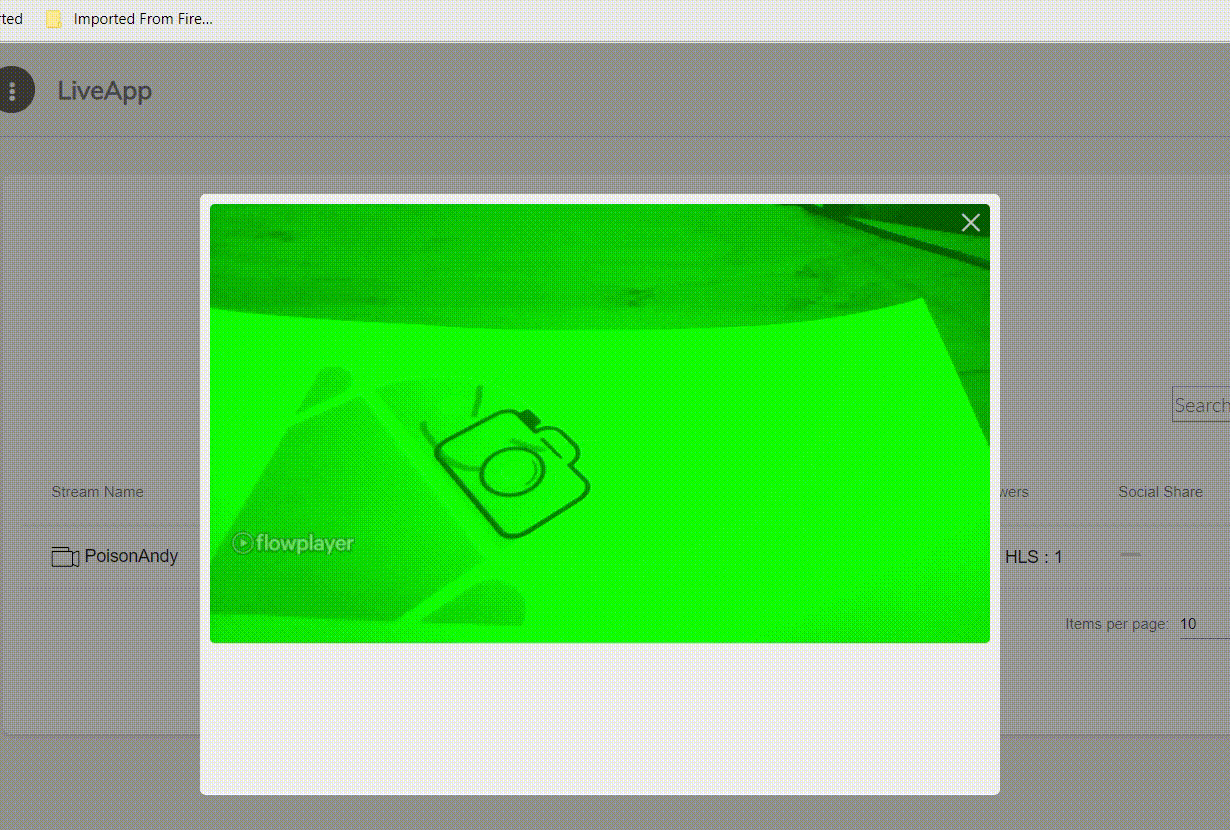
 mirsamantajbakhsh/livehiddencamera
Live Hidden Camera is a library which record live video and audio from Android device without displaying a preview.
 vichhka-git/universal-flutter-ssl-pinning
Automated SSL pinning bypass for any Flutter & Shorebird version — PyGhidra static analysis auto-discovers BoringSSL and generates ready-to-run Frida…
 h1nayoshi/smalien
Information flow analysis tool for Android applications
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
 unsignedchad/bcm4360-wpa3
wpa3 functionality for the wifi chip in a 2014 macbook pro
 betulssahin/cve-2025-0411-7-zip-mark-of-the-web-bypass
CVE-2025-0411 7-Zip Mark-of-the-Web Bypass
 stivenhacker/ghoststrike
C++ process hollowing injector that encrypts and obfuscates shellcode with XOR, Base64, and dynamic API resolution to deploy stealthy reverse shells…
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 ayoubfaouzi/al-khaser
Public malware techniques used in the wild: Virtual Machine, Emulation, Debuggers, Sandbox detection.
 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
 wrongbaud/hackaday-u
Course materials for hackaday.io Ghidra training
 secrary/ssma
SSMA - Simple Static Malware Analyzer [This project is not maintained anymore by me]
 nccgroup/driverbuddy
DriverBuddy is an IDA Python script to assist with the reverse engineering of Windows kernel drivers.








