
 #1
Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.
Kitploit recommended

 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 cloud-gouv/securix
SécurixOS is a NixOS-based secure operating system tailored for small to medium-sized teams. It provides a minimal, hardened environment with strong…
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 logpai/logparser
A machine learning toolkit for log parsing [ICSE'19, DSN'16]
 trustedsec/sysmoncommunityguide
TrustedSec Sysinternals Sysmon Community Guide
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
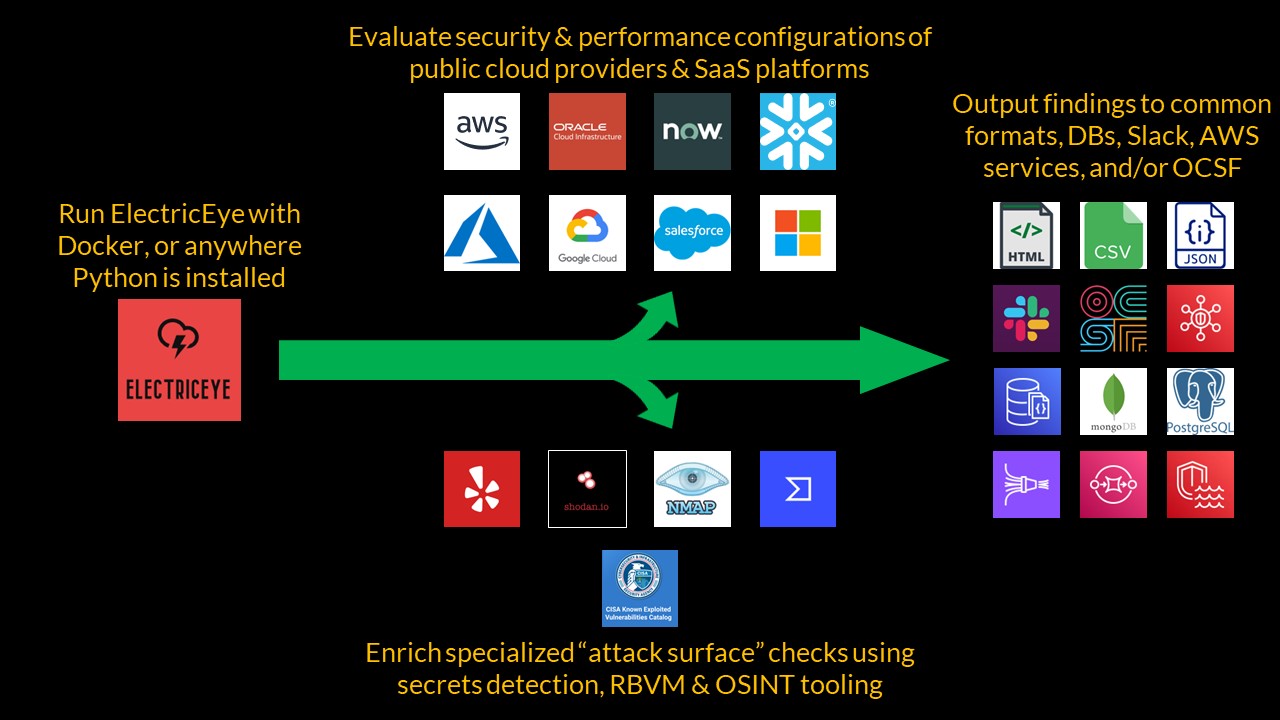 jonrau1/electriceye
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
 travisfsmith/sweetsecurity
Network Security Monitoring on Raspberry Pi type devices
 letsdefend/awesome-soc-analyst
Useful resources for SOC Analyst and SOC Analyst candidates.
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
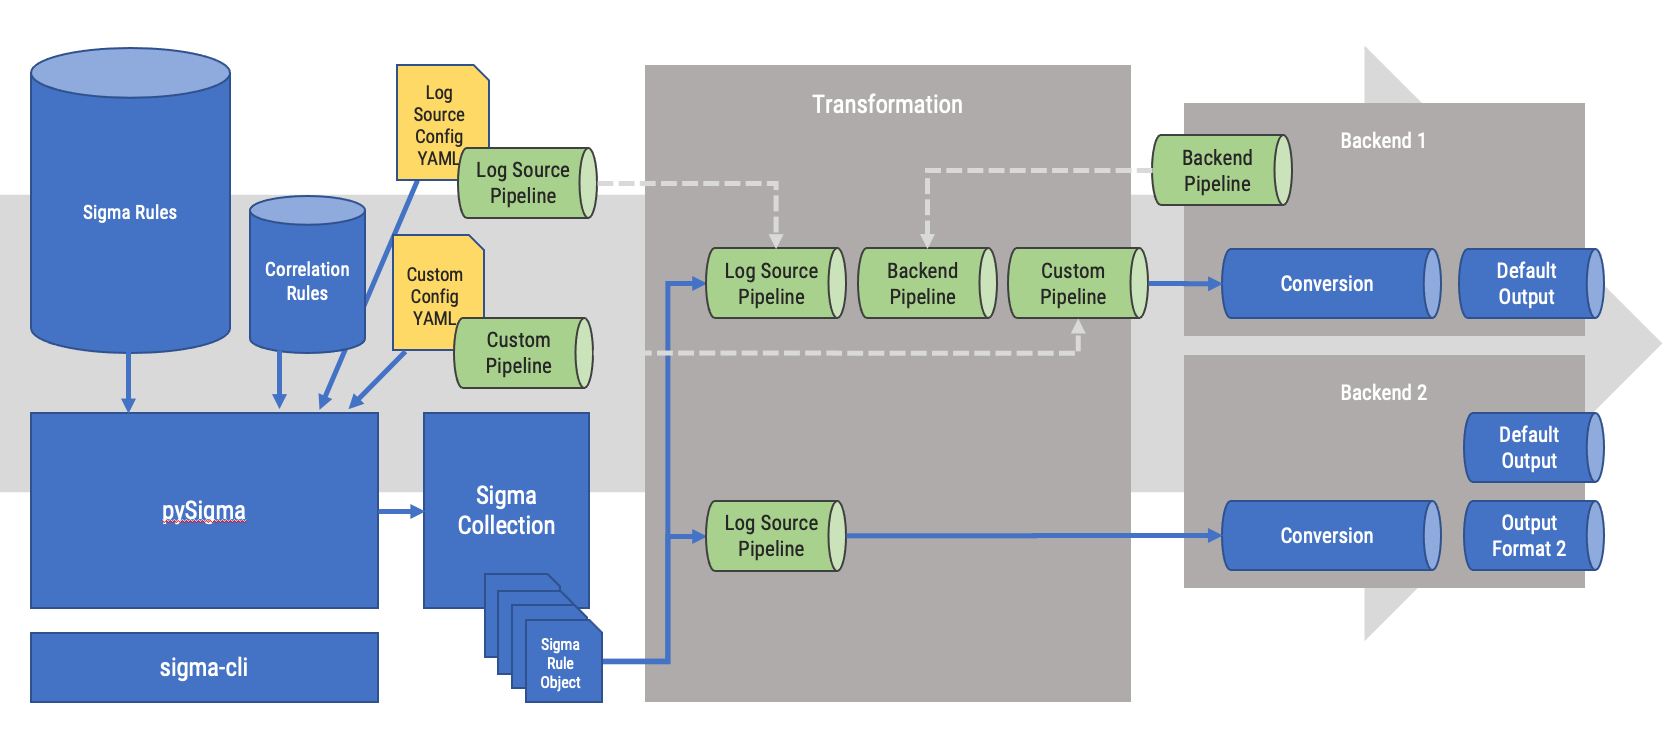 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…







