
 #1
Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.
Kitploit recommended
 ghostop14/sparrow-wifi
Next-Gen GUI-based WiFi and Bluetooth Analyzer for Linux
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
 reprise99/sentinel-queries
Collection of KQL queries

 cocoadebug/cocoadebug
iOS Debugging Tool 🚀
 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 paulsec/awesome-windows-domain-hardening
A curated list of awesome Security Hardening techniques for Windows.
 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
 logpai/loglizer
A machine learning toolkit for log-based anomaly detection [ISSRE'16]
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
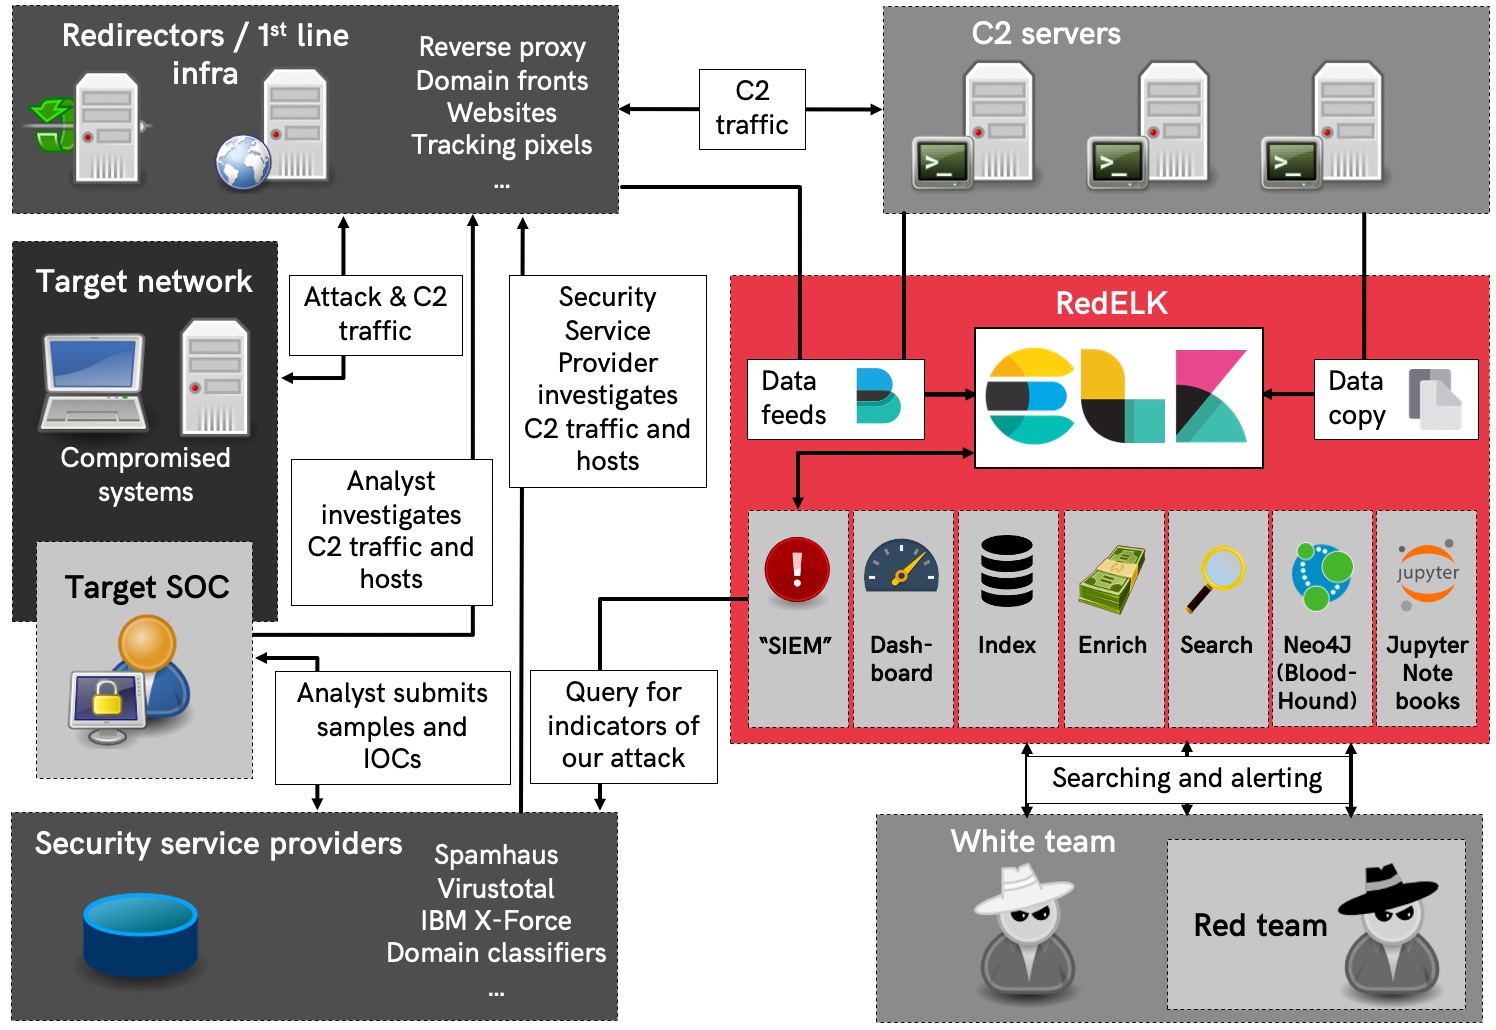 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 neo23x0/auditd
Best Practice Auditd Configuration
 betterdb-inc/monitor
Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
 otrf/ossem
Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…
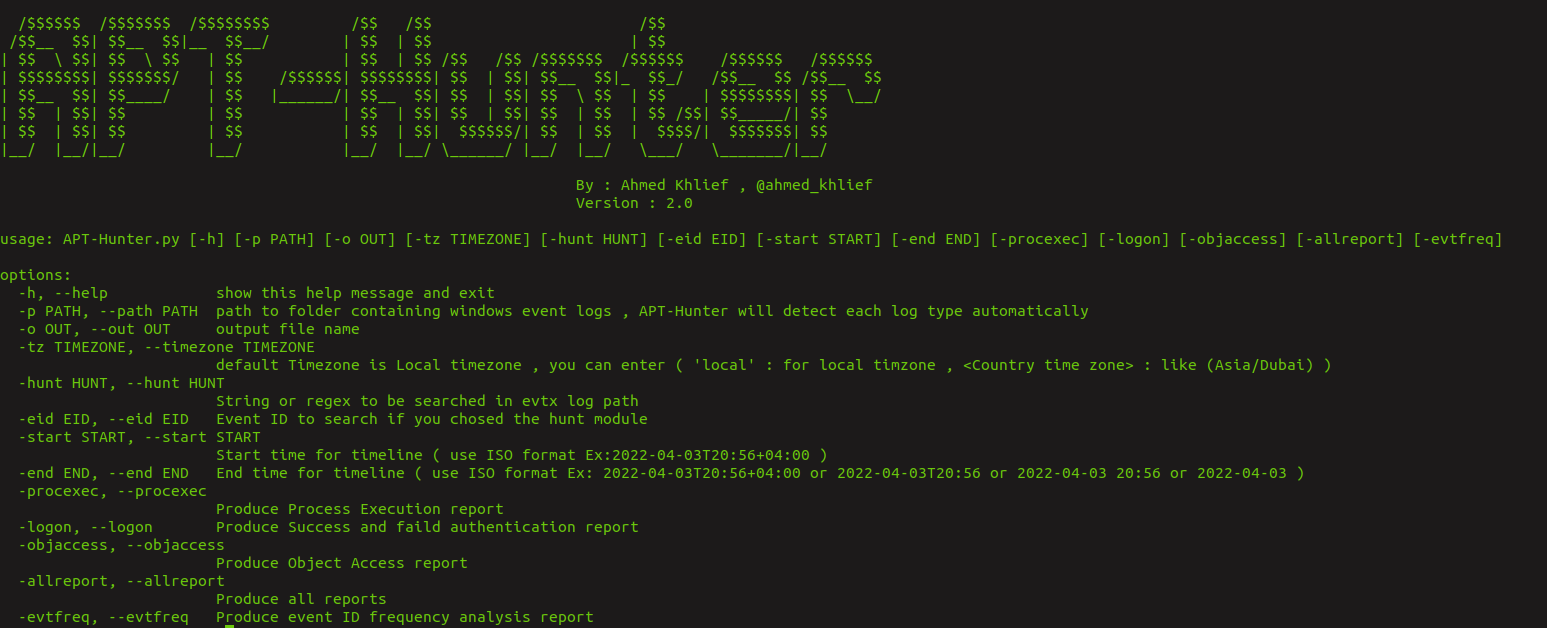 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…








