

ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting 100s of services and evaluations to harden your CSP & SaaS environments with controls mapped to over 20 industry, regulatory, and best practice controls frameworks

ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting 100s of services and evaluations to harden your CSP & SaaS environments with controls mapped to over 20 industry, regulatory, and best practice controls frameworks.


Up here in space
I'm looking down on you
My lasers trace
Everything you do
Judas Priest, 1982
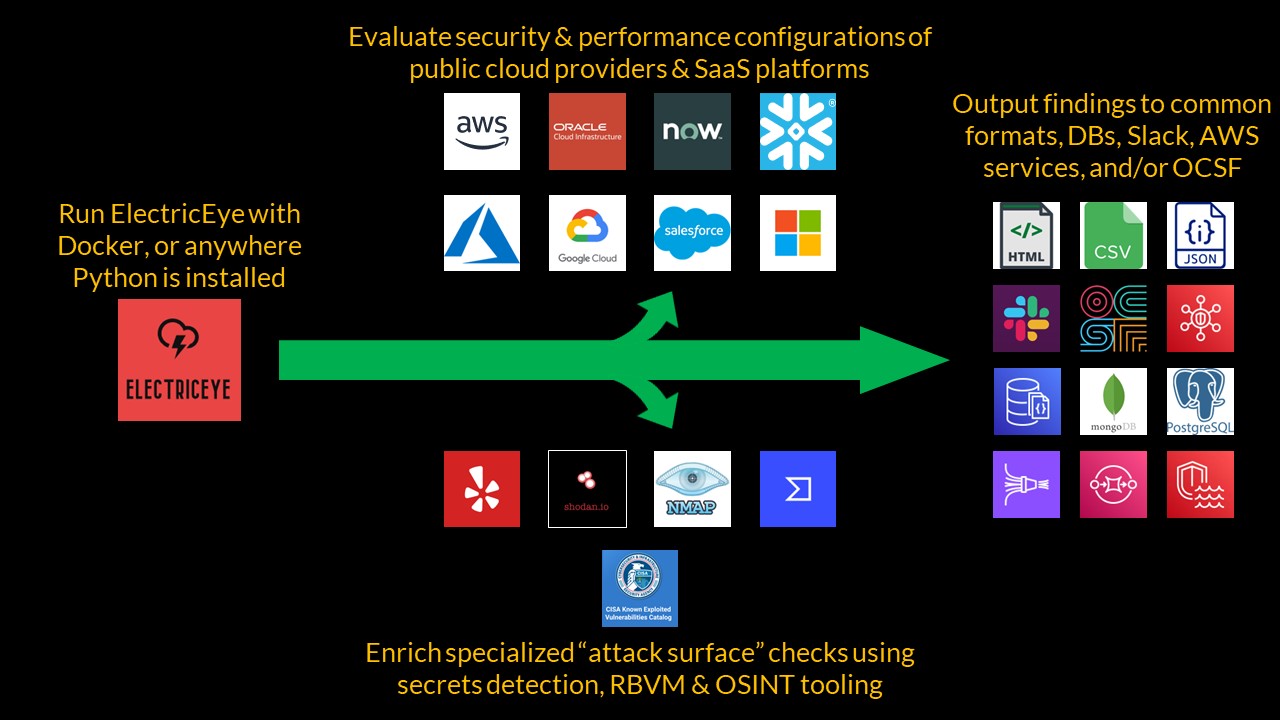
ElectricEye is a Python CLI tool that offers cross-Account, cross-Region, multi-Cloud & SaaS Asset Management, Security Posture Management, and Attack Surface Monitoring capabilities across AWS, all Partitions supported!, GCP, Oracle Cloud Infrastructure (OCI), ServiceNow, Microsoft 365 Enterprise (M365), Salesforce (SFDC), and Azure.
ElectricEye offers over 1000 Checks against security, resilience, performance, and financial best practices across more than 100 CSP & SaaS services, including atypical services not supported by CSP/SaaS-native asset management tools/views or mainstream CSPM & CNAPP tools.
Every single Check is mapped to over 20 controls frameworks covering general best practices, regulatory, industry-specific, and legal frameworks such as NIST CSF, AICPA TSCs (for SOC 2), the HIPAA Security Rule, NIST 800-171 Rev. 2, CMMC V2.0, European Central Bank's CROE Section 2, PCI-DSS V4.0, CIS Foundations Benchmarks, and more!
Multi-faceted Attack Surface Monitoring uses tools such as VirusTotal, Nmap, Shodan.io, Detect-Secrets, and CISA's KEV to locate assets indexed on the internet, find exposed services, locate exploitable vulnerabilities, and malicious packages in artifact repositories, respectively.
Outputs to AWS Security Hub, the Open Cyber Security Framework (OCSF) V1.1.0 in JSON, AWS DocumentDB, JSON, CSV, HTML Reports, MongoDB, Amazon SQS, PostgreSQL, Slack (via Slack App Bots), and FireMon Cloud Defense.
ElectricEye's core concept is the Auditor which are sets of Python scripts that run Checks per Service dedicated to a specific SaaS vendor or public cloud service provider called an Assessment Target. You can run an entire Assessment Target, a specific Auditor, or a specific Check within an Auditor. After ElectricEye is done with evaluations, it supports over a dozen types of Outputs ranging from an HTML executive report to AWS DocumentDB clusters - you can run multiple Outputs as you see fit.
ElectricEye also uses utilizes other tools such as Shodan.io, Yelp's detect-secrets, VirusTotal, the United States Cyber and Infrastructure Security Agency (CISA) Known Exploited Vulnerability (KEV) Catalog, and NMAP for carrying out its Checks and enriching their findings.
First, clone this repository and install the requirements using pip3: pip3 install -r requirements.txt.
If you are evaluating anything other than your local AWS Account, modify the TOML configuration located in ElectricEye/eeauditor/external_providers.toml, or provide a path to your own with with --toml-path. The TOML file specifies multi-account, mulit-region, credential, and output specifics.
Finally, run the Controller to learn about the various Checks, Auditors, Assessment Targets, and Outputs.
python3 eeauditor/controller.py --help
Usage: controller.py [OPTIONS]







