
 #1
Tools for acquiring, preserving, and analyzing digital evidence for legal or investigative purposes.
Kitploit recommended
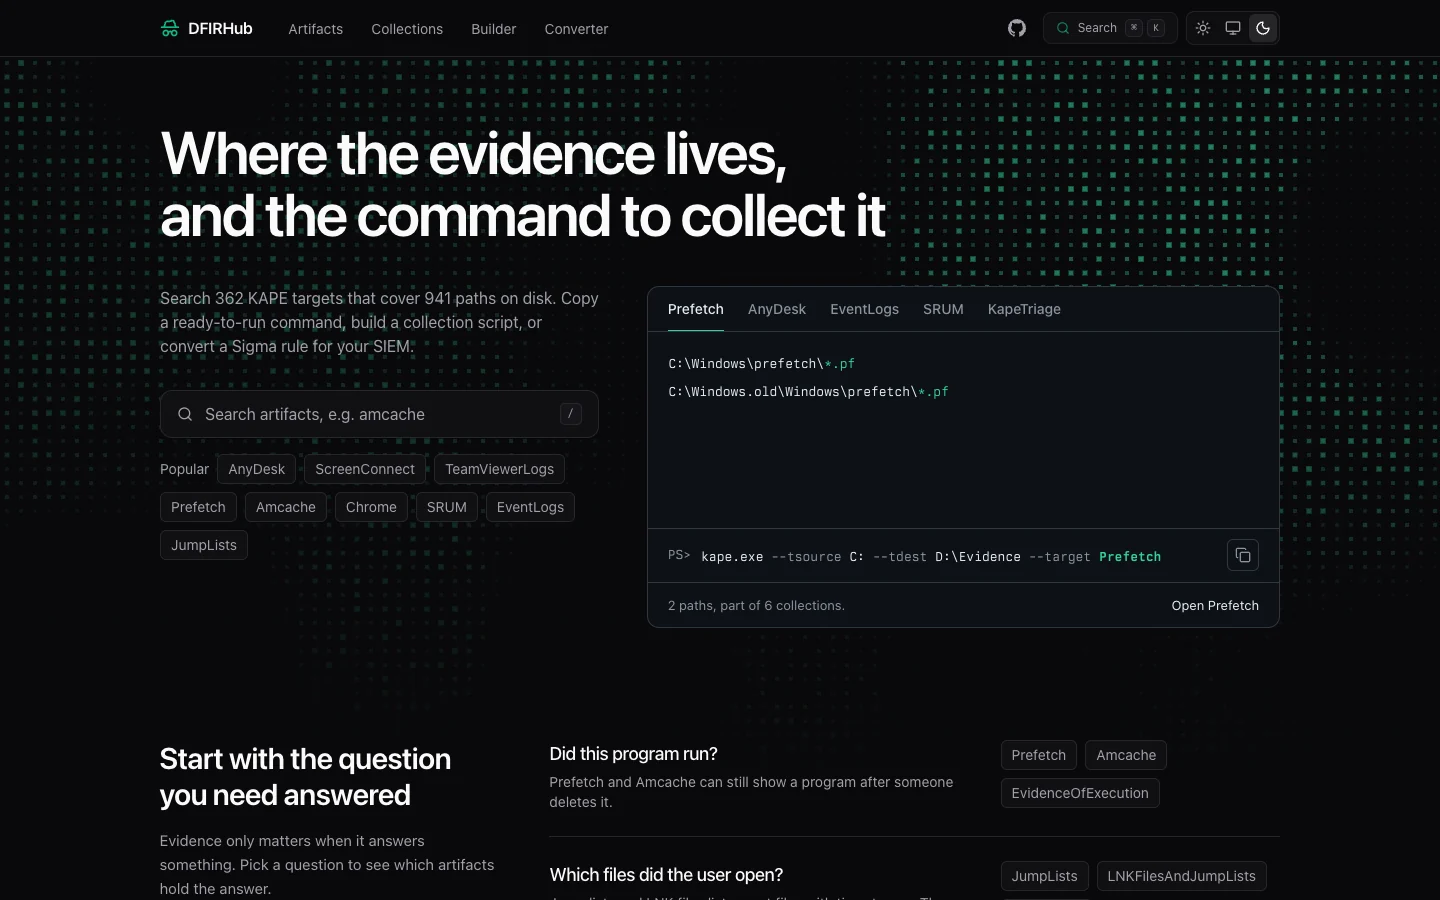
 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
 abraxas/qemu-colo-l4-oob
QEMU 11.1.2 - High - Local/Remote - OOB - COLO filter-rewriter short IPv4 L4 heap overflow
 abraxas/qemu-nvme-sgl-bar
QEMU 11.1.2 - High - Local - UAF - NVMe SGL span into BAR0 incomplete CVE-2021-3929
 abraxas/qemu-xhci-complete-uaf
QEMU 11.1.2 - High - Local - UAF - xhci_complete leftover of CVE-2026-17588 doorbell DMA
 abraxas/vbox-hgcm-ssm-cparms
VirtualBox 7.2.20 - High - Local - Heap overflow - HGCM SSM cParms wrap
 abraxas/vbox-lsilogic-sas-config
VirtualBox 7.2.20 - Critical - Local - Type confusion / arb R/W - SAS1068 CONFIG SCSI-SPI overlay
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 0xblackash/cve-2026-110912
Python/scapy proof-of-concept for CVE-2026-110912 (ARPBleed), an ARP ar_hln/ar_pln out-of-bounds read in DragonFly BSD that leaks kernel heap and…
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
 gmh5225/memtools
Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
 gmh5225/mapped-dumper
A program written in C++ for remotely dumping manual mapped modules.
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
 dwexi/entropystrip
Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine








