
 #1
Tools for acquiring, preserving, and analyzing digital evidence for legal or investigative purposes.
Kitploit recommended
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
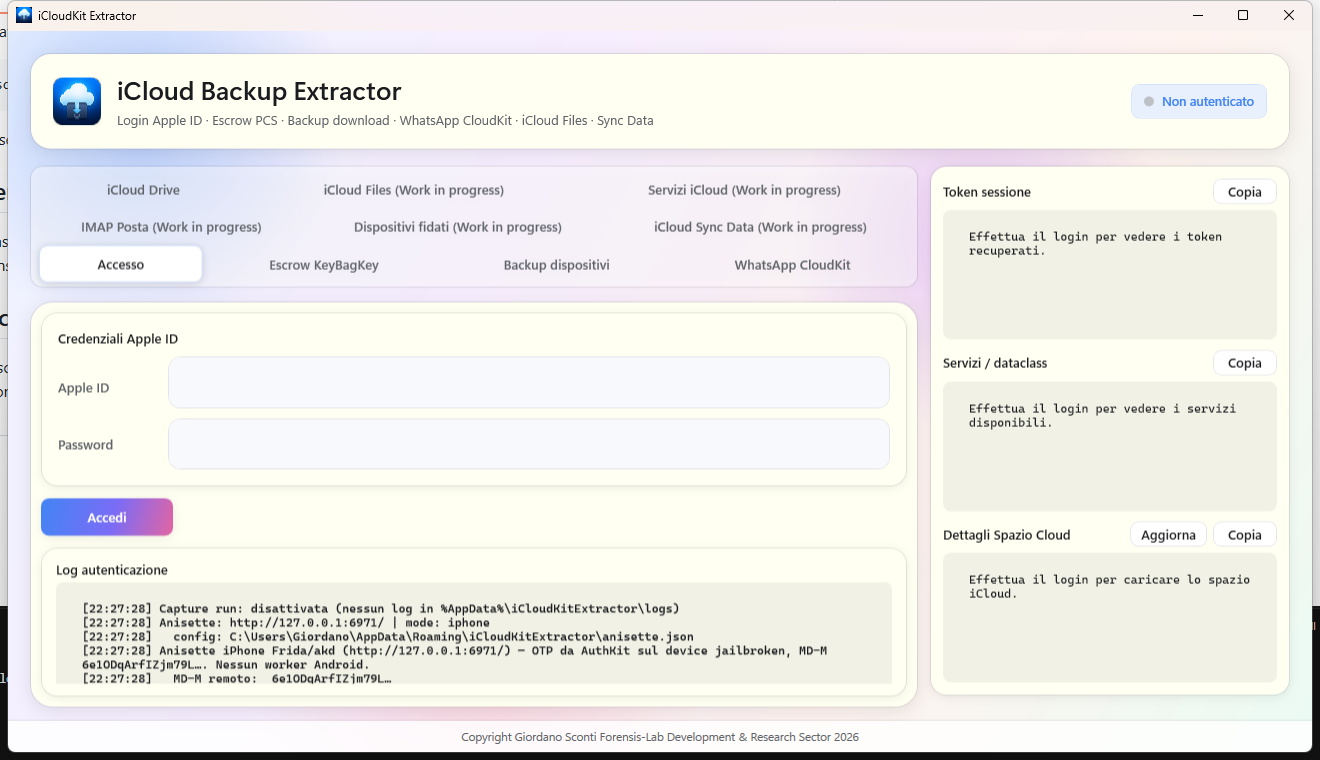 giordanosconti/icloudkitextractor
Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 blacktop/ipsw
iOS/macOS Research Swiss Army Knife
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 rdelasierra-uy/portfolio
Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…
 bitcoin/bitcoin
Full-node Bitcoin client that validates transactions and blocks on the peer-to-peer network, with integrated wallet, cryptographic security, and…







