
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended
 protectai/modelscan
Protection against Model Serialization Attacks
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
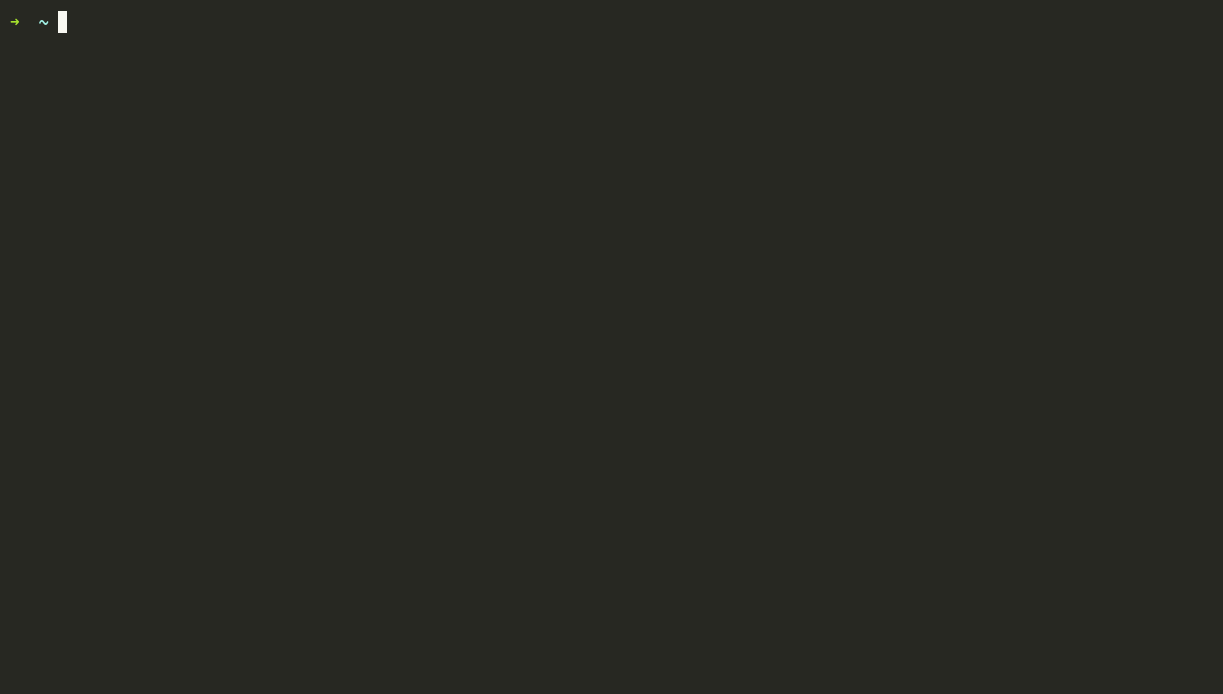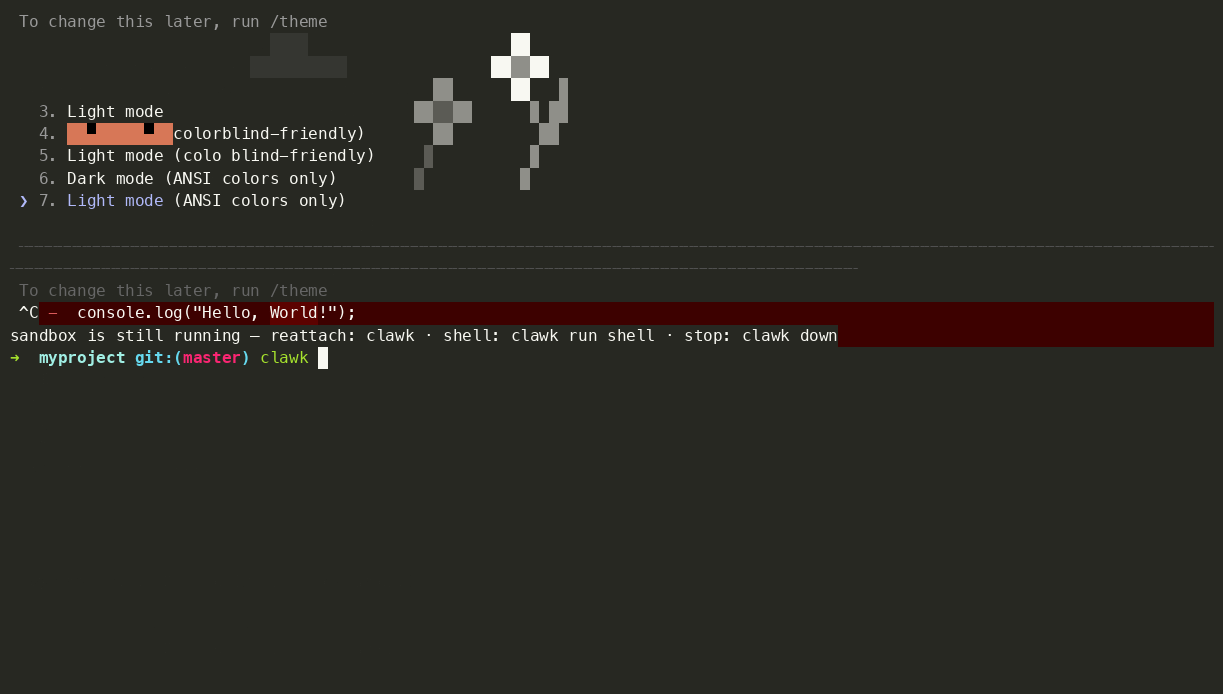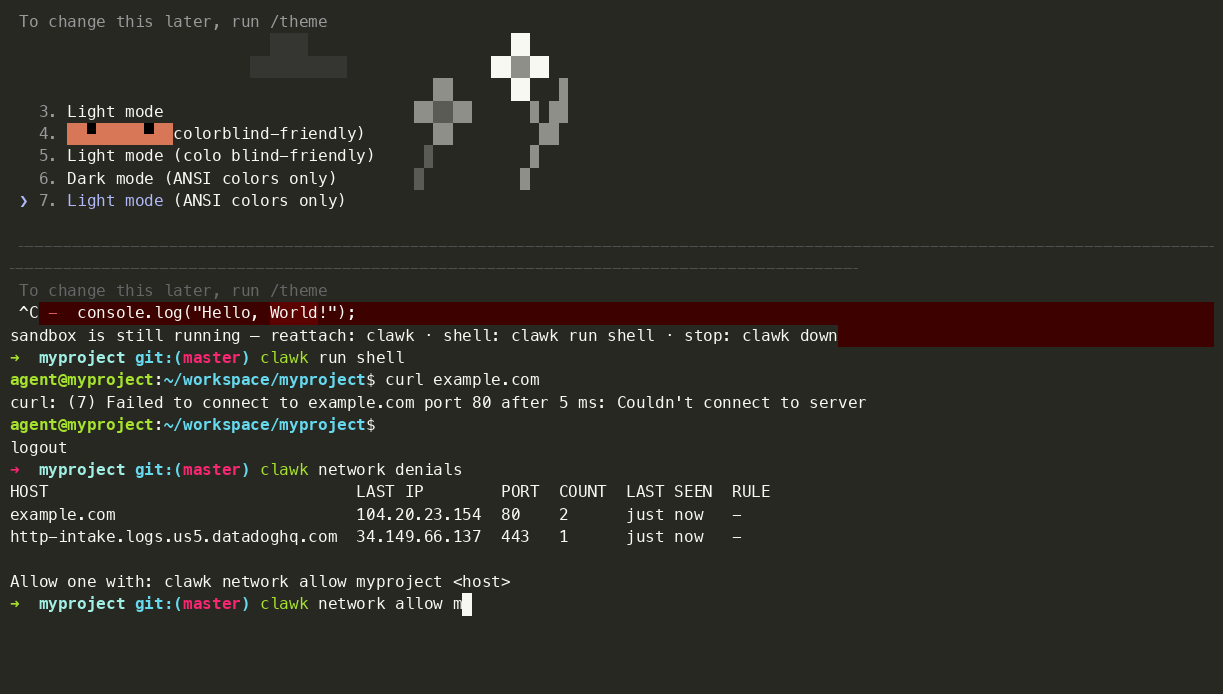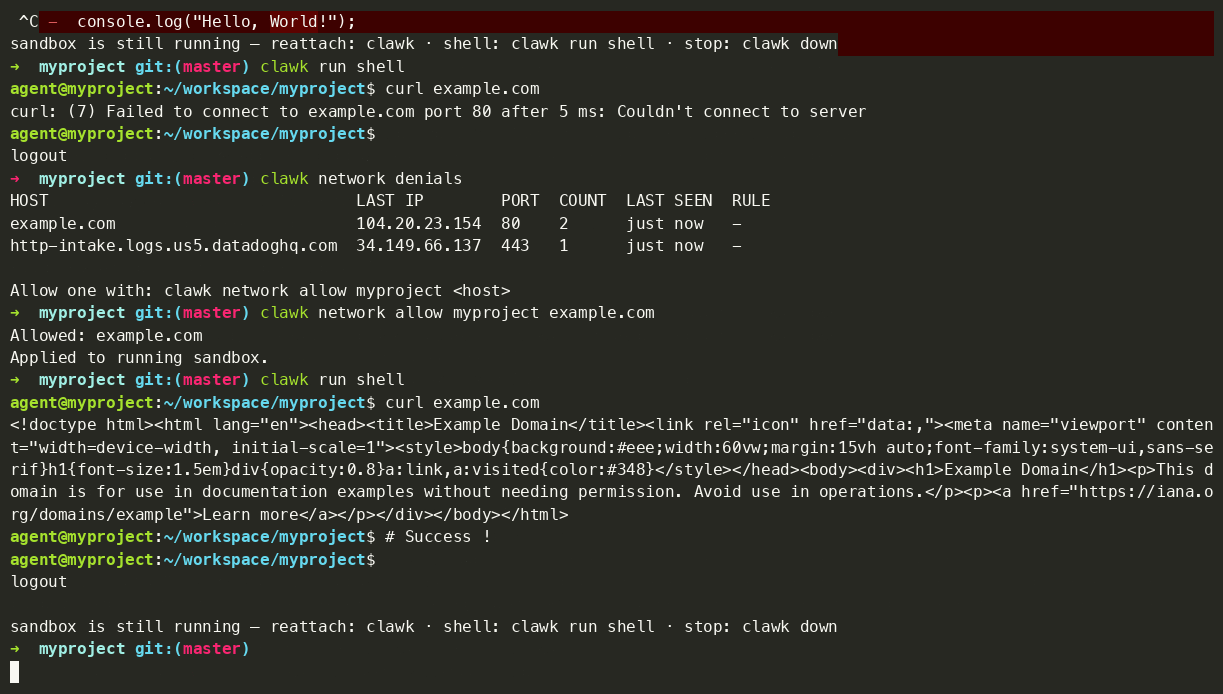 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 adversis/tailsnitch
A security auditor for Tailscale configurations. Scans your tailnet for misconfigurations, overly permissive access controls, and security best…
 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
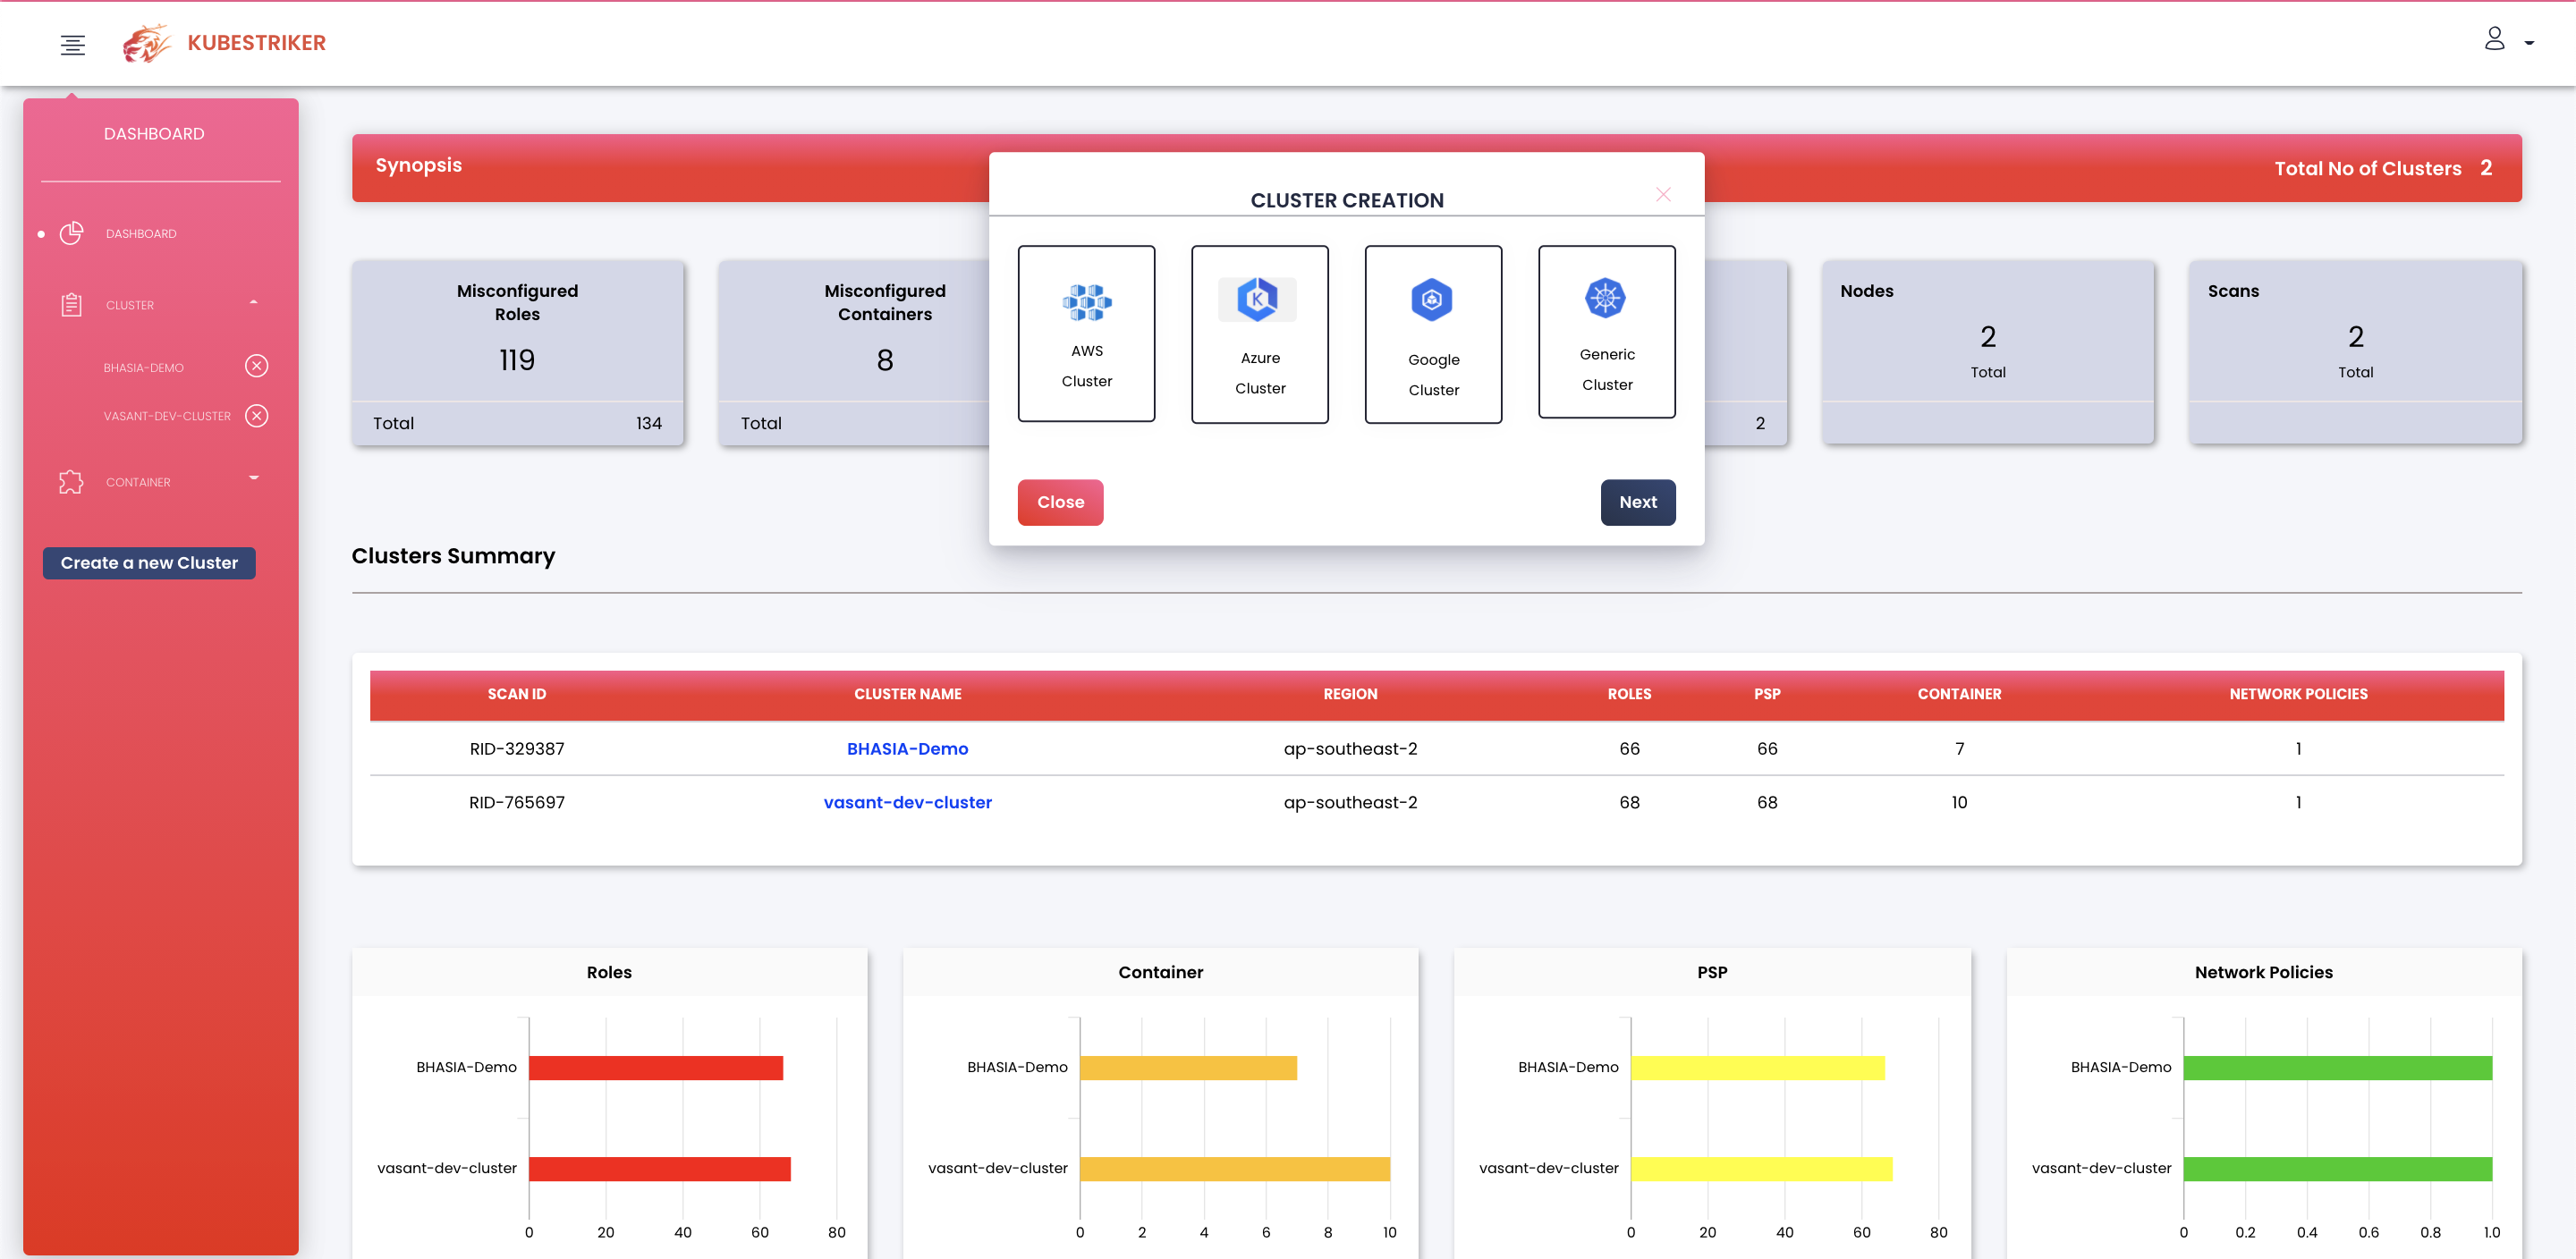 vchinnipilli/kubestriker
A Blazing fast Security Auditing tool for Kubernetes
 p0ssuidao/terraguard
🛡️ 🔒 This project's goal is to be simple to create and destroy your own VPN service using WireGuard.
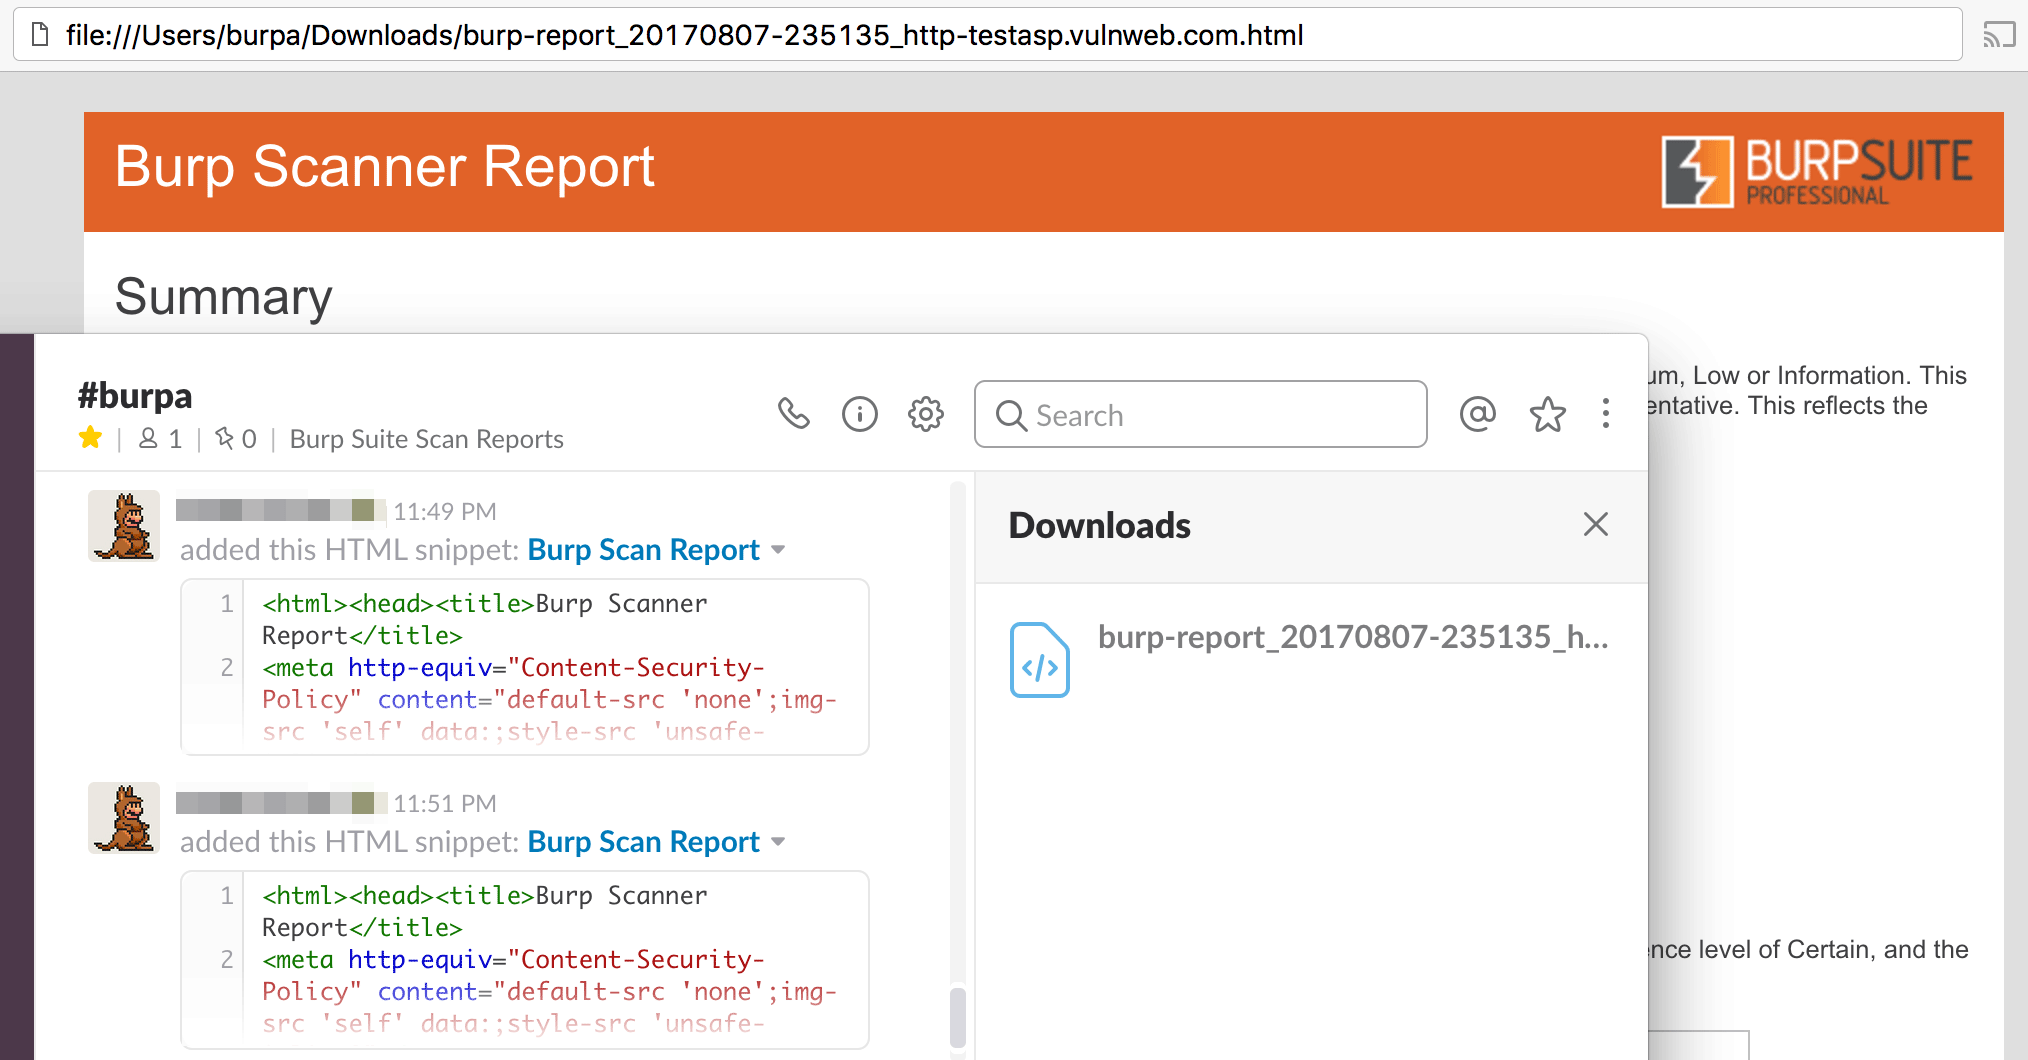 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 newrelic/rusty-hog
Multi-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…
 ossillate-inc/packj
Static and dynamic analysis tool that audits open-source packages for malicious, vulnerable, and risky attributes, with sandboxed installation to…
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
 liske/needrestart
System utility that identifies and restarts daemons using outdated libraries after package upgrades to maintain security. Supports containers and…
 threatcl/threatcl
Documenting your Threat Models with HCL








