#1

 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 legit-labs/legitify
Detect and remediate misconfigurations and security risks across all your GitHub and GitLab assets
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
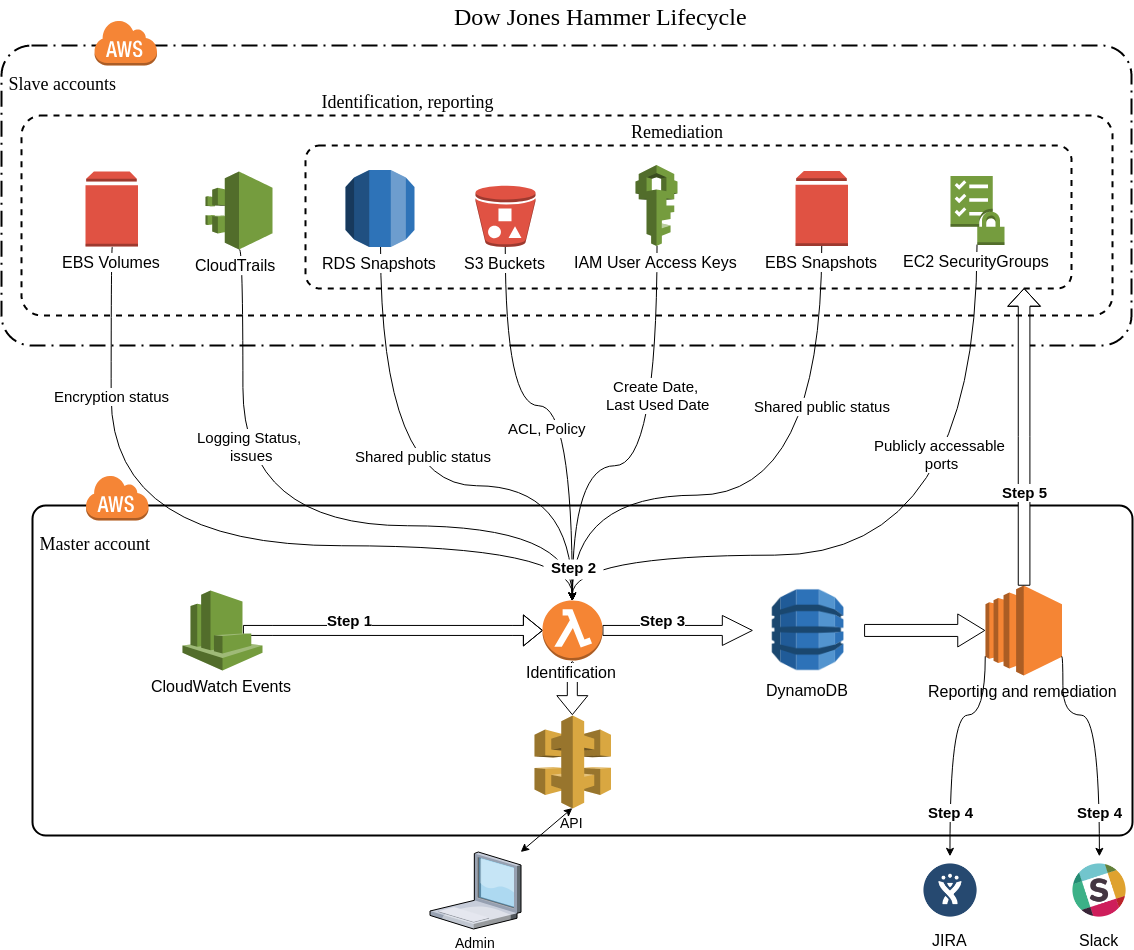 dowjones/hammer
Dow Jones Hammer : Protect the cloud with the power of the cloud(AWS)
 dev-sec/chef-os-hardening
This chef cookbook provides numerous security-related configurations, providing all-round base protection.
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 aerleon/aerleon
Generate firewall ACLs for Cisco, Juniper, Palo Alto, and more from a single YAML policy language via CLI or Python API.
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 cloudgraphdev/cli
The universal GraphQL API and CSPM tool for AWS, Azure, GCP, K8s, and tencent.
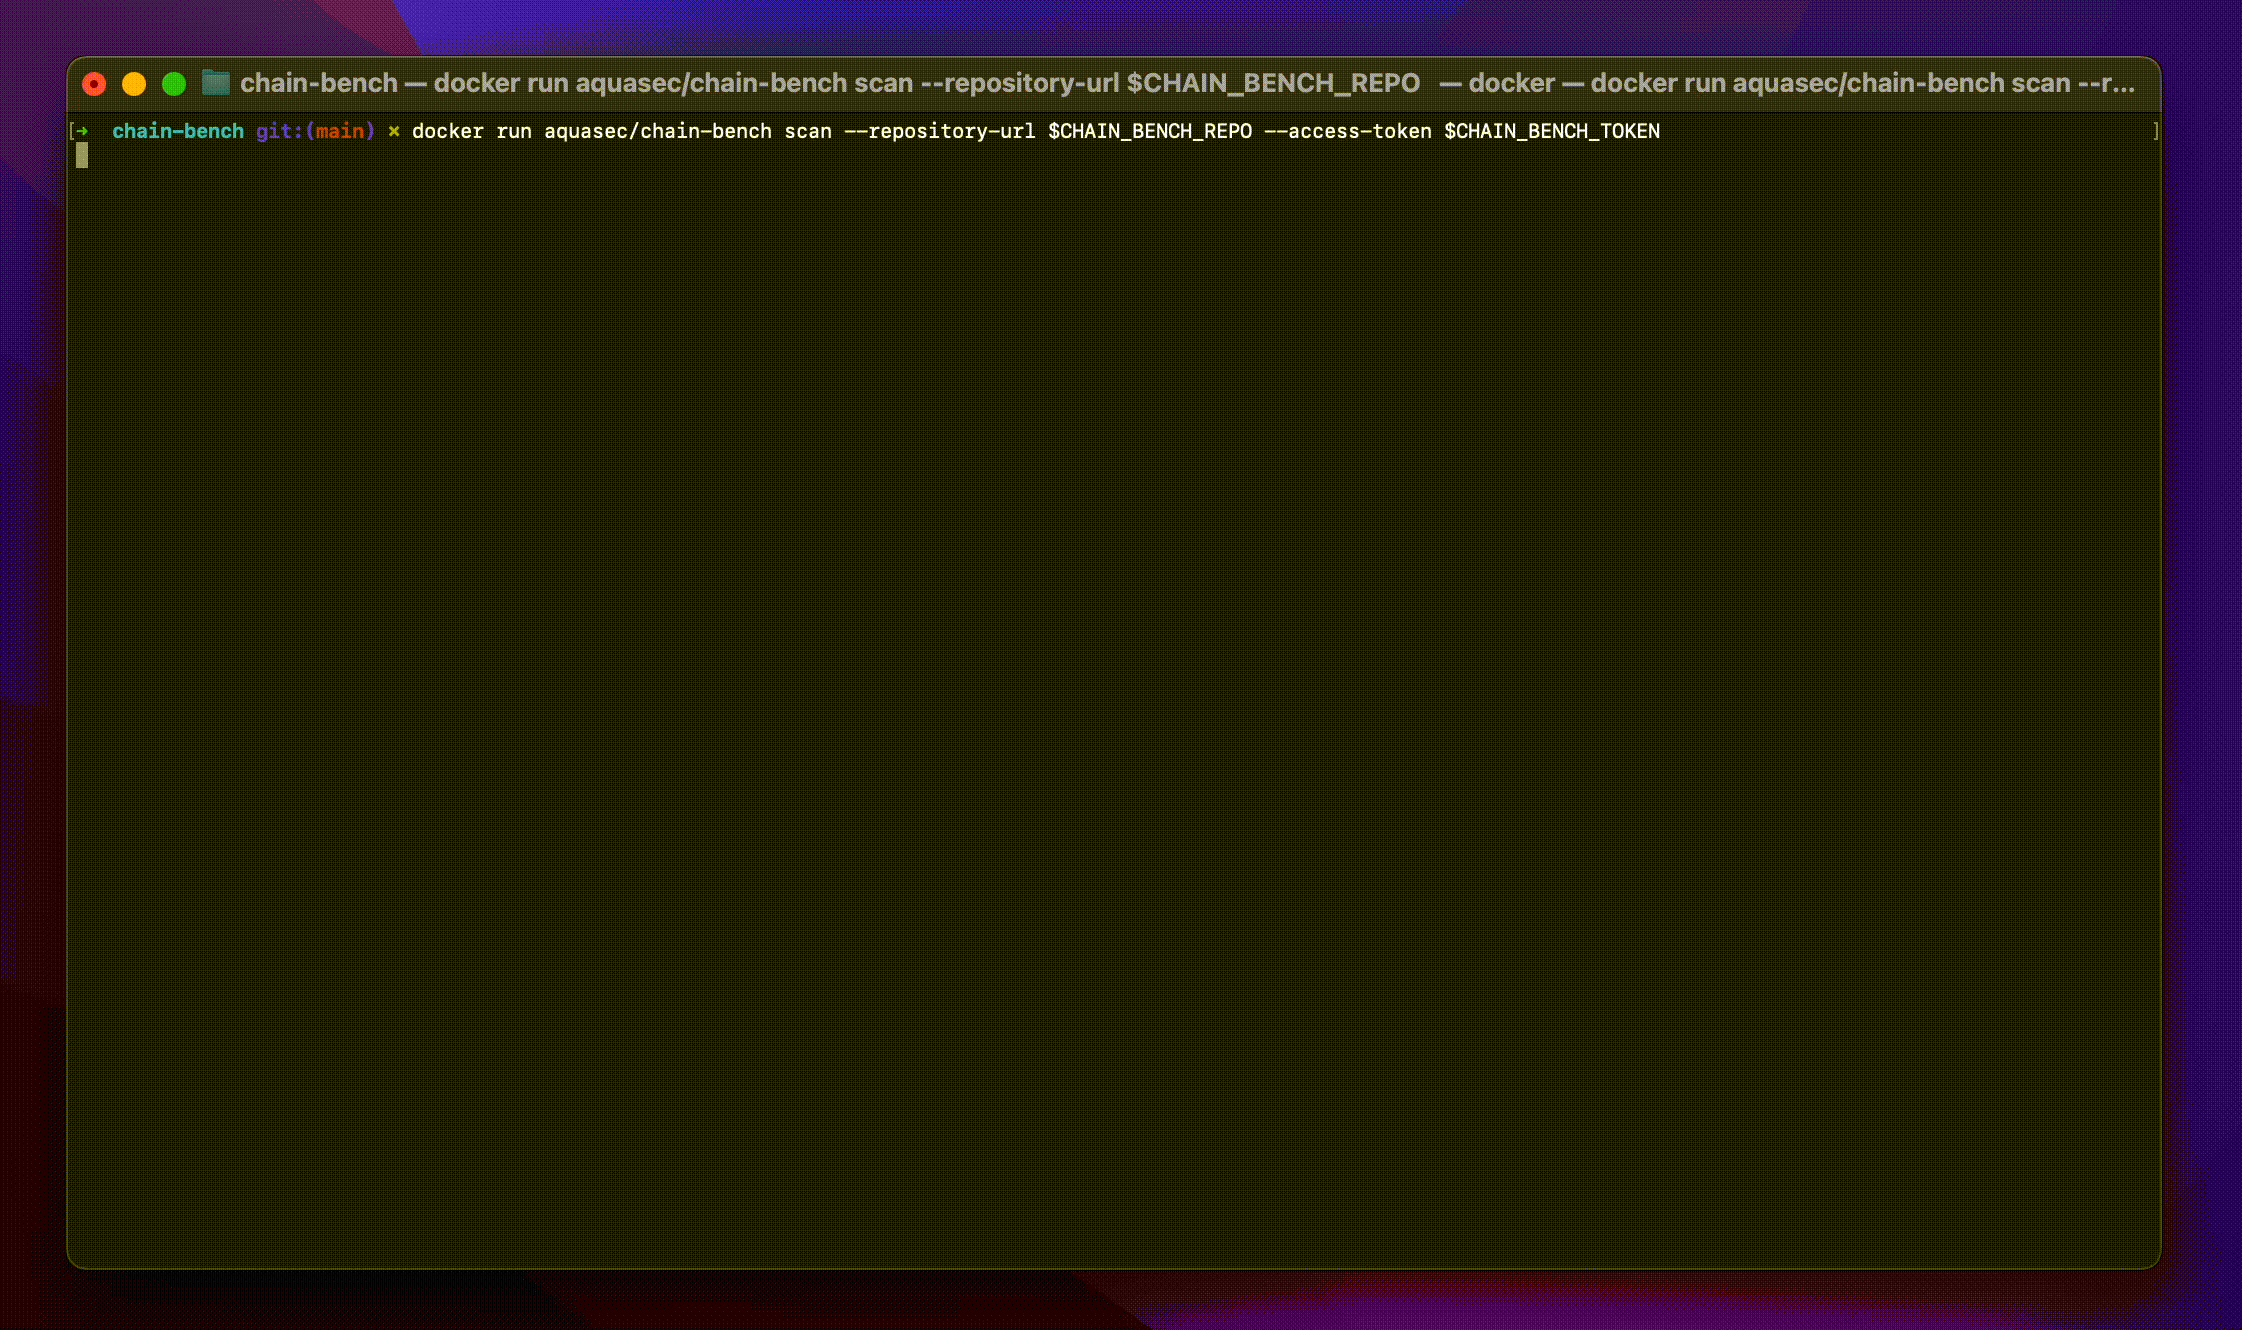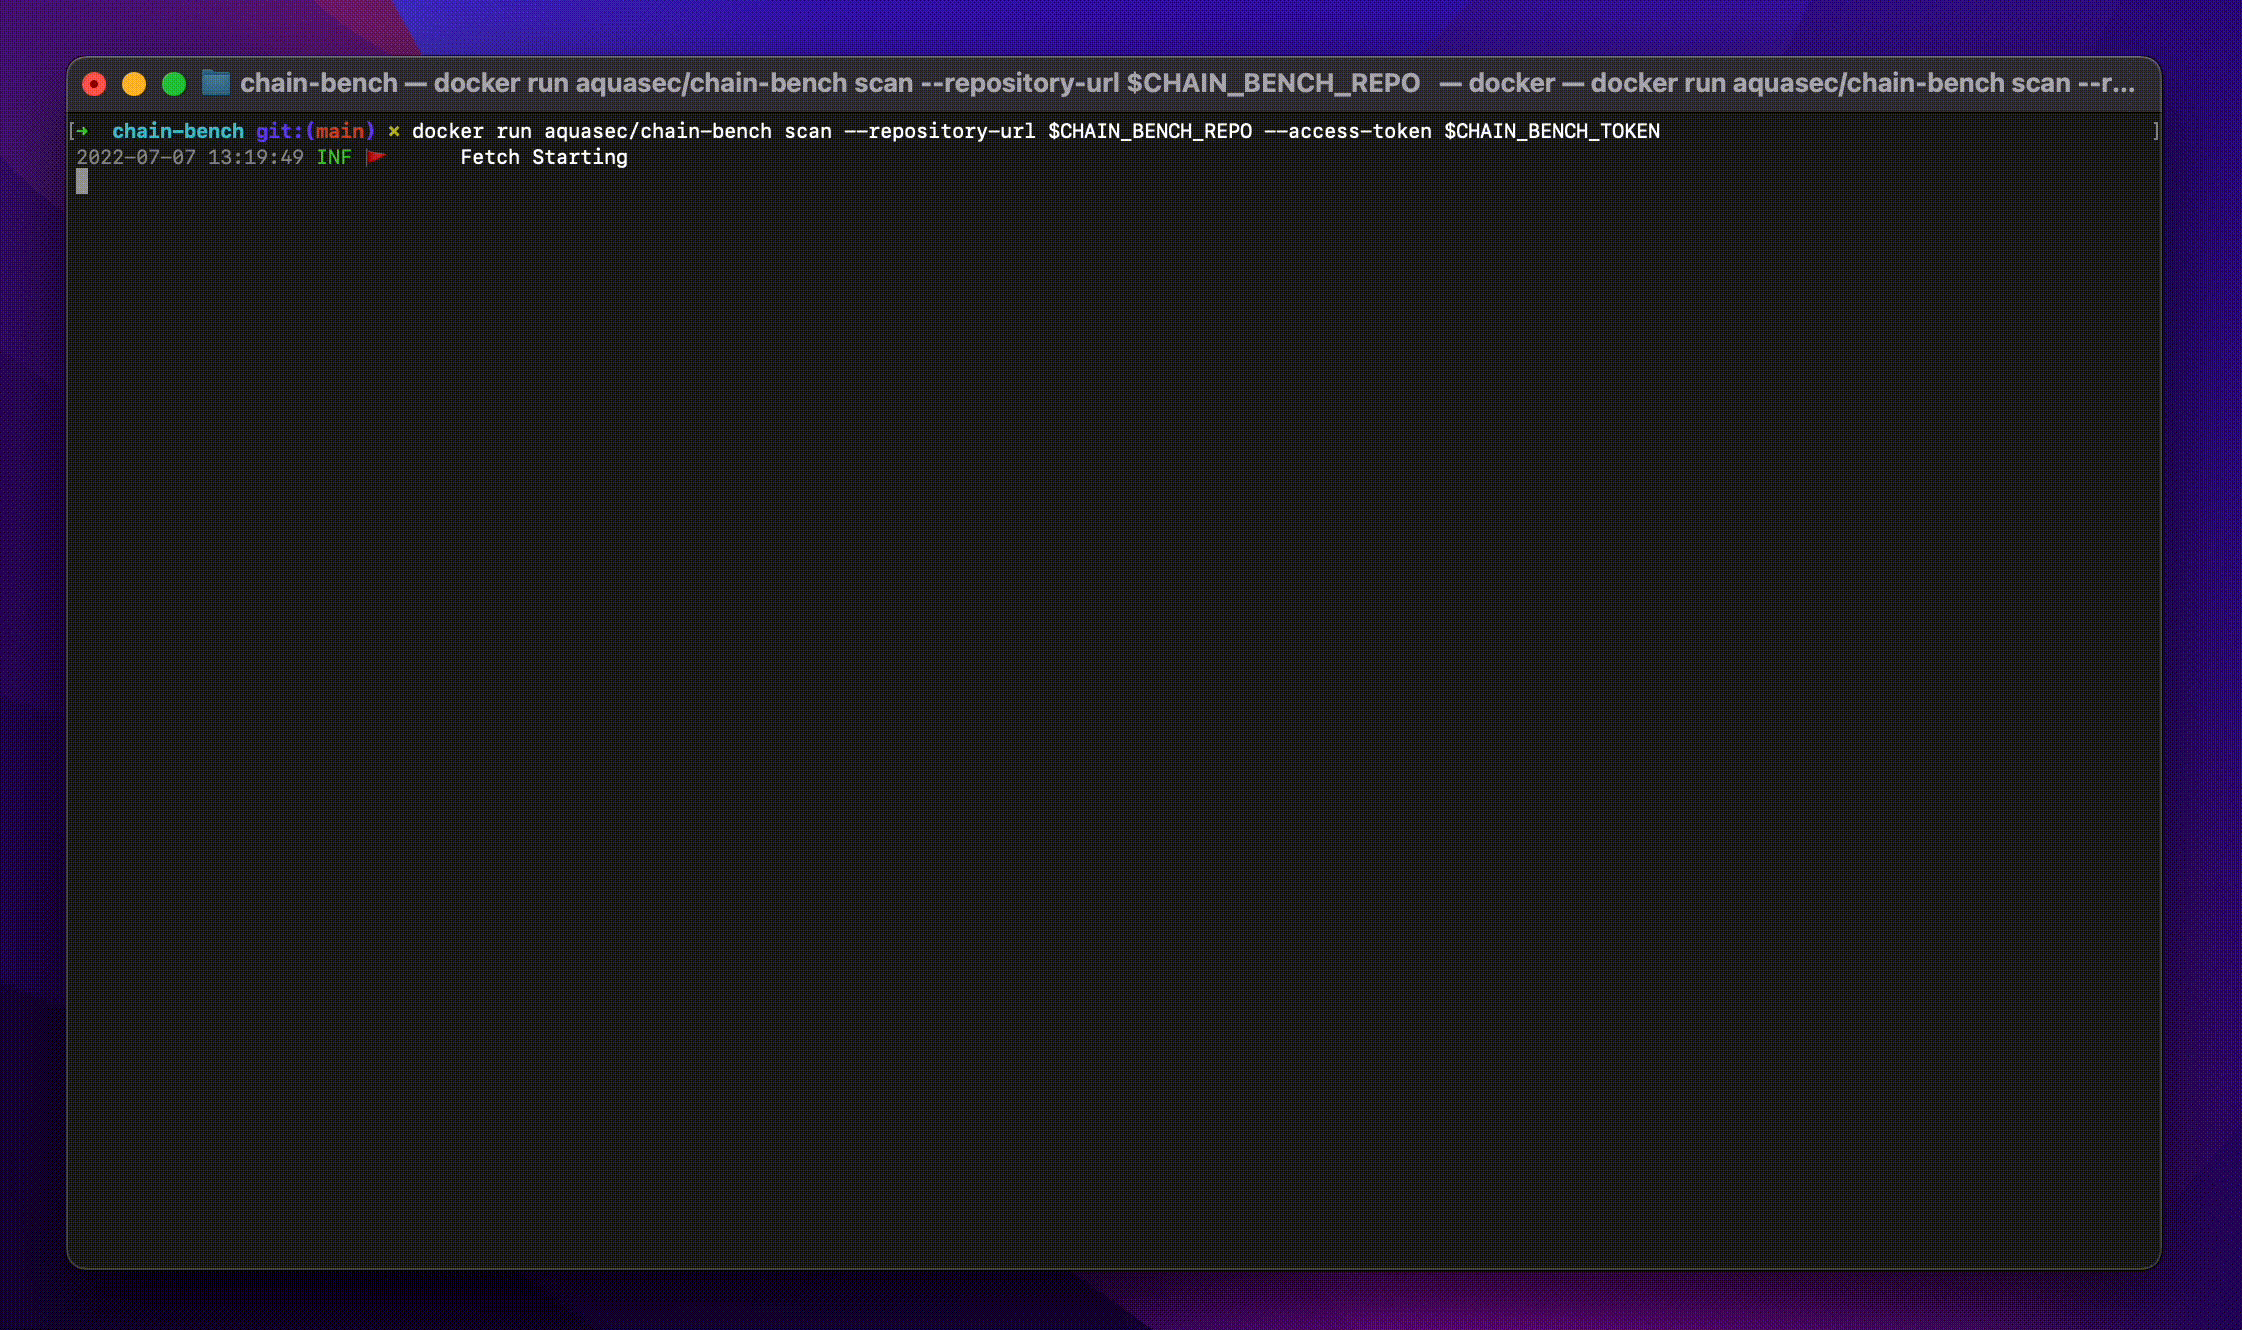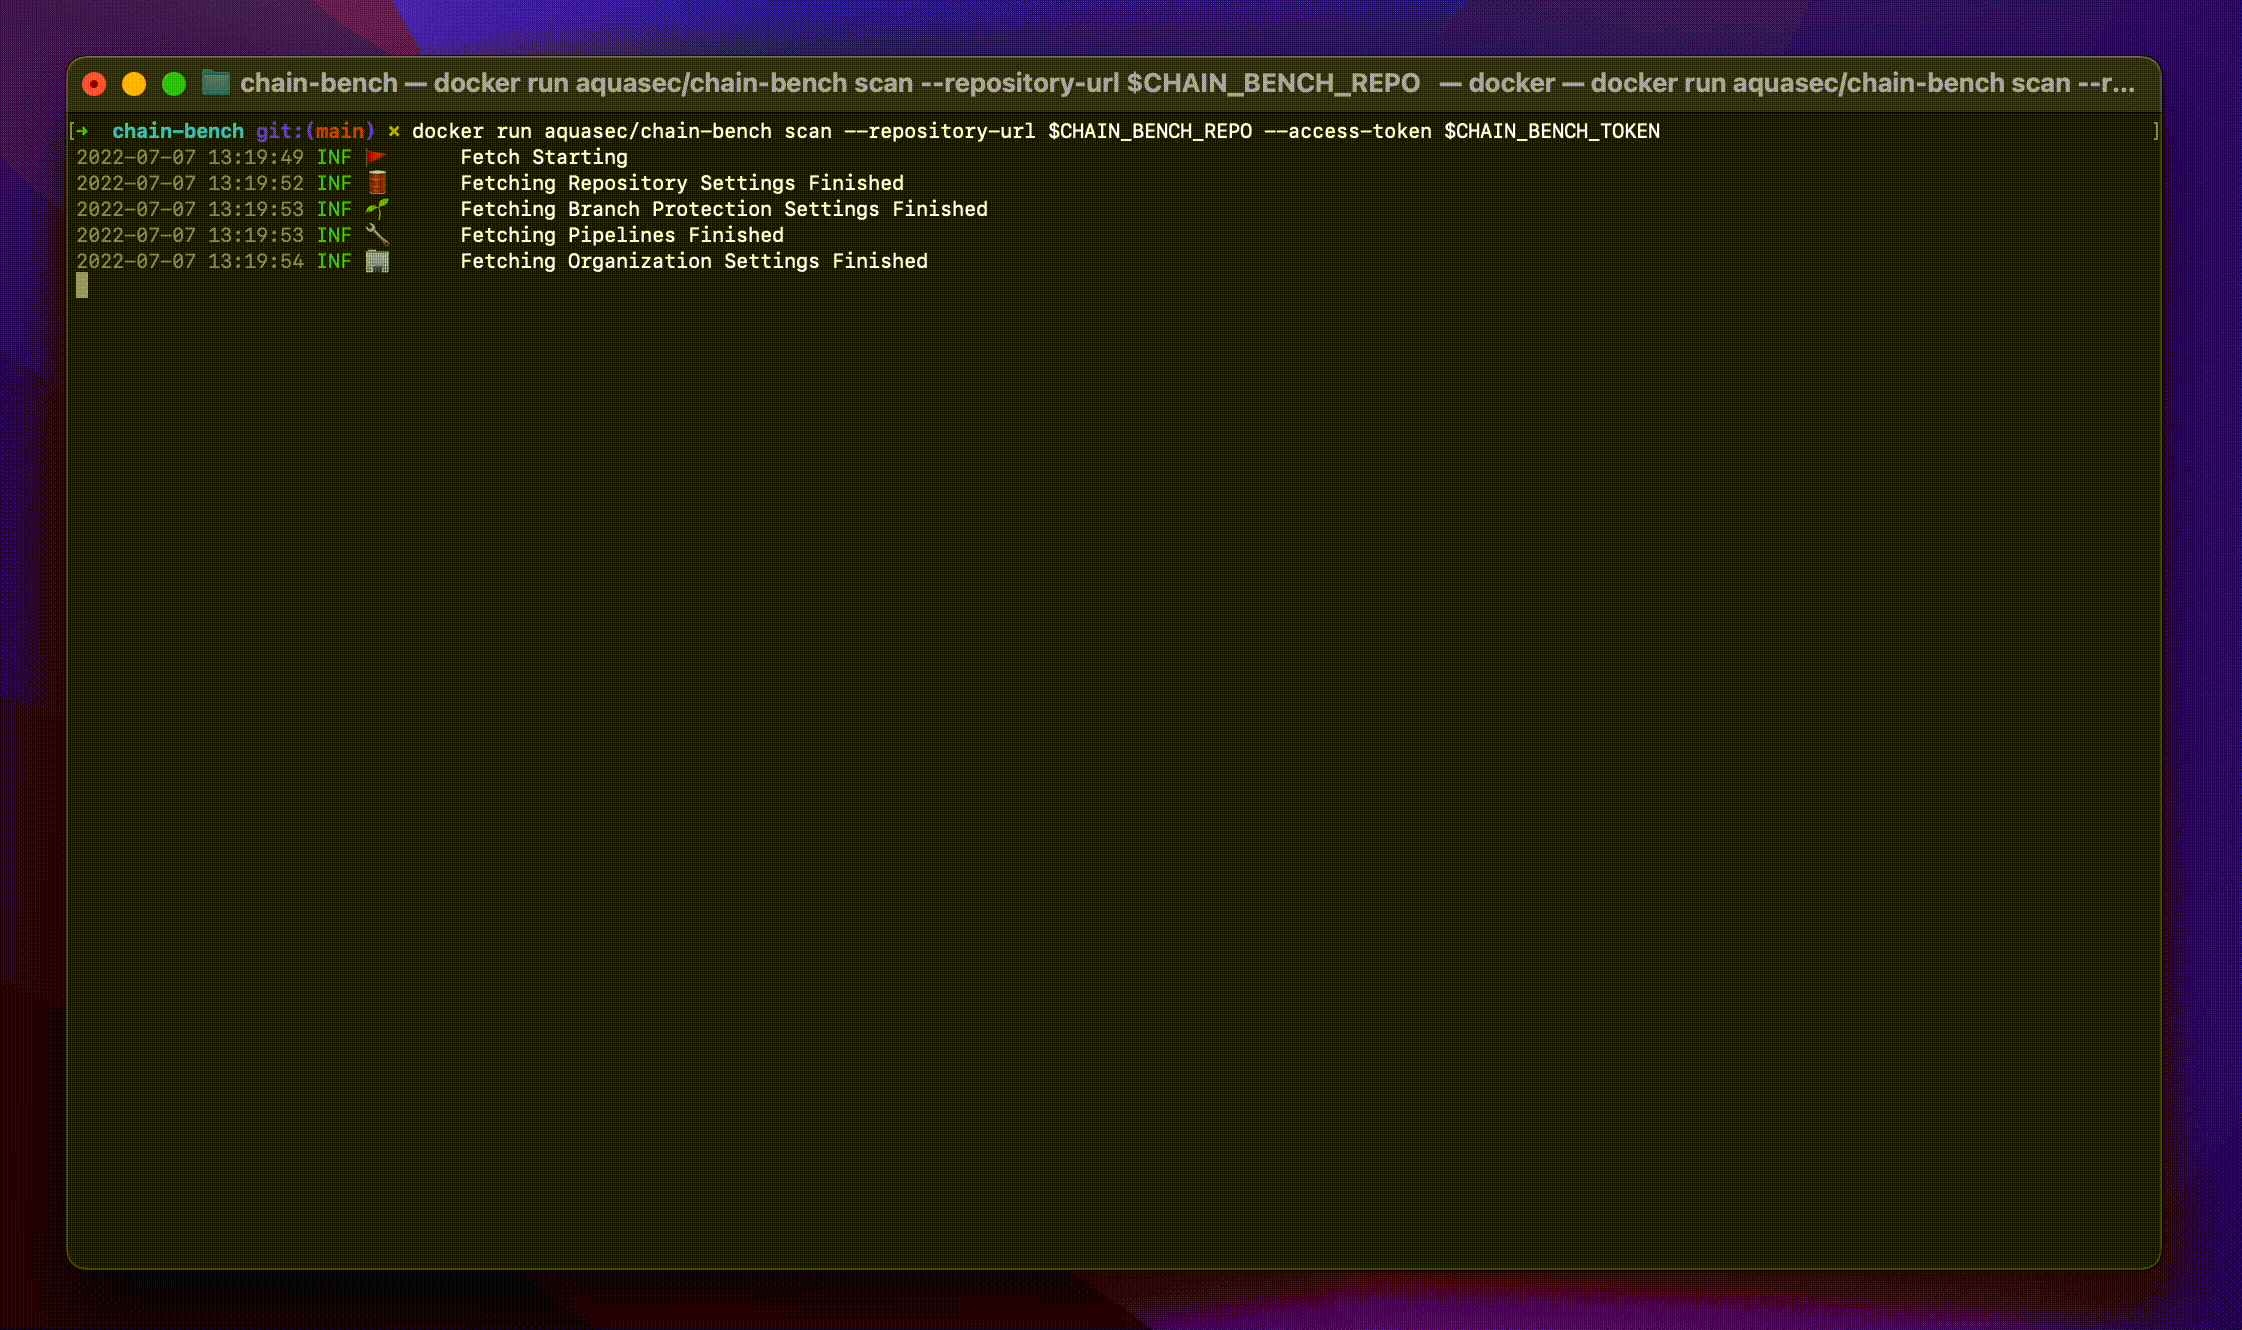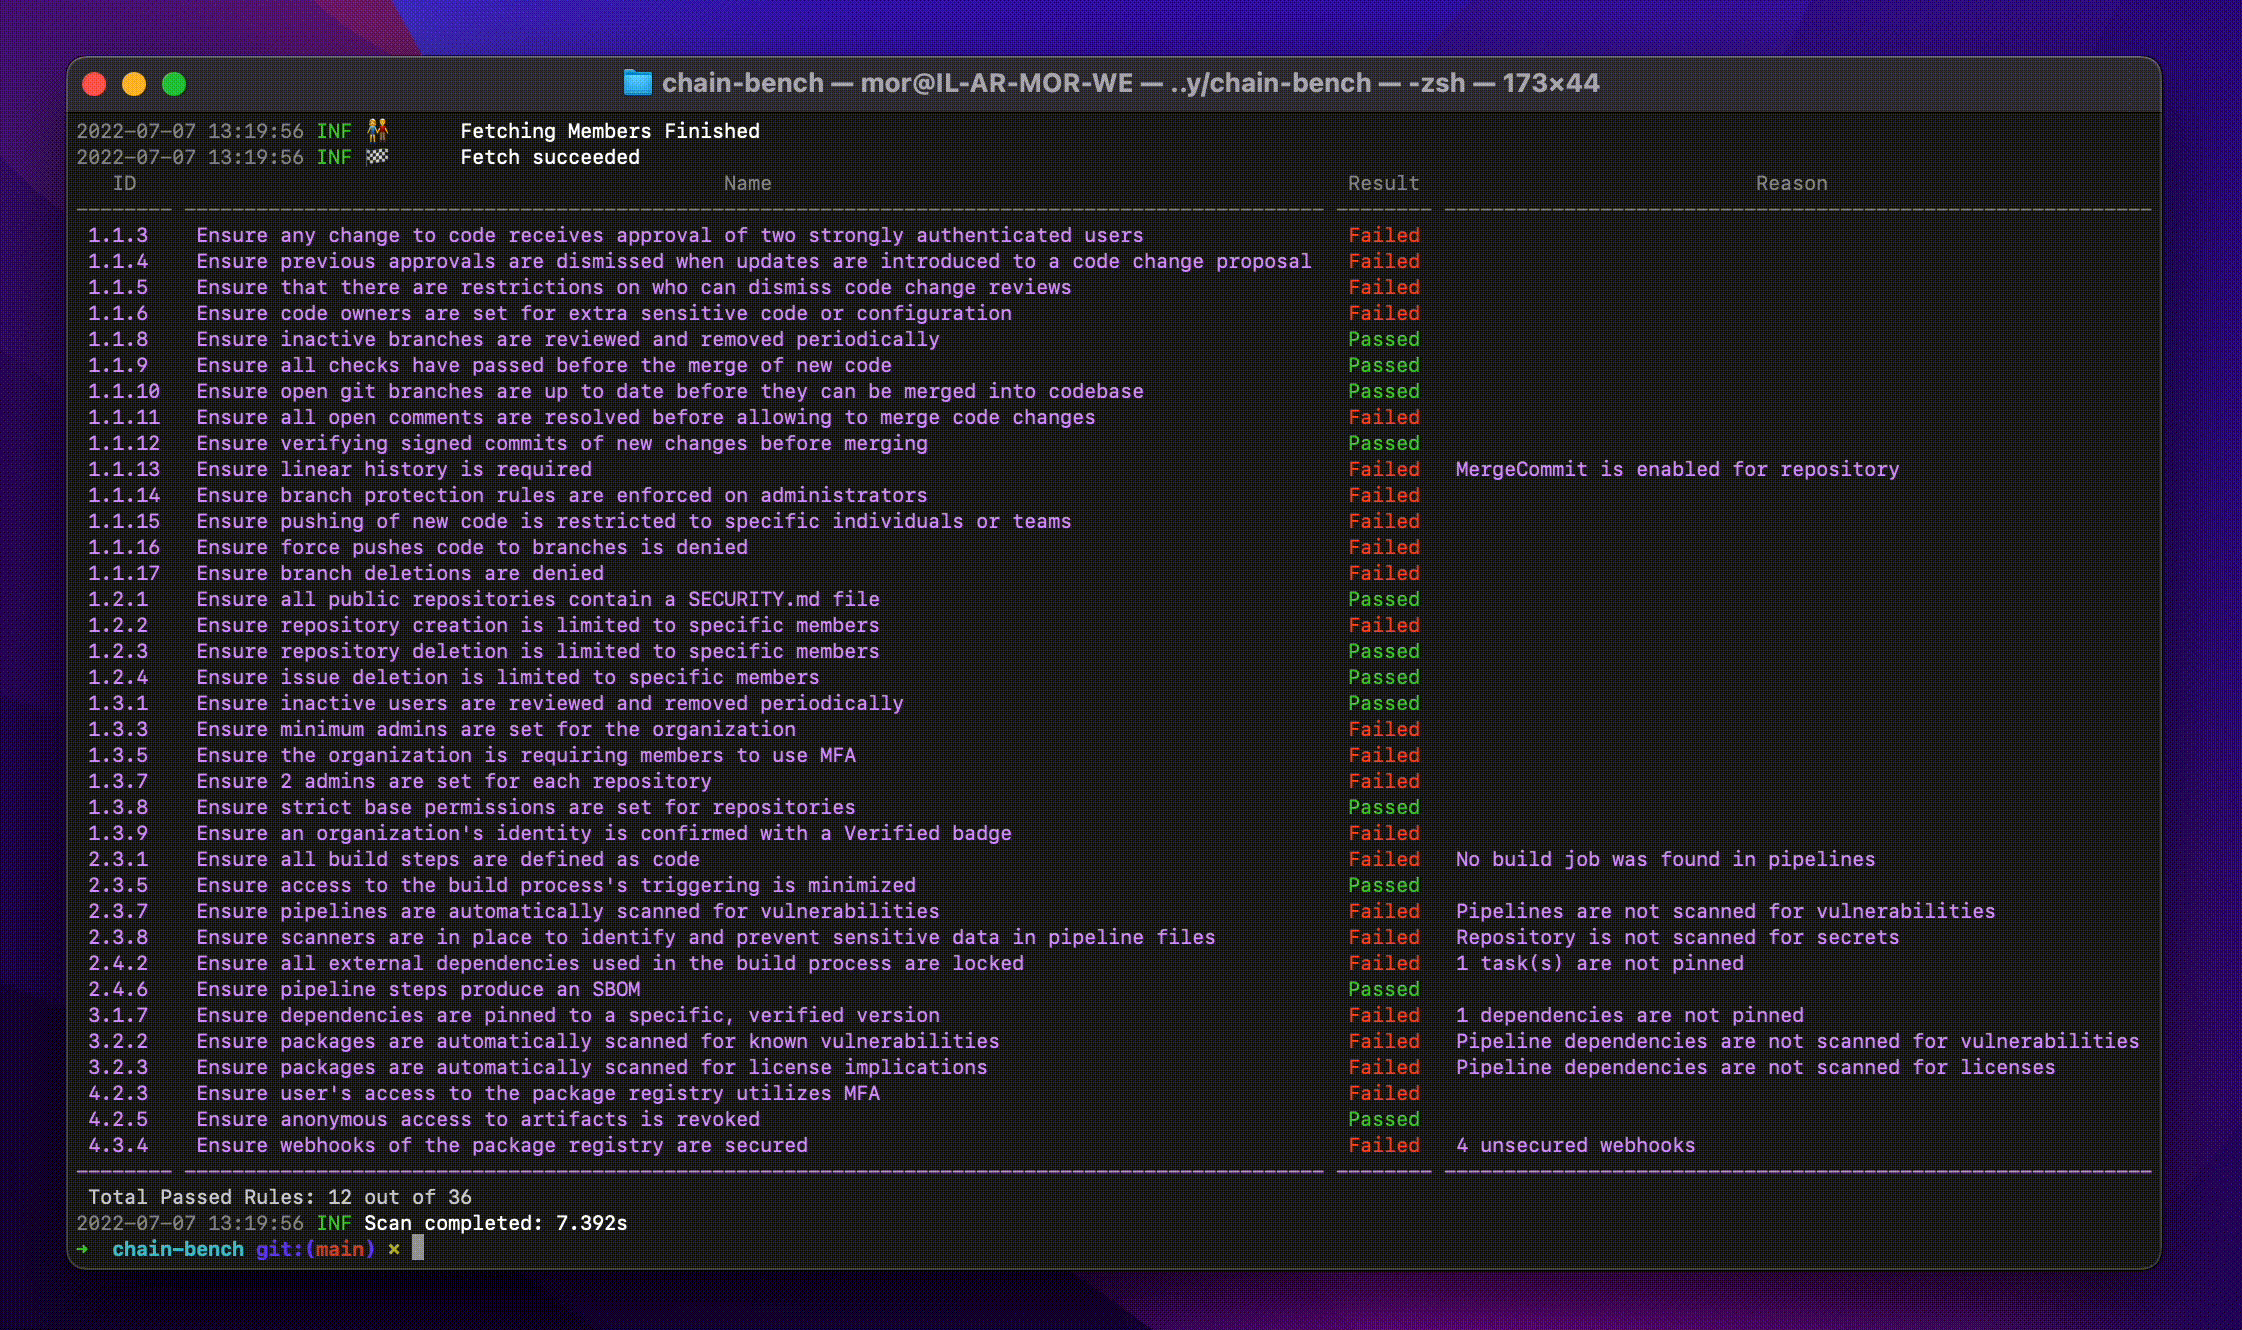 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
 batfish/pybatfish
Python client for Batfish, a network configuration analysis tool that validates security, reliability, and compliance by modeling network behavior…
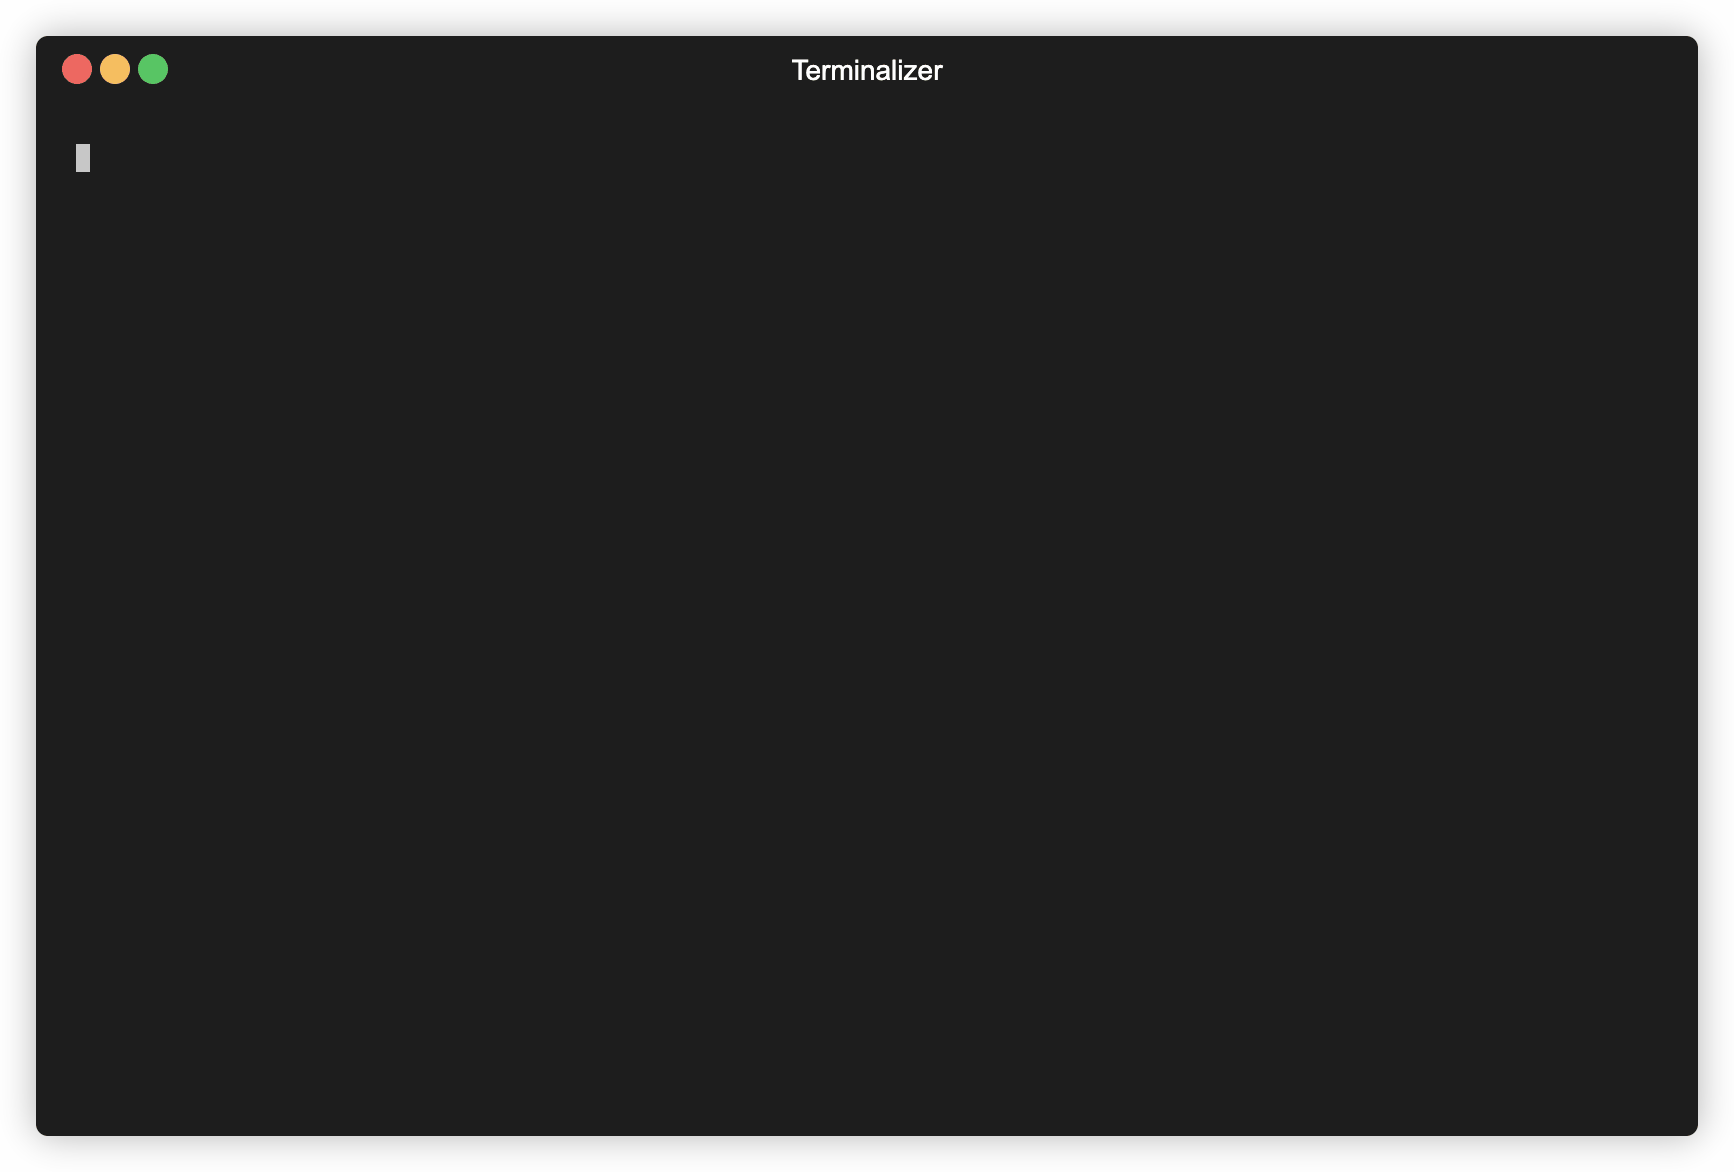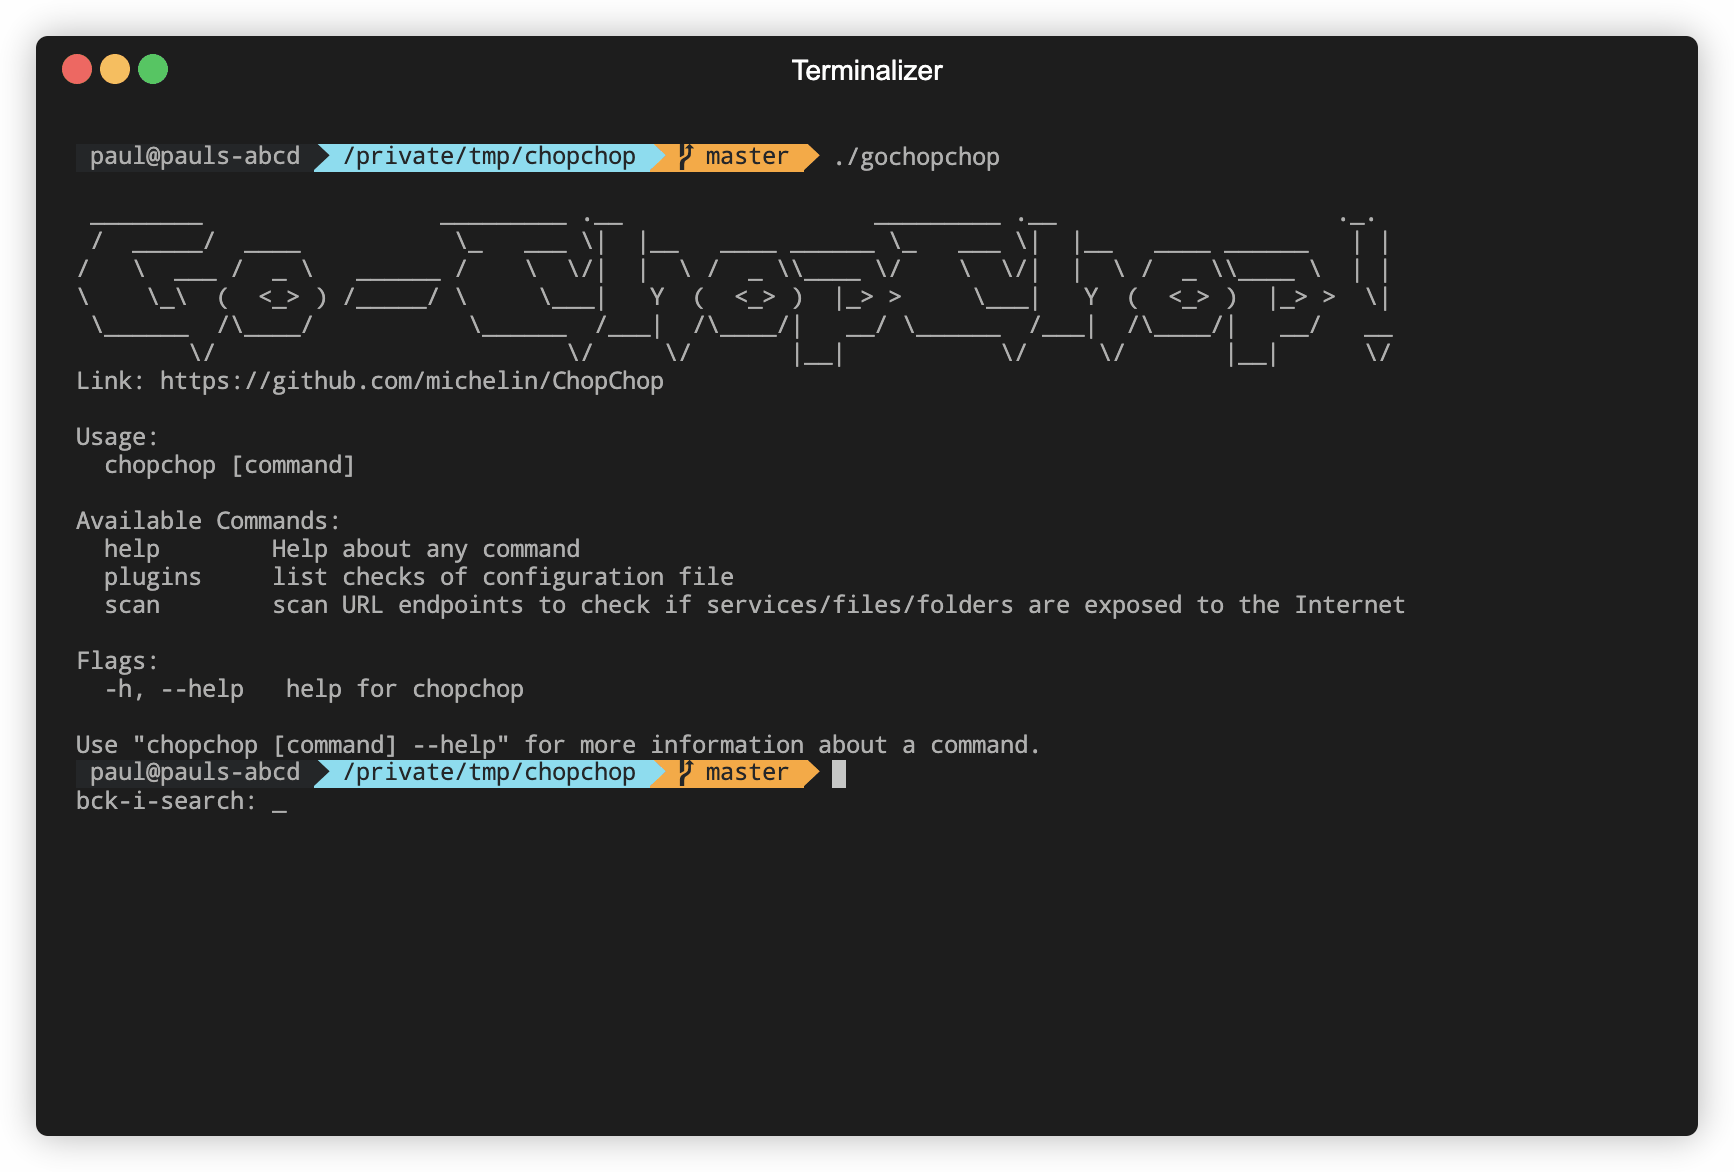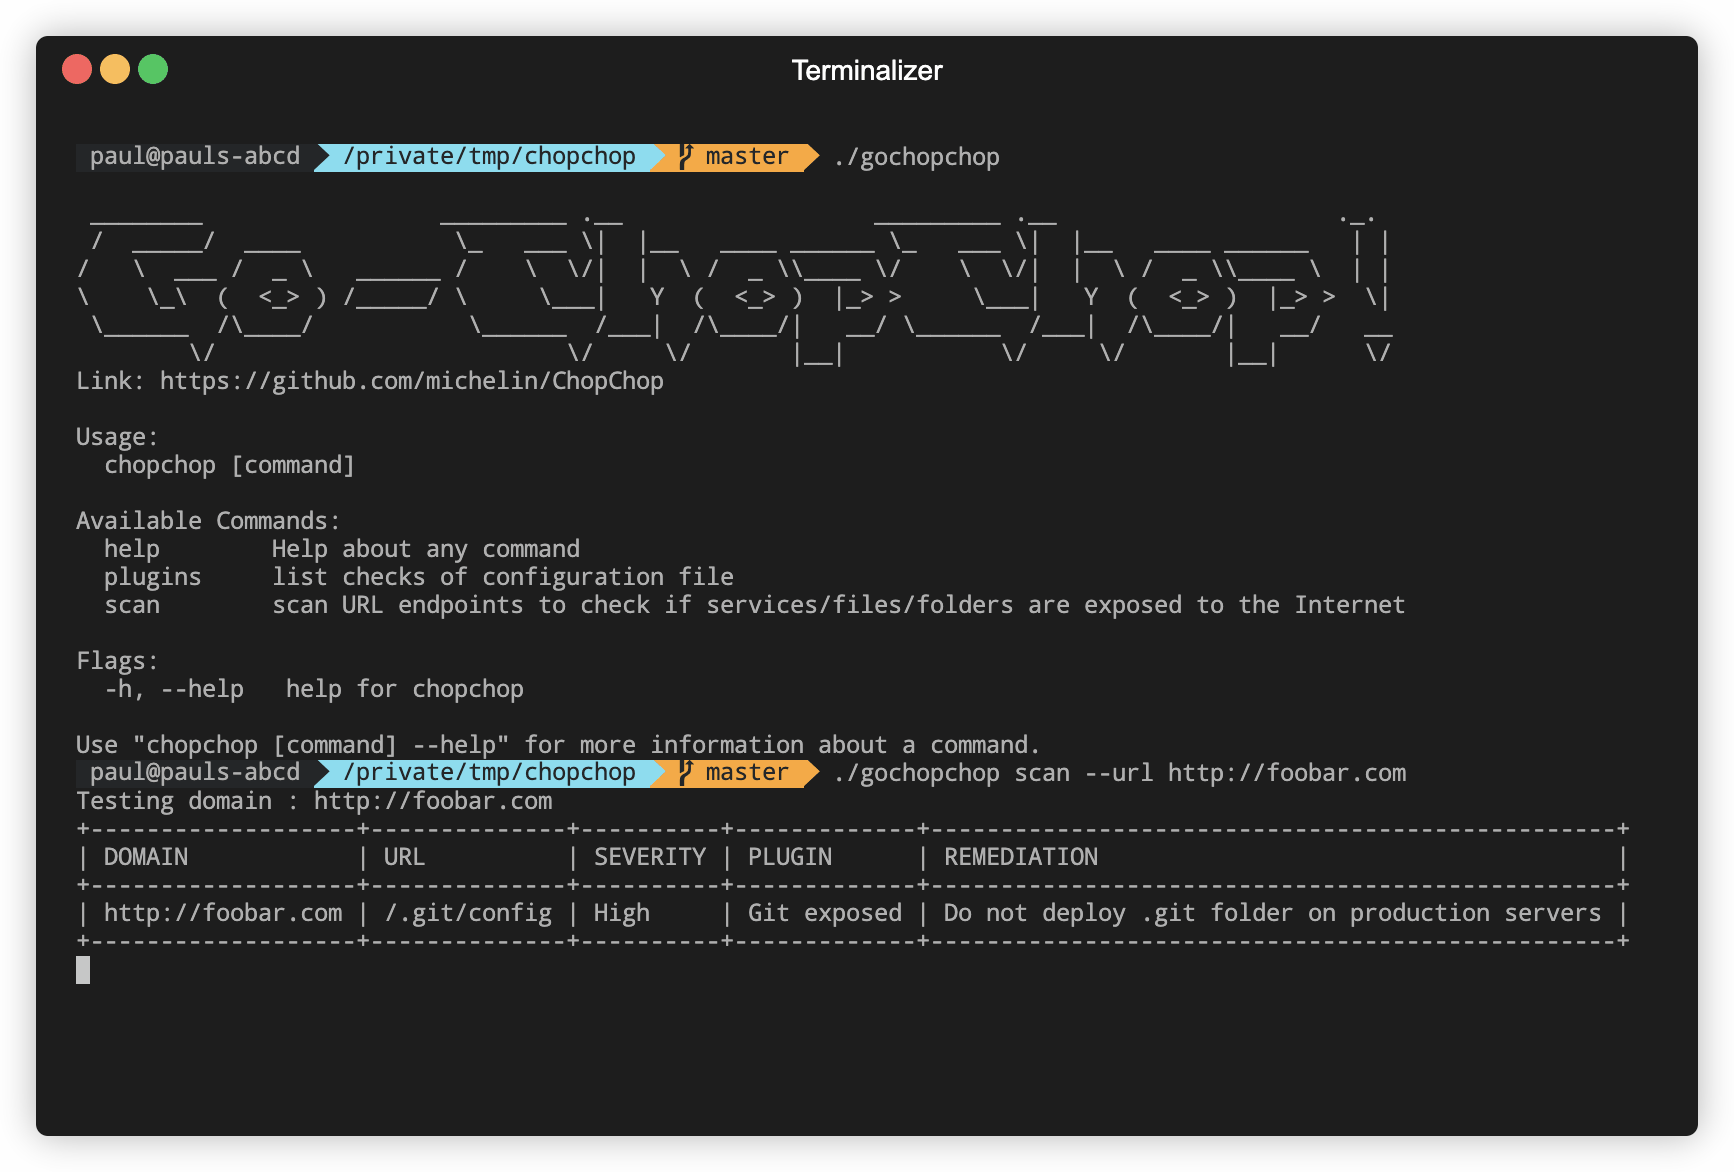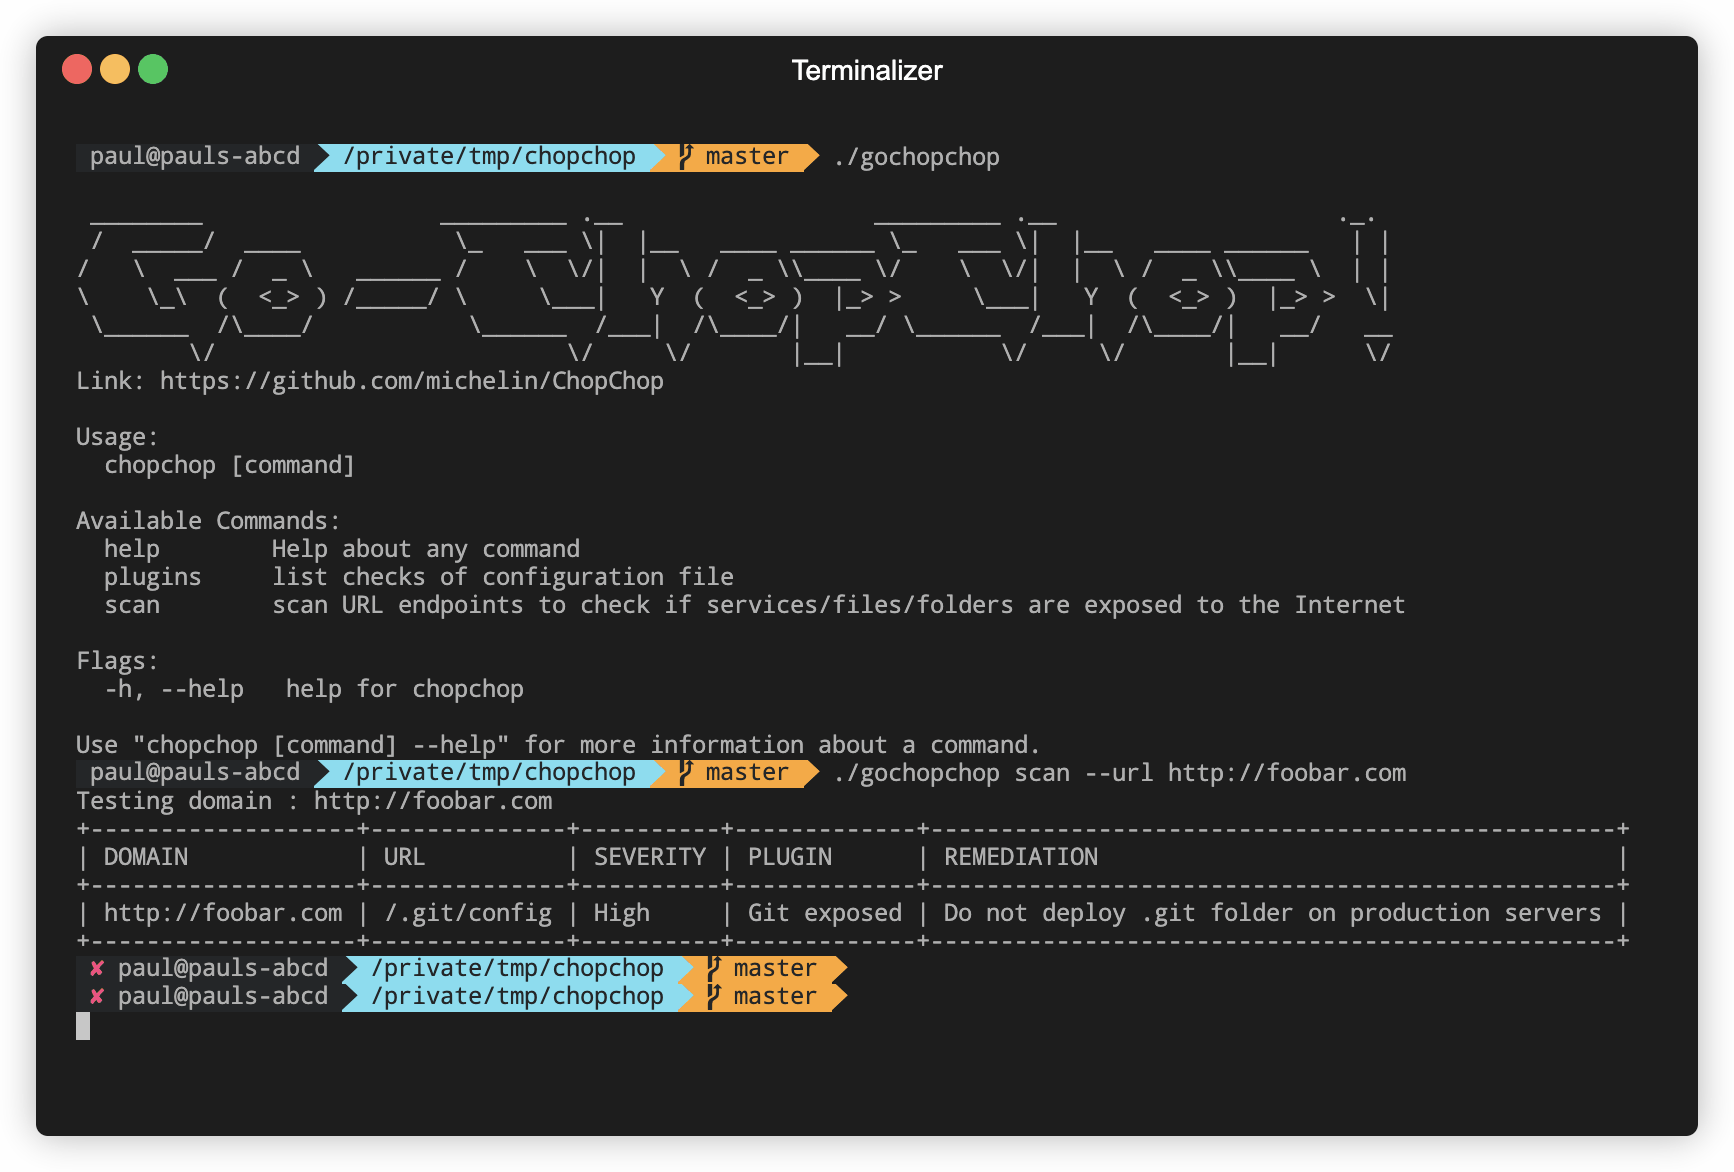 michelin/chopchop
YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…
 optiopay/klar
Integration of Clair and Docker Registry