#1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 nvidia/nemoclaw
Run agents like Hermes, LangChain Deep Agents, and OpenClaw more securely inside NVIDIA OpenShell with managed inference
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
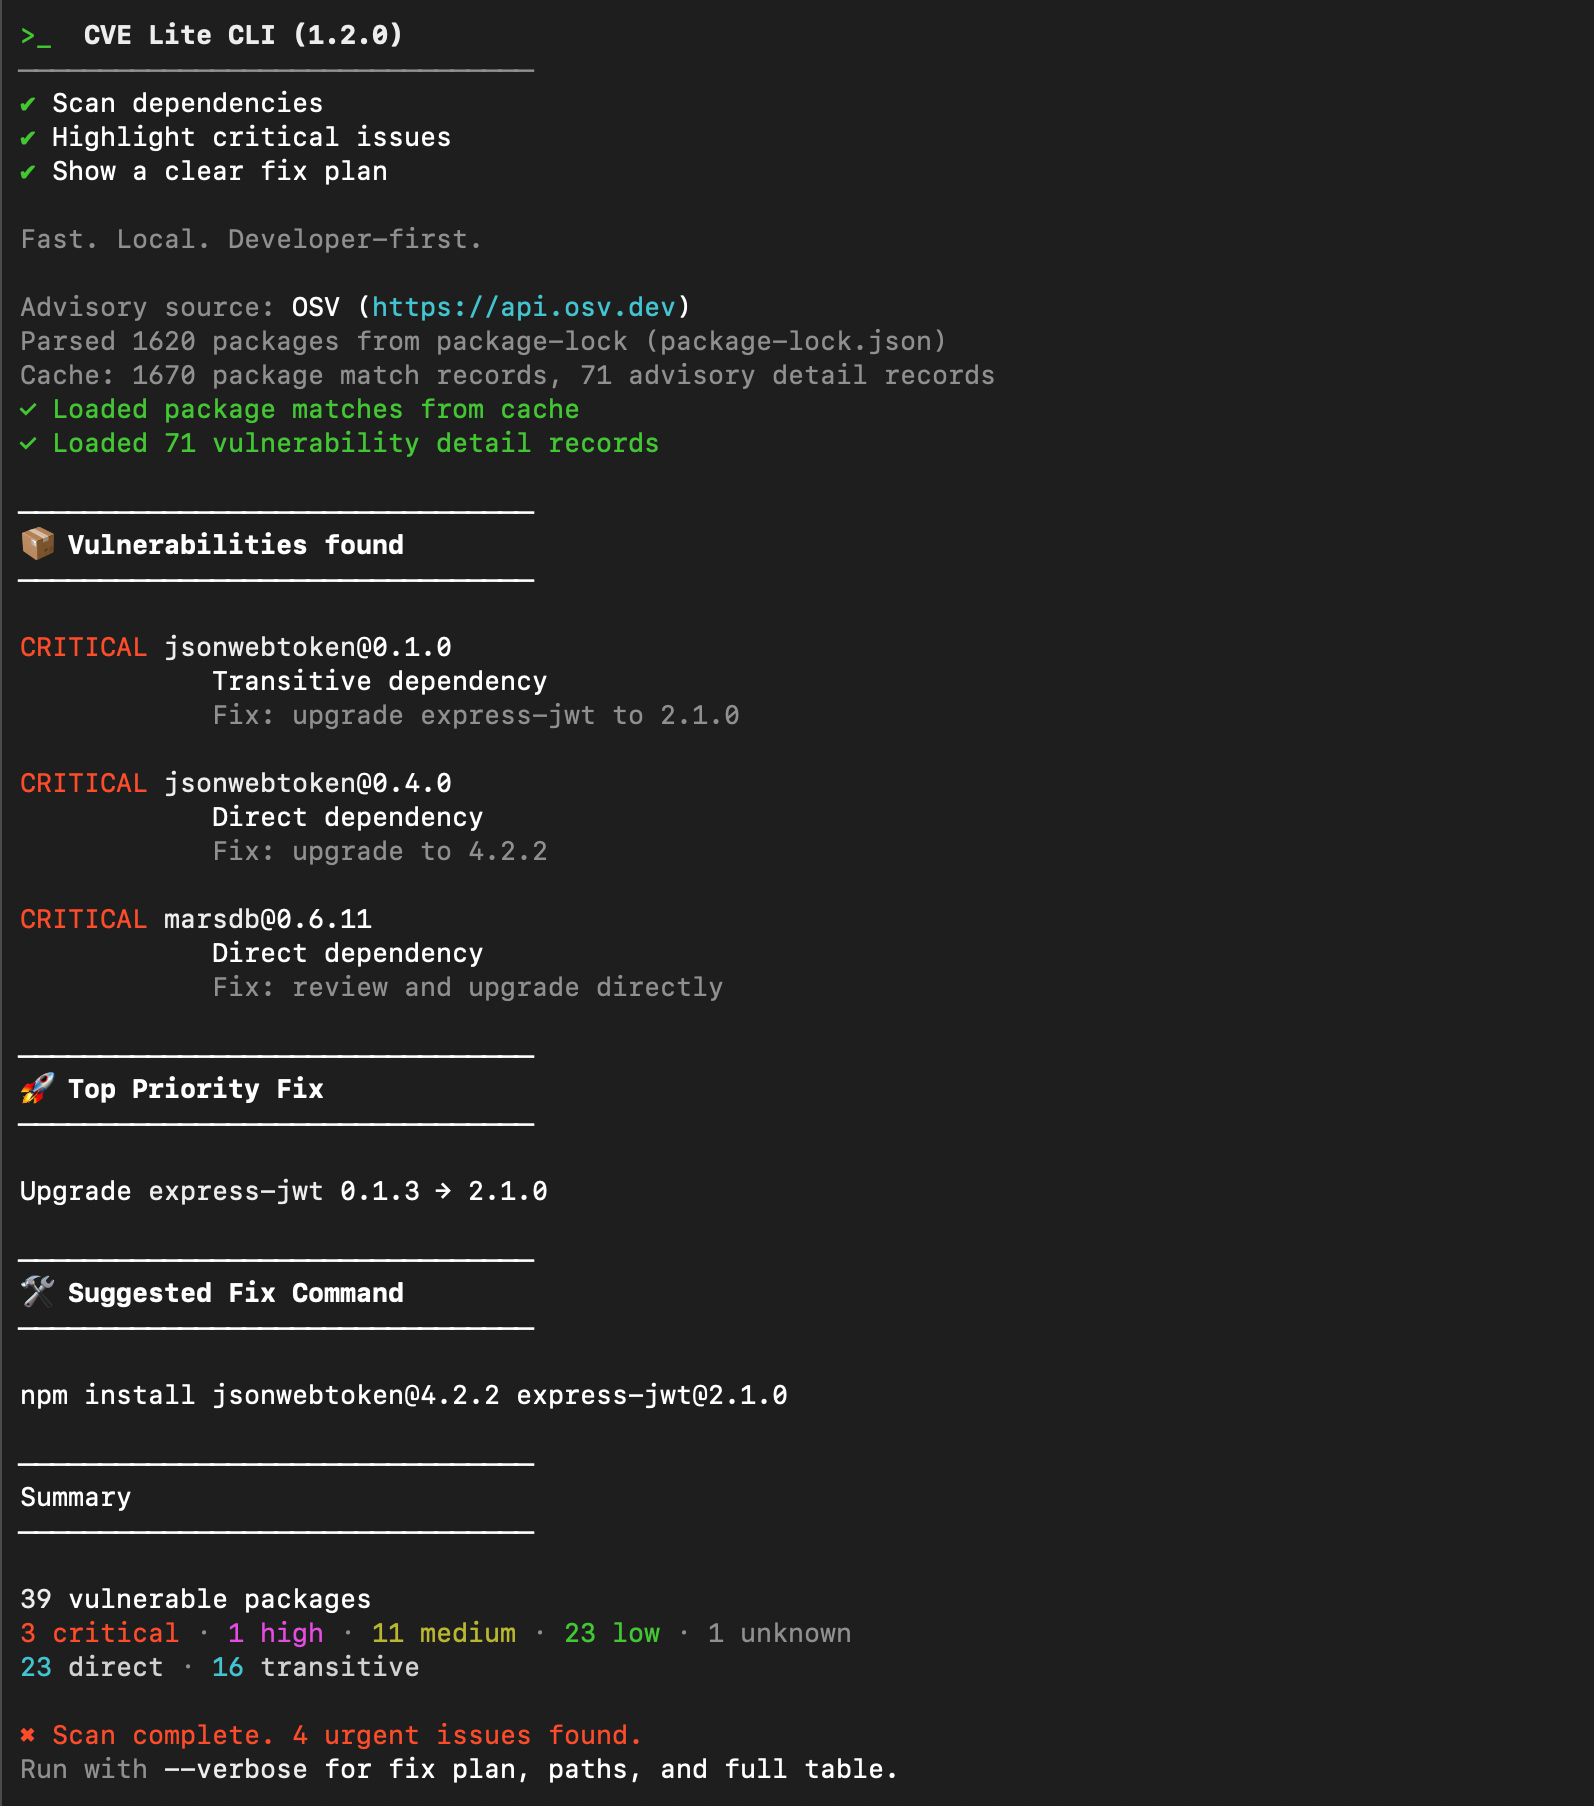 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 getsops/sops
Simple and flexible tool for managing secrets
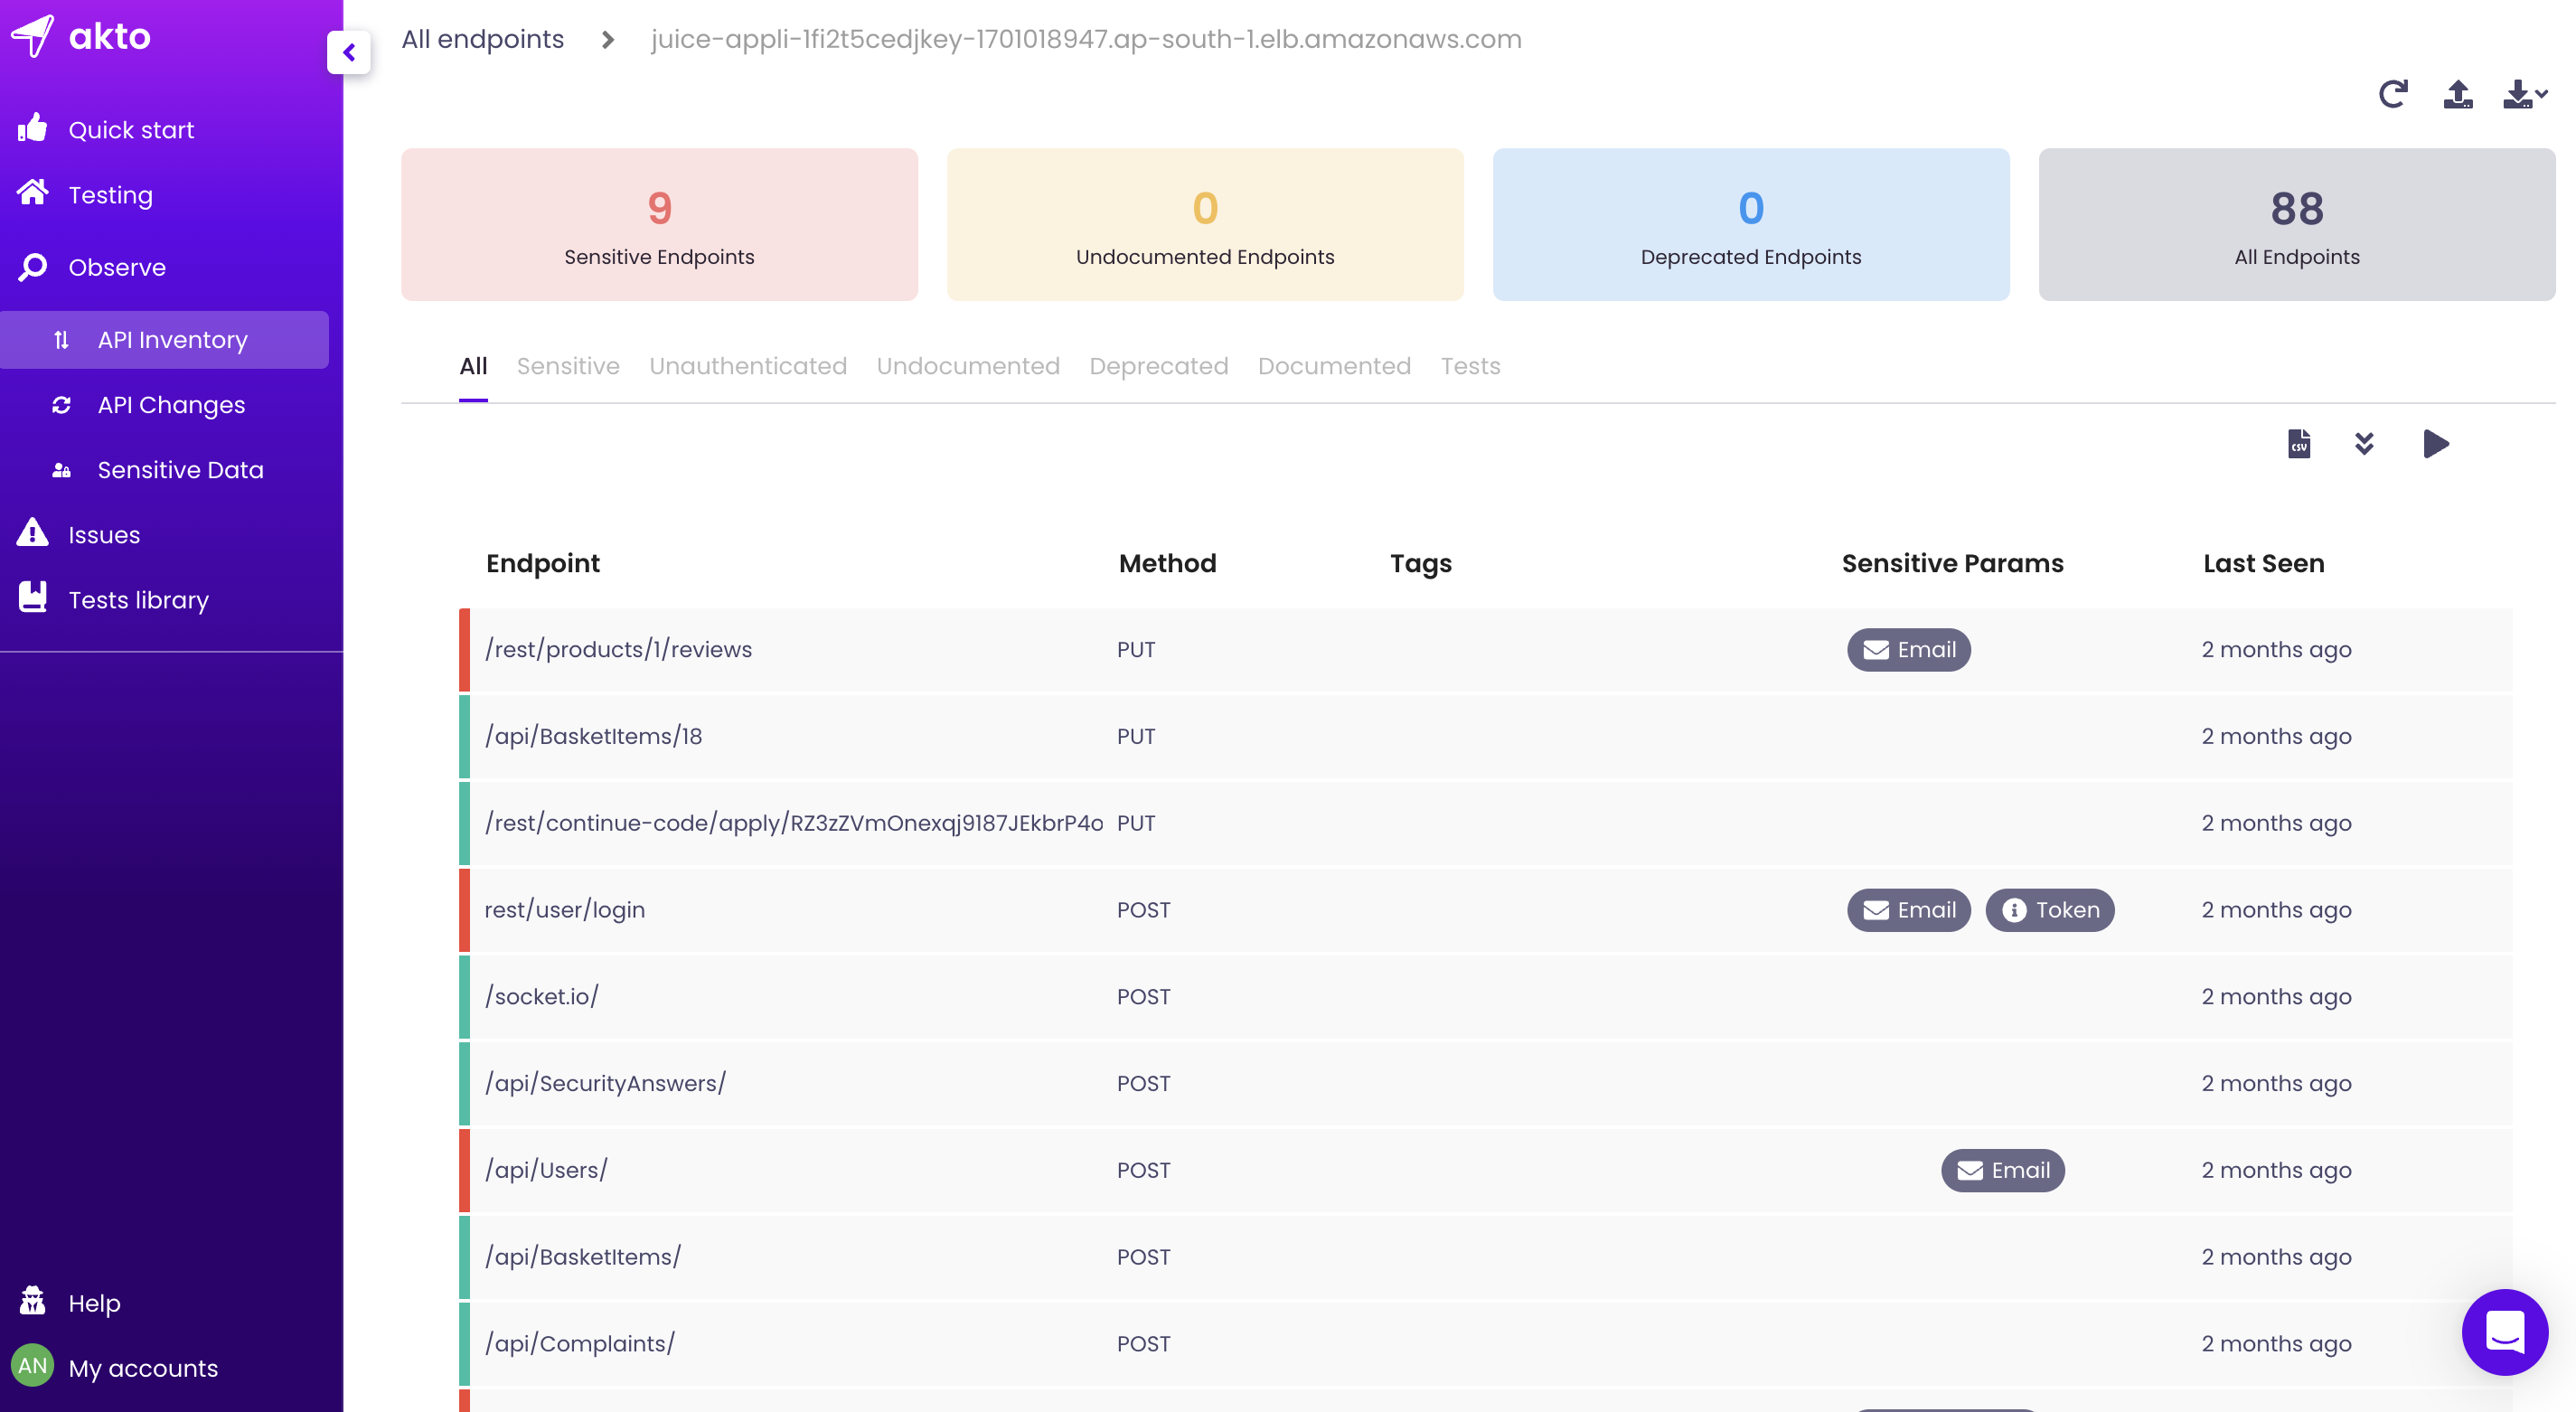 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 anomalyco/opencode
The open source coding agent.
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 microsoft/agent-governance-toolkit
Policy enforcement, zero-trust identity, execution sandboxing, and audit logging for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10 with…
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
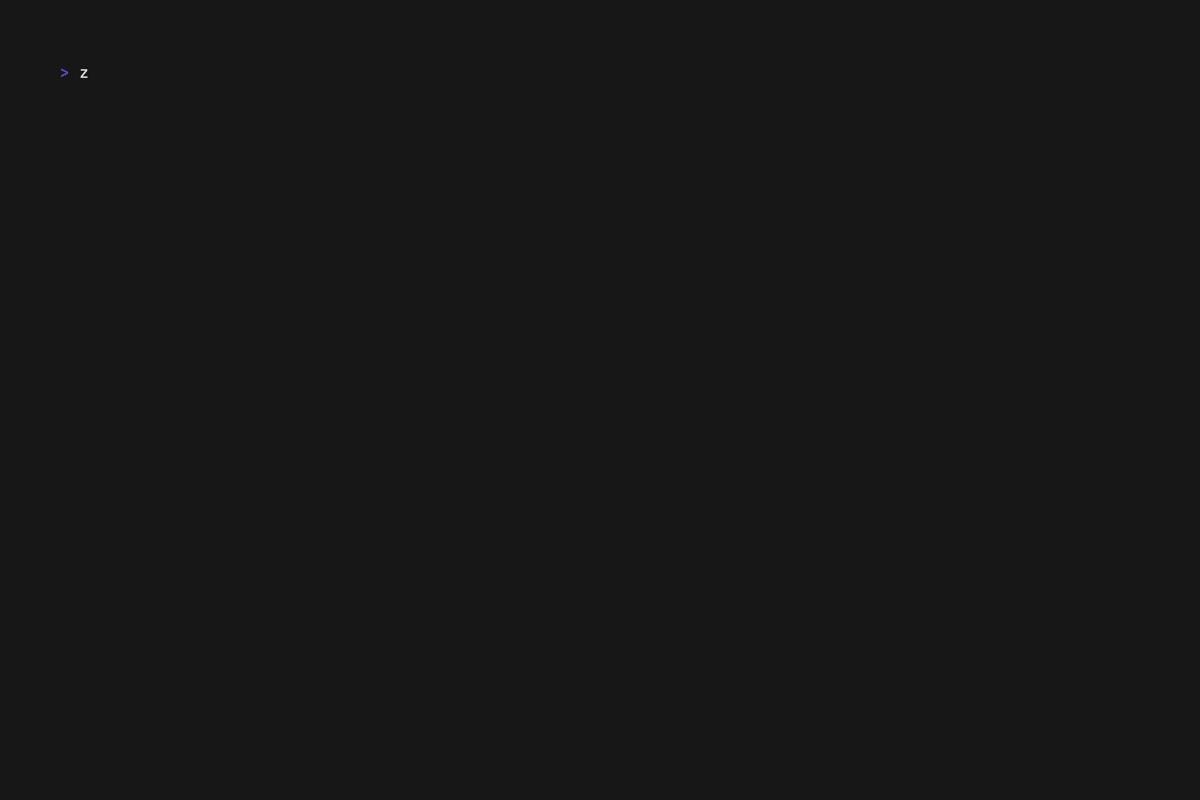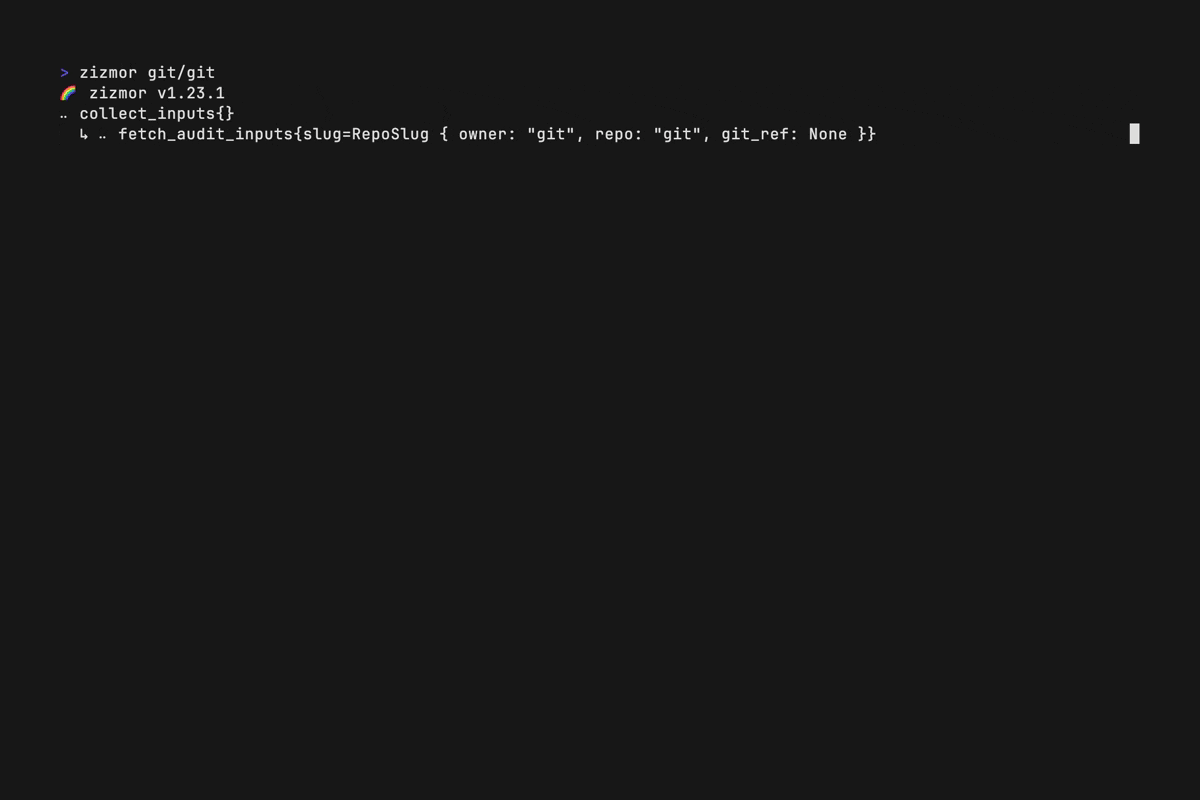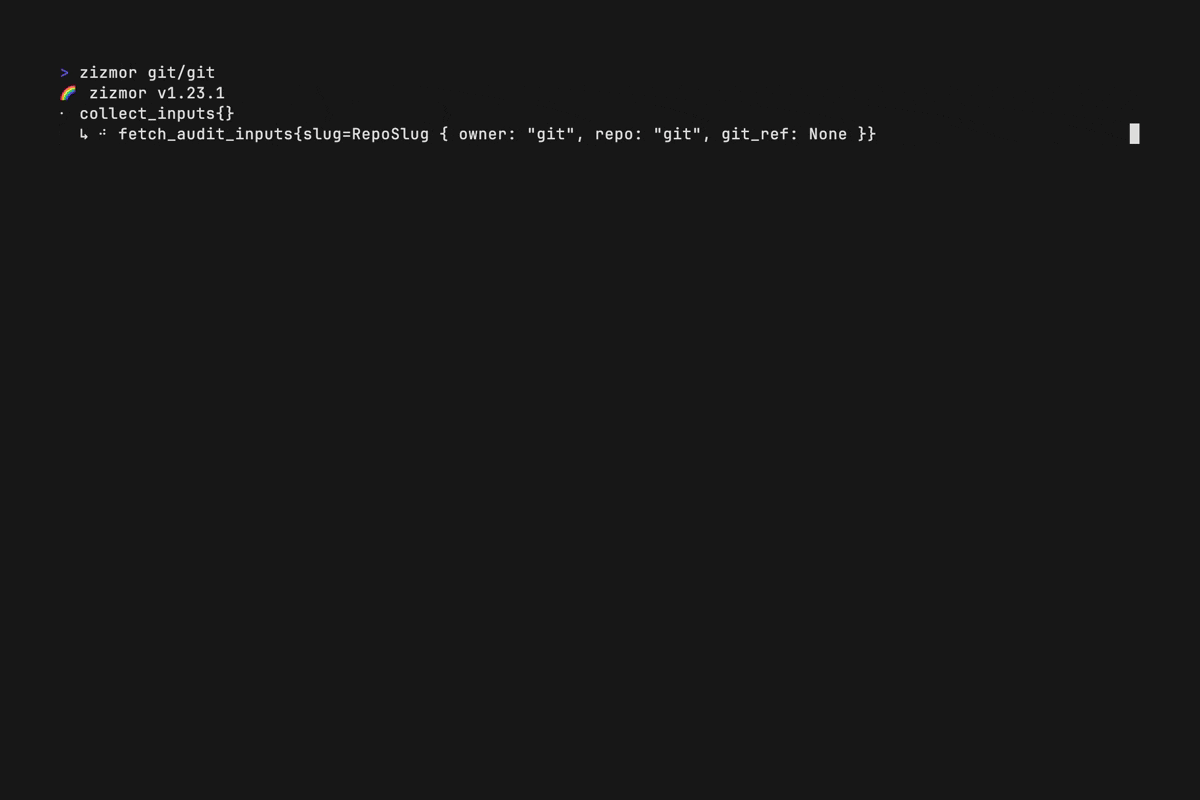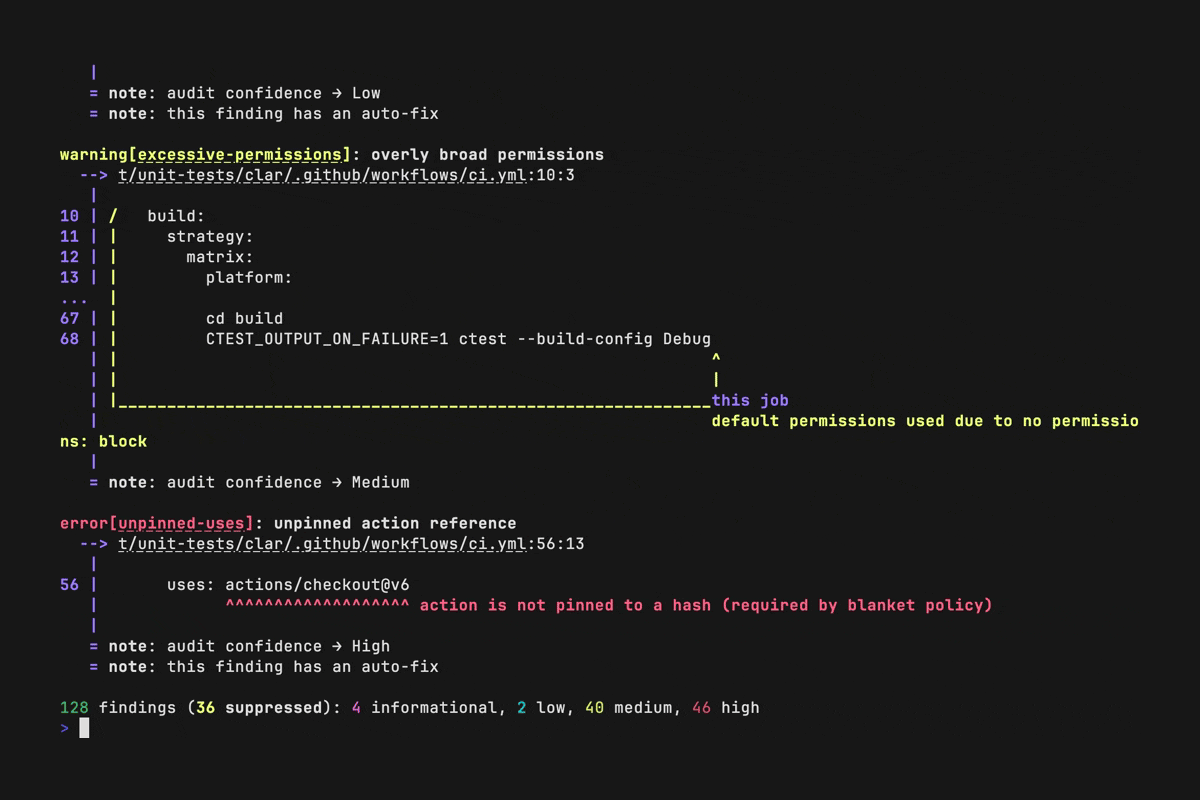 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…