
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 utkonos/lst2x64dbg
Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 hoangrealer/cve-2023-27216
Newbie's approach to firmware hacking
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 cheat-engine/cheat-engine
Cheat Engine. A development environment focused on modding
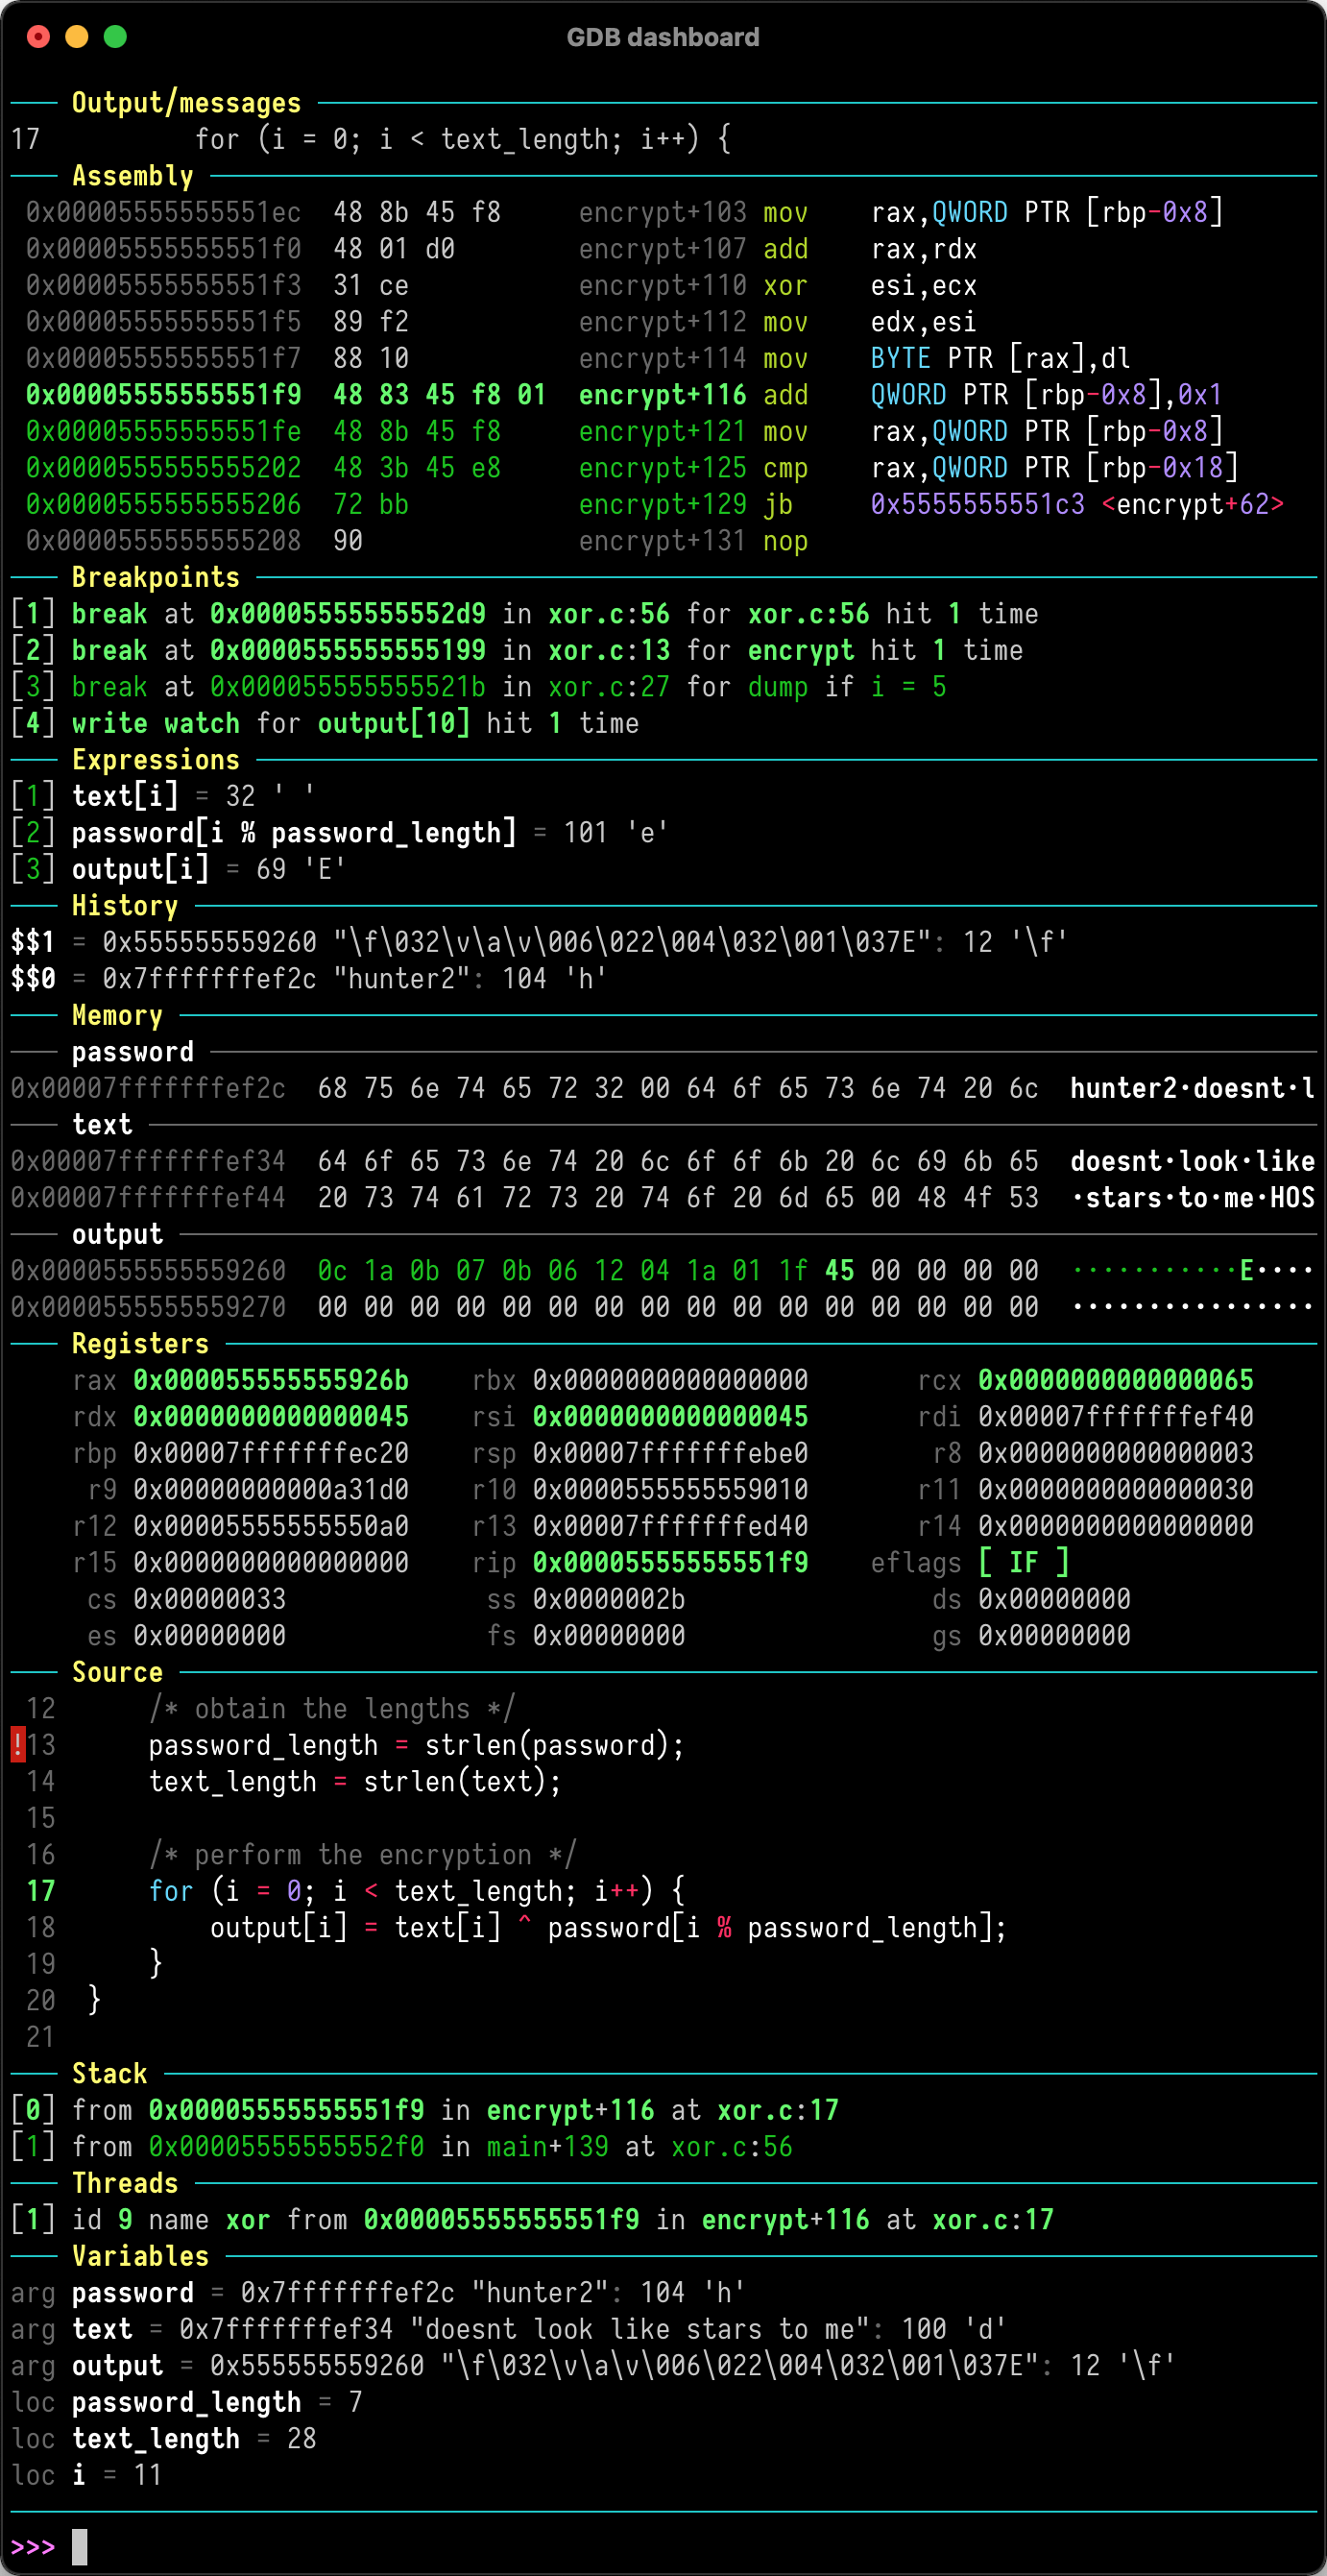 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 qustavo/httplab
Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.
 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 secrary/makin
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept
 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.
 felixber/findfunc
IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.








