
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
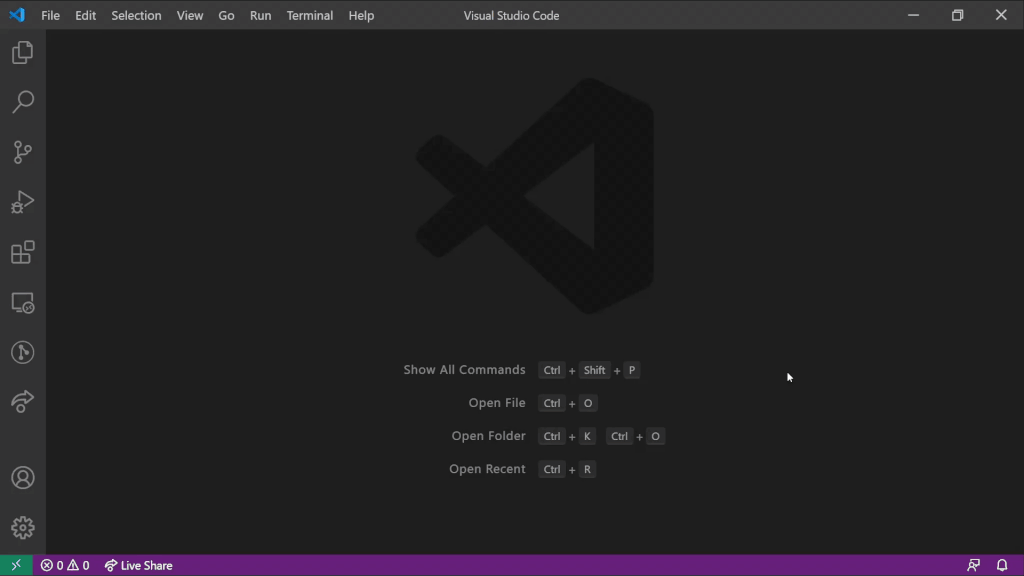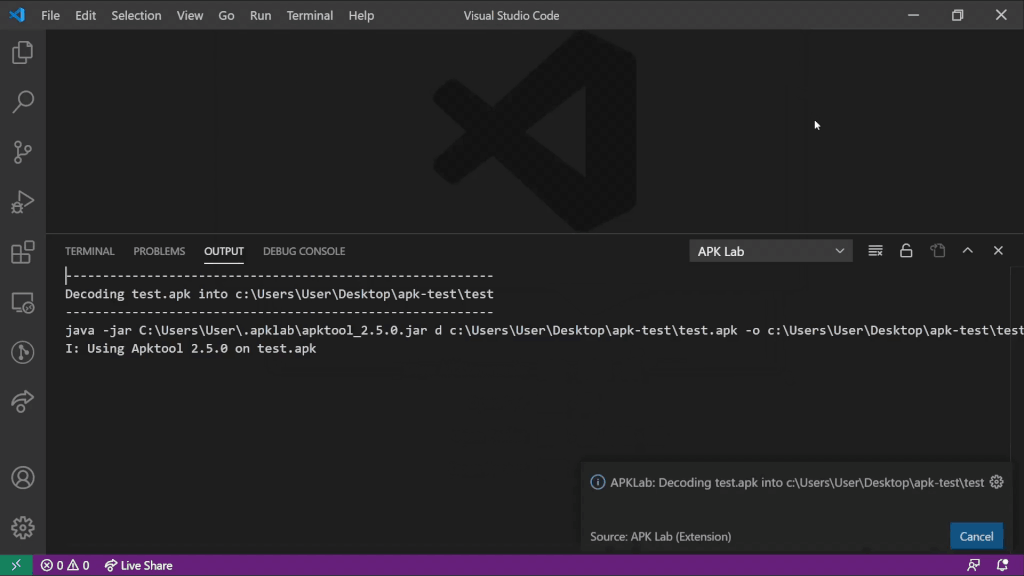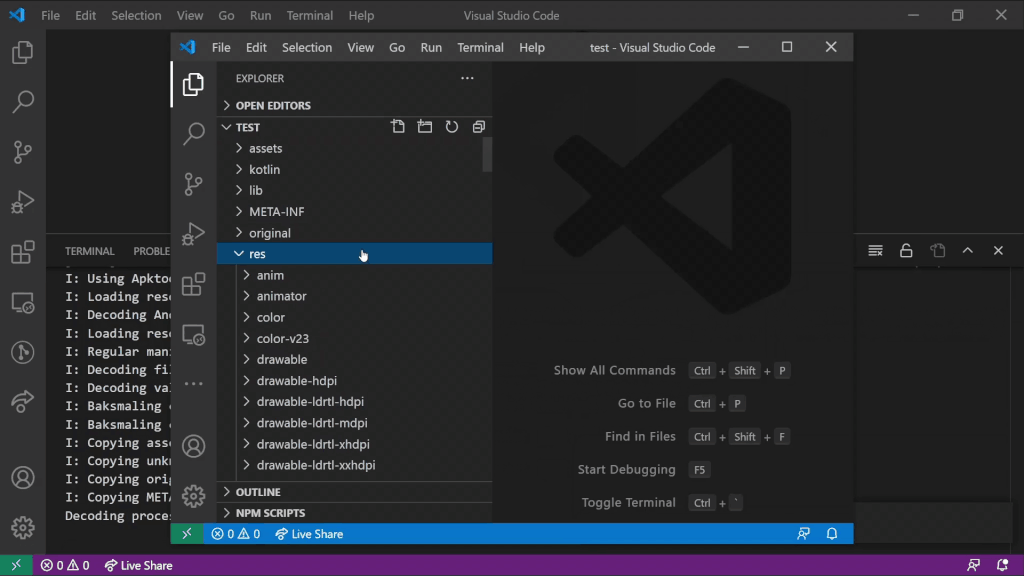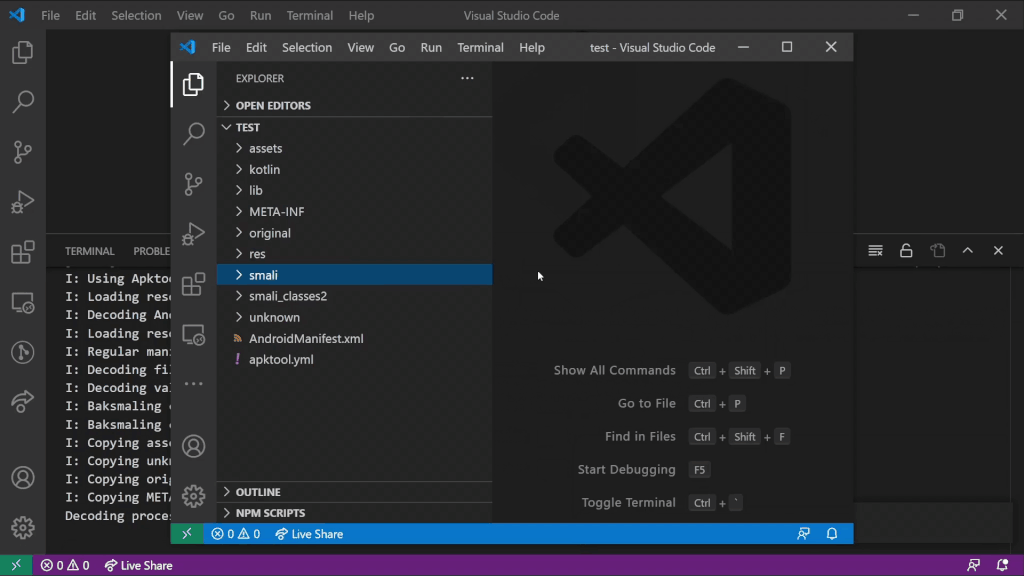 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
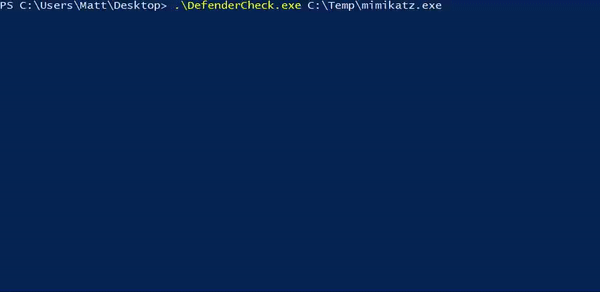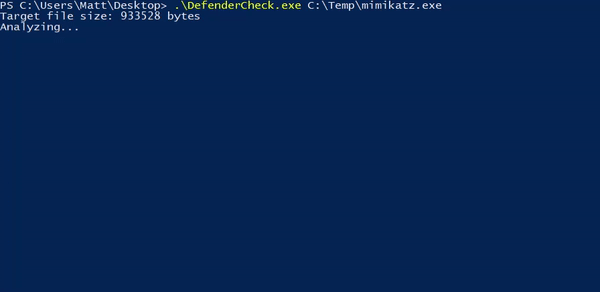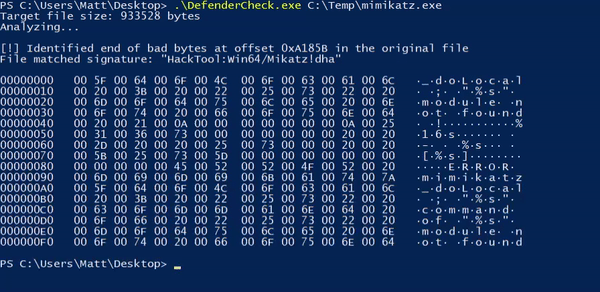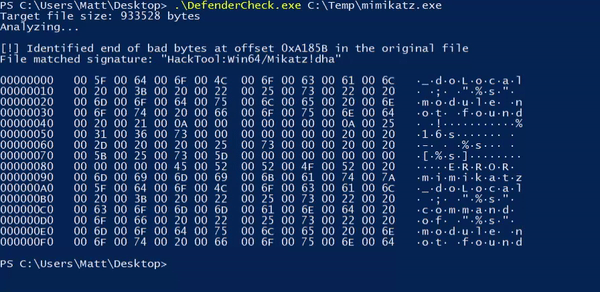 matterpreter/defendercheck
Identifies the bytes that Microsoft Defender flags on.
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
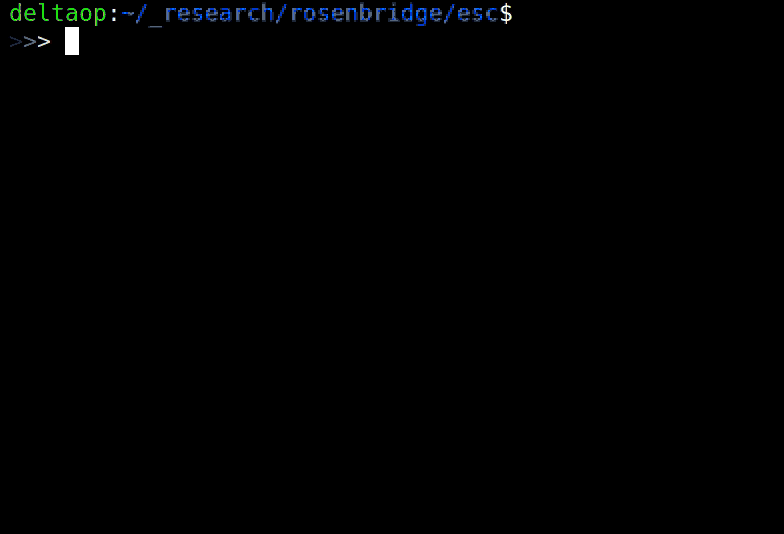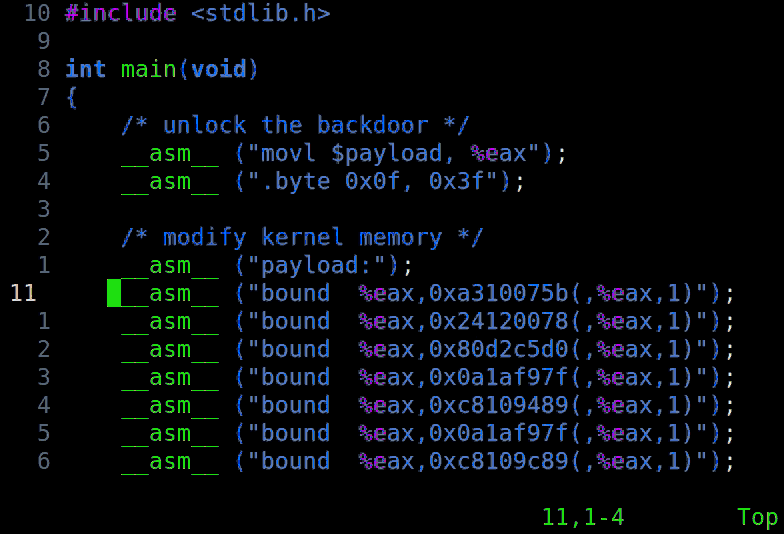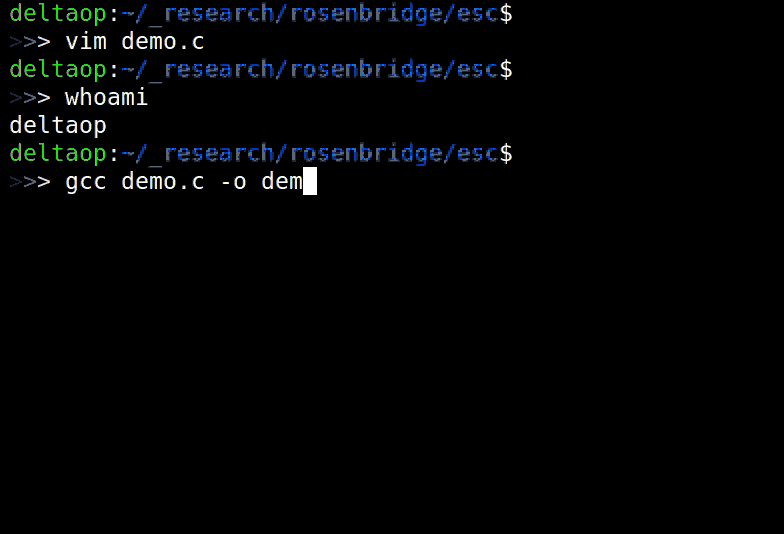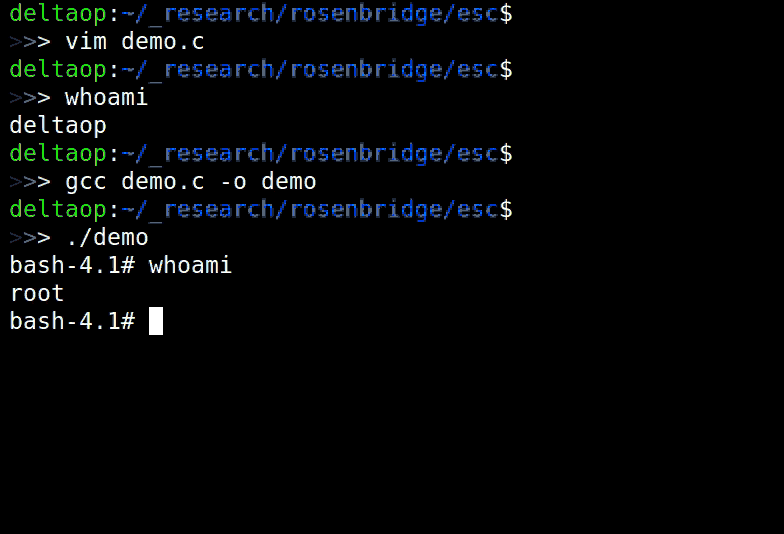 xoreaxeaxeax/rosenbridge
Hardware backdoors in x86 CPUs
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 ionescu007/simplevisor
Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…








