
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 phith0n/zkar
Go-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…
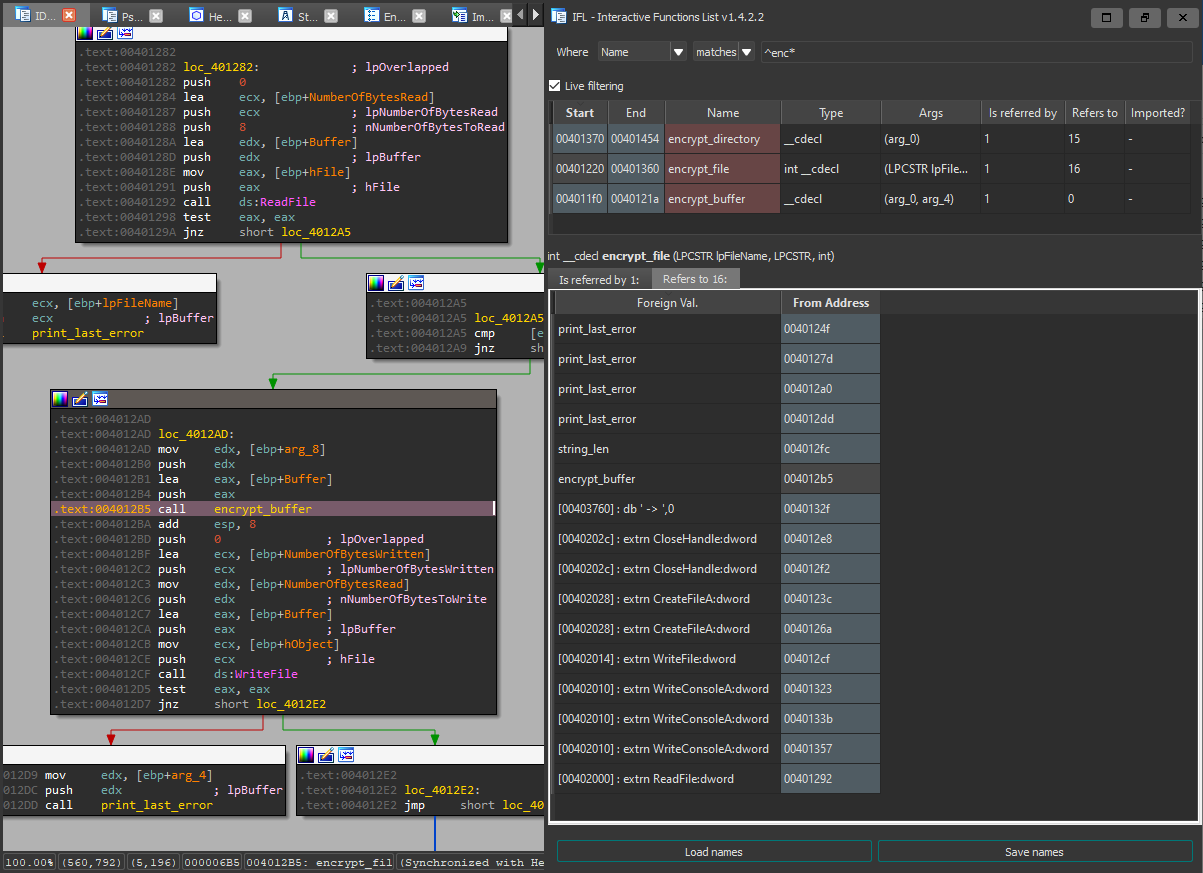 hasherezade/ida_ifl
IFL - Interactive Functions List (plugin for IDA Pro)
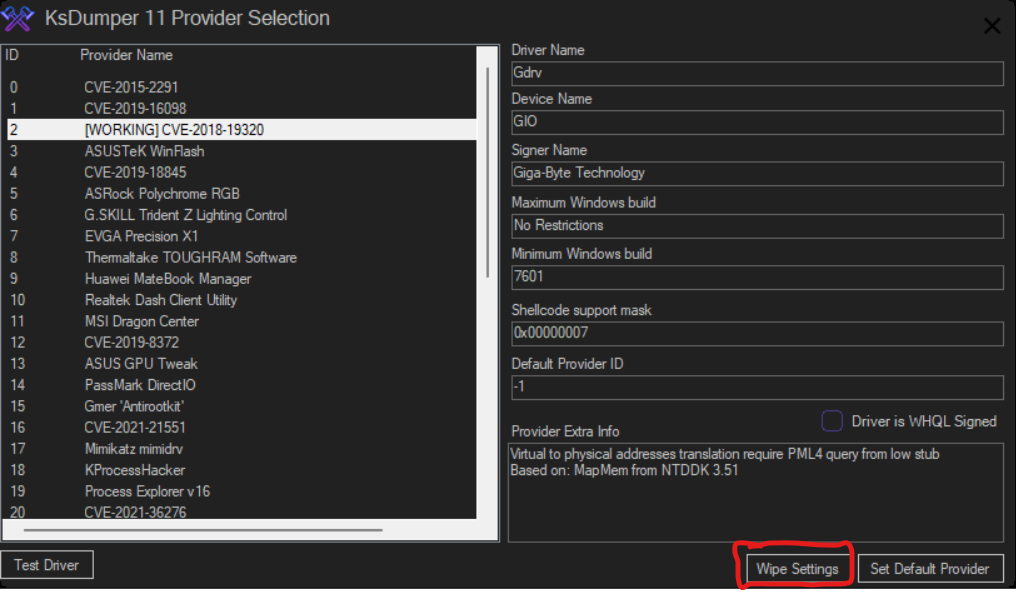 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
 instlatx64/instlatx64
Comprehensive database of x86/x64 instruction tables, latencies, and microarchitecture details for CPU performance analysis and low-level reverse…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 colton1skees/dna
LLVM based static binary analysis framework
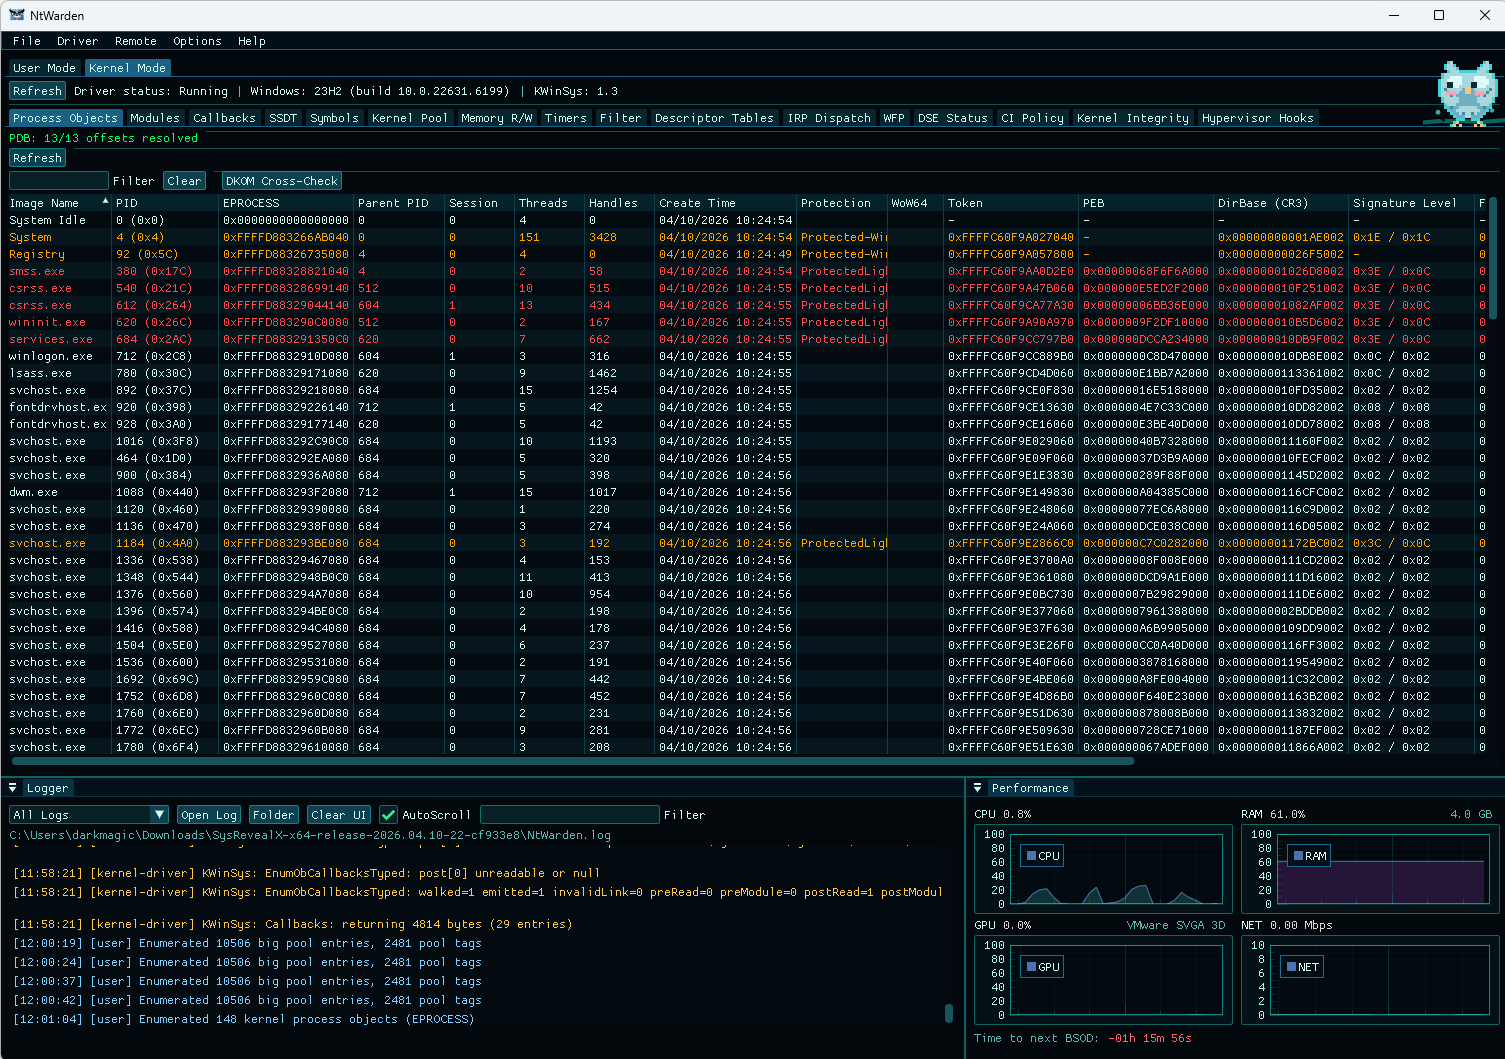 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
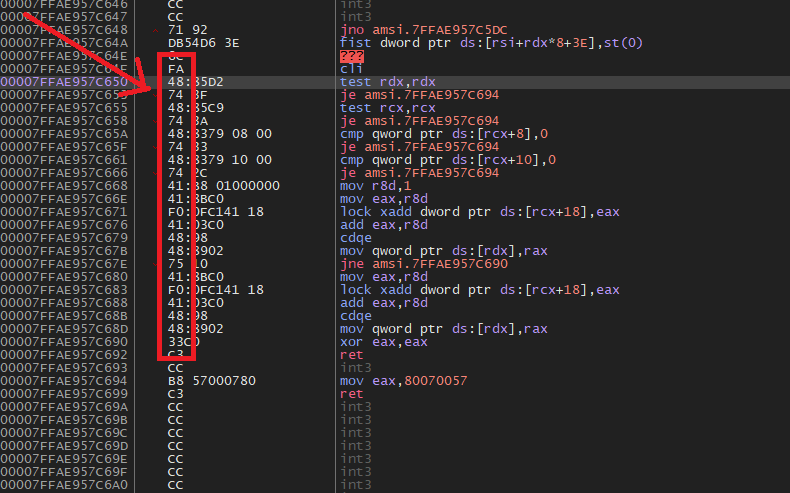 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 bazad/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
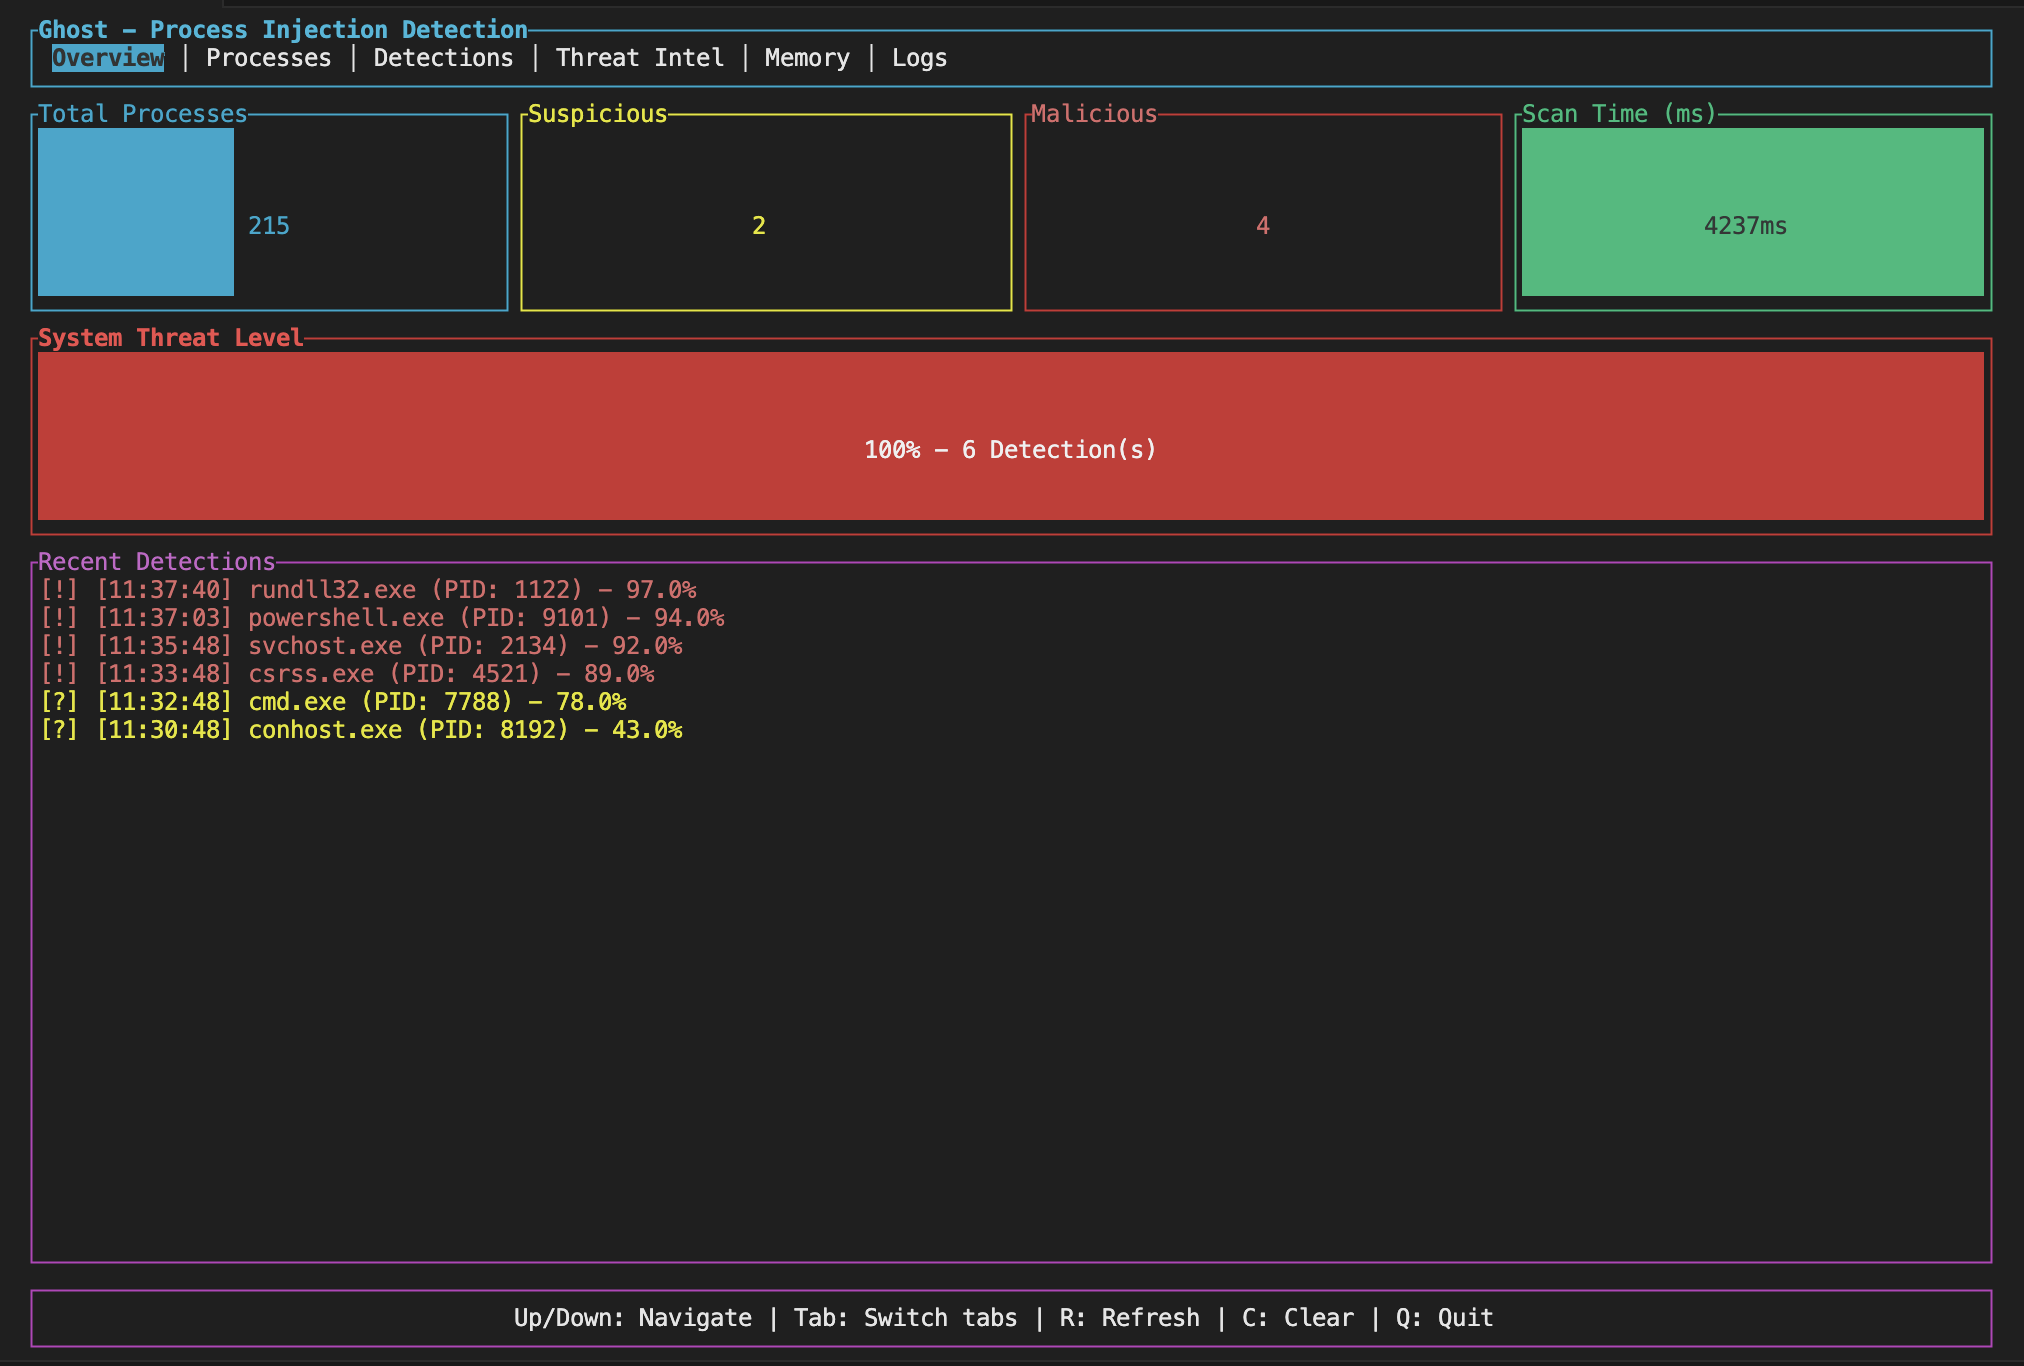 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
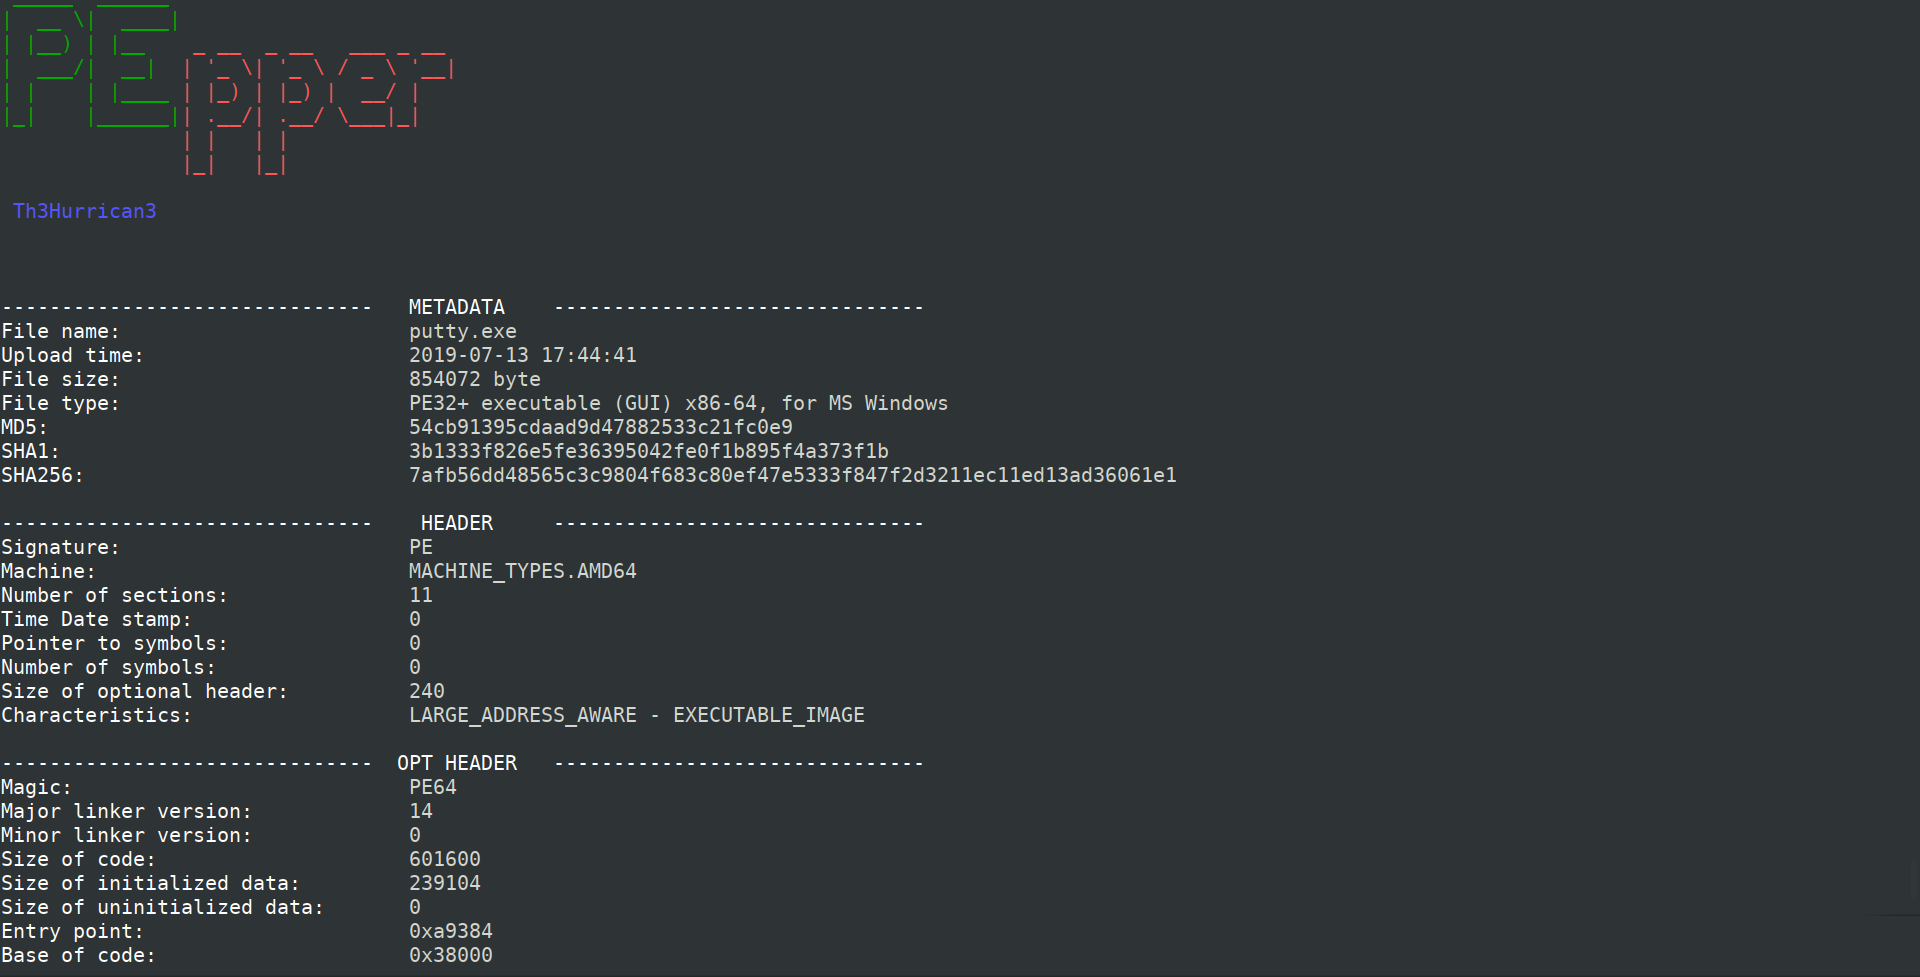 0x0be/pepper
An open source script to perform malware static analysis on Portable Executable
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 hugsy/gdb-static
Public repository of statically compiled GDB and GDBServer
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering








