Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
PEpper — An open source script to perform malware static analysis on Portable Executable | Kitploit
Tools/GitHubGitHub/0x0be/pepper
Static AnalysisForensicsMalware AnalysisBinary Analysis
GitHub0x0be/pepper

PEpper

An open source script to perform malware static analysis on Portable Executable

View Repository
33373354 years agoReviewed by Kitploit
Share

PEpper logo

PEpper

An open source tool to perform malware static analysis on Portable Executable

Installation

eva@paradise:~$ git clone https://github.com/blackeko/PEpper/
eva@paradise:~$ cd PEpper
eva@paradise:~$ pip3 install -r requirements.txt
eva@paradise:~$ python3 pepper.py ./malware_dir

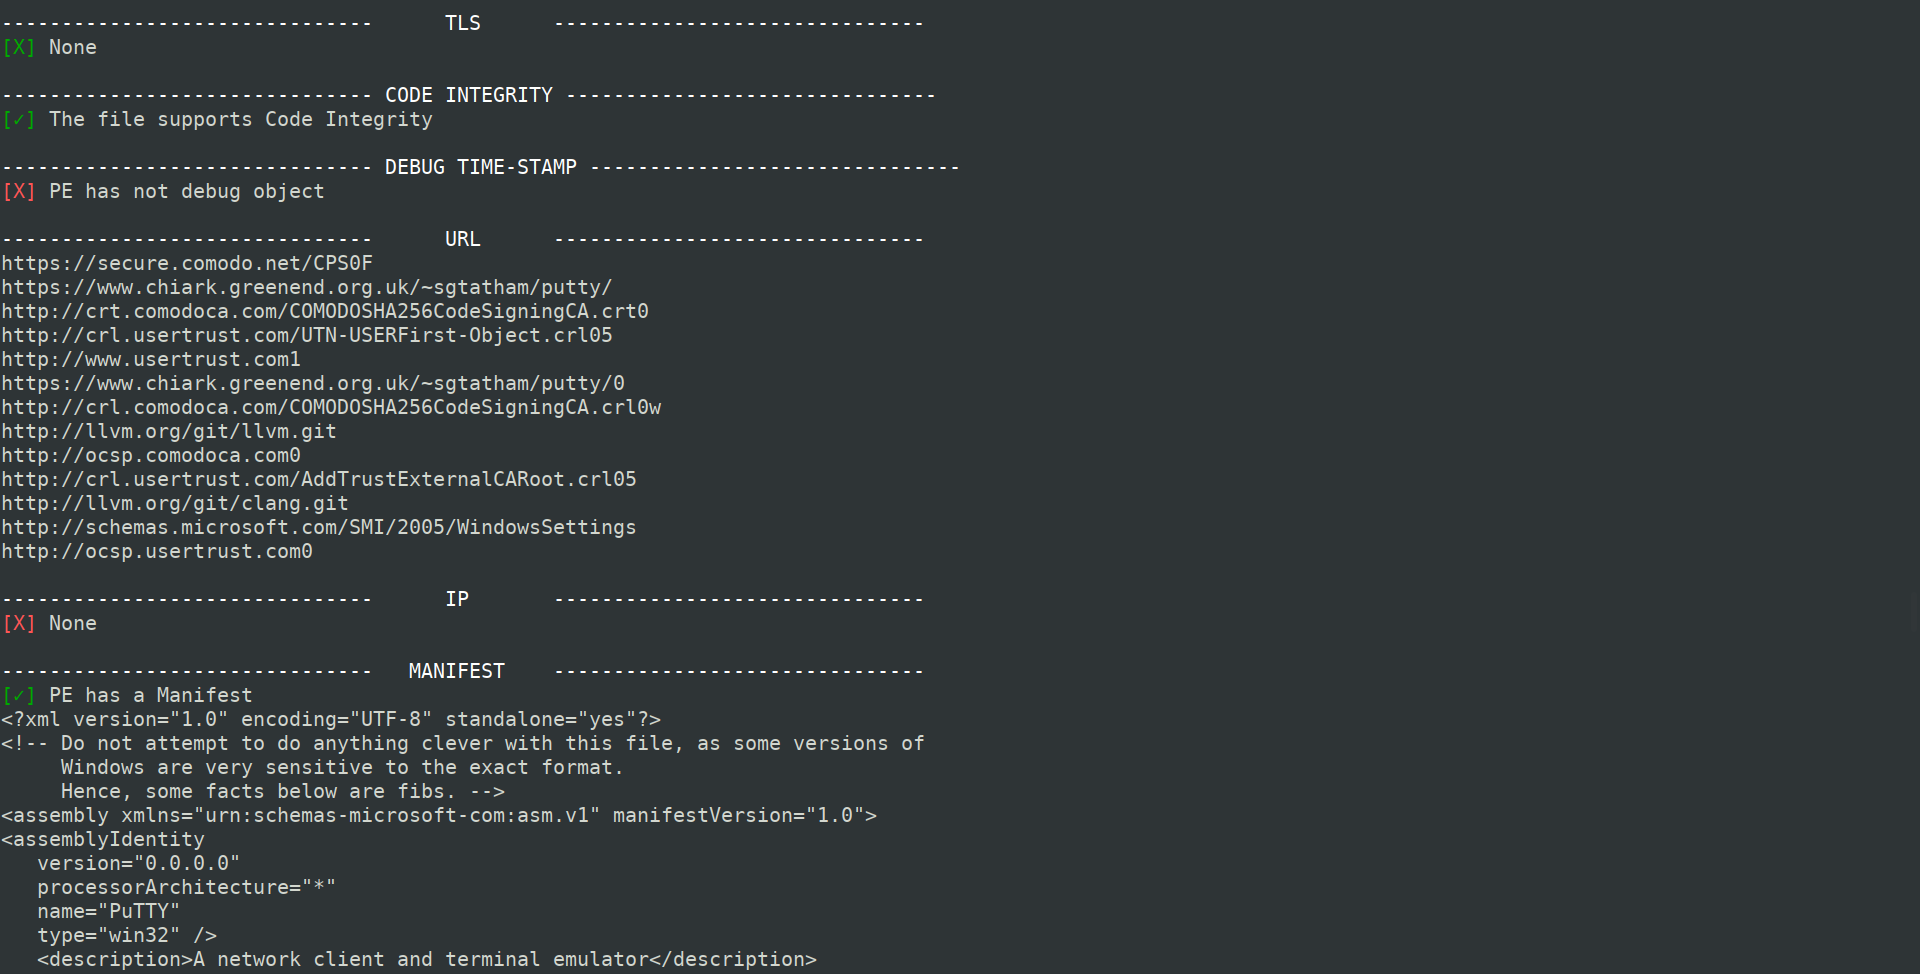
Screenshot

and more rows..

CSV output

outcome

and more columns..

Feature extracted

  • Suspicious entropy ratio
  • Suspicious name ratio
  • Suspicious code size
  • Suspicious debugging time-stamp
  • Number of export
  • Number of anti-debugging calls
  • Number of virtual-machine detection calls
  • Number of suspicious API calls
  • Number of suspicious strings
  • Number of YARA rules matches
  • Number of URL found
  • Number of IP found
  • Cookie on the stack (GS) support
  • Control Flow Guard (CFG) support
  • Data Execution Prevention (DEP) support
  • Address Space Layout Randomization (ASLR) support
  • Structured Exception Handling (SEH) support
  • Thread Local Storage (TLS) support
  • Presence of manifest
  • Presence of version
  • Presence of digital certificate
  • Packer detection
  • VirusTotal database detection
  • Import hash

Notes

  • Can be run on single or multiple PE (placed inside a directory)
  • Output will be saved (in the same directory of pepper.py) as FILENAME-output.csv
  • To use VirusTotal scan, add your private key in the module called "virustotal.py" (Internet connection required)
  • Software License

Credits

Many thanks to those who indirectly helped me in this work, specially:

  • The LIEF project and its awesome library
  • PEstudio, a really amazing software to analyze PE
  • PEframe from guelfoweb, an incredible widespread tool to perform static analysis on Portable Executable malware and malicious MS Office documents
  • Yara-Rules project, which provides compiled signatures, classified and kept as up to date as possible

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →