
 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit recommended

 tencent-hunyuan/diagsafe
Diagnostic LLM safety benchmark with 3,489 bilingual prompts, an 84-label taxonomy, and prompt-level rubric judging for explainable, fine-grained…
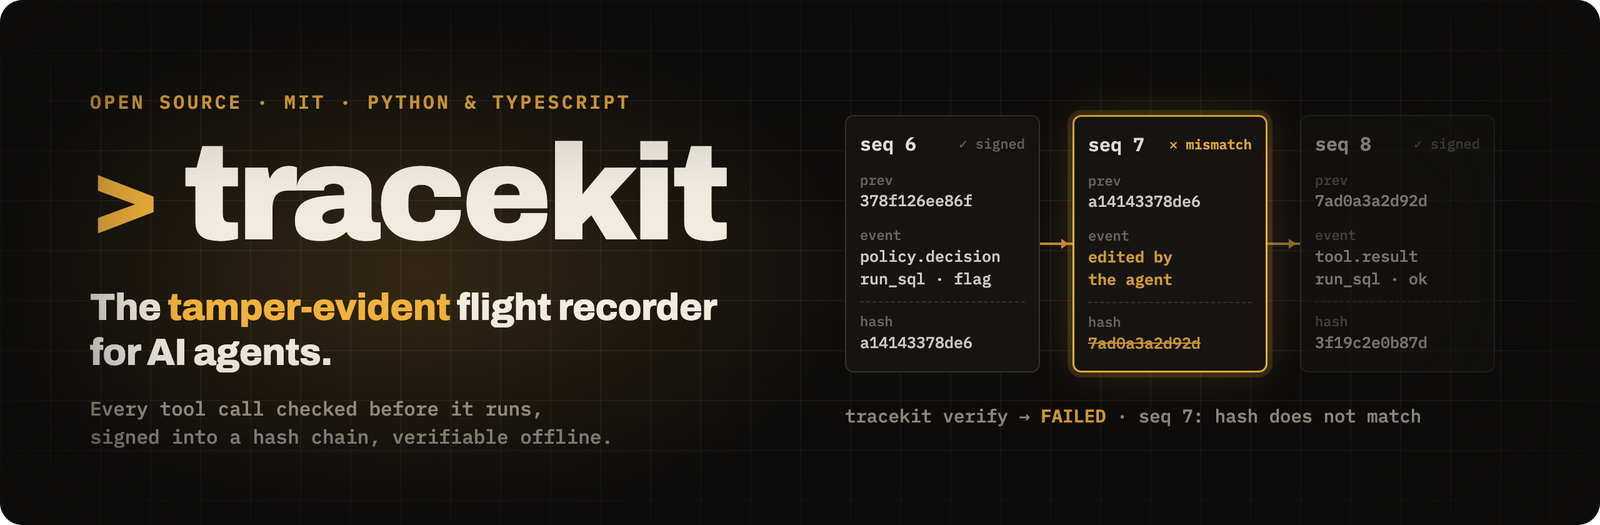 cygnux-labs/tracekit
Tamper-evident tracing, policy gates and cross-checks for AI agents: see what the agent did, and why.
 pixee/compaction-laundering
Security research on context compaction in coding agents: shows how forged role labels in untrusted content survive summarization and get executed,…
 genai-security-project/genai-llm-top10
OWASP Top 10 for Large Language Model Applications
 gmh5225/nova-framework
YARA-inspired prompt pattern matching engine that combines keyword, regex, semantic similarity, and LLM evaluation rules to detect jailbreaks and…

 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…
 hanxi19/black_hole_attack_for_vector_database
Research implementation of the Black-Hole Attack that poisons vector database indexes via centrality-driven hubness, with FAISS pipelines and…
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 peach-research-lab/authorizationbench
[🎖️ Honorable Mention in HAIPS @COLM'26] The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization…
 owasp/ai-threat-modeler
OWASP project for AI-assisted threat modeling, helping teams identify, analyze, and document security threats and mitigations in system designs.
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 tridents10/vader-pro-vdr
AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…
 infobyte/ai-pentest-agent
Standalone autonomous AI pentest agent with a plan→act→judge loop, generic skills, destructive-action gate, and swappable LLM providers, plus a…
 happytotoro116/ghidra-llm-pipeline
Deterministic PyGhidra extraction, triage, and local LLM compiler-backend pipeline for C reimplementation.
 fazmin/cve-intel
Local CVE triage engine aggregating 25 sources (NVD, EPSS, CISA KEV, OSV, Shodan) into 0-100 risk scores, with CLI, REST API, MCP server and…
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…








