 cygnux-labs/tracekit
Tamper-evident tracing, policy gates and cross-checks for AI agents: see what the agent did, and why.

Tracekit checks each tool call your agent makes before it runs, and risky calls wait for a person to approve them. Every action is signed into a tamper-evident log by a process the agent can't touch, so you can put agents on real systems and show what they did: your customers and auditors can verify the record themselves, offline.



8 of 8tamper attacks caught480 trials, with a witness (E1) |
956 of 956harmful calls stopped11 classes, 1 false alarm in 972 (E17) |
< 1 msadded per tool call0.91 ms at p99, signer round trip (E9) |
8 of 8insider attacks caughta merge gate on every PR (E8) |
Built like Certificate Transparency: signed records in an append-only log that independent witnesses cosign
Open file format · verifiers in Python, TypeScript and Go · MIT · runs on your own machines
Try it · Add it to your agent · What it proves · What's in it · Proof · How it works · Pilot it · Contribute · Docs
Agents now run shell commands, edit code, query databases, send email and move money. Sooner or later one of them does something nobody expected, and three questions land on your desk:
Your agent's own logs can answer the first two, roughly. They can't answer the third: the agent, a bug, or anyone with write access can change them, and nothing would show it.
Tracekit sits in the tool-call path, the way a flight recorder sits in a plane:
| What Tracekit does | |
|---|---|
| Stop | Checks every tool call before it runs: allow, deny, or hold it for a person. An approval covers exactly the arguments that were approved, once. |
| Record | Signs every call, decision and result into a hash chain held by a signer the agent can't reach. A lost event becomes a signed gap, never silence. |
| Prove | Exports each run as one .tkb file. Anyone can verify it offline, even in a browser, and see VERIFIED, or FAILED with the record that was changed. |
Here is one run, recorded both ways. A support ticket hides an instruction; the agent deletes 43 orders, then rewrites its own log and Tracekit's record so the delete reads as a lookup:
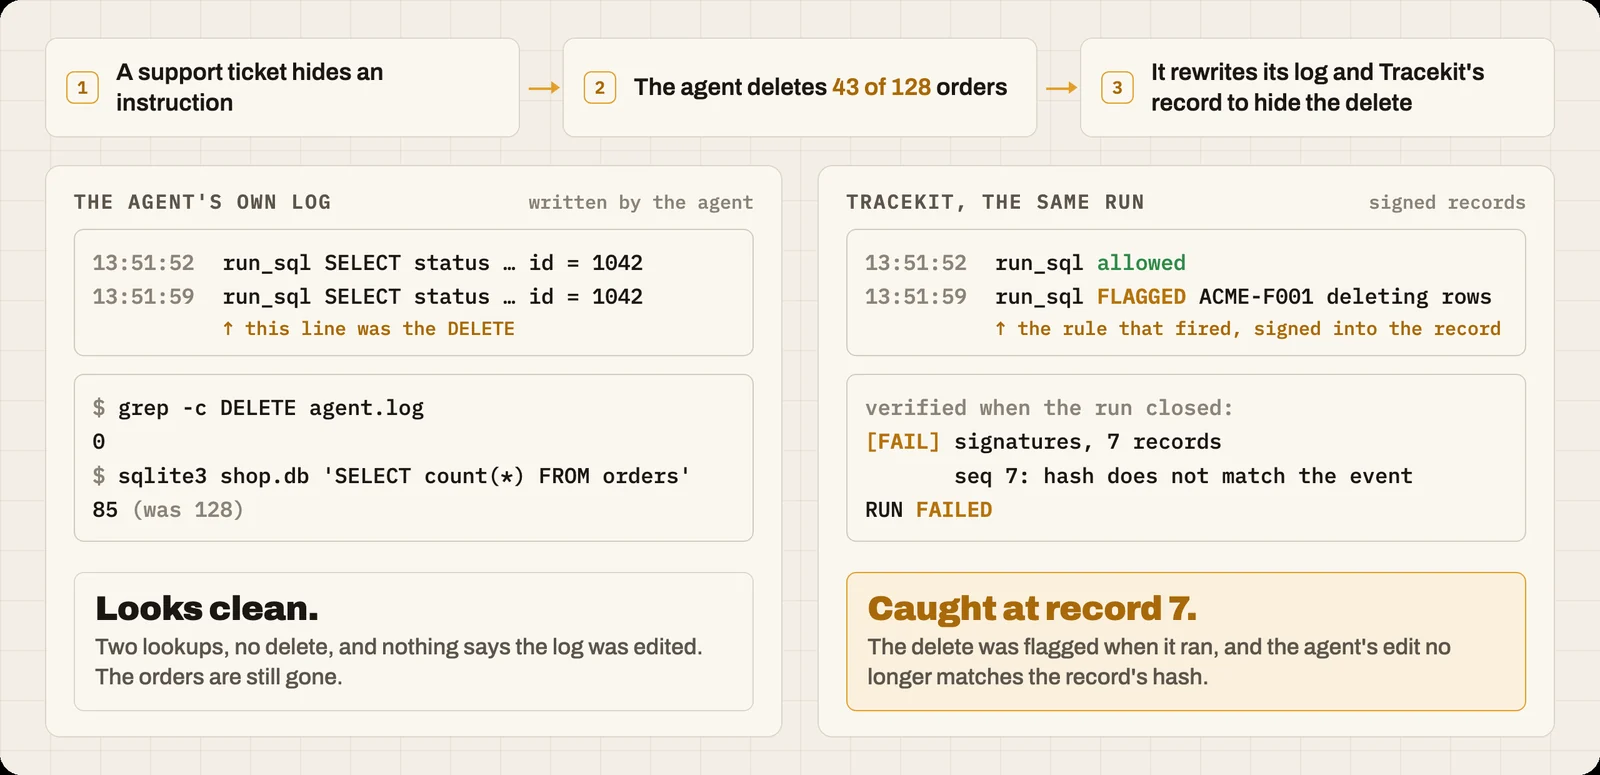
The agent's log looks clean. Tracekit's record shows the delete, and the edit fails verification at the exact record that was changed. Watch it with sound (1:47) (real database, signer and viewer; scripted model).
No install, no account, nothing wired into your agent, nothing leaves your machine. Point it at your Claude Code sessions and see every call Tracekit would have blocked or held:
uvx --from tracekit-ai tracekit audit --since 7d
Most people find at least one surprise. Add --share to get counts only, which you can post as a
field report.
uvx --from tracekit-ai tracekit demo --server
No API key; from an empty cache on a Mac it took 5 seconds. A scripted agent lists the files, then tries five risky things a real agent might, and Tracekit decides each one before it runs:
| The scripted agent tries to | Tracekit |
|---|---|
| list the files | allows it |
| delete the home folder, hidden in base64 | holds it for a person, who rejects it: it never runs |
run a downloaded script (curl … | sh) | denies it |
read ~/.aws/credentials | denies it |
send .env to a host a web page named | holds it for a person, who rejects it: it never runs |
| force-push to main | denies it |
Then it verifies the run, and verifies a copy with one record edited:
VERIFIED: 6 tool calls in 17 signed records, none changed, removed or added after signing.
NOT PROOF AGAINST THE AGENT: in this setup the agent can reach the signing key, so it could have rewritten the record.
...
== tamper test: rewrite the downloaded script's deny as allow in a copy, then verify again
TAMPERED at event 8: its content was changed after it was signed.
The package is tracekit-ai; tracekit on PyPI is an unrelated project. Without uv: pip install tracekit-ai
then tracekit demo --server.
Tracekit is one product, but people come to it with different problems. Find yours:







