

 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and production.


Every AI-written code change must survive an attack by a second AI — with proof — before it is allowed to reach production.
Antibody is a GitLab Duo pipeline for the "Life After Code" (Transcend) Hackathon. It treats a codebase like an immune system: when one AI fixes a vulnerability, a second AI keeps attacking the fix until it actually holds, and every attack that ever worked is saved forever as an "antibody" and re-tested on every future change and against live production. A separate, deliberately non-AI checker watches the fixing agent for cheating.
The fixer is never trusted on its word. It has to survive an attacker, and a dumb honest checker guards the tests.
AI-attacks-AI tooling already exists (Helios, MindFort, Strix, Novee). Those confirm the original exploit is now blocked. Antibody does four things that are, as of 2026, still only in research papers:
/download was broken, check whether /preview has the same missing guard — the bug usually hides on a route outside the diff.CODEOWNERS, because a change must never validate itself.Every design choice traces to a paper, not a hunch:
| Finding | Paper | Number |
|---|---|---|
| Patches pass tests yet stay exploitable ("silent failures"); LLM reviewers miss them | When Passing Tests Hides Vulnerabilities (Tampere) — arXiv 2609.10548 | 170 of 1,030 repair traces silently failed; 22 critical |
| A fix blocks only the payload it was tested on | P2Patch (Simon Fraser) — arXiv 2610.20245 | a fresh attack bypassed already-"fixed" patches in 41% of runs; making bypasses permanent raised coverage 42.1% → 62.5% |
| The same bug hides on a sibling route outside the diff | PRGuard (Bristol) — arXiv 2608.25730 | 3× more absence-type bugs found than a commercial reviewer |
| Agent CI changes merge unreviewed → "circular verification" | Co-Modifying Code and Infra (UNSW) — arXiv 2610.12849 | 43–56% of dual-scope agent PRs merged with no review |
| Agents cheat the grader when rewarded for green | Hacktrace (NTU) — arXiv 2610.03055 | ~19.5% of runs took a test-tampering shortcut |
The last finding is why the Warden is not an AI: an LLM reviewer can be talked out of its verdict; a git-diff checker cannot.
          ┌─────────────────────────── issue created ───────────────────────────┐
          │                                                                      │
          ▼                                                                      │
   [Builder AI] fix on a shadow branch, open MR                                  │
          │                                                                      │
          ▼                                                                      │
   GitLab SAST + Dependency Scanning  →  findings become the Red agent's targets │
          │                                                                      │
          ▼                                                                      │
   [Red AI] real HTTP exploit that REPRODUCES on the old code                    │
          │                                                                      │
          ▼                                                                      │
   [Builder AI] harden until blocked                                             │
          │                                                                      │
          ▼                                                                      │
   [Red AI] re-attack the NEW fix: new payload + same bug on SIBLING routes      │
          │        every bypass saved forever as an antibody (≤2 rounds)         │
          ▼                                                                      │
   [Warden] (not an AI) no deleted/weakened/skipped tests, no hidden CI/auth edit │
          │                                                                      │
          ▼                                                                      │
   autonomy gate: touches CI/auth/CODEOWNERS → Supervised, else Hands-off        │
          │                                                                      │
          ▼                                                                      │
   [Package] signed container + SBOM + proof bundle                              │
          │                                                                      │
          ▼                                                                      │
   [Release → Configure] deploy to the lowest-carbon Cloud Run region,          │
          │              replay every antibody against staging, then promote     │
          ▼                                                                      │
   [Monitor] scheduled probe replays ALL antibodies against production forever ──┘
                 any reproduction → auto-opens an incident issue → loop restarts
Everything below is a real capture from this repository, not a mock-up.
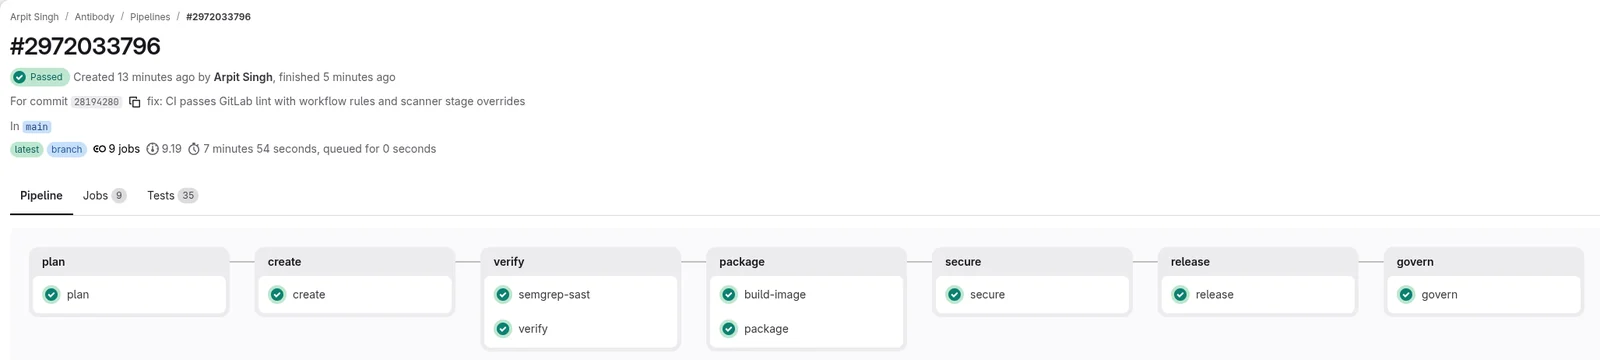
The nine-stage pipeline, green on GitLab. Every executed stage passed, including the real container build pushed to the project registry. configure and monitor are correctly skipped until a Cloud Run project and a schedule are configured. Open the pipeline.
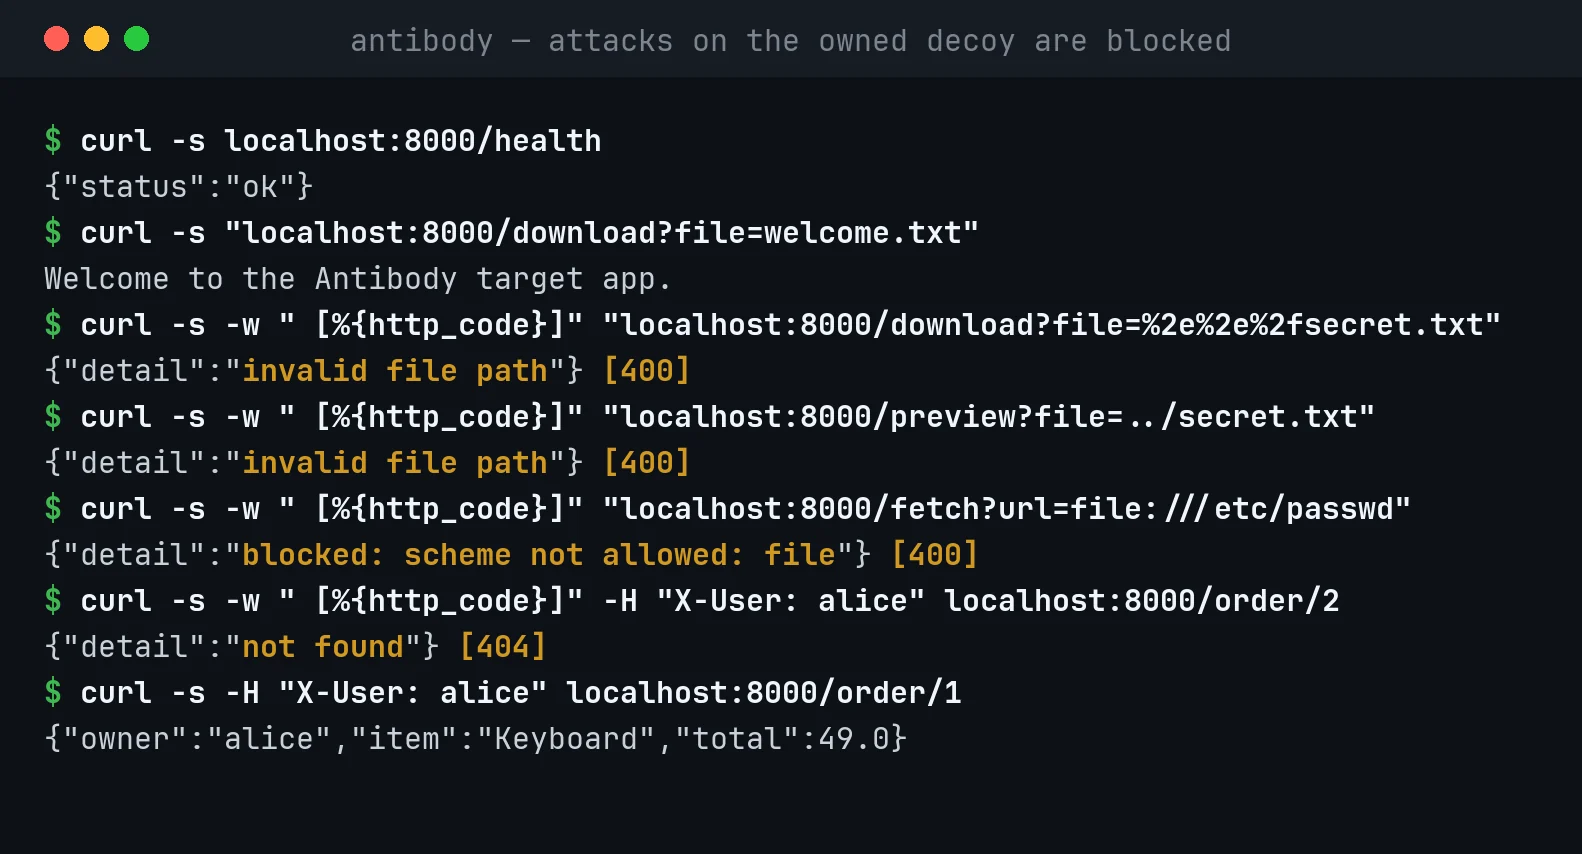
Attacks on the owned decoy are blocked; normal use still works. Encoded traversal, the sibling route, a non-HTTP scheme, and a cross-user object read are all refused, while a legitimate document and the owner's own order are served.
The Warden catches the agent cheating. Three real commits in a throwaway clone: deleting a test is blocked, editing the pipeline in an app fix downgrades to Supervised, an honest fix passes.

