
 #1
AI-powered decompilation, binary analysis, code summarization, and malware analysis tools.
Kitploit recommended
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
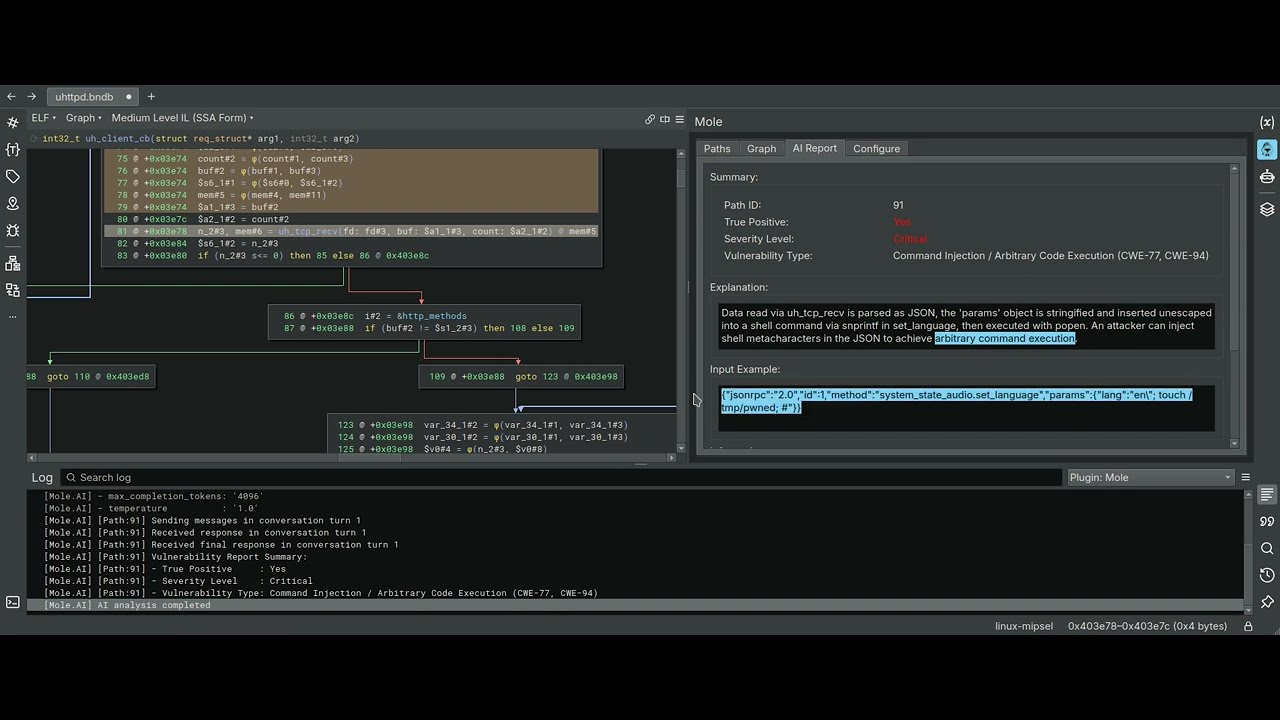 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 yuatemycat/superghidra
High-Performance Ghidra Architecture & GPU Acceleration Suite: LZ4/Zstd B-Tree Codec, Persistent Lock-Free Daemon, WGPU ARM64 Scanner, Z3 SMT Prover,…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 minglink/dsh-infinite-gen-5
DeepSeek v4.1 flash 逆向工具(无限五代) 求 Star 收藏 ⭐欢迎大家提交项目的改进
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 krxi/asmsense
Small language model that names and describes functions in stripped x86-64 binaries, with an open dataset, baselines, and LoRA fine-tuning…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.




