
 #1
AI-powered decompilation, binary analysis, code summarization, and malware analysis tools.
Kitploit recommended

 reverserid/jurig
a fully autonomous AI agent for reverse engineering
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
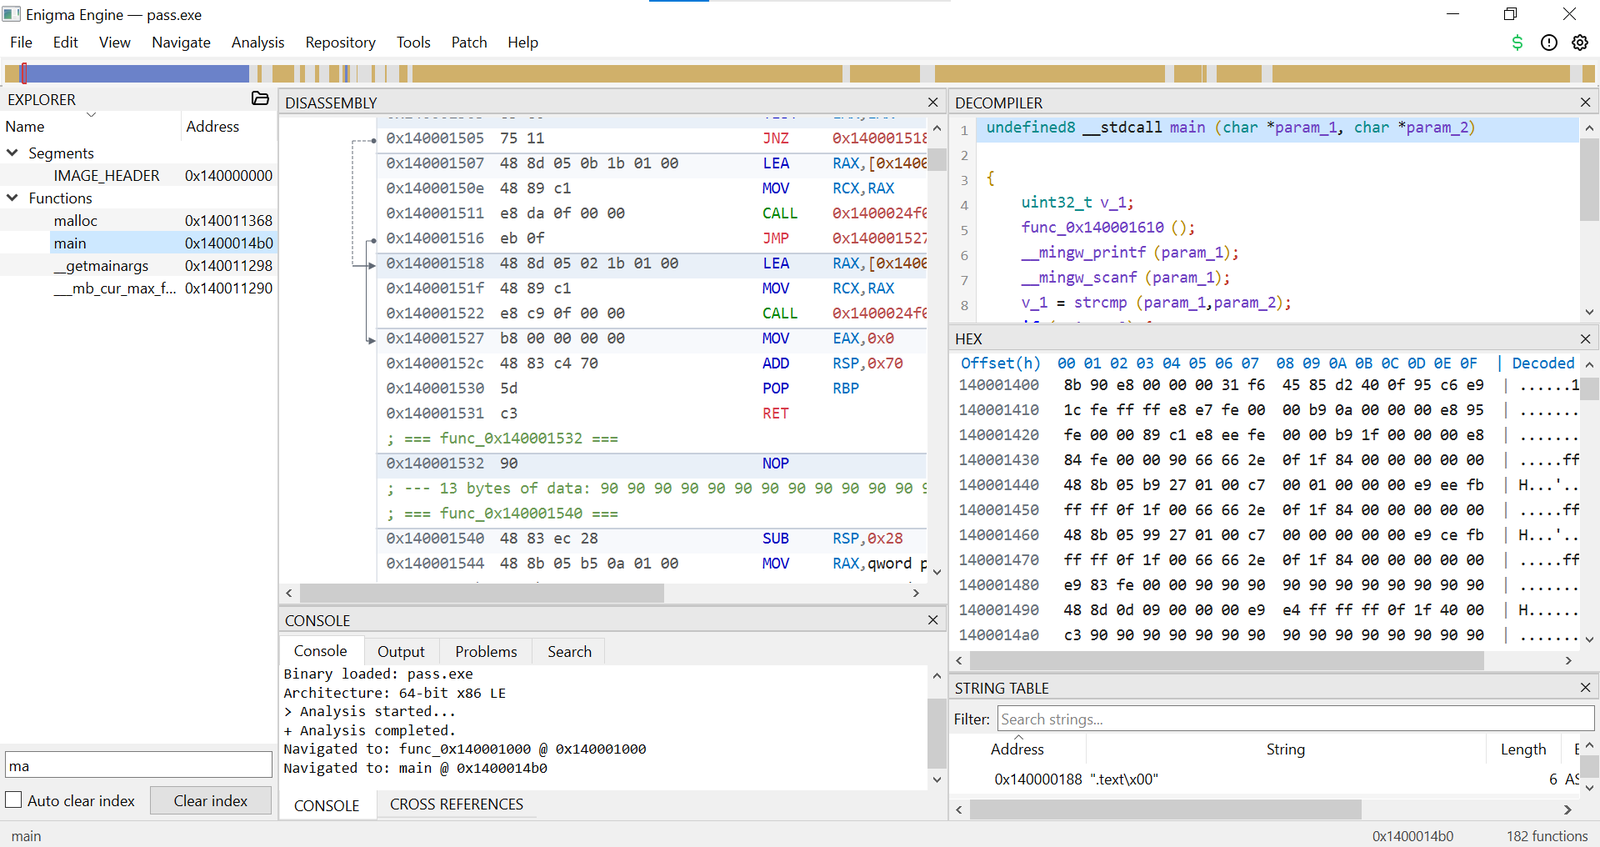 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
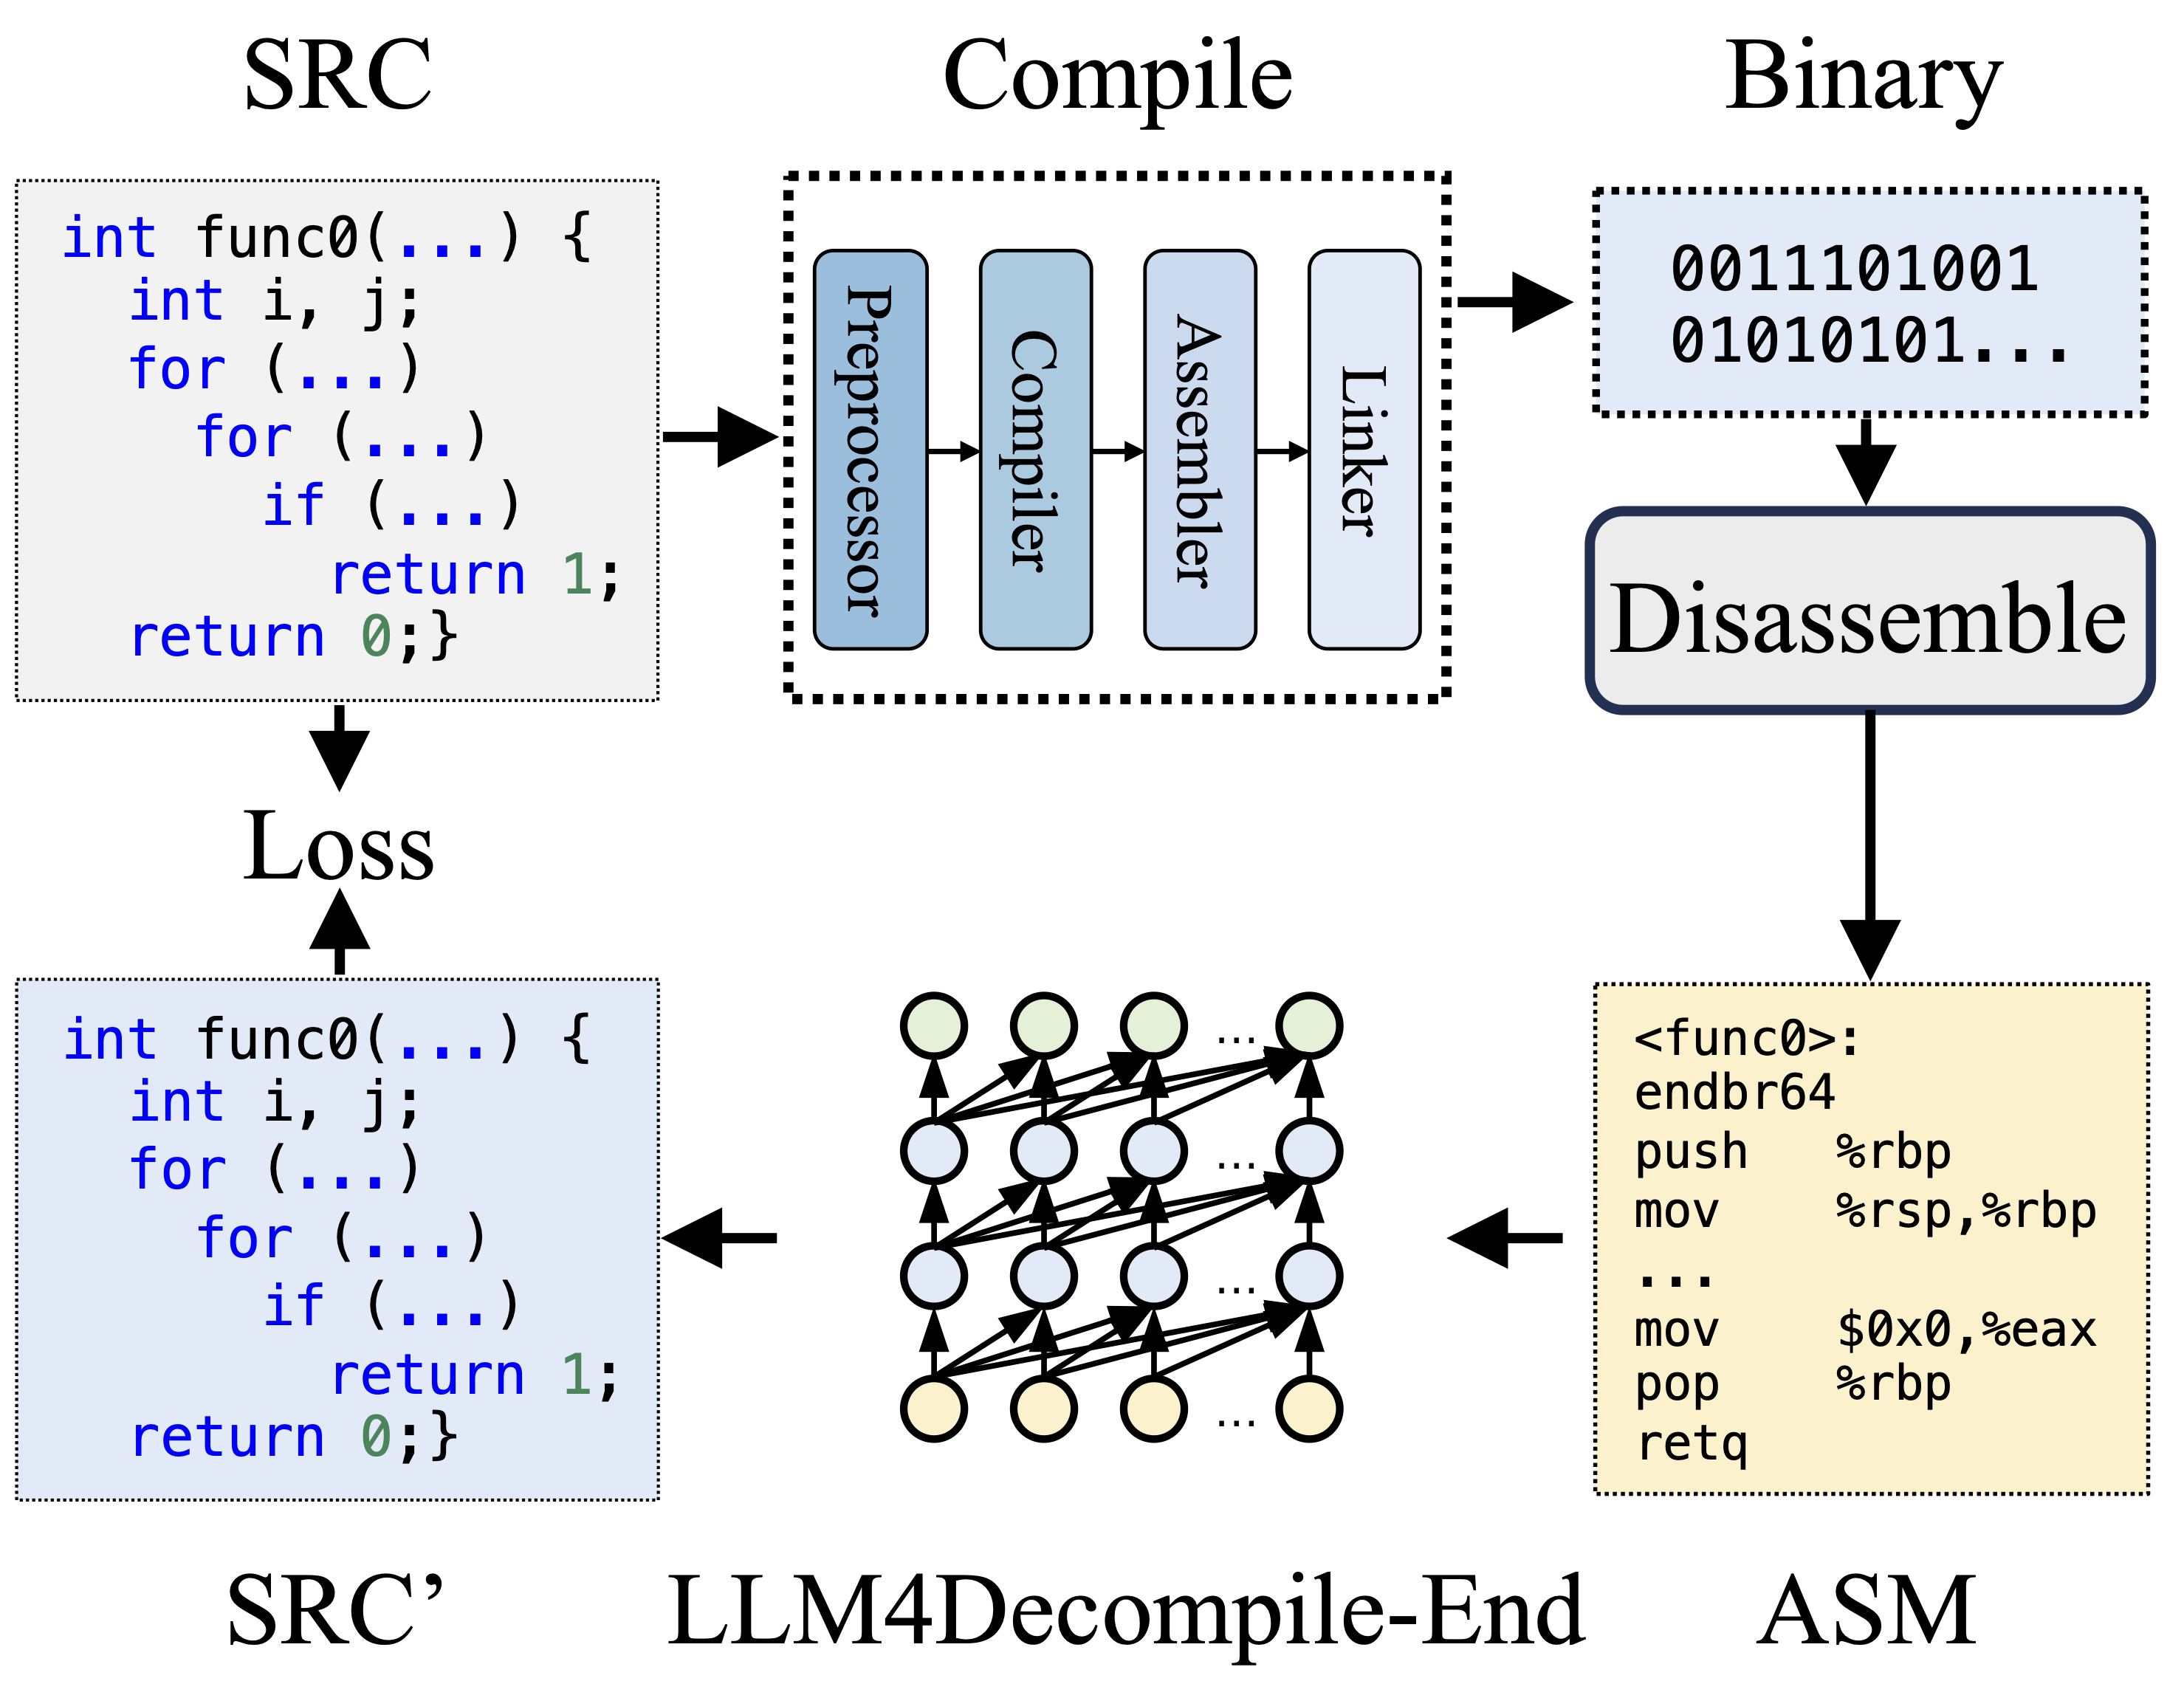 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 yuatemycat/superghidra
High-Performance Ghidra Architecture & GPU Acceleration Suite: LZ4/Zstd B-Tree Codec, Persistent Lock-Free Daemon, WGPU ARM64 Scanner, Z3 SMT Prover,…
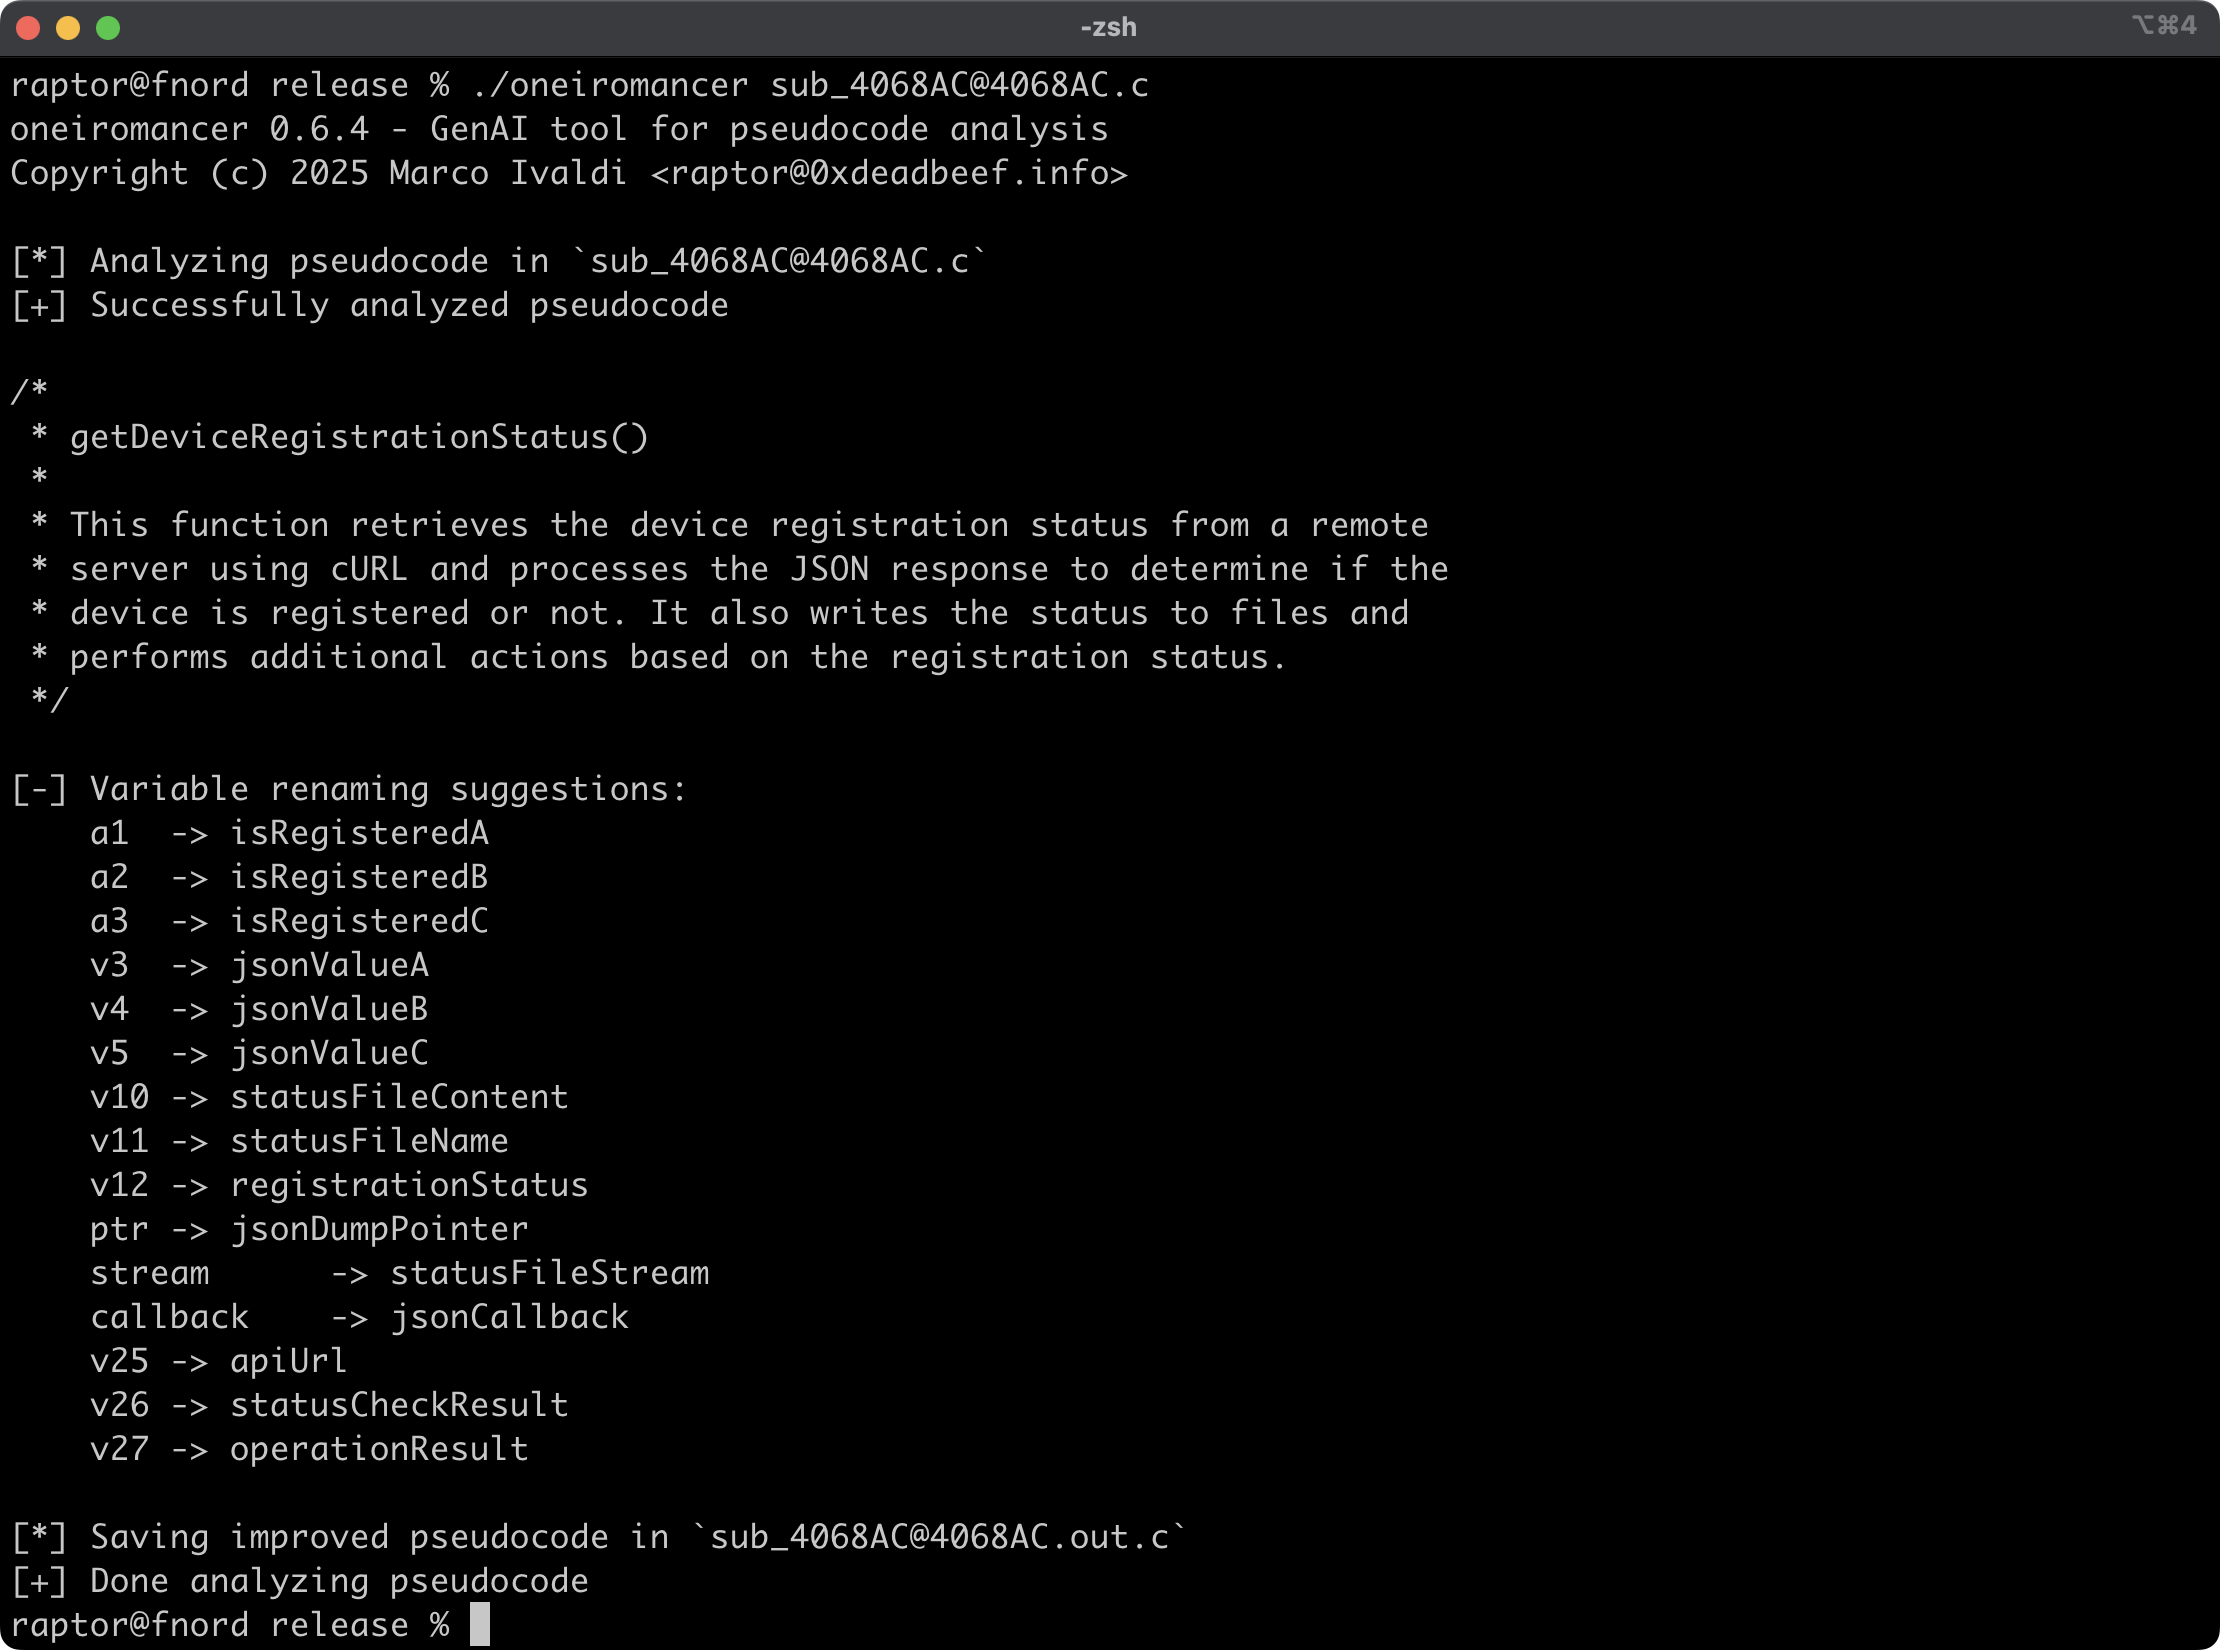 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 cosmosyi/autocontrol-arena
Automated framework for frontier AI safety evaluation that synthesizes executable, pressure-rich test environments to uncover latent risks in…
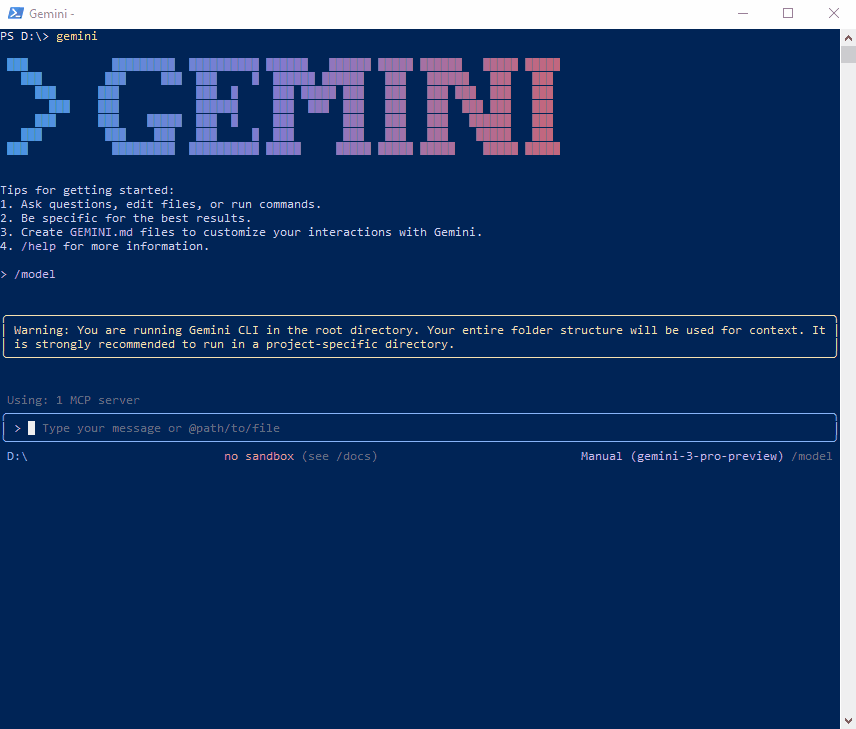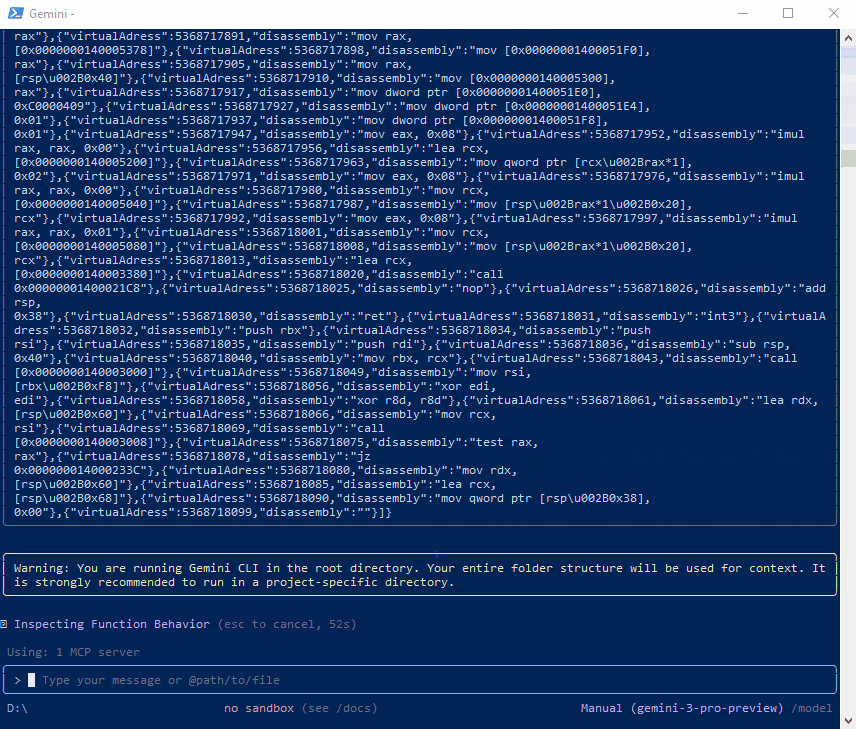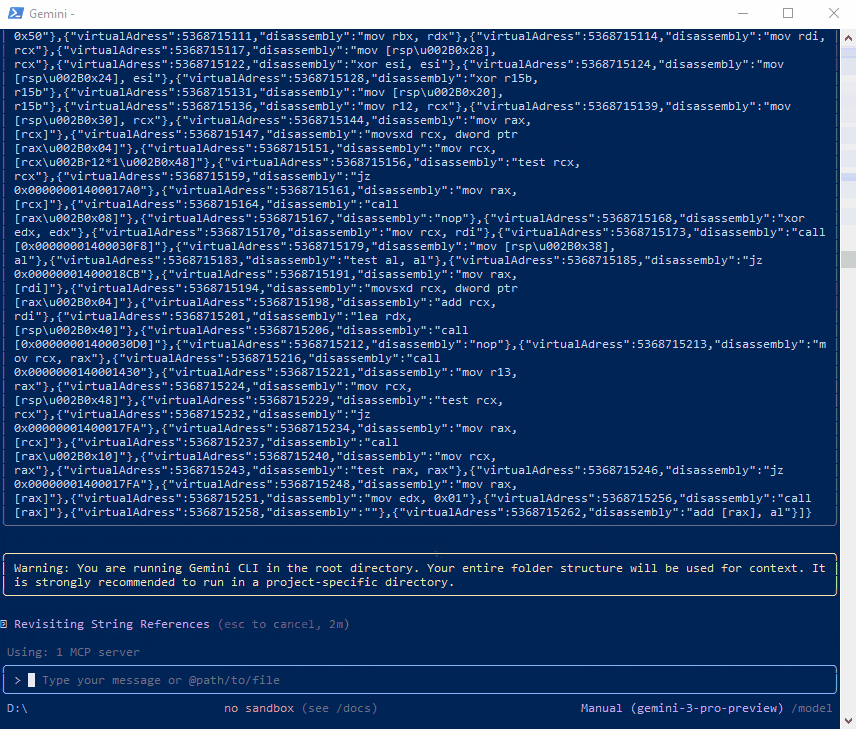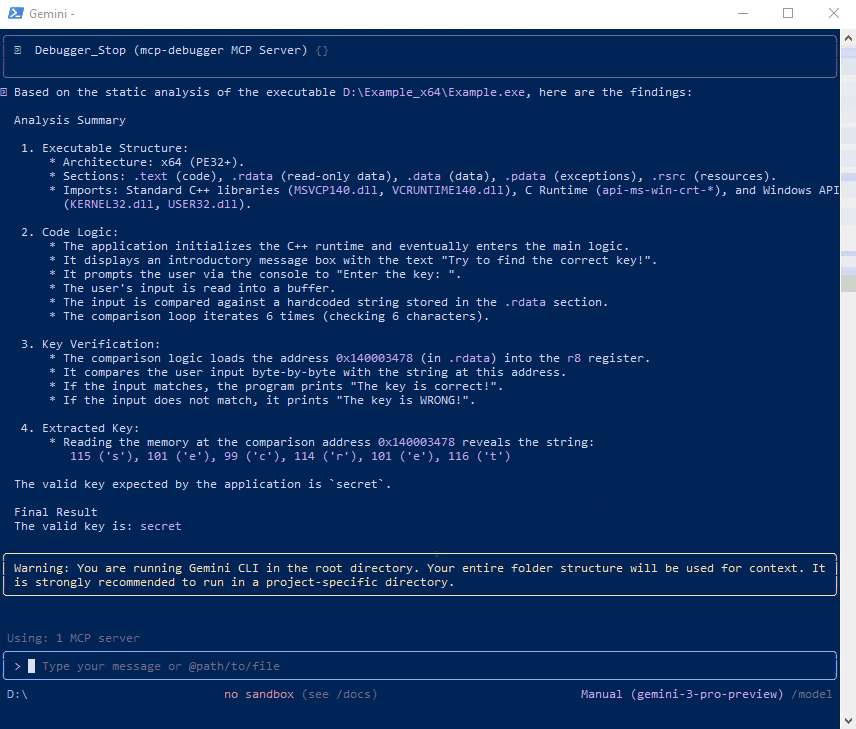 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
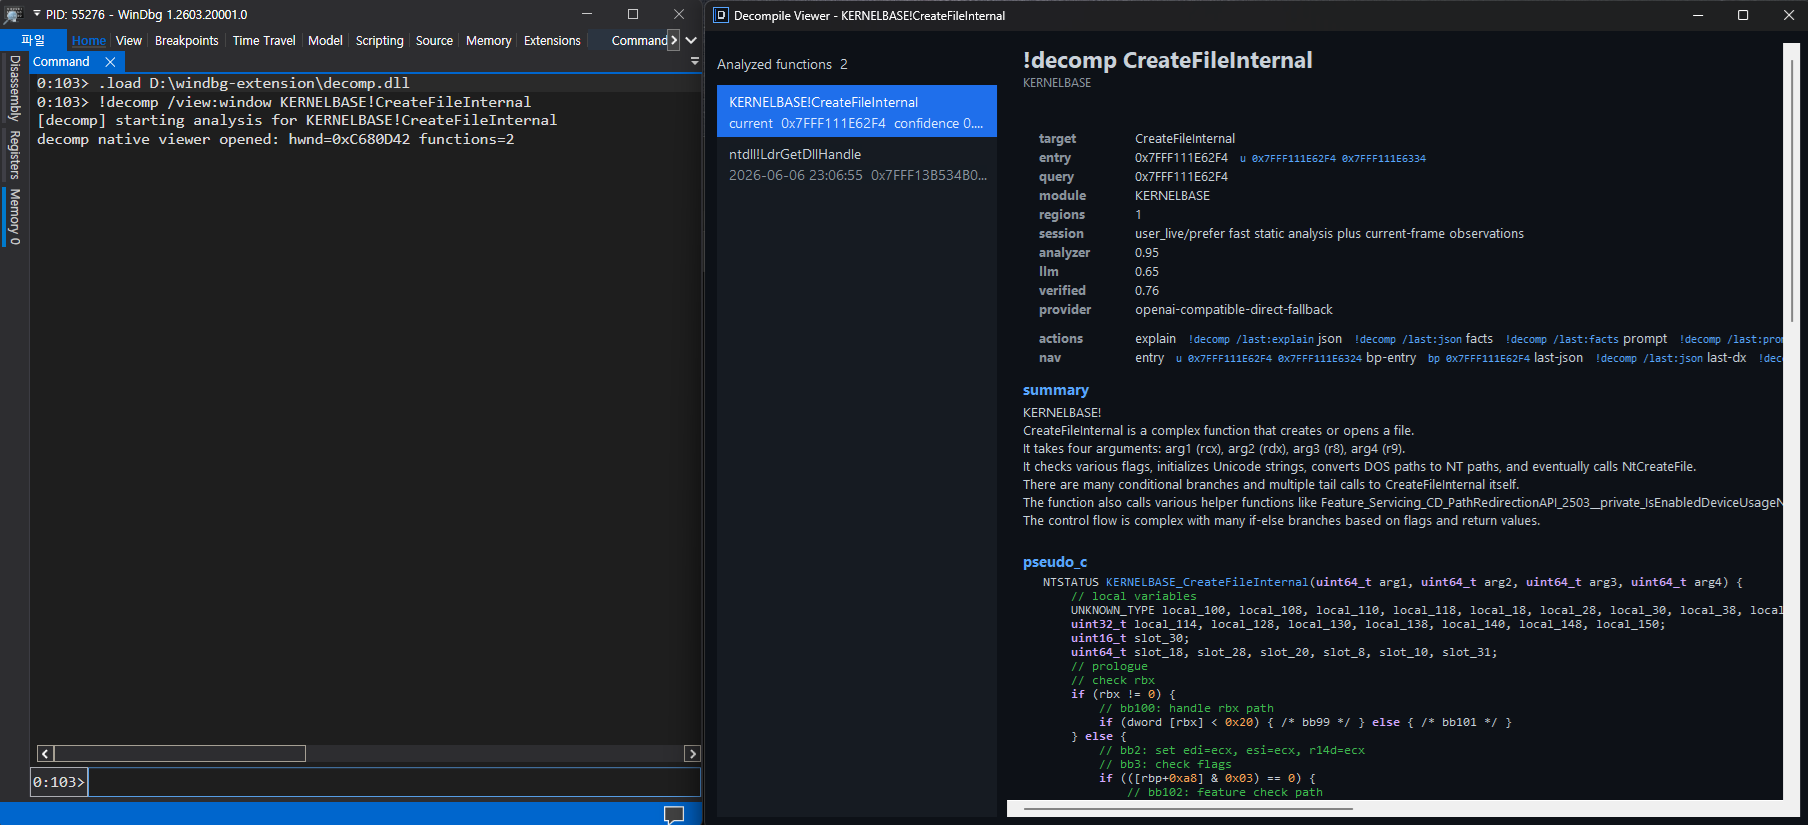 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
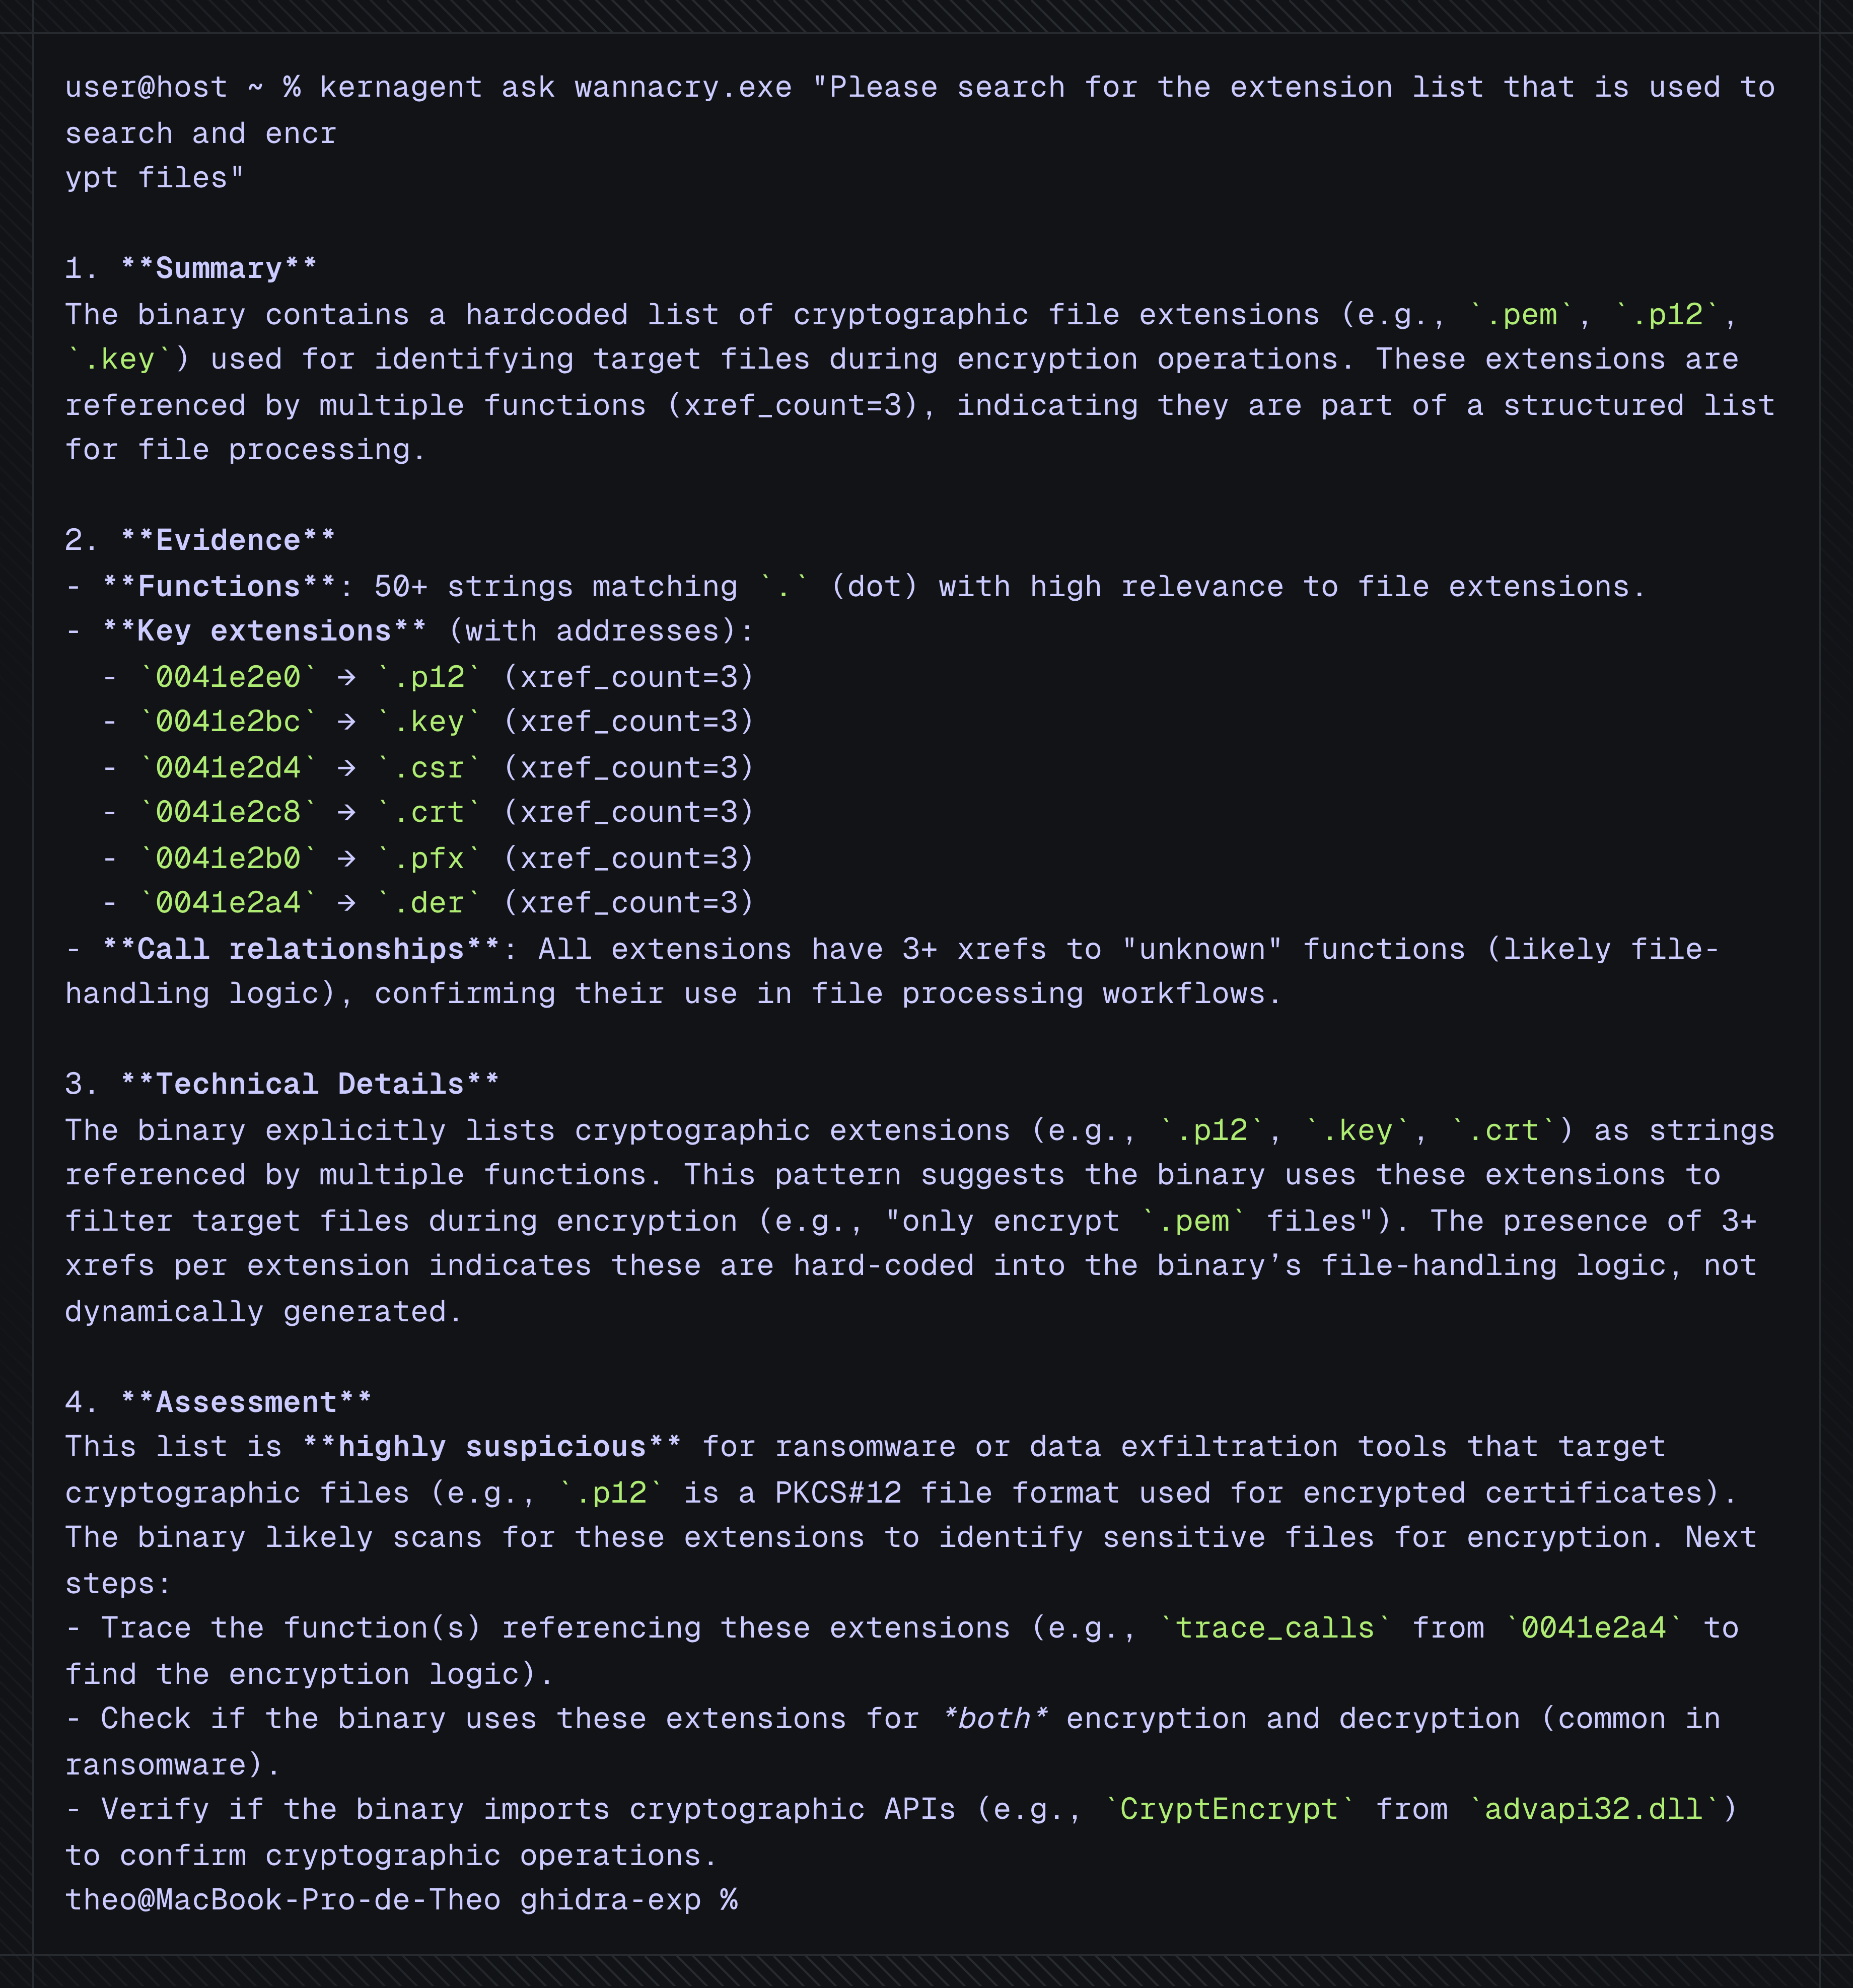 karib0u/kernagent
Headless AI agent for deterministic reverse engineering.
 lauriewired/ghidramcp
MCP Server for Ghidra





