

discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
osintreconnaissancevulnerability-scanners+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 hahwul/jwt-hack
JSON Web Token Hack Toolkit
 jonaslejon/malicious-pdf
Erstellt bösartige PDF-Testdateien für Penetrationstests, Bug-Bounty-Jagd und Red Teaming. Testet SSRF, XSS, XXE, NTLM-Credential-Diebstahl und…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 Module, 350 CVEs, 55 Hersteller, APT Group Engine. Deckt Router, IP-Kameras, GPON ONTs, ISP-CPEs,…
 yslxotwod/imsisting
GTK4- und CLI-Toolkit für zellulare Sicherheit mit 57 Modulen für 2G GSM, 3G UMTS, 4G LTE und 5G NR Funkschnittstelle, Kernnetz, SIM-Identität,…
 rapid7/metasploit-framework
Open-Source-Exploitation-Framework mit modularem Payload-, Encoder- und Hilfssystem für Penetrationstests, Schwachstellenvalidierung und…
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 nicetop1027/cve-2026-pending-django-summernote-rce
Proof-of-Concept für beliebiges Datei-Upload-RCE in django-summernote, wenn Pillow fehlt. Nutzt CWE-434 aus, um eine Web-Shell hochzuladen.
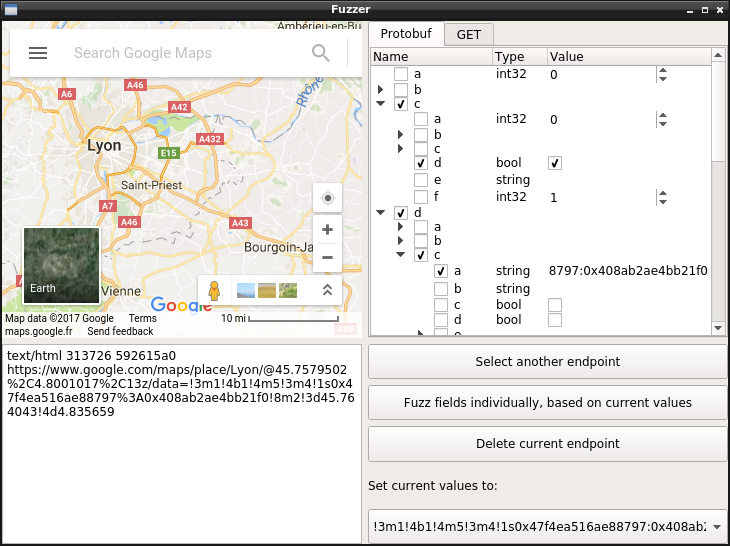 marin-m/pbtk
Ein Werkzeugsatz für Reverse Engineering und Fuzzing von Protobuf-basierten Anwendungen
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 azeemidrisi/phonesploit-pro
Ein All-in-One-Hacking-Tool zur Fernübernahme von Android-Geräten.
 ne0nd0g/merlin
Merlin ist ein plattformunabhängiger Post-Exploitation-HTTP/2-Command-&-Control-Server und -Agent, der in golang geschrieben ist.
 yasserbdj96/hiphp
PHP-basiertes Backdoor-Tool zur Fernsteuerung von Websites über HTTP/HTTPS. Ermöglicht Dateiverwaltung, Befehlsausführung und Tor-Konnektivität mit…
 bishopfox/sliver
Angreifer-Emulations-Framework
 affolter-engineering/xssearch
Rust-basierter XSS-Scanner mit kontextabhängiger Payload-Auswahl, WAF-Erkennung und -Umgehung, Crawling, Blind-XSS-Callbacks und statischer…
 bishopfox/joro
Ein kollaboratives Web-Exploitation-Framework.
 noraj/vbsmin
VBScript-Minifier
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…